Healthcare Cybersecurity

Cross-sector and Bi-partisan Collaboration Critical for Improving Healthcare Organizations

On February 21, 2019, Sen. Mark Warner (D-Va) wrote to several healthcare organizations and federal agencies requesting feedback on how the U.S. government and the healthcare industry can improve cybersecurity.

Sen. Warner is concerned about the number of successful healthcare cyberattacks in recent years, the huge numbers of Americans who are impacted by the attacks, and the cost to the healthcare industry of remediating the attacks. In his letter, Sen. Warner referenced a study conducted by Accenture in 2015 that suggested cyberattacks would cost the healthcare industry more than $305 billion over the next 5 years.

Se. Warner asked healthcare industry stakeholders several well-crafted questions inviting them to share their thoughts on steps that are currently being taken to improve cybersecurity, address vulnerabilities, and respond to attacks. He also sought suggestions on potential strategies for the U.S. government to adopt to improve cybersecurity at a national level.

Many of those contacted have responded to the request, including AdvaMed, the American Hospital Association (AHA), the American Medical Association (AMA), the College of Healthcare Information Management Executives (CHIME), the Healthcare Leadership Council (HLC), HITRUST, and the Virginia Hospital and Healthcare Association (VHHA).

Responses to Sen. Warner’s letter have been collected, amalgamated, and analyzed by the Institute for Critical Infrastructure Technology (ICIT).

ICIT identified several general themes from the responses. A common theme across all responses was the need for meaningful collaboration between public and private sector stakeholders and experts.

“Meaningful collaboration has proven one of the most under-utilized, cost-effective, and impactful strategies organizations can engage to mitigate hyper-evolving cyber threats,” wrote ICIT in its report (PDF).

Meaningful collaboration improves detection and response efforts and helps to prevent pass-through and supply chain attacks. While large healthcare organizations may have the resources to prevent, detect, and mitigate attacks, small healthcare organizations do not and are particularly vulnerable. Through collaboration, not only will smaller healthcare organizations be better protected, it will protect larger organizations against lateral movement from small partner networks.

There is a need for improved cybersecurity education and information sharing, which was highlighted by both the HLC and the AHA. The importance of ISAOs was also highlighted by AdvaMed. ISAOs provide timely cybersecurity information to allow members to be more proactive and prevent cyberattacks and data breaches.

Proactive cybersecurity was also a key theme. Healthcare organizations need to shift from reacting to incidents when they occur to being proactive and preventing data breaches. A lack of a proactive approach means patients suffer, as it is their sensitive data which will be stolen. While proactive cybersecurity naturally comes at a cost, it can be cost-effective as fines, breach remediation costs, and lawsuits can be avoided.

The AHA drew attention to the risks of attacks on legacy systems, which were developed at a time when cybersecurity was not a major consideration. The AHA stressed the importance of the FDA assisting in raising awareness of the threats to legacy systems and how to bolster cybersecurity.

The complexity of healthcare networks is a major concern, especially with the growing use of IoT devices. While many healthcare organizations have secured their servers, desktops, and laptops, management of other devices such as drug infusion pumps, embedded devices, and imaging systems needs to improve. Many healthcare organizations cannot even keep track of all the devices that connect to their networks, let along evaluate the security of each device.

“If health systems are forced to trust a conglomeration of open commercial networks to manage their endpoints, we will continue to have an issue securing our medical devices and other critical systems,” explained CHIME. “Unless we have a separate secure system, where trusted parties are vetted securely, as is done with military or other government networks, our medical devices and other end points will still be at risk.”

The complex nature of HIPAA means many resources need to be committed to compliance, yet only minimal standards for healthcare privacy and security are offered. Complying with HIPAA does not necessarily help prevent data breaches. Healthcare organizations that are HIPAA-compliant also tend to have fewer resources to commit to proactive cybersecurity.

“Instead of focusing on punishing healthcare providers who suffer cybersecurity incidents, and thereby further reducing their resources available to modernize systems or adopt layered security controls, emerging governance should incentivize organizations to learn from their mistakes and share those lessons with other stakeholders,” suggested ICIT.

HITRUST, CHIME, HLC, and the AHA all recommend the creation of a safe harbor for healthcare organizations that demonstrate they are in compliance with security regulations to give them immunity from enforcement actions following data breaches. The safe harbor would incentivize them to implement security controls that they might otherwise forgo. It would likely result in improvements to cybersecurity defenses instead of healthcare organizations opting for the minimal level of protection to ensure compliance.

Sen. Warner’s letter has started an important conversation about healthcare cybersecurity. It is hoped that the points raised and continued cross-sector and bi-partisan collaboration will help to see major improvements made to cybersecurity across the healthcare sector.

The post Cross-sector and Bi-partisan Collaboration Critical for Improving Healthcare Organizations appeared first on HIPAA Journal.
OCR Issues Warning on Advanced Persistent Threats and Zero-Day Exploits

The HHS’ Office for Civil Rights has raised awareness of the risk of advanced persistent threats and zero-day exploits in its spring cybersecurity newsletter.

Healthcare organizations are attractive targets for hackers due to quantity of sensitive data they store. Individual’s protected health information is highly valuable as it can be used for many different purposes, including identity theft, tax fraud, and gaining access to medical services. Sensitive information about medical conditions can also be used to blackmail individuals.

Healthcare organizations also store research data, genetic data, and data from experimental treatments, all of which are of great value cybercriminals. The information can be used by foreign governments to drive innovation.

There are many techniques that hackers use to break through defenses and silently gain access to networks, two of the most serious threats being advanced persistent threats and zero-day exploits.

An advanced persistent threat (APT) is a term used to refer to repeated cyberattacks that attempt to exploit vulnerabilities to gain access to information systems. These attacks are often sophisticated, but even relatively simple attacks are dangerous due to their persistence.

The aim of the attacks is to stealthily gain access to information systems and steal information over a long period of time. “Advanced” comes from the techniques used to access networks and remain undetected, such as the use of malware. “Persistent” refers to the length of time that systems are accessed and information is stolen. Several APT groups have succeeded in gaining access to healthcare IT systems in the United States and have used that access to steal sensitive patient information and propriety healthcare data.

Zero-day exploits – or zero-day attacks – involve the use of previously unknown vulnerabilities to attack organizations. By their very nature, these types of attacks can be difficult to prevent. Since the vulnerabilities are only known to hackers, no patches exist to correct the flaws.

Oftentimes, vulnerabilities are discovered as a result of them being exploited. Patches are promptly released to correct the flaws, but hackers will continue to take advantage of the vulnerabilities until systems are patched. It is therefore essential to apply patches promptly and ensure that all operating systems and software are kept up to date.

Once a zero-day vulnerability is publicly disclosed it doesn’t take long for an exploit to be developed. Oftentimes, exploits for recently discovered vulnerabilities are developed and used in attacks within days of a patch being released.

If patches cannot be applied promptly, such as if extensive testing is required, it is important to implement workarounds or other security controls to prevent the vulnerabilities from being exploited. The use of encryption and access controls can help to ensure that even if access to a network is gained through the exploitation of a vulnerability, damage is minimized.

OCR has warned of the danger of combination attacks involving APTs and zero-day exploits, such as the use of the NSA’s EternalBlue exploit. Within days of the exploit being made available online, it was incorporated into WannaCry ransomware which infected hundreds of thousands of computers around the world. A patch for the vulnerability that EternalBlue exploited was released by Microsoft 2 months before the WannaCry attacks. Organizations that patched promptly were protected against the exploit and WannaCry.

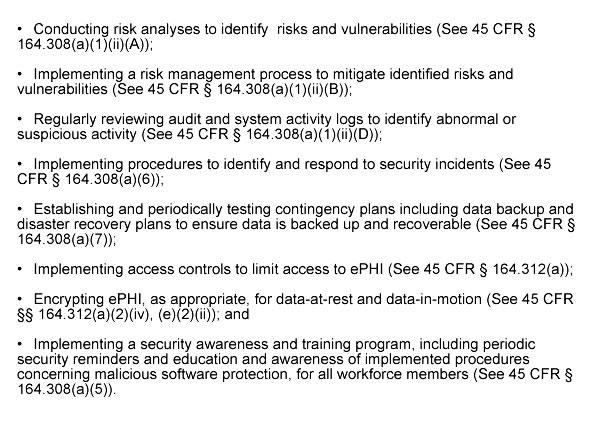
Healthcare organizations and their business associates can Improve their defenses against zero-day exploits and APTs by implementing measures outlined in the HIPAA Security Rule. OCR has draw attention to the following requirements of the Security Rule which can help prevent and mitigate zero-day exploits and APTs:

The post OCR Issues Warning on Advanced Persistent Threats and Zero-Day Exploits appeared first on HIPAA Journal.

Webinar: April 4, 2019: Email Security, DMARC, and Sandboxing

The healthcare industry is particularly vulnerable to phishing attacks and successful attacks commonly result in significant data breaches. It is now something of a rarity for a week to pass without a healthcare phishing attack being reported.

While healthcare organizations are providing security awareness training to staff and are using email security solutions, those defenses are not always effective.

To improve understanding of why advanced attacks are managing to evade detection by traditional email security solutions, email security solution provider TitanHQ is hosting a webinar.

During the webinar TitanHQ will explain about the threat from phishing and how organizations can protect themselves and their customers/patients. The webinar will also explain how two new features of TitanHQ’s SpamTitan email security solution – DMARC authentication and sandboxing – can protect against advanced email threats, zero-day attacks, malware, phishing, and spoofing.

Webinar Details:

Date : Thursday, April 4th, 2019

Time: 12pm EST

Duration: 30 minutes

Sign up to the Webinar here.

Disclaimer

This is not a sponsored event.  HIPAA Journal has no business relationship with the event holder.  HIPAA Journal promotes events that might be of interest to its readers. You may submit your event information on our contact page. HIPAA Journal does not accept payment for promoting events.

The post Webinar: April 4, 2019: Email Security, DMARC, and Sandboxing appeared first on HIPAA Journal.

Study Reveals Health Information the Least Likely Data Type to be Encrypted

Health information is the least likely data type to be encrypted, even though health information is highly valuable to cybercriminals, according to the Global Encryption Trends Study conducted by the Ponemon Institute on behalf of cryptographic solution provider nCipher.

The study was conducted on 5,856 people across several industry sectors in 14 countries, including the United States. The aim of the study was to investigate data encryption trends, the types of data most likely to be encrypted, how extensively encryption has been adopted to improve security, and the challenges faced by companies when encrypting data.

The study shows the use of encryption has steadily increased over the past four years. 45% of surveyed organizations said they have an overall encryption plan or strategy that is applied across the whole organization. 42% said they have a limited encryption plan or strategy, with encryption only used on certain applications and data types. 13% of respondents said they do not use encryption at all on any type of data.

The use of encryption varies considerably from country to country. Germany leads the world with the highest prevalence of encryption, followed by the United States, Australia, and the United Kingdom. Out of the 14 countries represented in the survey, the Russian Federation and Brazil had the lowest prevalence of encryption. 65% of companies in the United States had an overall encryption plan that was consistently applied across the whole organization.

The industries that had the highest prevalence of encryption were tech & software (52%), financial services (50%), and the healthcare and pharmaceutical industries (49%).

Encryption technology varied considerably and there was no single technology that dominates in organizations. The most common uses of encryption were for Internet communications, databases and laptop hard drives.

The main reasons for implementing encryption, cited by 54% of respondents, were to protect sensitive intellectual property and customers’ personal information.

The types of data most commonly encrypted are payment-related data (55%), financial records (54%), HR/employee data (51%), and intellectual property (51%). Health information was the least likely type of data to be encrypted. This is surprising, given the value of healthcare data to cybercriminals and the harm that can be caused should information fall into the wrong hands. Only 24% of respondents said health data was routinely encrypted.

Organizations looking to encrypt data face several challenges. The biggest challenge which was faced by 69% of respondents was identifying all sensitive data on the network. The initial implementation of encryption was a major challenge for 49% of respondents and 32% of respondents said they faced problems classifying which data they should encrypt.

One of the biggest encryption headaches is key management. Respondents were asked to rate key management on a pain scale of 1-10. 61% of respondents said key management was very painful and managing keys was a major challenge.

The main reason why key management is difficult is a lack of clear ownership of the key management function, a lack of skilled personnel, and isolated or fragmented key management systems.

Various key management systems are used by organizations, the most common being formal key management policy (KMP), followed by formal key management infrastructure (KMI) and manual process.

The post Study Reveals Health Information the Least Likely Data Type to be Encrypted appeared first on HIPAA Journal.

Concerns Raised About the Sharing of Health Data with Non-HIPAA Covered Entities via Apps and Consumer Devices

Earlier this month, the eHealth Initiative Foundation and Manatt Health issued a brief that calls for the introduction of a values framework to better protect health information collected, stored, and used by organizations that are not required by law to comply with Health Insurance Portability and Accountability Act (HIPAA) Rules.

Health information is increasingly being collected by a wide range of apps and consumer devices. In many cases, the types of data collected by these apps and devices are the same as those collected and used by healthcare organizations. While healthcare organizations are required to implement safeguards to ensure the confidentiality, integrity, and availability of health information and uses and disclosures of that information are restricted, the same rules do not cover the data if the information is collected by other entities.

It doesn’t matter what type of organization stores or uses the data. If that information is exposed it can cause considerable harm, yet this is currently something of a gray area that current regulations do not cover properly.

At the time when HIPAA and the subsequent Privacy and Security Rules were enacted, the extent to which health information would be collected and used by apps and consumer devices could not have been known. Now, new rules are required to ensure that health information is not exposed and remains private and confidential when collected by non-HIPAA covered entities.

Laws have been introduced that do extend to health data collected by apps and consumer devices, including the California Consumer Privacy Act (CCPA), but these laws only apply at the state level and protections for consumers can vary greatly from state to state.

HIPAA was updated by the HITECH Act of 2009, which does cover electronic medical records and health IT, but does not extend to apps and consumer devices. GDPR covers consumer data collected by apps and consumer devices, but only for companies doing business with EU residents.

The Brief, entitled, Risky Business? Sharing Data with Entities Not Covered by HIPAA explores the problem, the extent of data now being shared, and aims to clear up some of the confusion about when HIPAA applies to apps and consumer devices and when it does not and explores other federal guidance and regulations that has been issued by the FDA, FTC, and CMS covering mobile apps and consumer devices.

HIPAA does apply to business associates of HIPAA covered entities that provide apps and devices on behalf of the covered entity. However, if the app or device is not provided by a vendor acting as a business associate of a HIPAA covered entity, HIPAA Rules do not apply. Many healthcare organizations struggle to make the determination about whether a vendor is a business associate and if devices and apps are offered on behalf of the covered entity. The brief attempts to explain the often-complex process.

One area of particular concern is the growing number of people who are using genealogy services and are supplying companies with their DNA. Individuals are voluntarily providing this information, yet many are unaware of the implications of doing so and are unaware of the lucrative DNA market and the potential sale of their DNA profiles.

“Privacy and security in healthcare are at a critical juncture, with rapidly changing technology and laws that are struggling to keep pace,” explained Jennifer Covich Bordenick, Chief Executive Officer, eHealth Initiative Foundation. “Even as new laws like CCPA and GDPR emerge, many gray areas for the use and protection of consumer data need to be resolved. We hope the insights from papers like this help industry and lawmakers to better understand and address the world’s changing privacy challenges.”

The post Concerns Raised About the Sharing of Health Data with Non-HIPAA Covered Entities via Apps and Consumer Devices appeared first on HIPAA Journal.

Healthcare Industry Ranks 8th for Cybersecurity but Poor DNS Health and Endpoint Security of Concern

Through compliance with HIPAA, healthcare organizations have achieved a baseline standard of security, but there is still plenty of room for improvement and healthcare cybersecurity is at best mediocre.

The 2019 Healthcare Cybersecurity Report from Security Scorecard revealed the healthcare industry ranks 8th for cybersecurity out of the 18 industry sectors that were studied for the report.

The worst aspects of security for the healthcare industry were DNS health and endpoint security, where the industry ranked 13th and 12 th respectively.

Without proper DNS security measures in place, attacks could take place in which DNS records are changed. Such an attack would allow cybercriminals to route web traffic to fraudulent websites where credentials could be harvested. The US Department of Homeland Security’s Cybersecurity and Infrastructure Agency (CISA) issued a warning about this attack method in January 2019.

Endpoint security is another big concern. In healthcare, employees use a wide range of different types of devices to gain access to healthcare networks, which introduces risks and many healthcare organizations are struggling to address those risks effectively. Security Scorecard cites the 2018 HIMSS Cybersecurity Report which revealed 27.5% of healthcare employees surveyed thought there were too many endpoints in use, which was seen to be one of the biggest barriers to remediating and mitigating cybersecurity incidents.

The one area of apparent strength is network security, where the healthcare industry ranked 5th out of 18. The relatively high score in this area is not necessarily as good as it first appears. The high position means healthcare organizations are protecting the network perimeter through the use of firewalls and are segmenting their networks to limit access to devices and data in the event of a perimeter breach.

Security Scorecard notes that the network security and endpoint security scores suggest the healthcare industry is adopting an “eggshell security model” which means the perimeter controls are strong, but they are being used to defend a particularly soft and vulnerable internal network. If the perimeter is breached, insufficient controls are present to limit the harm that can be caused.

The other areas assessed for the report were application security and patching cadence, where healthcare was deemed mediocre with scores of 8/18 and 10/18 respectively. The application security score was relatively good, but Security Scorecard warned that the high number of applications used in healthcare creates multiple exploitable vectors to attack and the increasing use of networked medical devices could be placing data at risk.

Patching of known vulnerabilities is relatively slow. Patches are delayed to avoid system and application downtime and because they cause a significant increase in system resources. However, delays in patching leave organizations vulnerable. Many attacks occur within a few days of patches being released.

“The risk of ePHI exposure and unauthorized access is an increasing trend year after year,” said Fouad Khalil, VP of Compliance at Security Scorecard. “Healthcare organizations must adopt continuous assurance practices to maintain compliance and adequately protect data… Poor cybersecurity practices cannot be taken lightly.”

The post Healthcare Industry Ranks 8th for Cybersecurity but Poor DNS Health and Endpoint Security of Concern appeared first on HIPAA Journal.

Concerns Raised with FDA over Medical Device Security Guidance

The U.S. Food and Drug Administration (FDA) is reviewing feedback on the guidance for medical device manufacturers issued in October 2018.

Comments have been submitted on the guidance, Content of Premarket Submissions for Management of Cybersecurity in Medical Devices, by more than 40 groups and healthcare companies before the commenting period closed on March 18. Feedback will be taken on board and the guidance will be updated accordingly. The final version of the guidance is expected to be released later this year.

The requirement for medical device manufacturers to submit a ‘Cybersecurity Bill of Materials’ to the FDA as part of the premarket review has been broadly praised. The CBOM needs to include a list of software and hardware components which have vulnerabilities or are susceptible to vulnerabilities. The CBOM will help healthcare organizations assess and manage risk.

However, concerns have been raised by several groups about having to include all hardware components, as it may not even be possible for device manufacturers to provide that information. If hardware components and subcomponents are included, the list could be extensive and contain hundreds of different components. Requests have been made to limit the CBOM to software, and to change the language to Software Bill of Materials as hardware maybe outside the control of the device manufacturer.

The FDA has proposed a two-tier classification of medical devices based on cybersecurity risk. The first tier includes devices that have a high cybersecurity risk, which includes devices that connect to healthcare networks and devices that could potentially result in multiple patients coming to harm if a cybersecurity incident occurs. The second tier includes devices with a standard level of risk.

Several groups have submitted comments requesting changes to this tiered system, including dropping both tiers and adopting a single risk-based approach or the addition of a third tier for devices with low cybersecurity risk. It has also been suggested that the definition of the tiers be changed to include indirect harm to patients or an organization so as to include privacy risks from the exposure of sensitive data.

CHIME suggests the FDA should change its definition of medical device risk to include all risks associated with medical devices. Medical devices could be used as a platform to conduct further attacks on an organization and risks extend far beyond medical devices. CHIME suggested the FDA should expand the definition of risk to include risks to the entire health IT ecosystem.

CHIME also explained that some device manufacturers are not doing enough to address known risks. For example, the patch released to address the vulnerability that was exploited in the WannaCry ransomware attacks in 2017 still hasn’t been applied to many medical devices as manufacturers class the vulnerability as a controlled risk. In other cases, no action is being taken to address known vulnerabilities until the FDA decides a device recall is required. CHIME suggests it should not be up to the device manufacturer to decide whether a risk is controlled or uncontrolled.

CHIME also suggests that the FDA needs to be much clearer about the steps that medical device manufacturers are expected to take to address known vulnerabilities to ensure patient safety is not put at risk, and that there should be a requirement to meet a certification standard as there is for electronic medical records.

The post Concerns Raised with FDA over Medical Device Security Guidance appeared first on HIPAA Journal.

Critical Vulnerability Affects Medtronic CareLink Monitors, Programmers, and ICDs

Two vulnerabilities have been identified in the Conexus telemetry protocol used by Medtronic MyCarelink monitors, CareLink monitors, CareLink 2090 programmers, and 17 implanted cardiac devices. Both vulnerabilities require a low level of skill to exploit, although adjacent access to a vulnerable device would be required to exploit either vulnerability.

The most serious vulnerability, rated critical, is a lack of authentication and authorization controls in the Conexus telemetry protocol which would allow an attacker with adjacent short-range access to a vulnerable device to inject, replay, modify, and/or intercept data within the telemetry communication when the product’s radio is turned on.

An attacker could potentially change memory in a vulnerable implanted cardiac device which could affect the functionality of the device.

The vulnerability is being tracked as CVE-2019-6538 and has been assigned a CVSS v3 base score of 9.3.

A second, medium severity vulnerability concerns the transmission of sensitive information in cleartext. Since the Conexus telemetry protocol does not use encryption, an attacker with adjacent short-range access to a vulnerable product could intercept communications and obtain sensitive patient data.

The vulnerability is being tracked as CVE-2019-6540 and has been assigned a CVSS v3 base score of 6.5.

The vulnerabilities affect the following Medtronic devices:

  • Versions 24950 and 24952 of MyCareLink Monitor
  • Version 2490C of CareLink Monitor
  • CareLink 2090 Programmer

All models of the following implanted cardiac devices are affected:

  • Amplia CRT-D
  • Claria CRT-D
  • Compia CRT-D
  • Concerto CRT-D
  • Concerto II CRT-D
  • Consulta CRT-D
  • Evera ICD
  • Maximo II CRT-D and ICD
  • Mirro ICD
  • Nayamed ND ICD
  • Primo ICD
  • Protecta ICD and CRT-D
  • Secura ICD
  • Virtuoso ICD
  • Virtuoso II ICD
  • Visia AF ICD
  • Viva CRT-D

Medtronic has implemented additional controls for monitoring and responding to any cases of improper use of the telemetry protocol used by affected ICDs. Further mitigations will be applied to vulnerable devices through future updates.

In the meantime, users of the devices should ensure home monitors and programmers cannot be accessed by unauthorized individuals and home monitors should only be used in private environments. Only home monitors, programmers, and ICDs that have been supplied by healthcare providers or Medtronic representatives should be used.

Unapproved devices should not be connected to monitors through USB ports and physical connections and programmers should only be used to connect with ICDs in hospital and clinical environments.

The vulnerabilities were identified by multiple security researchers who reported them to NCCIC. (Peter Morgan of Clever Security; Dave Singelée and Bart Preneel of KU Leuven; former KU Leuven researcher Eduard Marin; Flavio D. Garcia; Tom Chothia; and Rik Willems.

The post Critical Vulnerability Affects Medtronic CareLink Monitors, Programmers, and ICDs appeared first on HIPAA Journal.