HIPAA Breach News

Denver Health Medical Plan Discloses Vendor Breach Affecting 238K Members

Denver Health Medical Plan has notified more than 238,000 individuals about a vendor-related data incident. Data breaches have also been announced by Johns Hopkins Bayview Medical Center and BASS Medical Group.

Denver Health Medical Plan

Denver Health Medical Plan, a Denver, Colorado-based non-profit health plan affiliated with the Denver Health and Hospital Authority, has recently disclosed a data breach involving the protected health information of 238,083 current and former plan members. The incident involved SquareML, the provider of an artificial intelligence and machine learning analytics platform. On August 14, 2026, Denver Health Medical Plan was notified that an access key used by the vendor was found on a public website. The access key could have been used to access a database maintained by its vendor that contained plan members’ information.

The key had inadvertently been added to a public website by the vendor on June 27, 2025, where it remained for more than a year. The access key was deactivated on August 18, 2026. Data exposed in the incident included full names, city/state/zip code, demographic information, dates of birth, health plan eligibility information, provider names, admission/discharge/transfer information, and health metrics such as BMI, HbA1c, and eGFR. Financial information and Social Security numbers were not exposed.

Denver Health Medical Plan said it has not identified any evidence that the key had been misused. If the access key was found and used, it would not have been possible to download, export, delete, or alter data, and the key only provided read-only access.  While the data breach involved SquareML, notification letters have been mailed to the affected individuals by Denver Health Medical Plan.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

Johns Hopkins Bayview Medical Center

Johns Hopkins Bayview Medical Center in Baltimore, Maryland, has discovered that the protected health information of 3,182 patients may have been exposed in an AI-related incident. A member of staff uploaded a spreadsheet containing limited patient data to a public AI tool that had not been approved for use by staff members. The error was identified by the medical center on September 21, 2026. The spreadsheet contained information on patients who had been admitted and treated between May 2026 and September 2026, including names, admission/treatment dates, department information, account numbers, medical record numbers, medications, and treating provider names.

When the incident was detected, the employee deleted the AI prompt and thread and removed the spreadsheet from the tool’s history. The medical center also contacted the provider of the tool and requested the data be deleted from the system. As a precaution against any data misuse, the affected individuals have been offered complimentary credit monitoring services for 12 months, and steps have been taken to prevent similar incidents in the future, including providing additional training to staff members on the AI platforms permitted for staff use.

BASS Medical Group

BASS Medical Group, a physician-owned multi-specialty practice based in Walnut Creek, California, has notified the California Attorney General about a data security incident first identified on September 4, 2026. An investigation was launched to determine the cause of suspicious network activity, and on September 22, 2026, the investigation determined that there had been unauthorized access to its network and personal and/or protected health information had been exposed and may have been viewed or acquired by an unauthorized third party.

The information that may have been compromised was limited to medical treatment codes, billing information, and health insurance information. BASS Medical Group has implemented additional safeguards to prevent similar incidents in the future. Notification letters started to be mailed to the affected individuals on October 22, 2026. The number of affected individuals has not yet been publicly disclosed.

The post Denver Health Medical Plan Discloses Vendor Breach Affecting 238K Members appeared first on The HIPAA Journal.

UltraMobile Imaging Identifies Data Breach Impacting 75,000 Individuals

Data breaches have been announced by UltraMobile Imaging in New York, Artistic Smiles in Colorado, Parkview Health in Indiana, and Cognitive Behavior Therapy Center in Virginia.

UltraMobile Imaging, New York

UltraMobile Imaging, a Rochester, New York-based mobile medical diagnostic service provider, has determined that the protected health information of 75,000 individuals was exposed in a data security incident earlier this year. A network disruption was experienced on July 30, 2026, impacting some of its computer systems. Third-party digital forensics experts were engaged to investigate the nature and scope of the incident and confirmed that there was unauthorized access to parts of its network for a limited time. The UltraMobile Imaging website breach notice does not state when its network was first compromised.

UltraMobile Imaging has determined that the information likely exposed in the incident included names, addresses, phone numbers, dates of birth, gender information, diagnoses, lab test results, medications, dates of service, study IDs, procedure types, CPT codes, ordering physician names, claims information, facility names, and financial account information. The affected individuals are now being notified. Credit monitoring services do not appear to have been offered.

Artistic Smiles, Colorado

Lift Dental PLLC, the operator of a dental practice in Longmont, Colorado called Artistic Smiles, has identified unauthorized access to its computer systems. The intrusion was identified on or around June 21, 2026, and the forensic investigation determined that an unauthorized third party had access to its network between June 14, 2026, and June 21, 2026.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The data review determined that the information exposed in the incident included names, addresses, dates of birth, and medical and dental treatment information. The data breach was recently reported to the HHS’ Office for Civil Rights as affecting 3,735 individuals. It is not clear if ransomware was involved; however, a ransomware group called Nightspire claimed responsibility for the incident and added Artistic Smiles to its dark web data leak site.

Parkview Health, Indiana

Parkview Health in Fort Wayne, Indiana, is investigating a potential cybersecurity incident. On October 19, 2026, the nonprofit community health system said it recently identified suspicious network activity and experienced a network-wide internet outage that prevented access to the MyChart portal and other online services. Without access to those systems, it was unable to issue appointment reminders.

The MyChart portal and Find a Doctor service have now been restored and can be used again by patients, although video visits are still not available and billing functions have yet to be restored. Staff are working to restore the remaining services as quickly as possible.  Parkview Health has not publicly confirmed if patient data was exposed or stolen.

Cognitive Behavior Therapy Center, Virginia

Cognitive Behavior Therapy Center in Chesapeake, Virginia, has been affected by a security incident at one of its third-party vendors – Express Billing Systems. The third-party billing company discovered unauthorized access to its computer network on August 24, 2026, and determined that files containing patient information were copied in the incident. The review of the impacted data confirmed that names, addresses, phone numbers, Social Security numbers, diagnoses, and information related to the services provided. Approximately 1,500 Cognitive Behavior Therapy Center patients are affected.

This was a data theft and extortion incident, and some patients have been contacted directly by the threat actor in an attempt to extort money. Express Billing Systems said it has taken steps to strengthen security to prevent similar incidents in the future and is providing additional training to its staff to help them identify phishing attempts and maintain security.

The post UltraMobile Imaging Identifies Data Breach Impacting 75,000 Individuals appeared first on The HIPAA Journal.

Patient Data Likely Accessed in Quest Diagnostics Hack

Quest Diagnostics, a Secaucus, New Jersey-based Fortune 500 diagnostic testing company, has notified the U.S. Securities and Exchange Commission (SEC) that it has identified unauthorized access to its Quantum Lab Services Manager (LSM) system and suspects patient records have likely been compromised. The scale of the data breach has yet to be determined. No threat group appears to have claimed responsibility for the intrusion.

In its October 22, 2026, Form 8-K filing, the company said the unauthorized access was first identified on October 21, 2026. An investigation has been launched to determine the nature and scope of the unauthorized activity, although the incident appears to be limited to its LSM system, which is used by certain clients to place test orders and receive and look up test results.

Upon detection, the company initiated its incident response protocol to contain the activity, and remedial measures have been implemented to prevent further unauthorized access. Third-party cybersecurity experts have been engaged to assist with the investigation, and federal law enforcement authorities have been notified. The incident has not affected the company’s ability to serve patients or impacted its business operations. Quest Diagnostics explained in a website notice that it temporarily paused access to the LSM system while the incident is investigated. Customers can continue to place orders and receive test results via fax, paper, or direct-customer LIS interfaces or EMRs.

Quest Diagnostics is one of the largest clinical diagnostic laboratory companies in the United States. The company operates more than 7,700 patient access points in North America, including around 2,000 patient service centers in 51 U.S. states and territories. The company serves around one-third of adult Americans, half of U.S. physicians and hospitals, and has around $11 billion in annual revenue.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The company has experienced a major data breach in the past via its debt collection vendor, American Medical Collections Agency (AMCA). Hackers breached AMCA systems between August 2018 and March 2019 and gained access to the protected health information of approximately 11.9 million Quest Diagnostics patients.  While Quest Diagnostics has confirmed that patient records were accessed in the latest incident, it is unlikely to be on a similar scale, as only certain customers use the impacted system. Quest Diagnostics will release further information on the incident as the investigation progresses.

The post Patient Data Likely Accessed in Quest Diagnostics Hack appeared first on The HIPAA Journal.

Data Breach at Manhattan Law Firm Involved PHI of 197,000 Individuals

The law firm Tarter Krinsky & Drogin has reported a breach of the protected health information of 196,645 patients of its healthcare clients. Data breaches have also been announced by Park Dental in Virginia and Heritage Pediatrics in Texas.

Tarter Krinsky & Drogin

A data breach has been announced by the Manhattan, New York-based law firm Tarter Krinsky & Drogin, which involved confidential and attorney-client privileged information and the protected health information of 196,645 patients of its healthcare clients. Suspicious activity was identified within its computer environment on September 10, 2025. Third-party digital forensics specialists were engaged to investigate the activity and confirmed that an unauthorized third party accessed some of its servers intermittently between July 9, 2025, and September 9, 2025. During that time, certain files on the servers were accessed or acquired.

The review of the affected files has recently been completed, and notification letters are now being mailed to the affected individuals. The types of data involved varied from individual to individual and may include some or all of the following: name, Social Security number, driver’s license number, date of birth, international tax identification number, passport number, tax identification number/individual tax identification number, financial account information, payment card information, username & password, medical information, health insurance information, and biometric data. The law firm has reviewed its security policies and procedures and implemented additional cybersecurity measures to prevent similar incidents in the future.

Young C. Park DDS (Park Dental)

Young C. Park DDS, PC, the operator of Park Dental in Roanoke, Virginia, has reported a data breach to the HHS’ Office for Civil Rights that has affected approximately 12,000 individuals. The practice learned that an unauthorized third party gained access to a workstation and an associate office email account. The unauthorized access occurred intermittently between June 10, 2026, and July 22, 2026, when the unauthorized access was identified.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The investigation confirmed that email accounts had been subject to unauthorized access, and potentially there was unauthorized access to patient records. Data exposed in the incident included names, addresses, phone numbers, email addresses, birth dates, patient charts/record numbers, appointment information, provider names, referral information and communications, x-rays and related imaging, diagnoses, treatment plans and notes, and insurance and billing information. Park Dental has strengthened account and remote access security, increased monitoring, changed passwords and updated access privileges, reinforced its data privacy and security practices, and identified additional areas for further employee training.

Heritage Pediatrics

Heritage Pediatrics PLLC in San Antonio, Texas, has started notifying individuals affected by an April 2026 email security incident. The pediatric medical practice identified fraudulent emails being sent from an employee’s email account. The account was immediately secured, and an investigation was launched to determine the extent of the compromise and the nature of data exposed in the incident. Third-party cybersecurity experts were engaged to assist with the investigation and confirmed that a single email account had been compromised. The account was reviewed and found to contain patient data.

The data involved varied from individual to individual and may have included names in combination with some or all of the following: contact information, Social Security number, date of birth, driver’s license number/state identification number, passport number, financial account information, debit/credit card information, health insurance information, clinical information, diagnosis information, treatment information, treatment/procedure codes, medical record number, and health insurance information. The affected individuals were notified on or around October 19, 2026. At the time of issuing notifications, no misuse of the exposed data had been identified.

The post Data Breach at Manhattan Law Firm Involved PHI of 197,000 Individuals appeared first on The HIPAA Journal.

Ridgeway Pharmacy Data Breach Affects 259,000 Individuals

A data breach at Ridgeway Pharmacy in Montana has affected almost 259,000 individuals. Data breaches have also been announced by IMS Care Center in Arizona and Persona Dental in Minnesota.

Ridgeway Pharmacy

Ridgeway Pharmacy Ltd, a Victor, Montana-based mail order and community pharmacy, has identified a data security incident involving its website that exposed the personal and protected health information of 258,920 of its customers.

Ridgeway Pharmacy said that on August 21, 2026, it became aware that personal information had been exposed via its third-party designed and developed website. An investigation was launched to determine the extent of the unauthorized access, with assistance provided by third-party digital forensics experts. They confirmed that the incident was limited to its website, and no internal systems were involved. Data potentially compromised in the incident included names, addresses, dates of birth, prescription information, health information, and insurance information. A subset of individuals also had payment card information exposed.

In response to the incident, Ridgeway Pharmacy has reviewed its third-party website maintenance and data security arrangements and has implemented additional security protections to prevent similar incidents in the future. They include switching to a new website platform, restricting access, and strengthening monitoring. As a precaution against data misuse, the affected individuals have been offered complimentary credit monitoring and identity theft protection services.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

IMS Care Center

IMS Care Center, a Phoenix, Arizona-based physician-owned multi-specialty medical practice, has identified unauthorized access to its email environment. Suspicious activity was identified on June 18, 2026. Its email system was secured, and an investigation was launched to determine the nature and scope of the unauthorized activity.

The investigation confirmed that an unauthorized third party accessed its email system between June 17, 2026, and June 18, 2026. The affected email accounts were reviewed, and on September 30, 2026, IMS Care Center confirmed that patient names, addresses, Social Security numbers, and medical information had been exposed. Notification letters were mailed to the affected individuals on October 16, 2026, and at least 12 months of complimentary credit monitoring and identity theft protection services have been offered to the affected individuals.

IMS Care Center said several steps have been taken to improve email security, including implementing new technical safeguards, Sophos MDR, geographical restrictions on email access, enhanced phishing training for the workforce, updated data privacy and security policies and procedures, and it has committed to periodic technical and nontechnical evaluations. The incident has been reported to state attorneys general and the HHS’ Office for Civil Rights; however, it has yet to be added to the OCR breach portal, so it is unclear how many individuals have been affected.

Persona Dental

Persona Dental, a Sartell, Minnesota-based family and cosmetic dental practice, has announced a data security incident that has affected 3,386 current and former patients.  Suspicious activity was identified within its computer network on or around April 30, 2026. The forensic investigation determined that its network had been accessed by an unauthorized third party between April 28, 2026, and April 30, 2026.

Its network was secured, and additional security measures have been implemented to prevent similar incidents in the future. The review of the affected files has recently been completed, and it has been confirmed that patient data such as names, dates of birth, diagnosis and treatment information, and health insurance information were involved. For certain patients, Social Security numbers were involved. Notification letters started to be mailed to the affected individuals on September 9, 2026, and individuals who had their Social Security numbers exposed have been offered complimentary credit monitoring services.

The post Ridgeway Pharmacy Data Breach Affects 259,000 Individuals appeared first on The HIPAA Journal.

Central Ohio Primary Care Physicians Data Breach Affects 1.4 Million Patients

Central Ohio Primary Care Physicians, one of the largest independent physician-owned primary care medical groups in the United States, has experienced a cybersecurity incident that involved the personal and protected health information of approximately 1.4 million current and former patients, according to local media reports.

The Westerville, Ohio-based medical group, which has more than 80 locations in Central Ohio, experienced a voice phishing (vishing) attack in August 2026 that resulted in unauthorized third-party obtaining credentials that provided access to internal systems. The unauthorized access was detected and blocked on August 25, 2026.

The investigation into the incident confirmed that files containing patient information were exfiltrated in the incident. The files have now been reviewed and found to contain patient names, addresses, Social Security numbers, financial information, health information, and other identifying information.

Notification letters are being mailed to the affected individuals, and complimentary credit monitoring, identity theft protection, and dark web monitoring services are being made available. Central Ohio Primary Care Physicians said it has not detected any misuse of patient information as a result of the incident at the time of issuing notification letters. Central Ohio Primary Care Physicians said it takes data privacy and security seriously and had implemented appropriate security measures prior to the incident. Security has since been enhanced to reduce the risk of similar incidents in the future.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The threat group behind the attack was not disclosed in the breach notices; however, it appears to be a ransomware group called Chaos. The group added Central Ohio Primary Care Physicians to its dark web data leak site and threatened to publish the stolen data if payment was not made. The group claimed that contact had not been made at the time of the listing, but Central Ohio Primary Care Physicians is no longer listed on the site.

The post Central Ohio Primary Care Physicians Data Breach Affects 1.4 Million Patients appeared first on The HIPAA Journal.

Mid Florida Dermatology & Plastic Surgery Data Breach Affects 85K Patients

Data breaches have been announced by Mid Florida Dermatology & Plastic Surgery, Kannarr Eye Care in Kansas, and Indiana University Health Affiliated Covered Entity.

Mid Florida Dermatology & Plastic Surgery

Mid Florida Dermatology & Plastic Surgery, a medical group with 33 locations in central Florida, has notified the HHS’ Office for Civil Rights about a data breach affecting 85,585 individuals. According to a September 10, 2026, notice on the medical group’s website, unusual activity was identified within its computer systems on March 30, 2026. The forensic investigation determined that an unauthorized third party had access to its network from March 26, 2026, to March 30, 2026, during which time files containing patient data may have been viewed or acquired.

The data review determined that the information potentially accessed or obtained included names, addresses, dates of birth, passport numbers, Social Security numbers, driver’s license numbers, Medicare numbers, other government identification numbers, financial account numbers, financial account access information, health insurance information, and medical information. The types of information involved varied from individual to individual. Mid Florida Dermatology & Plastic Surgery said it is reviewing its security policies and procedures and is taking steps to reduce the risk of similar incidents in the future.

Kannarr Eye Care

Kannarr Eye Care, an optometry practice based in Pittsburg, Kansas, has identified unauthorized access to its computer systems. The incident was identified on March 30, 2026, and the forensic investigation determined that an unauthorized third party accessed or acquired files containing patients’ personal and protected health information.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

A review of the affected data was completed on August 17, 2026, confirming that names, Social Security numbers, and health insurance information were involved. Kannarr Eye Care has enhanced its security measures, implemented additional technical safeguards, and strengthened its policies and procedures related to data privacy and security to reduce the risk of similar incidents in the future. Notification letters were mailed to the affected individuals on September 17, 2026. The data breach was reported to the HHS’ Office for Civil Rights as affecting 14,003 individuals.

Indiana University Health, Affiliated Covered Entity

Indiana University Health Affiliated Covered Entity, has disclosed a security incident that has affected 2,080 individuals. The incident involved one of its vendors, AME Group. AME Group provides information technology services for an isolated IU Health legacy system. IU Health learned on August 4, 2026, that a previously unknown security vulnerability was susceptible to exploitation. Steps were immediately taken to verify the security of its systems, and while it was established that its core systems and electronic medical records were unaffected, a review of AME’s external vendor-managed system confirmed that there had been unauthorized access to limited imaging center information related to patients in Southern Indiana.

The information involved varied from individual to individual and may have included names, birth dates, health plan ID numbers, and limited treatment information related to the imaging center. The affected individuals were notified on September 29, 2026.

The post Mid Florida Dermatology & Plastic Surgery Data Breach Affects 85K Patients appeared first on The HIPAA Journal.

July 2026 Healthcare Data Breach Report

In July 2026, 77 healthcare data breaches affecting 500 or more individuals were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights. July was the third consecutive month in which large healthcare data breaches increased, with a month-over-month increase of 10%.
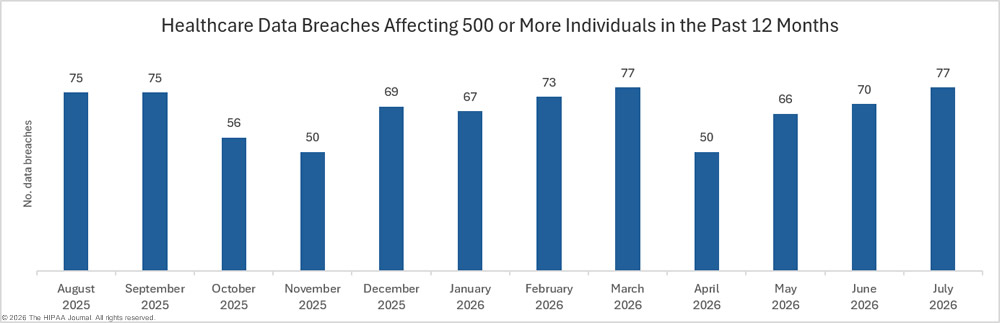
Large U.S. Healthcare data breaches in the past 12 months - July 2026

Last year was a record-breaking year for healthcare data breaches. The OCR data breach portal currently shows 806 large healthcare data breaches in 2025 – an increase of 8.6% from 2024. While 2026 was looking like there would be a fall in large healthcare data breaches, the year-to-date figures now suggest otherwise. The exact same number of data breaches are listed on the OCR data breach portal for January to July as this time in 2025, and it is likely that some breaches have yet to be added to the portal.
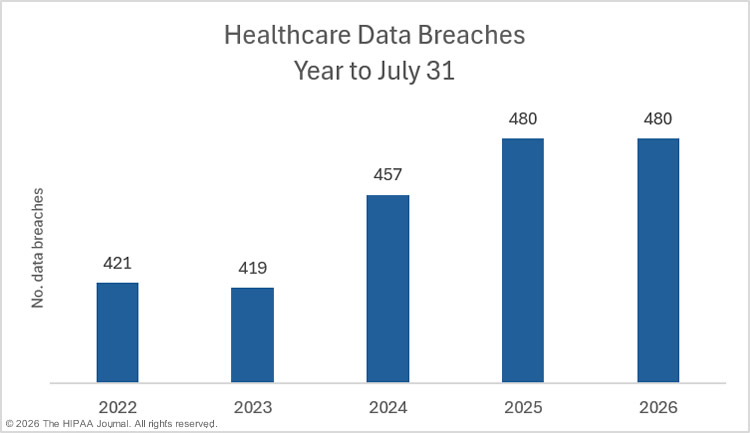
Year-to-date large healthcare data breaches - July 31, 2026

July was the worst month since October 2025 in terms of individuals affected by healthcare data breaches. Across the 77 large data breaches, the protected health information of at least 33,485,970 individuals was exposed or impermissibly disclosed – an increase of 642% from June 2026, and 154% higher than the 12-month average of 13.2 million individuals per month.
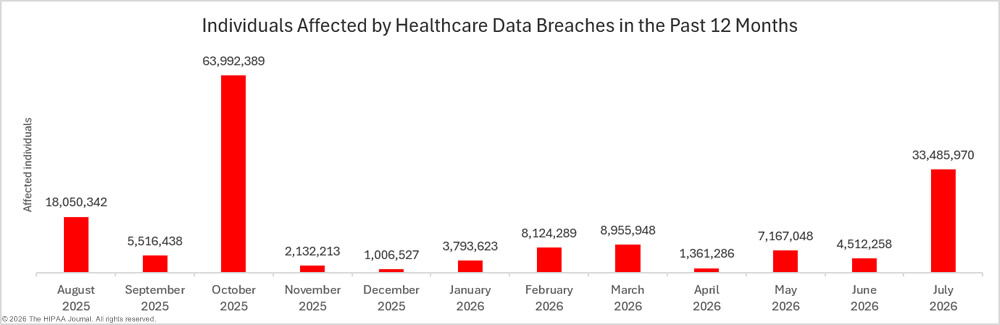
Individuals affected by large U.S. healthcare data breaches in the past 12 months - July 2026

The year-to-date figures show an increase in breach severity year-over-year. Between January and July 2026, the protected health information of 67,400,422 individuals was exposed or impermissibly disclosed; an increase of 35.1% from this time last year.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy
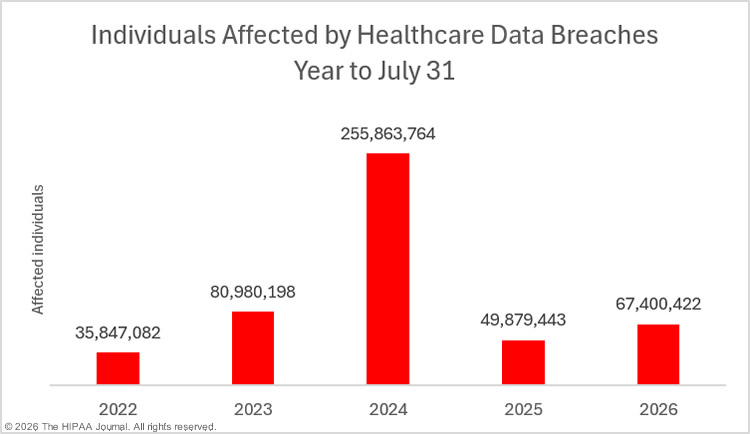
Year to date individuals affected by large U.S. healthcare data breaches - July 31, 2026

Biggest Healthcare Data Breaches in July 2026

In July, 23 security incidents were reported to OCR involving the protected health information of 10,000 or more individuals, including four very large data breaches that each affected more than 1 million individuals. One of the incidents was the 4th largest healthcare data breach of all time to be reported by a single HIPAA-regulated entity, affecting an estimated 15 million individuals. The four biggest healthcare data breaches in July affected more than 32 million individuals – more than 9% of the population of the United States.

The largest data breach occurred at DentaQuest, a Sun Life U.S-owned dental and vision benefits administrator, which fell victim to a cyberattack by the notorious data theft and extortion group ShinyHunters. In early June 2026, DentaQuest announced that it was investigating a cybersecurity incident involving a limited part of its computer network. The threat group had access to its network for around 3 days in May 2026. ShinyHunters claimed responsibility and said 234 GB of data was exfiltrated in the incident, then started leaking the stolen data as it failed to reach an agreement with DentaQuest on a ransom payment. The leak included around 2.6 million unique email addresses, and the breach was reported to OCR as affecting an estimated 15 million individuals. That total may increase as the investigation progresses.

The next three largest data breaches all occurred at business associates of HIPAA-covered entities. Aesto Health, a healthcare technology company that offers secure data migration, legacy data archiving, and electronic health record (EHR) exchanges, experienced a hacking incident that affected at least 39 of its healthcare clients and involved the protected health information of more than 9.5 million individuals. The incident occurred in December 2025 and involved unauthorized access to its AWS environment. No threat group appears to have claimed responsibility.

Unlimited Technology Systems, an Ohio-based revenue cycle management and practice management software company, discovered its network had been accessed by an unauthorized third party for five days in October 2025, and potentially obtained the protected health information of more than 3.8 million individuals. A similar-sized data breach was reported by CareCloud, a provider of cloud-based and AI-powered EHR, RCM, PM, and clinical documentation solutions, which discovered that a threat actor accessed its AWS environment over 6 days in March 2026, and likely exfiltrated databases containing the protected health information of more than 3.7 million individuals. As with the incident at Unlimited Technology Systems, no threat group appears to have claimed responsibility.

Regulated Entity State Covered Entity Type Individuals Affected Cause of Breach
DentaQuest, LLC MA Health Plan 15,000,000 Hacking incident (ShinyHunters data theft and extortion group)
Aesto, LLC AL Business Associate 9,540,683 Hacking incident
Unlimited Technology Systems, LLC OH Business Associate 3,803,750 Hacking incident
CareCloud, Inc. NJ Business Associate 3,756,469 Hacking incident
Lifespan Physician Group of Massachusetts, Inc. d/b/a Brown Health Medical Group-MA MA Healthcare Provider 311,760 Hacking incident
One Medical Group, Inc. CA Healthcare Provider 153,174 Hacking incident (ShinyHunters data theft and extortion group)
Madera Community Hospital CA Healthcare Provider 150,810 Hacking incident
zHealth, Inc. CA Business Associate 118,563 Ransomware attack (Kazu ransomware group)
Boundary Regional Community Health Center dba Kaniksu Community Health ID Healthcare Provider 88,000 Hacking incident at business associate Aesto (see above)
A-O-M-S, P.L.L.C. d/b/a Arkansas Oral & Maxillofacial Surgeons AR Healthcare Provider 64,831 Hacking incident (PEAR data theft and extortion group)
Casper Orthopedic Associates, PC DC Healthcare Provider 56,197 Hacking incident
Heart Care Centers of Illinois IL Healthcare Provider 52,562 Email phishing incident
Sunshine Health FL Health Plan 41,569 Vishing (voice phishing) incident
Brookhaven ENT Allergy and Facial Surgery MS Healthcare Provider 30,403 Hacking incident at vendor CloudCare
Alta Orthopaedics Medical Group, Inc. PA Healthcare Provider 24,496 Ransomware attack (INC Ransom ransomware group)
Nephrology Associates, M.D., P.A. KS Healthcare Provider 24,088 Ransomware attack (The Gentlemen ransomware group)
Jeffrey David Reuben, M.D. TX Healthcare Provider 17,017 Hacking incident
Regional Center of Orange County CA Business Associate 16,545 Improper disposal of paper records by janitorial service provider
ZenPatient, Inc. CA Healthcare Provider 15,749 Hacking incident (data theft confirmed)
Cornerstone Behavioral Healthcare ME Healthcare Provider 14,830 Ransomware attack (Group unknown)
Resource Center of Dallas, Inc. TX Healthcare Provider 12,490 Hacking incident
Agave Dental-Floresville TX Healthcare Provider 11,790 Ransomware attack (The Gentlemen ransomware group)
Any-Time Home Care, Inc. NY Healthcare Provider 11,753 Hacking/IT Incident

When the number of affected individuals is not known by the HIPAA Breach Notification Rule reporting deadline, OCR should be provided with an estimate. The total can then be amended when the data review is completed. It is common for regulated entities to provide an “estimate” of 500 or 501 individuals, as appears to be the case with seven of the breaches reported in July.

Regulated Entity State Covered Entity Type Individuals Affected Type of Breach
Open Door Health Center of Illinois WA Healthcare Provider 501 Network server hacking incident (INC Ransom ransomware group)
Champaign-Urbana Public Health District IL Healthcare Provider 501 Network server hacking incident
The Medical Imaging Partnership dba Precision Imaging Center FL Healthcare Provider 501 Network server hacking incident
Interim HealthCare of Oklahoma City, Inc. OK Healthcare Provider 500 Email/network server hacking incident (Genesis & Anubis ransomware groups)
Pennsylvania Dermatology Partners MD Healthcare Provider 500 Network server hacking incident
Alpine Agency of the Midlands, LLC SC Business Associate 500 Email hacking incident
Family Medical Associates of Raleigh, PA NC Healthcare Provider 500 Network server hacking incident

Causes of June 2026 Healthcare Data Breaches

A majority of the data breaches reported in July were due to hacking and other IT-related incidents, including all but one of the 23 data breaches affecting 10,000 or more individuals. In July, 67 of the month’s data breaches (87%) were reported as hacking/IT-related incidents, involving the protected health information of 33,446,371 of the month’s affected individuals (99.9%). The average breach size was 499,200 individuals, and the median breach size was 4,851 individuals.
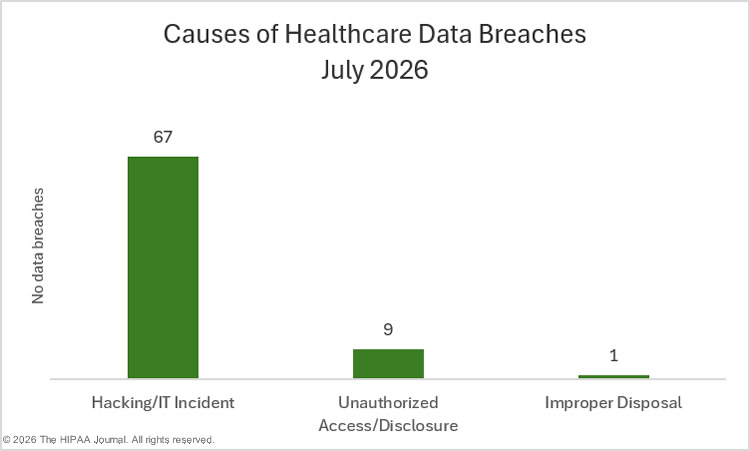
Causes of July 2026 large healthcare data breaches

Between January 1 and July 31, 414 hacking/IT incidents were reported – 86% of all data breaches – and they accounted for 97.8% of all affected individuals (65,89,1098 individuals). While the same number of healthcare data breaches have been reported as this time last year, hacking/IT incidents have increased by 7.3% year-over-year.

In July 2026, 9 of the month’s data breaches were reported as unauthorized access/disclosure incidents (11.7% of incidents), involving the protected health information of 23,054 of the month’s affected individuals (0.07%). The average breach size was 2,562 individuals, and the median breach size was 1,680 individuals. Between January 1 and July 31, 62 unauthorized access/disclosure incidents were reported – 12.9% of all data breaches – and they accounted for 2.2% of all affected individuals (1,490,420 individuals). Unauthorized access/disclosure incidents have decreased by 27% year-over-year.

In July 2026, only one of the month’s data breaches was due to the improper disposal of protected health information (1.3%), and that incident affected 16,545 individuals (0.05%). Between January 1 and July 31, 2 improper disposal incidents were reported – 2.6% of all data breaches – and they accounted for 0.03% of all affected individuals (17,545 individuals). Improper disposal incidents have doubled year-over-year.

No loss/theft incidents were reported in July. Between January 1 and July 31, only 2 loss/theft incidents were reported – 0.4% of all data breaches – and they accounted for 0.002% of all affected individuals (1,359 individuals). Loss/theft incidents have decreased by 400% year-over-year.

Location of Breached Protected Health Information

In July, network servers were the most common location of breached protected health information, followed by email systems.
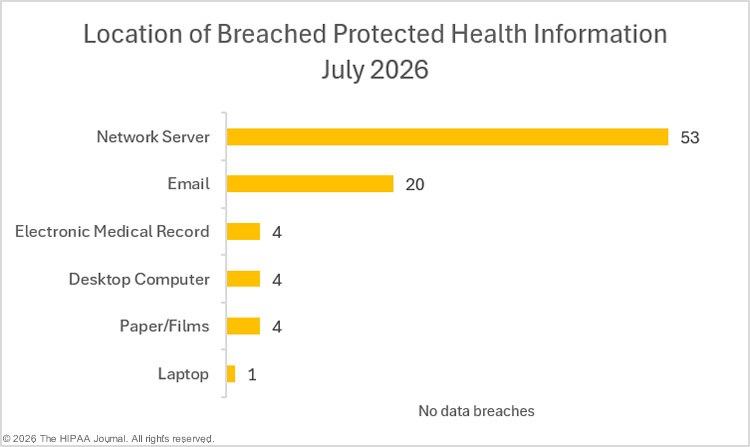
Location of breached PHI in July 2026 healthcare data breaches

Data Breaches at HIPAA Regulated Entities

The HIPAA Breach Notification Rule requires HIPAA-covered entities to report data breaches to OCR and notify the affected individuals. Notifications must also be issued when there is a data breach at a business associate of a HIPAA-covered entity; however, it is ultimately the responsibility of each affected HIPAA-covered entity to ensure that notifications are issued. A covered entity may delegate the reporting requirements to the business associate that experienced the data breach, or may choose to issue notifications themselves. The raw breach data on the OCR breach portal shows data breaches based on the reporting entity, not where the data breach occurred.

In July, healthcare providers reported 56 data breaches, business associates reported 12 breaches, and 9 breaches were reported by health plans. The pie charts below show where the breach actually occurred rather than the reporting entity to better reflect data breaches at business associates.
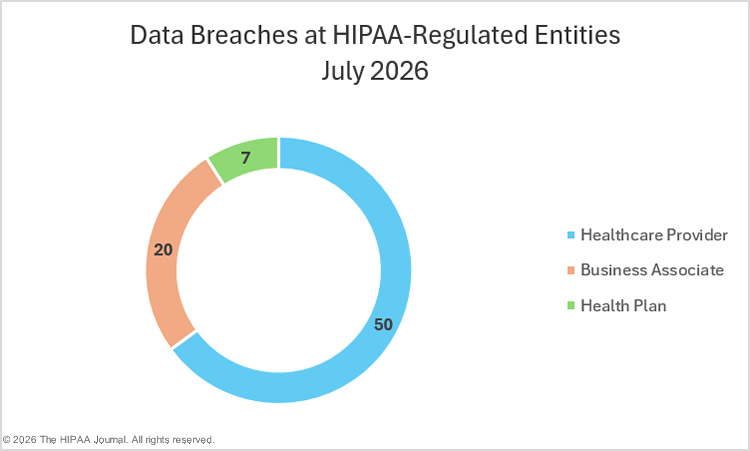
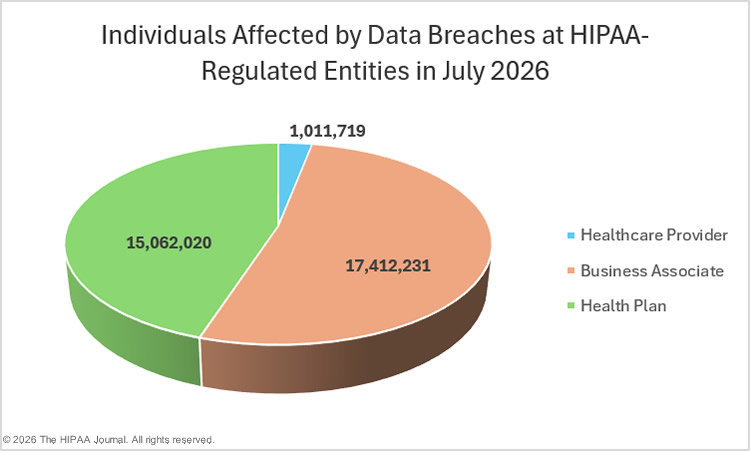
July 2026 large U.S. healthcare data breaches - regulated entities

individuals affected by large U.S. healthcare data breaches - July 2026

Geographical Distribution of Healthcare Data Breaches

In July, large healthcare data breaches were reported to OCR by HIPAA-regulated entities in 30 U.S. states and the District of Columbia. Texas was the worst affected state with 11 large data breaches, closely followed by California with nine.

State Breaches State Breaches
Texas 11 Arizona 1
California 9 Connecticut 1
Florida 5 District of Columbia 1
Massachusetts 5 Idaho 1
Illinois 4 Indiana 1
Minnesota 4 Iowa 1
New York 4 Kansas 1
North Carolina 4 Maine 1
Tennessee 3 Maryland 1
Wisconsin 3 Mississippi 1
Arkansas 2 Oklahoma 1
Michigan 2 Pennsylvania 1
New Jersey 2 South Carolina 1
Ohio 2 Virginia 1
Alabama 1 Washington 1

Massachusetts topped the list in terms of affected individuals, with more than 18 million individuals affected across its five data breaches, followed by Alabama, which experienced one data breach that affected more than 9.5 million individuals across the United States.

State Individuals Affected State Individuals Affected
Massachusetts 15,317,249 Wisconsin 18,549
Alabama 9,540,683 Minnesota 15,398
Ohio 3,805,854 Maine 14,830
New Jersey 3,759,869 Virginia 9,909
California 478,468 Tennessee 9,835
Idaho 88,000 Michigan 5,707
Texas 71,136 North Carolina 4,493
Arkansas 65,520 West Virginia 2,173
Florida 60,164 Connecticut 1,556
Illinois 56,638 Indiana 1,530
District of Columbia 56,197 Arizona 800
Mississippi 30,403 Iowa 746
Pennsylvania 24,496 Washington 501
Kansas 24,088 Maryland 500
New York 19,678 Oklahoma 500

HIPAA Enforcement Activity in July 2026

OCR announced one HIPAA enforcement action in July to resolve alleged violations of the HIPAA Rules. OSF Healthcare System is a Peoria, Illinois-based integrated health system that serves patients at 174 locations in Illinois and Michigan, including 16 hospitals. OSF Healthcare System was investigated by OCR in response to a reported cybersecurity incident that exposed the protected health information of 53,907 individuals. A ransomware group breached its network, stole patient data, encrypted files, and demanded payment to delete the stolen data and unlock the encrypted files. The attack was discovered by OSF Healthcare System in April 2021.

OCR’s investigators determined OSF Healthcare System failed to conduct a HIPAA-compliant risk analysis, there was an impermissible disclosure of the ePHI of 53,907 individuals, and a failure to provide timely notifications to OCR and the affected individuals. The alleged HIPAA violations were settled, with OSF Healthcare System and its Affiliated Covered Entities agreeing to pay a $552,250 financial penalty and adopt a corrective action plan to address the identified areas of noncompliance.

This was another enforcement action under OCR’s risk analysis enforcement initiative. While OCR has not announced a specific enforcement initiative targeting noncompliance with the HIPAA Breach Notification Rule, OCR appears to be looking closely at HIPAA Breach Notification Rule compliance. Since the start of 2025, eight HIPAA settlements have included penalties for Breach Notification Rule failures.

About this Report

The HIPAA Journal monthly data breach reports are based on data obtained from the HHS Office for Civil Rights and have been combined with breach report data from other sources. The data breaches included in this report were reported in July 2026 but occurred weeks or months previously. The data was obtained from OCR on October 10, 2026. The figures in this report may increase or decrease as HIPAA-regulated entities complete their breach investigations, and those changes will be reflected in our healthcare data breach statistics page and our annual HIPAA data breach reports. Further information about HIPAA enforcement actions can be found in our HIPAA violations cases page.

The post July 2026 Healthcare Data Breach Report appeared first on The HIPAA Journal.
Photon Health; Healthcare Highways Announce Data Security Incidents

Data breaches have been announced by the New York-based healthcare technology company Photon Health, the Texas-based medical provider network company Healthcare Highways, and the New York-based home health agency Any-Time Home Care.

Photon Health

Photon Health, a Brooklyn, New York-based healthcare technology company that operates a prescription network, has disclosed a cybersecurity incident involving unauthorized access to patient data. Photon Health learned on August 21, 2026, that a previously unknown security flaw in a self-hosted third-party application called Metabase had been exploited.

Metabase was used by Photon Health for business intelligence, product metrics, and customer dashboards. The threat actor exploited the zero-day vulnerability and gained access to stored data, which was potentially exfiltrated. Photon Health completed its data review on September 4, 2026, when it was confirmed that data compromised in the incident included names, addresses, phone numbers, birth dates, and prescription information. Notification letters started to be mailed to the affected individuals on October 8, 2026. At the time of issuing notification letters, Photon Health was unaware of any misuse of the impacted data. The Direwolf ransomware and data extortion group claimed responsibility for the attack.

The company has not yet publicly disclosed how many of its clients have been affected or the total number of individuals who had their data exposed in the incident, but has confirmed that complimentary credit monitoring and identity theft protection services have been offered to the affected individuals. Photon Health also confirmed that it is reviewing its cybersecurity measures and is taking steps to prevent similar incidents in the future.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

Healthcare Highways

Healthcare Highways, a Frisco, Texas-based medical provider network company and health plan administrator, has recently disclosed a cybersecurity incident that was first identified on August 4, 2026. An investigation was launched to determine the nature and scope of the activity, which confirmed that an unauthorized third party had access to its network between July 22, 2026, and July 27, 2026. During that time, the protected health information of certain individuals was accessed and acquired.

The review of the affected data is ongoing; however, it has been determined that the types of data compromised in the incident include names, addresses, dates of birth, dates of service, Social Security numbers, patient ID numbers, procedure codes and costs, procedure/provider information, diagnoses, claims information, health insurance information, and information related to payment for healthcare services.

Healthcare Highways has yet to publicly disclose the total number of individuals affected by the incident. While the group behind the attack was not disclosed, the Chaos ransomware group claimed responsibility and says it exfiltrated 235 GB of data.

Any-Time Home Care

The New York-based home health agency Any-Time Home Care has recently disclosed a ransomware attack that was identified in March 2026. The forensic investigation determined that an unauthorized third party first accessed its network on or around March 17, 2026, and encrypted files. Files on the compromised parts of its network have been reviewed and found to contain names, addresses, birth dates, health information, and Social Security numbers. In total, 30,017 individuals have been affected by the incident. The affected individuals have been offered 24 months of complimentary credit monitoring and identity theft protection services.

The post Photon Health; Healthcare Highways Announce Data Security Incidents appeared first on The HIPAA Journal.