Healthcare Cybersecurity

Misconfigured Public Cloud Databases are Found and Attacked Within Hours

Misconfigured public cloud databases are often discovered by security researchers. Misconfigurations that leave cloud data exposed could be due to a lack of understanding about cloud security or policies, poor oversight to identify errors, or negligent behavior by insiders to name but a few. A recent report from Trend Micro revealed cloud misconfigurations were the number one cause of cloud security issues.

Security researchers at Comparitech often discover unsecured cloud resources, commonly Elasticsearch instances and unsecured AWS S3 buckets. When the unsecured cloud databases are discovered, the owners are identified and notified to ensure data is secured quickly. Providing the owner can be identified, the databases are usually secured within a matter of hours, but there have been several cases where the database owner has been contacted but no response is received, and it is not always apparent to whom the data belongs.

In these cases, data can be left exposed online for several days or even weeks. During that time, the databases remain unprotected and can be accessed and downloaded by anyone that knows where to find them. Comparitech researchers are well practiced at finding unsecured Elasticsearch databases and AWS S3 buckets, but how quickly can malicious actors sniff out an unsecured database? Comparitech decided to find out. It turns out that it does not take long.

To determine the time it takes for unsecured data to be found, Comparitech’s security team conducted an exercise where they created a simulation of an Elasticsearch instance, similar to the many Elasticsearch instances they have found unsecured. They populated it with fake user data and left it exposed without any access controls. The database was exposed from May 11, 2020 to May 22, 2020.

In a recent blog post detailing the exercise, Comparitech security researcher Paul Bischoff explained that the first access request occurred 8 hours and 35 minutes after the database was created. During the 11 days that the database was exposed, there were 175 access requests. Their honeypot averaged 18 requests a day.

Exposed databases are usually located using an IoT search engine such as Shodan. It takes time for the data to be indexed by the search engines, in this case, Shodan indexed the database on May 16, five days after the database was created. Even though the database was not indexed until May 16, by the time it was there had been 3 dozen attempts to access the data. As soon as the database was indexed, the attacks spiked. Two access attempts were made within a minute of the database being indexed, with a further 20 access requests made that same day.

There are several reasons why attempts are made to find unsecured cloud resources. Databases often contain sensitive data, which can be used for identity theft and fraud or sold on underground forums. Databases can be hijacked and ransom demands issued to extort money from the data owners, but not all attacks were concerned with obtaining data. Several attempts were made to hijack the servers and download cryptomining scripts. In one case, an attacker attempted to switch off the firewall and delete the database.

While the test was concluded on May 22, 2020 and the data was mostly deleted, an further attack occurred on May 29. A malicious bot detected the honeypot and deleted the database, leaving a message demanding payment of 0.06 BTC to recover the data. That attack took 5 seconds from start to finish.

The exercise showed that even if databases are only exposed for a short period of time, it is highly likely that they will be found. While many companies say their data was not left unsecured for long when they are notified by Comparitech of an exposed cloud instance, it is probable that data has already been compromised unless data was only exposed for a few hours.

Comparitech pointed out that if the person setting up an Elasticsearch instance fails to put access controls in place, it is reasonable to assume that logging has also not been enabled. When companies report that no evidence was found to suggest data was accessed or exfiltrated, that does not mean data has not been accessed and stolen, only that there is a lack of evidence.   A 2019 report from McAfee suggested 99% of misconfigurations in the cloud go unreported when they are discovered. It is probable that data theft from cloud resources is far more likely than breach reports would lead you to believe.

The post Misconfigured Public Cloud Databases are Found and Attacked Within Hours appeared first on HIPAA Journal.
Attacks on Cloud Services Increased by 630% Between January and April

COVID-19 has forced businesses to close their offices and allow employees to work from home. Cloud services have been provisioned to support home working and communication solutions such as Zoom, Cisco WebEx, and Microsoft Teams have allowed remote workers in collaborate effectively.

A recently published report from cybersecurity company McAfee shows business use of cloud services increased by 50% in the first 4 months of 2020 and collaboration services saw an increase of 600% in usage during the same period. These solutions have allowed businesses to continue to operate, and many have reported productivity has actually improved during the pandemic; however, the rapid change to a largely at-home workforce has introduced vulnerabilities and cybercriminals have taken advantage.

Attacks on Cloud Services Have Surged During the Pandemic

An analysis of data from over 30 million McAfee cloud customers revealed cyberattacks on cloud services increased by 630% between January and April, 2020.

Threats to cloud services were split into two main categories: Excessive usage from an anomalous location and suspicious superhuman. The first involves logins from a location not previously detected. The threat actor then initiates high-volume data access and privileged access activity. Suspicious superhuman is the name given to a login attempt from one location followed by another from a geographically distant location, in a time frame shorter that the minimum time to travel from one location to the other.

McAfee’s analysis indicates the majority of attacks on cloud services are opportunistic rather than targeted and mostly consist of password spraying attacks, where stolen credentials are used to try to gain access to cloud resources.

Targeted attacks tend to be conducted by threat actors in China, Iran, and Russia. These hackers have extensive infrastructure and are well funded and can therefore conduct high volumes of attacks. The McAfee Cloud Adoption & Risk Report confirmed the healthcare industry has been heavily targeted during the pandemic and is the second most targeted vertical behind the financial services. 198 million IP addresses in Russia (111M), China (73M), and Iran (14M) were used in attacks on the healthcare industry during the first four months of 2020. The high number of attacks shows why it is important for healthcare providers to continuously monitor cloud activity and block attempts by malicious actors to gain access to their sensitive cloud data.

Working from home without direct supervision has not increased insider threats, according to McAfee. Insider threats have remained at the same level as before the pandemic. The rise in attacks on cloud services is mostly due to external actors.

Change in Business Operations Requires Changes to Security Solutions

The problem for many businesses is they have adopted cloud services to support remote working but are still using legacy security and networking solutions in a hub and spoke network. While these cloud services can be accessed directly, many organizations require employees to login to their network infrastructure to access those services, often through a VPN.

Unfortunately, while the VPN solutions that have been implemented prior to the pandemic were fine for small numbers of employees, they have struggled to cope with such a rapid increase in remote employees. Connection issues has meant many employees have experienced difficulties accessing data through VPNs. As a result, employees often take shortcuts and access cloud services such as Microsoft 365 directly. That means they bypass the security solutions in the organization’s data center, which increases risk.

“Securing a remote workforce shifts the major security focus control points to the device and cloud. A cloud-native approach to delivering security will provide the most complete coverage, capable of reaching devices off-network and connecting to cloud services directly,” explained McAfee.

McAfee recommends using a cloud-based secure web gateway to protect against web-based threat and permitting users to connect to sanctioned cloud services directly, rather than requiring the use of a VPN with data protected using a cloud access security broker (CASB). The CASB can be configured to perform device checks, implement data controls, and protect against attackers who can access SaaS accounts via the internet, including multi-factor authentication to reduce the risk of stolen credentials from being used to access cloud resources.

The post Attacks on Cloud Services Increased by 630% Between January and April appeared first on HIPAA Journal.

Proof of Concept Exploit Released for Critical SMBGhost Windows 10 SMBv3 Vulnerability

A functional proof of concept (PoC) exploit for a critical remote code execution vulnerability in the Microsoft Server Message Block 3.1.1 (SMBv3) protocol has been released and is being used by malicious cyber actors to attack vulnerable systems, according to an alert issued by the DHS Cybersecurity and Infrastructure Security Agency (CISA).

The vulnerability, referred to as SMBGhost, is due to the way the SMBv3 protocol handles certain requests. If exploited, a malicious cyber actor could remotely execute code on a vulnerable server or client by sending a specially crafted packet to a targeted SMBv3 server. An attack against a client would also be possible if an attacker configured a malicious SMBv3 server and convinced a user to connect to it.

The vulnerability could be exploited to spread malware from one vulnerable system to another in a similar fashion to the SMBv1 vulnerability that was exploited in the 2017 WannaCry ransomware attacks. No user interaction is required to exploit the flaw on vulnerable SMBv3 servers.

The flaw – tracked as CVE-2020-0796 – is present in Windows 10 versions 1909 and 1903 and was the subject of a Microsoft security advisory in early March. The flaw received a maximum CVSS v3 severity rating of 10 out of 10.

Microsoft released a patch to correct the flaw in early March; however, almost three months on and many organizations have yet to apply the patch and are vulnerable to attack. Microsoft also released details of a workaround to prevent exploitation, which involves disabling SMBv3 compression.

While the workaround would prevent the flaw from being exploited on a SMBv3 server, it would not prevent an attack on a client. The workaround involves running a simple PowerShell command. No reboot is required after the command has been executed. Details are available here. Scanners are available on GitHub that can be used to check for the CVE-2020-0796 vulnerability.

Security researchers developed exploits for the flaw with limited success, but the PoC exploit now available would allow an attacker to escalate local privileges and deliver malware. The PoC exploit is not 100% reliable, but more refined exploits are expected to be released. In its current form it could be used to successfully attack a vulnerable SMBv3 server. If the exploit were to fail, an attacker could simply keep on trying until it worked.

CISA strongly recommends that all organizations apply the patch to prevent exploitation. If the patch cannot be applied, the workaround should be used and SMB ports should be blocked from the internet using a firewall until the patch can be applied.

The post Proof of Concept Exploit Released for Critical SMBGhost Windows 10 SMBv3 Vulnerability appeared first on HIPAA Journal.

Voicemail Phishing Scam Identified Targeting Remote Healthcare Workers

The COVID-19 pandemic has forced many companies to change working practices and allow large numbers of employees to work remotely from home. In healthcare, employees have been allowed to work remotely and provide telehealth services to patients. While this move is important for virus control and to ensure patients still have access to the medical services they need, remote working introduces cybersecurity risks and cybercriminals are taking advantage. There has been a significant rise in cyberattacks targeting remote workers over the past three months.

A variety of tactics are being used to trick remote workers into installing malware or divulging credentials, including a new tactic that has recently been uncovered by cybersecurity firm IRONSCALES.

In a recent report, IRONSCALES revealed threat actors are spoofing messages automatically generated by Private Branch Exchange (PBX) systems to steal credentials. PBX is a legacy phone system used by many enterprises to automate the handling of calls. One of the features of these systems is the ability to record voicemail messages and send recordings directly to users’ inboxes. These systems have been hugely beneficial during the COVID-19 pandemic, as they ensure that employees never miss important voicemail messages while working remotely. They have also given cybercriminals another way of conducting an attack.

In this campaign, the attackers spoof messages from the PBX system and inform an employee that they have a new voicemail message. The emails are personalized and include the user’s name or company name to make it appear that the messages are genuine. Subject lines in the messages are also carefully crafted to spoof the messages sent by real PBX systems.

To hear the messages, users are directed to a website that spoofs PBX integrations with the aim of stealing credentails. “It may seem odd for attackers to create phishing websites spoofing PBX integrations as most voicemails are quite benign in the information shared. However, attackers know that the credentials could be used for multiple other logins, including for websites with valuable PII or business information,” explained IRONSCALES. “In addition, any sensitive information that is left in the voicemail could potentially be used for a social engineering attack.”

IRONSCALES detected this voice phishing (vishing) campaign in mid-May. According to the report, the campaign is being conducted globally and at least 100,000 mailboxes have been targeted.

“If your organization automatically sends voicemails to workers inboxes, then your company is at risk of falling victim to this scam. As we know, if an email looks real then someone will fall for it,” explained IRONSCALES.

IRONSCALES suggests raising awareness of this scam with remote workers and implementing an email security system capable of detecting and blocking email security threats such as this, which have so far been effective at bypassing DMARC anti-spoofing measures.

The post Voicemail Phishing Scam Identified Targeting Remote Healthcare Workers appeared first on HIPAA Journal.

Fake VPN Alerts Used as Lure in Office 365 Credential Phishing Campaign

A phishing campaign has been identified that uses fake VPN alerts as a lure to get remote workers to divulge their Office 365 credentials.

Healthcare providers have increased their telehealth services during the COVID-19 public health emergency in an effort to help prevent the spread of COVID-19 and ensure that healthcare services can continue to be provided to patients who are self-isolating at home.

Virtual private networks (VPNs) are used to support telehealth services and provide secure access the network and patient data. Several vulnerabilities have been identified in VPNs which are being exploited by threat actors to gain access to corporate networks to steal sensitive data and deploy malware and ransomware. It is therefore essential for VPN systems to be patched promptly and for VPN clients on employee laptops to be updated. Employees may therefore be used to updating their VPN.

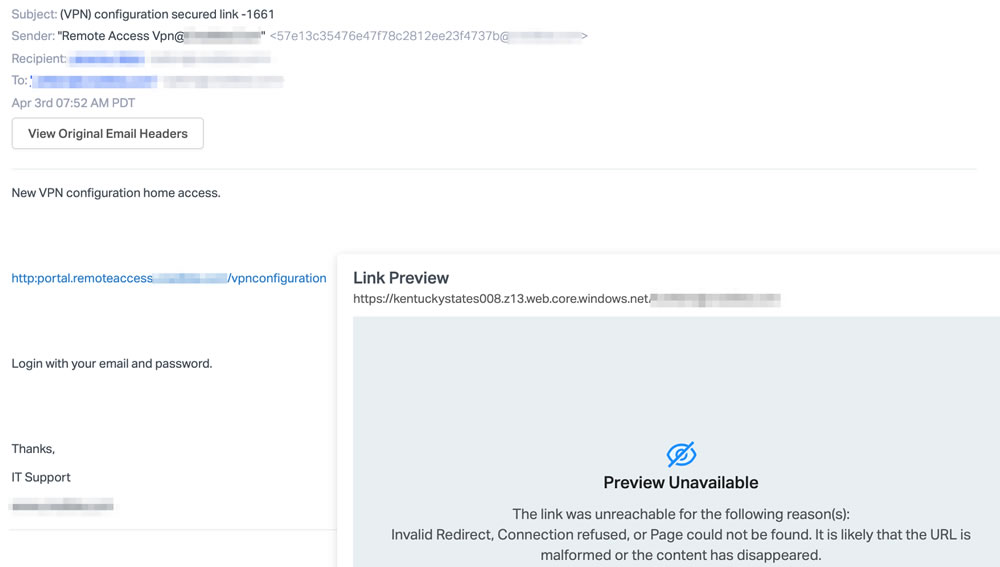
Researchers at Abnormal Security have identified a phishing campaign that impersonates a user’s organization and claims there is a problem with the VPN configuration that must be addressed to allow the user to continue to use the VPN to access the network.

The emails appear to have been sent by the IT Support team and include a hyperlink that must be clicked to install the update. The user is told in the email that they will be required to supply their username and password to login to perform the update.

This campaign targets specific organizations and spoofs an internal email to make it appear that the email has been sent from a trusted domain. The hyperlink has anchor text related to the user’s organization to hide the true destination URL to make it appear legitimate. If the user clicks the hyperlink in the email, they will be directed to a website with a realistic Office 365 login prompt. The phishing webpage is hosted on a legitimate Microsoft .NET platform so has a valid security certificate.

Fake VPN Alert Phishing

Source: Abnormal Security

Login credentials entered on the site will be captured by the attacker and can be used to access the individual’s Office 365 email account and obtain sensitive data in emails and attachments, as well as other data accessible using the Office 365 credentials through single sign-on.

Abnormal Security has found a variety of phishing emails that use variations of this message, which have been sent from several different IP addresses. Since the destination phishing URL is the same in each email, it suggests that the emails are part of the same campaign and have been sent by a single attacker.

The post Fake VPN Alerts Used as Lure in Office 365 Credential Phishing Campaign appeared first on HIPAA Journal.

Mobile Phishing Attacks Have Surged During the COVID-19 Health Crisis

Cybercriminals have changed their tactics, techniques, and procedures during the COVID-19 health crisis and have been targeting remote workers using COVID-19 themed lures in their phishing campaigns. There has also been a sharp increase in the number of phishing attacks targeting users of mobile devices such as smartphones and tablets, according to a recent report from mobile security company Lookout.

Globally, mobile phishing attacks on corporate users increased by 37% from Q4, 2019 to the end of Q1, 2020 with an even bigger increase in North America, where mobile phishing attacks increased by 66.3%, according to data obtained from users of Lookout’s mobile security software. Phishers have also been targeting remote workers in specific industry sectors such as healthcare and the financial services.

While the sharp increase in mobile phishing attacks has been attributed to the change in working practices due to the COVID-19 pandemic, there has been a steady rise in mobile phishing attacks over the past few quarters. Phishing attacks on mobile device users tend to have a higher success rate, as users are more likely to click links than when using a laptop or desktop as the phishing URLs are harder to identify as malicious on smaller screen sizes.

While the full URL is likely to be displayed on a laptop computer or desktop, a mobile device will only display the last section of the URL, which can be crafted to make the URL appear genuine on mobile devices. When working from home, employees are more likely to resort to using their mobile to perform tasks to stay productive, suggests Lookout, especially employees that do not have a large screen or multiple monitors at home as they do in the office.

Mobile devices typically lack the same level of security as laptops and office computers, making it less likely that phishing messages will be blocked. There are also more ways that phishing URLs can be delivered to mobile devices than laptops and desktops. On a desktop, phishing URLs will mostly be delivered via email, but on mobile devices they can easily be delivered via email, SMS, messaging apps, and social media and dating apps. There is also a tendency for mobile users to act faster and not stop and think about whether a request is legitimate, even though they may be particularly careful on a laptop or desktop.

The rise in phishing attacks targeting mobile users is a security concern and one that should be addressed by employers through education efforts and security awareness training, especially with remote workers. Phishing awareness training should cover the risk of mobile phishing attacks and explain how URLs can be previewed on mobile devices and other steps that should be taken to verify the validity of requests.

“If the message appears to come from someone you recognize but seems like a strange ask or takes you to a strange site, get in contact with that person directly and validate the communication,” said Hank Schless, senior manager of security solutions at Lookout. “In a time of remote work, it’s even more important to validate any sort of strange communication.”

Education alone may not be sufficient. Security software should also be used on mobile devices to better protect end users from phishing and malware attacks.

The post Mobile Phishing Attacks Have Surged During the COVID-19 Health Crisis appeared first on HIPAA Journal.

Russian Sandworm Group Targeting Exim Mail Servers, Warns NSA

A Russian hacking outfit called Sandworm (Fancy Bear) is exploiting a vulnerability in the Exim Mail Transfer Agent, which is commonly used for Unix-based systems. The flaw, tracked as CVE-2019-10149, is a remote code execution vulnerability that was introduced in Exim version 4.87.

An update was released on June 5, 2019 to correct the flaw, but many organizations have still not updated Exim and remain vulnerable to attack.

The vulnerability can be exploited by sending a specially crafted email which allows commands to be executed with root privileges. After exploiting the flaw, an attacker can install programs, execute code of their choosing, modify data, create new accounts, and potentially gain access to stored messages.

According to a recent National Security Agency (NSA) alert, Sandworm hackers have been exploiting the flaw by incorporating a malicious command in the MAIL FROM field of an SMTP message. Attacks have been performed on organizations using vulnerable Exim versions that have internet-facing mail transfer agents.

After exploiting the vulnerability, a shell script is downloaded from a remote server under the control of the hackers which is used to add privileged users, update SSH configurations to allow remote access, disable network security settings, and execute an additional script to allow further exploitation. This would potentially allow the hackers to gain full control of the email server. Were that to happen, all incoming and outgoing email could be intercepted and exfiltrated.

Sandworm is part of Russia’s General Staff Main Intelligence Directorate, otherwise known as GRU. The hackers have previously conducted attacks on countries in Europe and the United States. The group has conducted several cyberattacks on foreign governments is believed to have been involved in Russia’s efforts to influence the outcome of the 2016 presidential election.

The NSA has suggested mitigations to prevent exploitation of the flaw, the most important of which is updating Exim immediately to version 4.93 or a later release. The update will correct the CVE-2019-10149 vulnerability and other vulnerabilities that could potentially be exploited. After updating, administrators should make sure that software versions are regularly checked and updated as soon as new versions are released. Exim Mail Transfer Agent software can be updated through the Linux distribution’s package manager or directly from Exim.

If it is not possible to update immediately, it may be possible to detect and block exploit attempts. For instance, “Snort 3 rule 1-50356 alerts on exploit attempts by default for registered users of a Snort Intrusion Detection System (IDS).” Administrators should also routinely verify there have been no unauthorized system modifications such as additional accounts and SSH keys. Modifications would indicate a compromise.

The NSA recommends limiting user access privileges when installing public-facing mail transfer agents and network segmentation should be used to separate roles and requirements. It is important to keep public mail transfer agents separate from sensitive internal resources in a DMZ enclave, and firewall rules should be set to block unexpected traffic from reaching trusted internal resources. It is also important to only permit mail transfer agents to send outbound traffic to necessary ports. All other ports should be blocked.

“If an MTA DMZ was configured in a least access model, for example to deny by default MTA initiated outbound traffic destined for port 80/443 on the Internet while only permitting traffic initiated from an MTA to necessary hosts on port 80/443, the actors’ method of using CVE-2019-10149 would have been mitigated,” explained the NSA in their alert.

The post Russian Sandworm Group Targeting Exim Mail Servers, Warns NSA appeared first on HIPAA Journal.

HHS’ OIG to Scrutinize HHS COVID-19 Response and Recovery Efforts

The HHS’ Office of Inspector General (OIG) has published a strategic plan for oversight of the COVID-19 response and recovery efforts of the Department of Health and Human Services.

OIG will assess how well the HHS has performed in its mission to ensure the health and safety of Americans, determine whether HHS systems and data have been adequately protected, evaluate the effectiveness of the HHS response, and assess whether the $251 billion in COVID-19 funding has been correctly distributed by the HHS.

OIG has a mandate to oversee the activities of the HHS to promote the economy, efficiency, effectiveness, and integrity of HHS programs. OIG explained that “COVID-19 has created unprecedented challenges for the HHS and for the delivery of health care and human services to the American people.” Through audits, risk assessments, and data analytics, OIG will be assessing the HHS’s COVID-19 response and recovery efforts.

The HHS has a responsibility to protect the health and safety of Americans during a public health emergency such as the COVID-19 pandemic and protect beneficiaries that receive services through the HHS health care and human services programs. OIG will be providing the HHS with assistance and will support the HHS’s ongoing COVID-19 response efforts and will assist in fighting fraud and scams that endanger HHS beneficiaries and the public.

OIG will be investigating cases of fraud and will be working closely with law enforcement to protect the public and HHS beneficiaries. OIG will also assess the effectiveness and impact of HHS programs on the health and safety of the public and beneficiaries through audits and evaluations, including the acquisition, management, and distribution of resources from the Strategic National Stockpile, production, approval, and distribution of COVID-19 tests; vaccine and treatment research and development, and HHS health care and human services programs.

OIG’s oversight and enforcement activities include protecting HHS funds from fraud, waste and abuse and promoting transparency and accountability of HHS spending. In May 2020, $251 billion was made available to the HHS for COVID-19 response and recovery. OIG will be assessing whether that funding has been paid out in accordance with program requirements, determining whether recipients of funds met use and reporting requirements, and will investigate and fight fraud and abuse that has diverted COVID-19 funding from its intended purposes.

Cyberattacks against the HHS and healthcare organizations have increased considerably during the COVID-19 pandemic, and nation-states have been attempting to obtain sensitive data and intellectual property in relating to SARS-CoV-2 and the COVID-19 response. OIG explained that technologies that have been employed as part of the COVID-19 response could be targeted by threat actors to gain access to sensitive data. It is therefore essential that HHS IT infrastructure is properly protected, and vulnerabilities are proactively identified and addressed.

OIG will be assessing the capabilities of the HHS for detecting and mitigating IT vulnerabilities, will be conducting audits to determine whether vulnerabilities have been mitigated, and will investigate cybersecurity threats and attacks on HHS systems. OIG will provide assistance to the HHS to support a secure and robust infrastructure.

OIG will also be investigating the effectiveness of the HHS’s COVID-19 response and recovery programs and will identify opportunities to increase effectiveness and help ensure recipients of HHS COVID-19 response and recovery funding achieve the program goals. Successful practices and lessons learned during the COVID-19 response and recovery will be used to strengthen HHS programs in the future and improve preparedness planning for future public health emergencies.

The post HHS’ OIG to Scrutinize HHS COVID-19 Response and Recovery Efforts appeared first on HIPAA Journal.

NetWalker Ransomware Gang Targeting the Healthcare Industry

While some threat groups have stated that they will not attack healthcare organizations on the frontline in the fight against COVID-19, that is certainly not the case for the operators of NetWalker ransomware, who have been actively targeting the healthcare industry during the COVID-19 public health emergency .

Recent research conducted by Advanced Intelligence LLC has revealed the operators of the ransomware have been conducting extensive attacks on healthcare industry targets and operations are now being significantly expanded.

Most ransomware attacks conducted by Russian-speaking threat actors involve large-scale phishing campaigns rather that targeted attacks. NetWalker ransomware has been spread in this manner during the COVID-19 pandemic through spam emails claiming to provide information about SARS-CoV-2 and COVID-19 cases. The emails include a Visual Basic script file attachment named CORONAVIRUS_COVID-19.vbs, which downloads the ransomware from a remote server.

While phishing emails are still being used, the group is now moving into large-scale network infiltration. Representatives of the group have been posting advertisements on top-tier darknet forums announcing a new affiliate program under the ransomware-as-a-service model. While many threat groups are not particularly choosy about who they recruit to spread their ransomware, the NetWalker gang is opting for a quality rather than quantity approach and is only looking to recruit capable affiliates who have or are able to gain access to enterprise networks.

The gang is prioritizing affiliates who already have access to enterprise networks and is looking to work with hackers who have extensive experience who are capable of conducting regular attacks. As is common with Russian threat groups, affiliates are forbidden from attacking Russian or CIS targets.

The group claims it has the ability to exfiltrate data prior to data encryption and files stolen from victims will be published on its blog if the ransom is not paid, as is the case with other manual ransomware groups. The group also states that it will always decrypt files when the ransom is paid.

To attract experienced hackers, the group is offering a high percentage of the ransom payment for the affiliate. Many affiliate programs offer a 30/70 split of ransom payments, with the 70% going to the affiliate. NetWalker is offering 80% of all ransom payments if under $300K, and 84% for payments in excess of $300K. The ransoms demanded by the group so far have been significant, ranging from several hundred thousand dollars to millions.

The group has conducted attacks on several healthcare organizations, including the Champaign-Urbana Public Health District in Illinois in March, along with attacks on other major targets such as Toll Group, an Australian shipping firm, and the Australian customer experience firm Stellar.

The group has been using fileless ransomware according to Trend Micro. Fileless ransomware is not written to the disk and only operates in the memory, which makes it hard for security solutions to identify attacks. Microsoft has warned of attacks on healthcare providers in which the attackers used misconfigured IIS-based applications to deploy the Mimikatz credential-stealing tool, and PsExec to deploy NetWalker.

The change in tactics, techniques and procedures favoring highly targeted attacks, the current affiliate recruitment campaign, and the high percentages offered to affiliates are likely to see NetWalker ransomware become an even bigger threat over the coming months with the group joining other prolific manual ransomware threat groups such as Maze and REvil.

With manual ransomware attacks on healthcare organizations increasing, network defenders should take preemptive measures to reduce risks, such as addressing known vulnerabilities, securing vulnerable internet-facing systems, checking servers and applications for misconfigurations, and monitoring for the use of penetration testing tools, security log tampering, and credential theft activities which could indicate an previous system compromise.

The post NetWalker Ransomware Gang Targeting the Healthcare Industry appeared first on HIPAA Journal.