Healthcare Providers and AI: How to Protect Your Patients and Practice – JD Supra
HIPAA Privacy Rule Overhaul: 8 Important Takeaways from the New HIPAA Privacy Rule – JD Supra
Why HIPAA Compliance Is a Year-One System Architecture Decision – – HIT Consultant
HHS Finalizes HIPAA Privacy Rule Changes: What Business Associates Need to Know – ACA International
HIPAA Privacy Rule
The HIPAA Privacy Rule provides a federal floor of privacy standards that protects individuals’ health information and other identifying information by limiting the permissible uses and disclosure of such information by “covered entities” and “business associates” without authorization. The HIPAA Privacy Rule also gives individuals the rights to control how their health information is used and disclosed, to request copies of information maintained about them, and request corrections when omissions or errors exist.
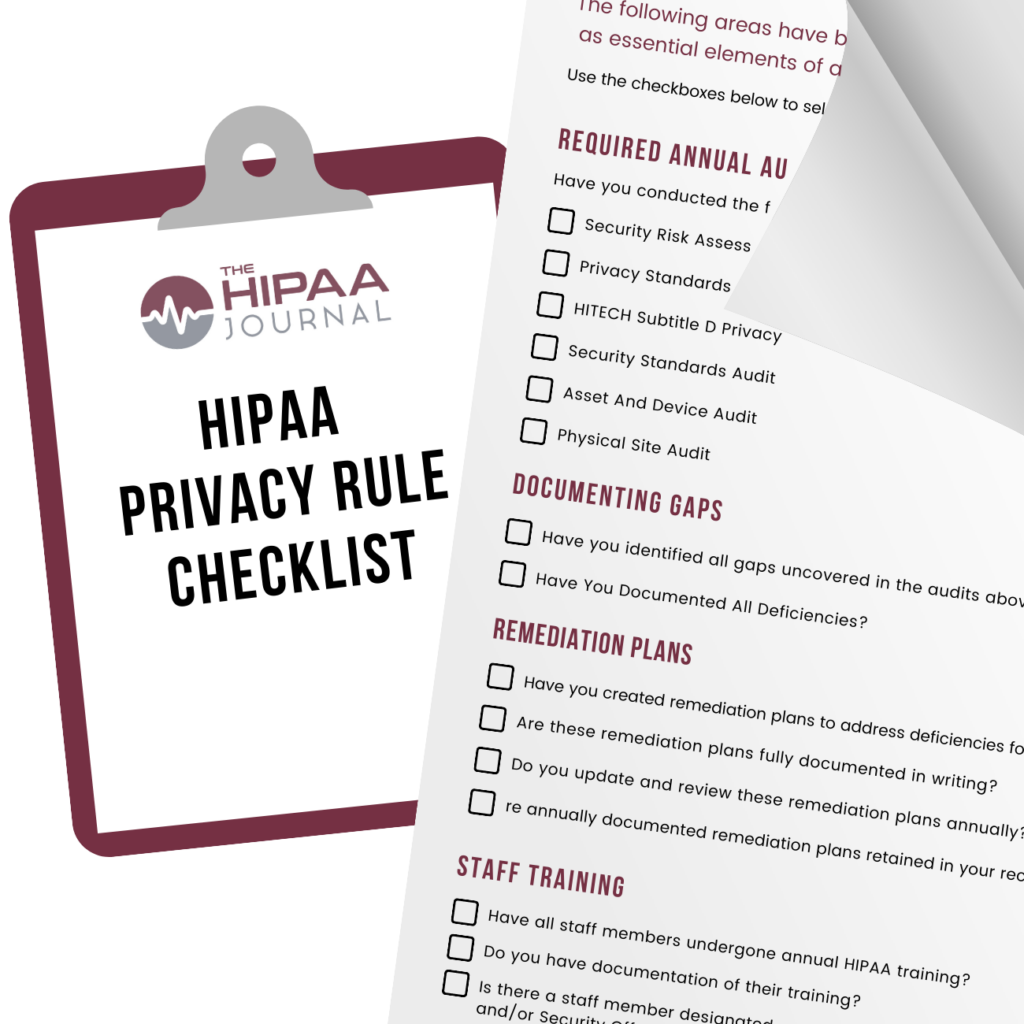 This guide to the HIPAA Privacy Rule explains why it exists, who it applies to, what it protects, and how to maintain compliance. It should be used in conjunction with our free, easy to use HIPAA Privacy Rule Checklist PDF which can be ordered by using any form on this page.
What is the Privacy Rule in the Context of HIPAA?
In the context of HIPAA, the Privacy Rule is a subpart of the Administrative Simplifications Regulations (45 CFR Parts 160,162, and 164). The protections provided by the Privacy Rule to individually identifiable health information apply to other subparts of the Administrative Simplification Regulations and how the standards within those subparts are applied.
For this reason, it is important for entities that are not usually required to comply with the HIPAA Privacy Rule (i.e., data storage services and vendors of personal health devices) to understand what the Rule protects and how. It can also be useful for those whose information is protected by the Privacy Rule to understand how the HIPAA privacy standards are applied to prevent misconceptions.
Your privacy respected – Read our privacy policy
Your privacy respected – Read our privacy policy
Get The HIPAA Privacy Rule Checklist
Free and Immediate Download
Please enable JavaScript in your browser to complete this form.

Delivered via email so please ensure you enter your email address correctly.
Your Privacy Respected
HIPAA Journal Privacy Policy
HIPAA Privacy Rule Fact Sheet
- The Privacy Rule was published in 2002. It is one of several sets of standards that evolved from HIPAA.
- It stipulates permissible uses and disclosures of Protected Health Information and individuals’ rights.
- Most health plans, health care clearinghouses, and healthcare providers are required to comply with the Privacy Rule.
- Business Associates may also be required to comply with the Privacy Rule depending on the service being provided.
- The Privacy Rule defines Protected Health Information to include identifiers maintained in the same designated record set.
- All patients and plan members must be given a HIPAA Notice of Privacy Practices on the first encounter or as soon as reasonable.
- The Notice of Privacy Practices must explain what Protected Health Information may be disclosed, to whom, and why.
- The Notice of Privacy Practices must also explain an individual’s right to access, amend, or transfer their Protected Health Information.
- If organizations violate the HIPAA Rules, individuals have the right to complain to the organization or HHS’ Office for Civil Rights.
- The Office for Civil Rights has the authority to impose corrective action plans or financial penalties on noncompliant organizations.
Who Falls Under the HIPAA Privacy Rule
 Before discussing what information is protected by the HIPAA Privacy Rule and how the HIPAA Privacy Standards ensure individuals’ rights, it is important to understand who the HIPAA Rules apply to because some organizations are not required to comply with every HIPAA Rule or every part of every HIPAA Rule. It is also the case that exceptions can exist to the applicability of each Rule.
Most health plans, health care clearinghouses, and healthcare providers that conduct electronic transactions listed in Part 162 of the Administrative Requirements are required to comply with the HIPAA Privacy Rule, the HIPAA Security Rule, and the HIPAA Breach Notification Rule that was introduced as part of the HITECH Act in 2009. Collectively, these organizations are referred to as “covered entities”.
Business associates are also required to comply with the HIPAA Security Rule and HIPAA Breach Notification Rule; and, depending on the nature of the service provided for or on behalf of a covered entity, any applicable standards of the Administrative Requirements and HIPAA Privacy Rule. Some of the exceptions mentioned above include:
- Health care providers that bill clients directly are not covered entities.
- Neither are insurance issuers who offer health insurance as a secondary benefit.
- Neither are health plans for certain types of benefits that are offered separately.
- The HIPAA Rules may apply to employers who self-administer a group health plan.
- But not to employment records containing individually identifiable health information.
- Vendors of personal health devices are only required to comply with HIPAA when they provide a service as a business associate.
To further complicate who the HIPAA Rules apply to, some organizations can be hybrid entities when some of their activities are covered by HIPAA, while others are not; or temporarily subject to the HIPAA Rules, for example, when a healthcare provider who does not qualify as a covered entity provides a service for or on behalf of a covered entity as a business associate. In such cases, the healthcare provider has to comply with the HIPAA Rules for as long as they are providing the service.

Why Does the HIPAA Privacy Rule Exist?
Prior to the passage of HIPAA, the privacy of medical records was determined by a patchwork of state regulations. The first Clinton administration (1993 to 1997) attempted to introduce a comprehensive federal health privacy framework, but the ambitious Health Security Act failed due to opposition from the private insurance industry and a lack of congressional support.
After the Act failed, Congress attempted to pass separate medical privacy legislation but could not agree on a national standard. Consequently, the buck was passed to the Secretary of Health and Human Services, who was instructed in the text of HIPAA to make recommendations “with respect to the privacy of certain health information”. At a minimum, the recommendations had to include:
- The rights that an individual who is a subject of individually identifiable health information should have.
- The procedures that should be established for the exercise of such rights.
- The uses and disclosures of such information that should be authorized or required.
The instruction adds that, if Congress does not pass legislation to protect the privacy of individually identifiable health information within three years of the passage of HIPAA, the Secretary shall promulgate a further Rule addressing the minimum recommendations. Congress did not pass privacy legislation within three years and a proposed HIPAA Privacy Rule was published in 1999. After years of addressing stakeholders’ comments, the HIPAA Final Privacy Rule was published in 2002 and became effective in 2003.
Get The HIPAA Privacy Rule Checklist
Free and Immediate Download
Please enable JavaScript in your browser to complete this form.
Delivered via email so please ensure you enter your email address correctly.
Your Privacy Respected
HIPAA Journal Privacy Policy
What Information is Protected by the HIPAA Privacy Rule?
Any individually identifiable health information relating to an individual’s past, present, or future physical or mental condition, treatment for the condition, or payment for the treatment is protected by the HIPAA Privacy Rule, along with individually identifiable non-health information maintained in the same “designated record set”.
Information maintained in a designated record set is known as Protected Health Information (PHI), even though elements of the set may not contain health information.
This definition of what information is protected by the HIPAA Privacy Rule can cause confusion because some sources claim that all information relating to an individual is protected – and that is not always the case. Individually identifiable health information and any other information that identifies – or that could be used to identify – the subject of the health information (known as an “identifier”) is protected only while it is maintained in a designated record set.
Whenever identifiers are maintained separately from individually identifiable health information, they are no longer Protected Health Information and the protections of the HIPAA Privacy Rule no longer apply. As an example, if a designated record set includes a patient’s diagnosis, their home telephone number, the name of their partner, and their healthcare payment details, all four elements of information are protected while they are maintained in the same designated record set.
If a separate record set is created containing a copy of the home telephone number and partner’s name (perhaps to provide the partner with an update on the patient’s health), these elements are not protected by the HIPAA Privacy Rule because there is no health information included in the record set. It is important to be aware that in such circumstances, although the HIPAA Rules do not apply, state privacy and security rules may.
How is Information Protected by the HIPAA Privacy Regulations?
The HIPAA Privacy Regulations, or “standards”, protect information by stipulating when uses and disclosures or Protected Health Information are required, permitted, or subject to an individual’s authorization. There are only two occasions when uses and disclosures are required; when an individual exercises their access rights and when access is required by HHS’ Office for Civil Rights for an investigation or compliance review. Both of these events are discussed in greater detail later.
Permissible uses and disclosures include those necessary to carry out treatment, payment, or health care operations, those required by law or for public health activities, and those necessary to avert a serious threat to health or safety. Among the disclosures permitted by HIPAA, there are some that are required by state laws. For example, disclosures to report abuse, neglect, or domestic abuse. Some “permissible” disclosures may also be “required” during emergency incidents.
Other than the uses and disclosures required or permitted by the HIPAA Privacy Regulations, and some for which the individual should be given an opportunity to object when feasible, all other uses and disclosures of Protected Health Information are prohibited unless they are authorized by the individual who is the subject of the Protected Health Information or their personal representative. Such uses and disclosures include uses for marketing and disclosures of psychotherapy notes.
Authorizations have to be written in clear language and explain to the individual what Protected Health Information is being used or disclosed, who to, and what for. If the covered entity is receiving a remuneration for the use or disclosure, this has to be included in the authorization, as does a warning that the covered entity may have no control over further disclosures of the Protected Health Information if, for example, it is published on a social media platform.
Get The HIPAA Privacy Rule Checklist
Free and Immediate Download
Please enable JavaScript in your browser to complete this form.
Delivered via email so please ensure you enter your email address correctly.
Your Privacy Respected
HIPAA Journal Privacy Policy
How do the HIPAA Privacy Standards Ensure Individuals’ Rights?
The HIPAA Privacy Standards ensure individuals’ rights by first requiring covered health plans and healthcare providers to give a HIPAA Notice of Privacy Practices to new patients or plan members on the “first encounter” whenever possible or as soon as reasonable afterwards.
The Notice must describe the ways in which the covered entity may use or disclose Protected Health Information and describe how individuals can exercise their rights to access copies of their Protected Health Information.
The right to access copies of Protected Health Information is the “required” disclosure mentioned above, but it is important for individuals to understand they are only able to access information maintained in a designated record set.
It is also important to understand that complying with an access request may take some time when multiple designated record sets are maintained per individual, or when Protected Health Information is in the possession of a business associate.
Once an individual has received a copy of their Protected Health Information the HIPAA Privacy Standards allows individuals to request corrections to the information if it is inaccurate or incomplete.
Individuals can also request information is transferred to another provider, or that specific information is withheld from certain organizations. For example, if a patient has paid for treatment privately, they have the right to request this information is withheld from their insurer.
Individuals also have the right to request an accounting of disclosures. This document should contain a list of the times when Protected Health Information has been disclosed for reasons other than those permitted by the HIPAA Privacy Regulations or authorized by the individual themselves. Individuals have the right to query any entry on the accounting of disclosures and, if not satisfied with the response, make a complaint about their privacy rights being violated.
Who Enforces HIPAA Privacy Rules?
The Department of Health and Human Services’ Office for Civil Rights (OCR) is the enforcer of the HIPAA Privacy Rule. Noncompliance could lead to civil and criminal penalties, highlighting the importance of rigorous adherence.
What Happens if You Violate HIPAA Privacy Regulations?
The violation of privacy rights is one of the leading reasons for complaints to HHS’ Office for Civil Rights; and when a complaint is received by the agency, it has to be reviewed and investigated if it appears there has been a violation of HIPAA regulations.
When HHS’ Office for Civil Rights conducts an investigation, a covered entity must disclose whatever Protected Health Information is necessary for the agency to conclude its investigation – as mentioned previously in the section explaining how information is protected.
Most violations of HIPAA regulations are resolved by technical assistance or a corrective action plan. This means that the covered entity or business associate may have to develop and implement new policies and procedures to resolve the issue responsible for the violation of the HIPAA regulations. The organization may then have to train its workforce on the new policies and procedures and, depending on the scale of the violation(s), undergo a period of compliance monitoring.
In cases where there has been a willful neglect of the HIPAA regulations, HHS’ Office for Civil Rights has the authority to impose civil monetary penalties on noncompliant organizations. Historically, financial settlements and civil monetary penalties have been reserved for the worst offenders following large-scale data breaches. More recently, the agency has pursued a campaign to address violations of the HIPAA regulations that deny individuals their Privacy Rule rights.
Get The HIPAA Privacy Rule Checklist
Free and Immediate Download
Please enable JavaScript in your browser to complete this form.
Delivered via email so please ensure you enter your email address correctly.
Your Privacy Respected
HIPAA Journal Privacy Policy
As well as organizations being penalized for non-compliance, members of the workforce can be sanctioned as well. The degree of sanction will depend on the nature of the violation and the content of the organization’s sanctions policy. In the worst cases of knowing and wrongful disclosures of PHI for personal gain, cases can be referred to the Department of Justice – who can pursue custodial sentences of up to ten years and fines of up to $250,000.
When was the Last Update to the HIPAA Privacy Rule?
The most recent update to the HIPAA Privacy Rule is the final rule HIPAA Privacy Rule: Changes to Support Coordinated Care and Individual Engagement and Reduce Regulatory Burdens. The HHS Office for Civil Rights (OCR) announced it on November 16, 2026, and it was published in the Federal Register on November 19, 2026. The update was a long time coming. HHS first proposed the changes in December 2020, and the Notice of Proposed Rulemaking was published in the Federal Register on January 21, 2021, almost six years before the final rule was issued.
What were the Major Changes Introduced by the Update?
The 2026 HIPAA Privacy Rule update has three main aims: strengthening the individual right of access, making it easier to share information for care coordination, and reducing the administrative burden on covered entities. The final rule also adds definitions of “electronic health record” and “personal health application” to the Privacy Rule.
Changes to Patients’ Right of Access
The biggest change for most covered entities is the time allowed to respond to access requests. It has been cut from 30 days to 15 days. The option of one 30-day extension remains. Individuals can ask for copies of ePHI in a designated record set to be sent to a personal health application of their choice. Covered entities only have to do this if the ePHI is readily producible in that form. They don’t have to implement new technology to make it possible, but they must use technology they already have or that other laws require. Individuals can also direct a covered health care provider to send ePHI held in an electronic health record to a third party.
Covered entities can no longer charge individuals for inspecting their PHI in person or for accessing their ePHI through an internet-based method, such as a patient portal or a personal health app connected through an API. Access that involves workforce labor, such as emailing a PDF on request, is not considered internet-based, so a reasonable, cost-based fee may still be charged. For other types of access, fees are limited to:
- labor for copying
- supplies for non-electronic copies
- postage
- preparing a summary or explanation, if the individual agrees to it
Covered entities with a website must post a fee schedule on it and make the schedule available at the point of service. They are also encouraged to consider the financial circumstances of the person making the request. Covered entities must not impose unreasonable identity verification requirements. They also must not create barriers to access, such as accepting requests only through a patient portal.
Changes to Facilitate Better Care Coordination
The final rule expressly allows covered entities to disclose PHI for individual-level care coordination and case management to third parties, such as social services agencies, community-based organizations, and home and community-based services providers. The minimum necessary standard still applies to these disclosures where relevant. A covered entity is not liable if the recipient later misuses or improperly discloses the information. The definition of health care operations has also been clarified to include care coordination and case management at both the individual and population level. This is particularly relevant to health plans.
Reducing the Administrative Burden
Covered health care providers no longer have to make a good faith effort to obtain written acknowledgment that a patient received the Notice of Privacy Practices (NPP). They also no longer have to document why an acknowledgment was not obtained. HHS estimates that this change alone will save around $798 million a year. Related changes to reduce the administrative burden include:
- Disclosures to Telecommunications Relay Services (TRS) communications assistants are permitted, and TRS providers are no longer considered business associates.
- The permission to use and disclose the PHI of Armed Forces personnel for mission readiness now covers all uniformed services, including the U.S. Public Health Service Commissioned Corps and the NOAA Commissioned Corps.
Other Changes Introduced by the Update
Other changes introduced by the 2026 HIPAA Privacy Rule update include that individuals have the right to discuss the content of the Notice of Privacy Practices (NPPs) with a designated contact, and NPPs must be updated to explain this new right. The NPP header must also refer to “health information” rather than “medical information.” The right to receive an NPP is also extended to inmates of correctional facilities that qualify as HIPAA covered entities.
Several proposals from the 2021 Notice of Proposed Rulemaking were not finalized. These include allowing individuals to take photographs of their PHI during in-person inspections, changing the standard for disclosures to family members and caregivers from “professional judgment” to “good faith,” and capping the fees that can be charged for sending copies of PHI to third parties.
How Long do HIPAA-Regulated Entities Have to Comply with the 2026 HIPAA Privacy Rule Update?
The final rule takes effect on January 18, 2027, 60 days after it was published in the Federal Register. Covered entities and business associates then have a further 180 days to comply. The compliance date is July 17, 2027. After that date, OCR can enforce the new requirements and may impose civil monetary penalties for noncompliance. Until then, the current requirements still apply, including the 30-day timeframe for responding to access requests.
By the compliance date, covered entities need to update their policies and procedures, publish their access fee schedules, and retrain their workforces on the new requirements. They also need to have their revised NPPs available on their websites, posted at their facilities, and ready to give to new patients.
There is a longer transition period for business associate agreements. Existing agreements that comply with the current requirements will be deemed compliant until whichever of these comes first:
- the agreement is renewed or modified after July 17, 2027
- January 18, 2028
The same transition period applies to agreements between business associates and their subcontractors. Verbal arrangements are not covered by the transition provision.

HIPAA Privacy Rule Compliance Overview
To support HIPAA compliance efforts, the information in this article should be used in conjunction with our free, easy to use HIPAA Privacy Rule Checklist PDF which can be ordered by using any form on this page.
Privacy Rule HIPAA compliance necessitates organizational actions and technical precautions. Organizationally, covered entities and business associates must implement and enforce privacy policies and procedures in line with the HIPAA Privacy Rule.
A privacy official should be appointed to oversee the development and implementation of these policies. Regular training sessions must be held to familiarize workforce members with these guidelines.
Covered entities must also inform individuals about their privacy rights and the potential use of their information. A HIPAA Notice of Privacy Practices should be readily available for anyone requesting it.
Breaches of unsecured PHI must be reported to the individuals affected, the Secretary of Health and Human Services, and in certain circumstances, to the media.
For instances where PHI needs to be shared, covered entities should create contracts ensuring that business associates will protect the information. These contracts, known as Business Associate Agreements (BAAs), are a critical part of Privacy Rule HIPAA compliance.
HIPAA Privacy Rule FAQs
What are the eighteen identifiers that determine whether health information should be protected?
There is sometimes a misconception that the eighteen “HIPAA identifiers” listed under §164.514 of the HIPAA Privacy Rule are Protected Health Information at all times. This is not the case. These identifiers relate to the information that must be removed from a designated record set before any remaining health or payment information is considered de-identified under the safe harbor method.
As explained above, any identifier that is maintained in a designated record set along with health or payment information is protected while it is maintained in the same designated record set. When maintained in a database that does not contain health or payment information, identifiers are not protected by HIPAA, although state privacy and security laws may apply.
It is important to be aware that the list of eighteen HIPAA identifiers was compiled more than twenty years ago and has not been updated to reflect changes in how individuals can be identified. For example, if details of a patient’s emotional support animal are maintained in a designated record set, and the patient could be identified by the emotional support animal, these details also need to be removed from a designated record set before any remaining health information is de-identified.
Get The HIPAA Privacy Rule Checklist
Free and Immediate Download
Please enable JavaScript in your browser to complete this form.
Delivered via email so please ensure you enter your email address correctly.
Your Privacy Respected
HIPAA Journal Privacy Policy
What is the difference between health information, individually identifiable health information, and Protected Health Information?
In the context of the HIPAA Privacy Rule, health (or payment) information does not include any information about who a health condition, treatment for the condition, or payment for the treatment relates to. “The patient has a broken leg” or “the patient’s treatment is being paid by Medicare” is health information for the purposes of complying with the HIPAA Privacy Rule.
As soon as any element of information is combined with health or payment information that could identify or be used to identify an individual, it becomes individually identifiable health information. If the identifying information is maintained by a covered entity or business associate in the same designated record set as the health information, it is Protected Health Information.
Within HIPAA, how does security differ from privacy?
The HIPAA Privacy Rule and the HIPAA Security Rule both have the same objectives with regards to protecting the confidentiality, integrity, and availability of Protected Health Information. The difference between them is that the HIPAA Security Rule only applies to electronic Protected Health Information, while the HIPAA Privacy Rule applies to Protected Health Information in any format.
Who enforces the HIPAA Privacy Rule?
Externally, the HIPAA Privacy Rule is enforced by the U.S. Department of Health and Human Services’ Office for Civil Rights (OCR). OCR officers are most often made aware of HIPAA Privacy Rule violations via public complaints, HIPAA audits, and covered entities complying with the requirements to notify OCR of data breaches. OCR also enforces the HIPAA Security Rule and HIPAA Breach Notification Rule.
Internally, the HIPAA Privacy Rule is enforced by a Privacy Officer. The Privacy Officer has the responsibility of conducting risk assessments, developing policies and procedures to reduce risks to a reasonable level, training members of the workforce on the policies and procedures, and enforcing the HIPAA sanctions policy for violations of the organization’s policies and procedures.
Are there specific technologies that are HIPAA compliant?
No technology is HIPAA-compliant because it is how the technology is configured and used that determines compliance, not the capabilities of the technology itself. If a technology is implemented that has access to Protected Health Information, a Business Associate Agreement may have to be in place with the vendor for the technology to be considered capable of supporting HIPAA compliance.
What is the Minimum Necessary Standard?
The Minimum Necessary standard stipulates that uses and disclosures of Protected Health Information must be limited to the minimum necessary to accomplish the intended purpose of the use or disclosure. The standard applies to most uses and disclosures, but there are exceptions to this standard it is important to be aware of in order to avoid unnecessary complaints.
Get The HIPAA Privacy Rule Checklist
Free and Immediate Download
Please enable JavaScript in your browser to complete this form.
Delivered via email so please ensure you enter your email address correctly.
Your Privacy Respected
HIPAA Journal Privacy Policy
In what circumstances can an individual object to disclosures of Protected Health Information?
These most often relate to disclosing information via a facility directory or notifying an individual’s family when (for example) an individual is admitted to hospital. Individuals can consent to limited information being disclosed in these circumstances or, if the individual is incapable of providing consent, covered entities can determine whether the disclosure is in the best interests of the individual. The information that can be disclosed in such circumstances is listed in §164.510.
What is the difference between individual consent and individual authorization?
For any other uses or disclosures of Protected Health Information other than those required or permitted by the HIPAA Privacy Rule, an individual has to give their consent or authorization. Consent, which can be verbal, is only allowed for the uses and disclosures included in §164.510. All other uses and disclosures require a written authorization signed by the individual. As a guideline, consent relates to obtaining permission for routine activities. Authorization is necessary when PHI is going to be used or disclosed for a non-routine activity.
What happens if you disclose Protected Health Information without an authorization?
If you disclose Protected Health Information impermissibly, it is a violation of HIPAA. The consequences of any HIPAA violation depend on various factors such as the nature of the violation, the harm to the individual, the organization’s sanctions policy, and the previous compliance history of both the person responsible for the violation and the organization they work for.
The impermissible disclosure of Protected Health Information may qualify as a data breach, in which case both the individual and HHS’ Office of Civil Rights need to be notified of the event. If the disclosure does not qualify as a data breach, the individual can still complain to HHS’ Office for Civil Rights, who may decide to investigate the organization depending on its compliance history.
What are the 3 Rules of HIPAA?
The three Rules of HIPAA that covered entities are required to comply with are the HIPAA Privacy Rule, the HIPAA Security Rule, and the HIPAA Breach Notification Rule which was introduced via the HITECH Act of 2009. There are two other Rules commonly associated with HIPAA; the HIPAA Enforcement Rule, which describes the process for compliance investigations, and the Omnibus HIPAA Final Rule which, in 2013, updated the HIPAA Privacy Rule and HIPAA Security Rule with other measures introduced by the HITECH Act.
In addition, it is important not to overlook the HIPAA General Provisions (Part 160, Subpart A) which explains many of the terms used in the HIPAA laws and regulations, and the Organization Requirements of Part 164 (§164.105) which explain which components of the HIPAA Privacy Rule apply to non-standard covered entities (i.e., Organized Health Care Arrangements, etc.). Covered entities and business associates are also required to comply with, or oversee compliance with, the Part 162 Rules relating to transactions and code sets.
What is the purpose of the Privacy Rule?
The purpose of the Privacy Rule is to set a federal floor of privacy protections for individuals’ individually identifiable health information. The Privacy Rule also gives individuals an opportunity to better control how their health information is used and disclosed, to take a more active role in their healthcare, and choose the best healthcare provider for their requirements.
Who is not covered by the HIPAA Privacy Rule?
Any organization that does not qualify as a covered entity or that does not provide a service for or on behalf of a covered entity as a business associate is not covered by the HIPAA Privacy Rule. It is important to be aware that business associates are only required to comply with the Privacy Rule “where provided”, and this is usually established in a Business Associate Agreement. Some business associates may not be covered by the HIPAA Privacy Rule depending on the service provided, and may only required to comply with the HIPAA Security and Breach Notification Rules.
When does the Privacy Rule not apply to health information?
The Privacy Rule does not apply to health information in a number of circumstances. These include when an organization does not qualify as a HIPAA covered entity or business associate, when the health information belongs to a student and is covered by FERPA, when other, more stringent, Rules than HIPAA apply, and when an individual has authorized a use or disclosure which may be subject to further uses and disclosures that a covered entity has no control over (i.e., when it is published on social media).
Why is the Privacy Rule important?
Research suggests when patients believe their health information is protected, they are more willing to discuss intimate details with healthcare providers. With more information, healthcare providers can make more accurate diagnoses and prescribe more effective courses of treatment, leading to better patient outcomes, higher morale in the workplace, and increased hospital satisfaction scores.
What are HIPAA Rules and why are they different?
The HIPAA Rules are the standards within the Administrative Simplification Regulations that govern how covered entities must protect the privacy of Protected Health Information, how electronic Protected Health Information should be safeguarded to ensure its confidentiality, integrity, and availability, and how covered entities should respond in the event of an impermissible use or disclosure or a data breach.
The reason they may be considered “different” is that they are a baseline of privacy and security standards. In many states, more stringent privacy and/or security standards, or regulations providing individuals with greater access rights, overlay parts of HIPAA. Some states also have privacy and security standards that cross borders, protecting the individually identifiable health information of state residents wherever they are in the United States.
What is the difference between the Privacy Rule of HIPAA, the HIPAA Privacy Law, and the HIPAA Privacy Act?
There is no difference between the Privacy Rule of HIPAA, the HIPAA Privacy Law, and the HIPAA Privacy Act. These are names sometimes used to describe the “Standards for the Privacy of Individual Identifiable Health Information” published in Subpart E of Part 164 of the HIPAA Administrative Simplification Regulations.
Most sources, including the HHS’ Office for Civil Rights, refer to the Standards as the “HIPAA Privacy Rule” to avoid confusing the agency-promulgated standards with Laws or Acts passed by Congress. For example, the HIPAA Act was passed by Congress, but the HIPAA Rules were promulgated by the U.S. Department of Health and Human Services.
Get The HIPAA Privacy Rule Checklist
Free and Immediate Download
Please enable JavaScript in your browser to complete this form.
Delivered via email so please ensure you enter your email address correctly.
Your Privacy Respected
HIPAA Journal Privacy Policy
The post HIPAA Privacy Rule appeared first on The HIPAA Journal.
Healthcare Employees Sharing Patient Data with AI Tools Viewed as Major Emerging Risk
Healthcare security leaders are increasingly concerned about patient privacy incidents, HIPAA violations, and intellectual property loss due to employees sharing sensitive data with public AI models. While there is a risk of employees uploading patient data to unapproved tools such as ChatGPT, Gemini, or Claude, sensitive data may also be disclosed by unauthorized browser extensions, plug-ins, or an OAuth grant, which can be approved in a few clicks. According to a recent survey by the cybersecurity company DNS Filter, 43% of healthcare security leaders said they believe employee sharing of sensitive data with AI models is the biggest emerging AI risk in the next 12 months. The biggest perceived risk is loss of intellectual property through AI training data, rated as the biggest risk by 53% of respondents, compared to 31% in other sectors.
Multiple privacy incidents have already been reported by healthcare providers involving employees uploading sensitive patient data to public AI models, in violation of their organization’s data privacy and security policies and the HIPAA Rules. Recent examples include Johns Hopkins Bayview Medical Center, Weill Cornell Medicine, and the Washington Department of Social and Health Services. Since breaches of protected health information are only made public via the HHS’ Office for Civil Rights breach portal if they affect 500 or more individuals, and media notices are only required for breaches of that magnitude, the problem could be far more extensive. The DNSFilter survey findings suggest that may well be the case.
Around half of healthcare respondents have either confirmed (27%) or suspect (23%) that employees have connected an unapproved AI tool to Google Workspace, Microsoft 365, or their SSO environment. While patient data may not have been involved in those actual or suspected incidents, it is a significant risk, and a lack of AI governance means privacy violations may go unnoticed.
According to the DNSFilter report – Seeing the Risk, Missing the Signal: AI Security in Healthcare – only 27% of respondents said every security tool they own is actively monitored, and 40% of respondents said they actively monitor 50% or fewer security tools. While 70% of organizations confirmed they have implemented formal policies prohibiting the use of unapproved AI tools, only 40% said their policy is consistently enforced. Half of respondents said AI security and governance is one of their biggest security gaps; the highest share of any sector.
Your privacy respected – Read our privacy policy
Your privacy respected – Read our privacy policy
Six out of 10 respondents said they are reliant on their AI and SaaS vendors to alert them to security incidents, which is more than the 43% of respondents from other sectors. Only 23% of healthcare respondents said they catch SaaS and AI incidents through employee reporting, compared to 44% in other sectors. An additional concern is that 47% of healthcare organizations said their employer can authorize a new AI tool to access company systems without higher-level approval.
Despite the security gaps, confidence is high in the ability to detect breaches. In healthcare, 87% of respondents said they are confident that they could detect a breach within 6 hours, and 40% said they are very confident. One-third said they had experienced an incident that originated from a SaaS or AI tool in the past 12 months, and the same percentage said they had experienced such an incident that was never formally reported or disclosed.
Despite the risks, only a small percentage of healthcare organizations rate AI security and governance as one of the most important areas for IT security spending. Only 33% of respondents said they are sending their next dollar to AI security and governance, compared to 41% in other industries. This shows that while concern about risk is growing, money to address the problem is not following.
“Healthcare security leaders know exactly where AI puts their data at risk. What they’re missing is the moment that risk becomes an incident, and too many are hearing about it from a vendor instead of their own team. When the data involved is protected health information, the risk only becomes more significant. Before the next dollar goes to AI governance, healthcare organizations need to see which AI services their people are already using without clearance,” said Ken Carnesi, CEO, DNSFilter.
The post Healthcare Employees Sharing Patient Data with AI Tools Viewed as Major Emerging Risk appeared first on The HIPAA Journal.
Alleged U.S Hospital Ransomware Attacker Extradited to U.S. to Face Charges – The HIPAA Journal
Alleged U.S Hospital Ransomware Attacker Extradited to U.S. to Face Charges
The U.S. Department of Justice has announced that a Kazakh national suspected of engaging in ransomware attacks on U.S. hospitals, healthcare organizations, and schools has been extradited to the U.S. to face charges. Roman Khlynovskiy, 43, is alleged to have been a member of the 8-Digits Team, a ransomware group with links to the INC Ransom and Lynx ransomware groups. Along with other members of the 8-Digits Team, Khlynovskiy is alleged to have repeatedly targeted schools, hospitals, and other healthcare providers in at least six U.S. states.
Khlynovskiy is alleged to have breached protected networks, exfiltrated data, and encrypted files. Victims were threatened with publication of the stolen data to pressure them into paying ransoms. According to the Federal Bureau of Investigation (FBI), 8-Digits Team claimed to have exfiltrated more than 50 terabytes of sensitive data, including more than 70 million private and confidential health records, threatened to publish the data, and demanded at least $500 million in ransom payments.
Khlynovskiy travelled to Rimini, Italy, in July 2025 for a family vacation and was arrested and detained by Italian authorities. He was recently extradited to the United States and has been formally charged with conspiracy to commit computer fraud and identity theft, conspiracy to commit wire fraud, extortion involving computers, conspiracy to commit money laundering, and threats to disclose nonconsensual intimate images in violation of the TAKE IT DOWN Act. The TAKE IT DOWN Act criminalizes the non-consensual online publication of intimate images and was signed into law in May 2025. Khlynovskiy made his initial appearance in federal court in Knoxville, Tennessee, on November 16, 2026. Khlynovskiy is presumed innocent until proven guilty beyond a reasonable doubt in a court of law. If he is convicted on all counts, Khlynovskiy faces a maximum penalty of 27 years in jail.
The FBI is committed to bringing ransomware attackers and other cybercriminals to the United States to face charges for their crimes. According to FBI Director Kash Patel, those efforts are among the most aggressive work the agency has conducted to bring fugitives to the United States. In the past 12 months, there have been 84 Foreign Transfers of Custody (FTOCs), an increase of 71%, and 157 extraditions, an increase of 121%. “Those who victimize Americans cannot evade justice by operating overseas, and the FBI will continue to pursue them wherever they may be,” said Patel.
Your privacy respected – Read our privacy policy
Your privacy respected – Read our privacy policy
The post Alleged U.S Hospital Ransomware Attacker Extradited to U.S. to Face Charges appeared first on The HIPAA Journal.