41,000 Connecticut Medicaid Recipients Affected by DHS Data Incident – The HIPAA Journal
41,000 Connecticut Medicaid Recipients Affected by DHS Data Incident The HIPAA Journal
Data breaches have been announced by the Connecticut Department of Social Services, Public Partnerships LLC, Hattiesburg Eye Clinic, and the Eye Care Center of Snohomish.
The Connecticut Department of Social Services (DSS) has reported a data breach involving the protected health information of 41,000 individuals. The incident involved claims and payment information related to the Connecticut Medicaid (HUSKY) program, which was exposed after an unauthorized user gained access to a Connecticut Medicaid provider reimbursement account. DSS was informed about the data breach by its fiscal agent and account administrator, Gainwell Technologies, on June 25, 2026. The investigation determined that the unauthorized access was most likely financially motivated, rather than to obtain patient data; however, data theft could not be ruled out.
The provider portal has been secured, and the affected individuals have been offered complimentary credit monitoring and identity theft protection services. Electronic medical records, financial information, and Social Security numbers were not involved. The breach involved a combination of names, identification numbers associated with Medicare claims or provider payment accounts, dates of service, payment information, information about the services received, amounts paid, and information related to non-Medicaid health insurance.
This is the second such incident to be announced this year. An earlier breach in March 2026 affected approximately 22,500 individuals and involved unauthorized access to the HUSKY system using the compromised credentials of a Hartford Healthcare employee.

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
A data breach we had previously missed was reported by Public Partnerships LLC in early August that involved the attempted sale of the protected health information of 12,018 individuals. Public Partnerships is the single fiscal intermediary (FI) for the New York Consumer Directed Personal Assistance Program (CDPAP). CDPAP is a state Medicaid program that allows individuals who require home care to choose, hire, train, and manage their own caregivers.
In June 2026, Public Partnerships learned that a former facilitator had attempted to sell consumer data to another New York CDPAP facilitator. The former facilitator had been terminated by Public Partnerships in March 2026 for (unspecified) non-compliance with the program integrity requirements. The facilitator who was approached and offered the data refused and reported the incident to Public Partnerships.
Before Public Partnerships became the single FI for CDPAP, the state used hundreds of localized independent organizations. These legacy FIs became network facilitators or subcontractors under Public Partnerships under the single statewide contract with Public Partnerships. When it learned of the alleged sale, the former FI was contacted, informed about the allegation, and was told that offering to sell CDPAP data is unlawful and a breach of its ongoing contractual obligations. The former FI was instructed to delete all CDPAP data in its possession. Public Partnerships also notified all remaining facilitators of their contractual obligations and that the sale and purchase of CDPAP data is unlawful.
The case has been reported to the HHS Office for Civil Rights and the HHS Office of Inspector General, and all potentially impacted individuals have been notified by mail. The impacted data included names, addresses, dates of birth, Medicaid ID numbers, PPL ID numbers, and information relating to enrollment in New York Medicaid. While the sale appears not to have gone ahead, and there have been no other known cases, the affected individuals have been offered complimentary identity protection and credit monitoring services.
Hattiesburg Eye Clinic, P.A. in Mississippi has reported a data security incident that potentially involved unauthorized access to the protected health information of 6,137 individuals. A network disruption was experienced on August 18, 2026, and third-party cybersecurity experts were engaged to investigate and determine the nature and scope of the activity. The review of the incident concluded on September 16, 2026, and confirmed that patient data had been exposed and may have been acquired. The affected data varied from individual to individual and may have included first and last names, phone numbers, Social Security numbers, and medical diagnoses/conditions.
Additional technical safeguards have been implemented to prevent similar incidents in the future, and notification letters have been mailed to all potentially affected individuals. A ransomware and data theft/extortion group called The Gentlemen claimed responsibility for the incident and maintains that patient data was stolen.
Anup K. Deol, OD PS, doing business as Eye Care Center of Snohomish in Washington, has identified unauthorized access to parts of its network containing the protected health information of 3,059 patients. The unauthorized access was identified on August 12, 2026, and third-party cybersecurity experts were engaged to investigate the activity. The investigation confirmed that an unauthorized third party gained access to limited files on its network on or around July 28, 2026.
The review of the affected files was completed on September 28, 2026. The data involved varied from individual to individual and may have included names, addresses, birth dates, and medical information, which may have included lab results, diagnoses, medications, and treatment information. The incident was reported to law enforcement, and additional safeguards have been implemented to prevent similar incidents in the future.
The post 41,000 Connecticut Medicaid Recipients Affected by DHS Data Incident appeared first on The HIPAA Journal.
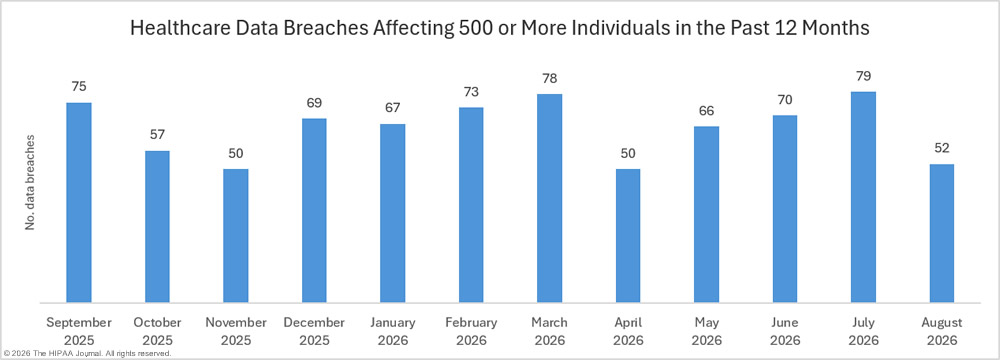
An analysis of data breaches affecting 500 or more individuals reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) in August 2026 shows a considerable improvement from the previous month. Data breaches are down 34% month-over-month, with August’s total of 52 data breaches, the second-lowest monthly total in the past 12 months, well below the 12-month average of 66 data breaches per month.
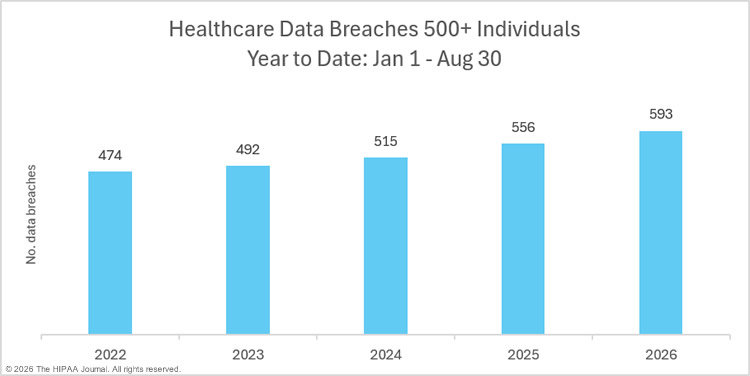
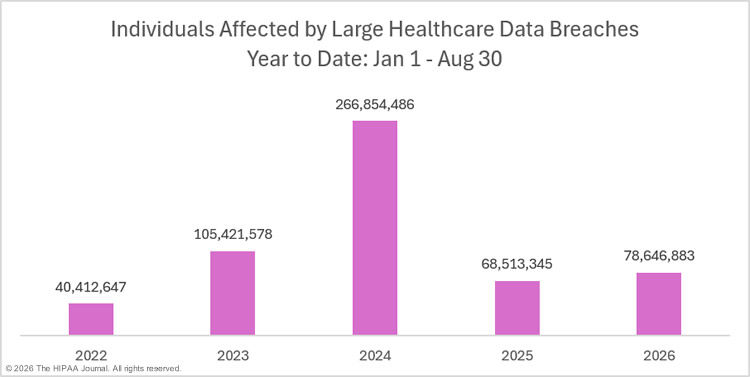
While August was a relatively good month for healthcare data breaches, the year-to-date figures show that 2026 is turning out to be another bad year for healthcare data breaches. Last year was the worst-ever year for healthcare data breaches, with 807 incidents reported. So far this year, 593 large healthcare data breaches have been reported to OCR. At this time last year, the total stood at 556 data breaches. That’s a 6.7% year-over-year increase.
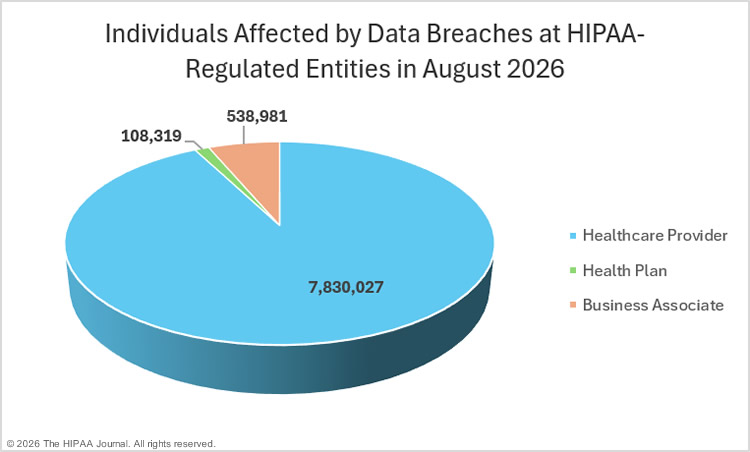
Across the 52 data breaches, the protected health information of at least 8,377,327 individuals was exposed or impermissibly accessed or disclosed. While that represents a 75% month-over-month decrease in affected individuals, July was one of the worst months in recent history for breached healthcare records, with more than 33 million affected individuals.
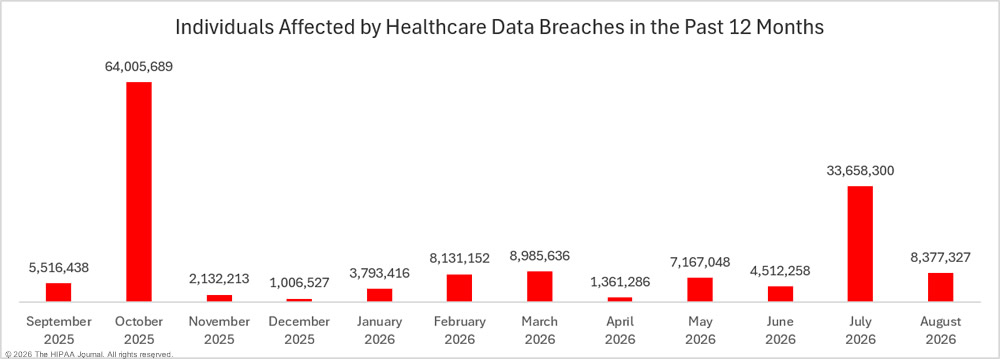
This year has already seen the protected health information of 78.6 million individuals exposed or impermissibly accessed or disclosed. That represents a 14.8% year-over-year increase in affected individuals.
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Two data breaches stand out in August in terms of scale. The largest data breach of the month, and the fourth largest data breach to be reported by a HIPAA-regulated entity so far this year, involved unauthorized access to the protected health information of more than 4.1 million individuals. The incident occurred at AdaptHealth, a healthcare company that provides home medical equipment, diabetes supplies, and sleep therapy products. AdaptHealth was contacted by a member of the ShinyHunters data theft and extortion group in June and was informed that its network had been accessed and sensitive data exfiltrated. Data theft was later confirmed.
The second largest data breach was reported by the clinical genomics company Baylor Genetics. An unknown hacker accessed parts of its network that contained the protected health information of more than 2.8 million patients. These were two of 17 data breaches affecting more than 10,000 individuals, and all but two of those incidents were hacking incidents. No information has been released on one of the non-hacking incidents. The other involved data theft by a former facilitator who stole data and attempted to sell it to another individual.
| Regulated Entity | State | Covered Entity Type | Individuals Affected | Type of Breach | Location of Breached Information | Cause of Breach |
| AdaptHealth, LLC | PA | Healthcare Provider | 4,115,802 | Hacking/IT Incident | Network Server | Hacking incident involving data theft |
| Baylor Genetics | TX | Healthcare Provider | 2,810,878 | Hacking/IT Incident | Network Server | Hacking incident |
| American Addiction Centers | TN | Business Associate | 327,754 | Hacking/IT Incident | Network Server | Hacking incident involving theft of data from its Salesforce environment |
| Premier Medical Group of the Hudson Valley P.C. | NY | Healthcare Provider | 282,075 | Hacking/IT Incident | Network Server | Hacking incident |
| Boston Healthcare for the Homeless Program | MA | Healthcare Provider | 201,260 | Hacking/IT Incident | Network Server | Hacking incident |
| Midwest Spine & Brain Institute | MN | Healthcare Provider | 108,487 | Unauthorized Access/Disclosure | Network Server, Other | Hacking incident at business associate (3C Care Systems) |
| Oakdale Ear Nose & Throat PA d/b/a Minnesota ENT | MN | Healthcare Provider | 99,714 | Hacking/IT Incident | Unauthorized access to six employee email accounts | |
| Osceola Mental Health Inc. dba Park Place Behavioral Healthcare | FL | Healthcare Provider | 71,702 | Hacking/IT Incident | Network Server | Hacking incident |
| Kern Psychiatric Health and Wellness Center, Inc | CA | Healthcare Provider | 51,352 | Hacking/IT Incident | Network Server | Hacking incident at its management company (Genesis Healthcare Management) |
| NFI North, Inc. | NH | Healthcare Provider | 49,540 | Hacking/IT Incident | Network Server | Hacking incident |
| Hawaii Dental Group, Inc DBA Hawaii Family Dental | HI | Healthcare Provider | 45,853 | Hacking/IT Incident | Hacking incident involving a compromised email account | |
| Connecticut Department of Social Services | CT | Health Plan | 41,000 | Hacking/IT Incident | Network Server | Hacking incident involving a provider reimbursement account |
| Advantage Home Health Care | IN | Healthcare Provider | 19,851 | Hacking/IT Incident | Network Server | Hacking incident involving data exfiltration |
| Viking Enterprises, Inc. d/b/a City Ambulance Service | TX | Healthcare Provider | 14,324 | Hacking/IT Incident | Ransomware attack (Qilin) | |
| Public Partnerships LLC | NY | Business Associate | 12,018 | Unauthorized Access/Disclosure | Network Server | Insider data theft incident involving a former network facilitator |
| Kim Knobbe | MO | Business Associate | 11,927 | Unauthorized Access/Disclosure | Network Server, Other | Unauthorized access/disclosure incident – no information available |
| Silver Summit Medical Corporation | CA | Healthcare Provider | 11,349 | Hacking/IT Incident | Network Server, Other | Hacking incident at an unnamed vendor. Data theft confirmed |
When the breach notification deadline is reached, and the number of affected individuals has yet to be determined, data breaches need to be reported to OCR using an estimate of the number of affected individuals. Most regulated entities choose to report these breaches using a figure of 500 or 501 affected individuals, then update the breach report when the data review is concluded. In August, 7 such incidents were reported using these placeholder figures. These incidents are likely to have affected substantially more individuals than the initial breach report suggests.
| Regulated Entity | State | Covered Entity Type | Individuals Affected | Type of Breach |
| AnMed Health | SC | Healthcare Provider | 501 | Ransomware attack (The Gentlemen) |
| Baraga County Memorial Hospital | MI | Healthcare Provider | 501 | Ransomware attack (Wallstreet) |
| Longview ER Operations, LLC | TX | Healthcare Provider | 501 | Hacking incident |
| Horizon Eye Care Laser & Eye Surgery Center | NJ | Healthcare Provider | 501 | Hacking incident |
| Vista Del Mar Child and Family Services | CA | Healthcare Provider | 500 | Hacking incident |
| WellDyneRX, LLC | FL | Healthcare Provider | 500 | Hacking incident |
| Well Child, Inc. | TN | Healthcare Provider | 500 | Hacking incident – data theft confirmed |
The majority of the month’s data breaches were hacking and other IT incidents, which accounted for 78.8% of the month’s data breaches and 98% of the affected individuals (8,215,959). On average, these incidents involved the exposure or theft of the protected health information of 205,399 individuals, with a median breach size of 5,258 individuals.
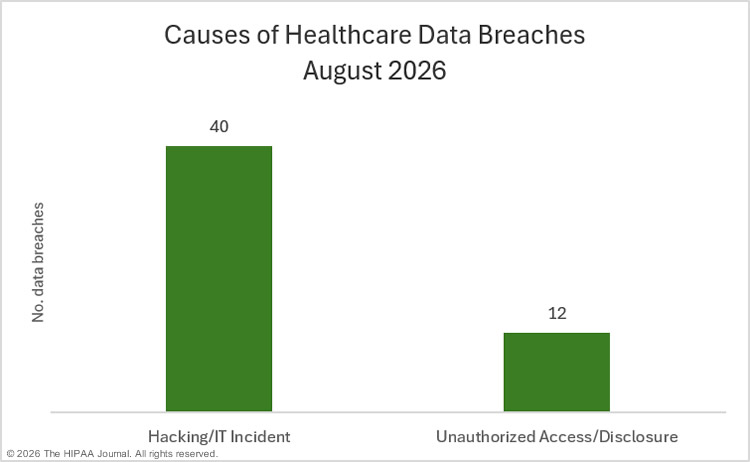
The year-to-date figures show a slight year-over-year increase in hacking/IT incidents. Between January 1 and August 30, 2026, 457 hacking/IT incidents have been reported, compared to 453 incidents for the corresponding period in 2025. While hacking incidents are only up by 0.9% year-over-year, 74,315,731 individuals have been affected, which is an 18.7% increase compared to this time last year.
There were 12 unauthorized access/disclosure incidents in August, involving the protected health information of 161,368 individuals. The average breach size was 13,447 individuals, and the median breach size was 4,024 individuals. The year-to-date figures show a 21.2% decrease in unauthorized access/disclosure incidents compared to this time last year, with incidents dropping from 94 for the period from January 1 to August 31 to 74 this year. So far this year, 1,651,788 individuals have been affected by these incidents, 71.7% fewer individuals than this time last year.
No loss, theft, or improper disposal incidents were reported in August. The year-to-date figures show a 75% year-over-year decrease in loss/theft incidents, with only two such incidents reported so far this year compared to 8 last year. There have been two unauthorized disposal incidents reported this year, compared to one such incident for the corresponding period in 2025.
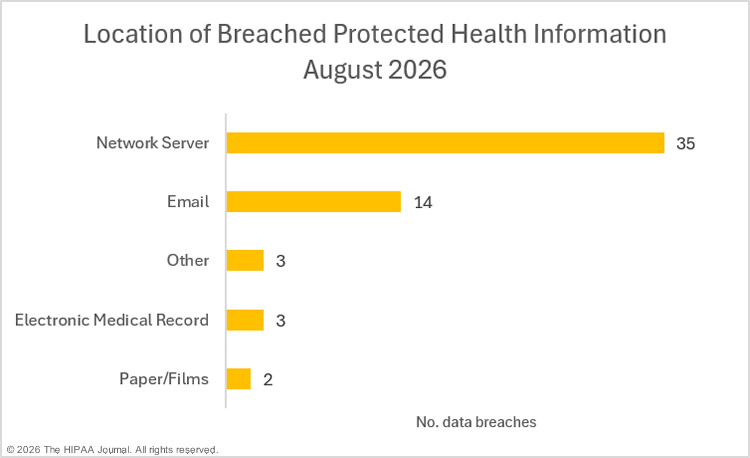
In August, the most common location of breached protected health information was network servers, with email accounts the next most common location of breached data.
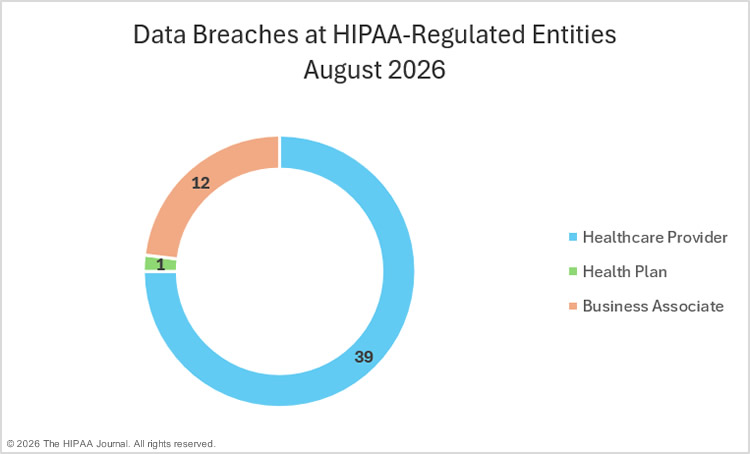
The HIPAA Breach Notification Rule requires HIPAA-covered entities to report data breaches to OCR and notify the affected individuals. Notifications must also be issued when there is a data breach at a business associate of a HIPAA-covered entity; however, it is ultimately the responsibility of each affected HIPAA-covered entity to ensure that notifications are issued. A covered entity may delegate the reporting requirements to the business associate that experienced the data breach or may choose to issue notifications themselves. The raw breach data on the OCR breach portal shows data breaches based on the reporting entity, not where the data breach occurred.
In August, healthcare providers reported 41 data breaches, business associates reported 8 breaches, and 3 breaches were reported by health plans. The pie charts below show where the breach actually occurred rather than the reporting entity to better reflect data breaches at business associates.
In August, large healthcare data breaches were reported by HIPAA-regulated entities in 29 states. Texas was the worst affected with 7 large data breaches, with California and Florida taking joint second spot with 4 breaches each.
| State | Breaches | State | Breaches |
| Texas | 7 | Idaho | 1 |
| California | 4 | Indiana | 1 |
| Florida | 4 | Kansas | 1 |
| Illinois | 3 | Maine | 1 |
| New York | 3 | Michigan | 1 |
| Pennsylvania | 3 | Missouri | 1 |
| Tennessee | 3 | North Dakota | 1 |
| Hawaii | 2 | New Hampshire | 1 |
| Massachusetts | 2 | New Jersey | 1 |
| Minnesota | 2 | Ohio | 1 |
| Arkansas | 1 | Oklahoma | 1 |
| Arizona | 1 | South Carolina | 1 |
| Colorado | 1 | Vermont | 1 |
| Connecticut | 1 | West Virginia | 1 |
| Georgia | 1 | ||
While only three HIPAA-regulated entities in Pennsylvania reported data breaches, the state ranked top in terms of affected individuals, with Texas taking second spot and Tennessee in third.
| State | Individuals Affected | State | Individuals Affected |
| Pennsylvania | 4,121,776 | Colorado | 5,378 |
| Texas | 2,838,764 | Maine | 5,000 |
| Tennessee | 333,448 | Kansas | 4,649 |
| New York | 295,031 | Arizona | 3,000 |
| Minnesota | 208,201 | Georgia | 2,750 |
| Massachusetts | 206,100 | North Dakota | 1,750 |
| Florida | 79,588 | Arkansas | 1,500 |
| California | 69,251 | Vermont | 1,408 |
| Hawaii | 54,172 | West Virginia | 1,215 |
| New Hampshire | 49,540 | Ohio | 808 |
| Connecticut | 41,000 | Idaho | 553 |
| Indiana | 19,851 | Michigan | 501 |
| Illinois | 13,474 | New Jersey | 501 |
| Missouri | 11,927 | South Carolina | 501 |
| Oklahoma | 5,690 | ||
OCR announced one enforcement activity in August to resolve noncompliance with the HIPAA Rules. Azul Vision, Inc., a California optometry and ophthalmology service provider, agreed to settle an alleged violation of the HIPAA Privacy Rule’s right of access for $50,000. A patient was not provided with timely access to her medical records. She filed a complaint with OCR after 3 months and finally received the records two years after the initial request was made. State Attorneys General may also impose penalties for HIPAA violations, although no HIPAA violation cases were announced in August.
About this Report
The HIPAA Journal monthly data breach reports are based on data obtained from the HHS Office for Civil Rights and have been combined with breach report data from other sources. The data breaches included in this report were reported in August 2026 but occurred weeks or months previously. The data was obtained from OCR on October 23, 2026. The figures in this report may increase or decrease as HIPAA-regulated entities complete their breach investigations, and those changes will be reflected in our healthcare data breach statistics page and our annual HIPAA data breach reports. Further information about HIPAA enforcement actions can be found in our HIPAA violations cases page.
The post August 2026 Healthcare Data Breach Report appeared first on The HIPAA Journal.
