Feature Articles

Free Webinar: The Most Overlooked HIPAA Challenges of 2026

Do your employees know the right thing to do in each of these common HIPAA challenges faced by medical practices?

An online review calls for a response.

A patient asks for a copy of their records.

A new vendor needs access to patient information.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please enable JavaScript in your browser to complete this form.

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { margin-bottom: 18px; } .inpage_banner_12838 a { max-width: 80%; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } } .hj_co_m_12838 { margin-bottom: 30px; } .hj_co_m_12838 .sbwf-main-form-container { max-width: 340px; margin: 0 auto; box-shadow: 0 4px 6px rgba(0,0,0,0.05),0 6px 6px rgba(0,0,0,0.05); padding: 30px; box-sizing: border-box; border: 1px solid #f4f4f4; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 200px; margin: 0 auto; display: block; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { text-align: center; border-top: 1px dashed #c8c8c8; padding: 20px 0 0; margin: 30px 0 20px; color: #753043; font-weight: 600; line-height: 30px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { text-align: center; font-size: 16px; color: #3B3B3B; line-height: 24px; font-weight: 600; margin: 0; padding: 0; } #sidebar .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 span { font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container p.terms, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms { text-align: center; font-size: 11px; padding-bottom: 0; line-height: 19px; margin: 10px 0 10px; } .hj_co_m_12838 .sbwf-main-form-container p.terms a { color: #753044; text-decoration: none; } .hj_co_m_12838 .sbwf-main-form-container p.terms a:hover { text-decoration: underline; } .hj_co_m_12838 .sbwf-main-form-container p.terms_title, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms_title { text-align: center; font-size: 11px; font-weight: 600; color: #752f43; padding-bottom: 0; line-height: 19px; } .hj_co_m_12838 .sbwf-main-form-container p.info, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.info { text-align: center; color: #727272; font-size: 14px; line-height: 20px; padding-bottom: 20px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input.wpforms-field-medium { width: 100%; max-width: 100%; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form .wpforms-field { padding-top: 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="text"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="email"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="tel"] { border: 2px solid #f4f3f3; font-size: 14px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full { margin: 24px 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 260px; height: 61px; font-size: 16px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_co_m_12838 .sbwf-main-form-container { padding: 20px; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 170px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { font-size: 22px; line-height: 28px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { font-size: 18px; line-height: 24px; } .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="text"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="email"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="tel"] { height: 36px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 220px; height: 52px; font-size: 15px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_sb_m_12838 div.wpforms-container-full .wpforms-form .wpforms-field-row.wpforms-field-medium { max-width: 100%; } form[data-zi-mapped-form] #wpforms-28160-field_1, form[data-zi-mapped-form] #wpforms-28160-field_1-last, form[data-zi-mapped-form] #wpforms-28160-field_3-container, form[data-zi-mapped-form] #wpforms-28160-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28160-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_6-container[data-zi-field-enriched="false"] { display: block !important; } form[data-zi-mapped-form] #wpforms-28155-field_1, form[data-zi-mapped-form] #wpforms-28155-field_1-last, form[data-zi-mapped-form] #wpforms-28155-field_3-container, form[data-zi-mapped-form] #wpforms-28155-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28155-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_6-container[data-zi-field-enriched="false"] { display: block !important; }

Overlooked areas can quickly turn into HIPAA problems

In this live webinar Sidney Secchiaroli and Sean Harris will share the common questions they field every day, and the biggest challenges practices either don’t know to explore or completely forget about,

Sidney and Sean have helped hundred’s of medical practices work through day-to-day HIPAA and OSHA compliance questions. They’ll explain what gets missed, where things tend to go wrong and what you can do differently in your practice.

You’ll learn how to:

  • Take the right first steps after a suspected HIPAA incident and assess whether it’s a breach.
  • Avoid common mistakes when responding to patient requests for copies of their records.
  • The do’s and don’ts when dealing with vendors.
  • Handle patient testimonials and respond to online reviews (negative and positive) without disclosing Protected Health Information.

Date of Live Webinar: November 18, 2026

Time: 12 PM ET, 11AM CT, 10 AM MT, 09 AM  PT

Duration: 01:00 Hour

Can’t join live? Register and we’ll send you the recording. 


About The Speakers:

As customer support specialists at Abyde, Sidney Secchiaroli and Sean Harris serve as dedicated HIPAA and OSHA compliance resources for thousands of Abyde’s  medical practice customers. Together, they work hands-on with practices nationwide, answering questions, guiding them through their unique situations, and keeping them confident and audit-ready.

Sidney Secchiaroli Customer Success SpecialistSidney Secchiaroli | Customer Success Specialist, Abyde

Sidney Secchiaroli brings a firsthand understanding of how a busy medical practice operates from her work as a certified medical assistant. At Abyde, she draws on that experience to help practice teams apply HIPAA and OSHA requirements to their daily work. She’ll bring that frontline perspective to the webinar, showing where HIPAA can get overlooked during routine tasks and what teams can do about it.

Sean Harris Customer Success SpecialistSean Harris | Customer Success Specialist, Abyde

Sean Harris has been helping practices with compliance at Abyde since at least 2022. He previously spent several years in construction staffing, where OSHA safety standards were part of daily operations. Today, he helps healthcare teams work through HIPAA and OSHA questions, with a focus on turning requirements into clear steps staff can follow when a problem comes up.

Abyde’s Customer Success team helps thousands of customers across the country put HIPAA requirements into practice.


Date of Live Webinar: November 18, 2026

Time: 12 PM ET, 11AM CT, 10 AM MT, 09 AM  PT

Duration: 01:00 Hour

Can’t join live? Register and we’ll send you the recording. 

The post Free Webinar: The Most Overlooked HIPAA Challenges of 2026 appeared first on The HIPAA Journal.

Free Webinar Today: A Practical Guide to a HIPAA Security Risk Assessment

Security Risk Assessment for HIPAA ComplianceA missing or inadequate HIPAA Security Risk Assessment (SRA) can leave a major gap in your HIPAA compliance program. It is also one of the issues most frequently identified in OCR enforcement actions.

Yet many practices remain uncertain about what an SRA should cover, how often it should be updated, and what distinguishes a genuine risk analysis from a simple checklist.

Join Bradley King, Senior Compliance Consultant, for a practical 30-minute webinar that will explain the role of the SRA and help you identify your next steps. Whether you are completing an SRA for the first time or reviewing your existing documentation, you will leave with a clearer understanding of what your organization needs to do.

You will discover:

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

  • What is-and-is-not a HIPAA Security Risk Assessment
  • Where the SRA fits within your wider HIPAA compliance program
  • When your SRA should be reviewed and updated
  • Why SRA deficiencies are a recurring focus of OCR enforcement
  • The practical steps your organization can take to strengthen its approach

The HIPAA Security Risk Assessment, or SRA, is arguably the most foundational document in your practice when it comes to HIPAA compliance. As your organization gets ready for the next year, compliance may not be at the top of your to-do list. However, the holidays present a perfect opportunity to finally catch up on administrative tasks, especially your annual SRA.

If you can’t attend the live event, then register anyway, and we will send you the recording.


Date of Live Webinar: October 28, 2026

Time: 12:00 – 12:30 PM ET, 11:00 – 11:30 AM CT, 10:00 – 10:30 AM MT, 09:00 – 09:30 AM  PT

Duration: 00:30 Hour

Can’t join live? Register and we’ll send you the recording. 


This webinar is presented by Abyde in partnership with The HIPAA Journal.

Speaker: Bradley King, Senior Compliance Consultant

Bradley King has many years of experience in HIPAA and OSHA compliance consulting. He has spoken at national conferences and delivered continuing education webinars on HIPAA and OSHA compliance best practices, and has worked directly with thousands of practices, from solo, owner-operator practices to multi-location, multistate healthcare organizations, on building and maintaining compliance programs.

Abyde is a leader in the compliance software industry, streamlining HIPAA & OSHA requirements for thousands of practices across the United States.


Date of Live Webinar: October 28, 2026

Time: 12-12:30 PM ET, 11-11:30 AM CT, 10-10:30 AM MT, 09-09:30 AM  PT

Duration: 00:30 Hour

Can’t join live? Register and we’ll send you the recording. 

The post Free Webinar Today: A Practical Guide to a HIPAA Security Risk Assessment appeared first on The HIPAA Journal.

Is Your Website Sharing Patient Data With Trackers? How to do a Web Scan

Website Privacy RiskWebsite privacy risks

Website privacy risks can remain hidden across a health provider’s digital estate until a patient, regulator, or plaintiff discovers them.

A pixel installed for one advertising campaign, a script introduced through a plugin, or an analytics tool added by an outside agency can continue operating long after anyone remembers approving it, creating a website tracking privacy risk.

Privacy and compliance teams may not know every tool that is operating, what information it collects, or where that information is sent. For a health provider managing multiple hospitals, locations, subdomains, service-line websites, and campaign pages, one forgotten or incorrectly configured script can affect hundreds or thousands of webpages.

Healthcare websites are constantly being updated

A large healthcare organization may operate a main corporate website alongside hospital websites, provider directories, service-line pages, campaign landing pages, patient portal login pages, recruitment sites, blogs, mobile applications, and websites inherited through acquisitions. Different marketing teams, agencies, developers, and technology vendors may all be able to introduce new code.

Your privacy respected – Read our privacy policy

Your privacy respected – Read our privacy policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { background-color: #D1D0CB; margin-bottom: 18px; max-width: 510px; display: block; margin: 0 auto 18px; padding: 20px 0; } .inpage_banner_12838 a img { margin-bottom: 10px; } .inpage_banner_12838 p.terms_title { text-align: center; font-family: sans-serif; font-size: 12px; font-weight: 400; color: #33342F; padding-bottom: 0; line-height: 19px; } .inpage_banner_12838 p.terms_title a { color: #33342F; text-decoration: underline; } .inpage_banner_12838 p.terms_title a:hover { text-decoration: none; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } .inpage_banner_12838 { background-color: #D1D0CB; margin-bottom: 18px; max-width: 300px; display: block; margin: 0 auto 18px; padding: 20px 0; } .inpage_banner_12838 a img { margin-bottom: 10px; } .inpage_banner_12838 p.terms_title { text-align: center; font-family: sans-serif; font-size: 12px; font-weight: 400; color: #33342F; padding-bottom: 0; line-height: 19px; } .inpage_banner_12838 p.terms_title a { color: #33342F; text-decoration: underline; } .inpage_banner_12838 p.terms_title a:hover { text-decoration: none; } }

The result is a constantly changing web environment in which compliance, privacy, and information security teams may not have a complete picture of every third-party technology operating across the organization.

Is your privacy policy accurate?

Research suggests that third-party data transfers are present on the overwhelming majority of hospital websites.

A 2024 study of a nationally representative sample of 100 nonfederal acute care hospitals found that 96% of their websites transferred user information to at least one third party. The websites communicated with a median of nine third-party domains, and 86% had at least one third-party cookie.

Only 71 of the 100 hospital websites had a publicly accessible website privacy policy. Among those 71 policies, just 40 specifically identified third-party companies or services receiving user information.

The findings highlight an important distinction: Having a privacy policy does not guarantee that an organization has full visibility into its data practices or that the policy accurately describes current activity. A privacy policy that was accurate when it was written can become outdated as new technologies, vendors, campaigns, and websites are introduced.

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_58549 { margin-bottom: 18px; } .inpage_banner_58549 a { max-width: 510px; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } .inpage_banner_58549 { margin-bottom: 18px; } .inpage_banner_58549 a { max-width: 300px; display: block; margin: 0 auto; } }

Why larger healthcare organizations face greater challenges

Health systems and multi-location healthcare groups can have hundreds of people involved in their digital operations. Marketing may select an analytics platform, an agency may deploy advertising pixels, a service line may introduce a new scheduling application, and a recently acquired practice may continue using its existing website technology.

Each decision may appear reasonable in isolation. Collectively, however, they can create a complex and poorly documented network of data connections.

Common problems include:

  • No central inventory of websites, subdomains, microsites, and landing pages
  • Different privacy and consent practices across affiliated organizations
  • Inconsistent use of tag management systems
  • Technologies added without privacy, security, or legal review
  • Inherited tracking code following mergers and acquisitions
  • Expired campaigns with active tags
  • Privacy policies that do not reflect actual website behavior
  • Vendors introducing additional subprocesses or technologies
  • Unclear responsibility for approving and monitoring website tools
  • Script ownership that isn’t well documented, so when a team member moves on, their scripts keep running without anyone else realizing it

A review of the main health system homepage will not necessarily reveal what is happening on a specialty clinic website, an appointment page, a recruitment portal, or a location-specific landing page. That’s why it is important for any web scan to go beyond the homepage.

When does website tracking become a HIPAA issue?

For Covered Entities and Business Associates, the HIPAA Rules apply when information collected through tracking technologies or disclosed to tracking technology vendors includes PHI.

Pages that deserve particularly careful examination include:

  • Authenticated patient portals
  • Patient portal login and registration pages
  • Online appointment scheduling pages
  • Symptom checkers
  • Provider search tools
  • Pages that collect an email address or other identifying information
  • Forms through which an individual describes a condition or reason for seeking care
  • Pages containing treatment, prescription, billing, or medical record information

The Department of Health and Human Services’ Office for Civil Rights states that a privacy policy, website notice, or terms of use document does not, by itself, make a disclosure of PHI permissible. OCR also states that an ordinary cookie consent banner is not a HIPAA-compliant authorization.

If a tracking vendor creates, receives, maintains, or transmits PHI on behalf of a regulated entity for a covered function, the vendor may qualify as a Business Associate. The organization must determine whether the disclosure is permitted and whether an appropriate Business Associate Agreement is required.

The solution for website privacy risks

Automated website privacy monitoring tools can help close the visibility gap. Tools can scan public-facing pages for third-party scripts and cookies, identify external technologies operating across websites and subdomains, and flag activity that may require further investigation.

They can also compare observed website behavior with statements in the organization’s privacy policy and monitor for changes over time.

These tools do not replace legal analysis or determine whether a disclosure violates HIPAA, but they can help privacy, compliance, marketing, and technology teams find potential risks sooner, prioritize their response, and demonstrate ongoing oversight.

Not every visit to a healthcare webpage involves PHI

The legal position is more nuanced than some early reporting on tracking technologies suggested.

In June 2024, a federal court vacated part of OCR’s tracking technology guidance in American Hospital Association v. Becerra. The court rejected the position that an IP address combined with a visit to a public, unauthenticated webpage about a particular condition or healthcare provider was sufficient, by itself, to trigger HIPAA obligations.

OCR’s current guidance acknowledges that a visit to a public healthcare webpage does not automatically constitute a disclosure of individually identifiable health information simply because a tracking technology connects the visit with an IP address.

For example, someone may visit an oncology page because they are conducting academic research, helping a relative, reading the news, or looking for employment. The webpage visit alone does not establish that the visitor has cancer or is seeking cancer treatment.

However, the court decision did not create a general exemption for healthcare websites. HIPAA may still apply when identifiable information is connected with an individual’s health, care, or payment for care. Information entered into an appointment form, registration page, symptom checker, or authenticated portal presents a substantially different risk from an anonymous visit to a general information page.

Regulatory and litigation risks extend beyond HIPAA

In July 2023, OCR and the Federal Trade Commission (FTC) sent joint warning letters to approximately 130 hospital systems and telehealth providers. The letters drew attention to technologies such as Meta Pixel and Google Analytics and warned that they could disclose sensitive health information to third parties.

The FTC can take action when an organization makes misleading privacy promises or uses and discloses consumer health information in ways that are unfair or deceptive. State consumer protection, privacy, and wiretapping laws may also apply.

This means an organization should not conclude that a tracking activity is low risk merely because the information being shared with third parties does not meet the HIPAA definition of PHI.

The enforcement record illustrates the wider exposure:

  • The FTC alleged that GoodRx disclosed health information to Facebook, Google, and other companies contrary to its privacy promises. GoodRx agreed to a $1.5 million civil penalty and restrictions on sharing health information for advertising.
  • BetterHelp agreed to pay $7.8 million to resolve FTC allegations involving the disclosure of email addresses, IP addresses, and health questionnaire information for advertising purposes.
  • In a separate class action, patients alleged that tracking pixels on Advocate Aurora Health’s websites, app, and patient portal disclosed their information to Meta and Google. They brought claims under federal and state privacy laws, including the federal Wiretap Act. The court approved a $12.225 million settlement, without ruling on the underlying allegations. The case shows how website tracking can lead to privacy litigation outside a HIPAA enforcement action.

Private litigation has created additional risk. Plaintiffs have pursued claims against healthcare organizations under federal and state wiretapping, privacy, consumer protection, and contract laws. Not every claim has succeeded, and the outcomes frequently depend on the information involved, the wording of the relevant statute, the consent process, and how the technology operated.

The absence of a successful HIPAA enforcement action does not therefore mean that an organization has no legal exposure.

A cookie banner is not a complete solution

Website Privacy RiskConsent management is important, particularly under state privacy laws, but a cookie banner cannot compensate for a lack of technical visibility.

An organization needs to establish:

  • Which technologies operate before a visitor can make a choice about whether to opt out
  • Whether scripts are actually prevented from loading if a visitor rejects them
  • Whether the consent mechanism covers every relevant website and subdomain
  • Whether a visitor’s preferences are passed to connected systems
  • Whether the policy accurately identifies the information collected and its recipients
  • Whether HIPAA authorization or another legal permission is required

A banner may tell visitors that cookies are used, but it does not answer whether a particular script is receiving an appointment event, a patient identifier, or information entered into a form.

The evolution of the patient journey

Healthcare websites have become an important part of the patient journey. Visitors use them to research symptoms, compare services, find doctors, schedule appointments, complete forms, access patient portals, watch educational videos, use chat tools, and locate nearby facilities.

These functions often depend on third-party technologies, including:

  • Analytics platforms
  • Advertising and conversion pixels
  • Tag management systems
  • Appointment scheduling applications
  • Embedded forms
  • Chat and chatbot services
  • Session replay technologies
  • Heatmaps
  • Maps and location services
  • Embedded videos
  • A/B testing and personalization tools
  • Social media integrations

Many of these tools provide genuine operational or marketing value. The risk arises when an organization does not fully understand what information a technology collects, when that information is collected, where it is sent, or what the receiving company is permitted to do with it.

A technology added to measure conversions on one campaign page may later be deployed across an entire website. A script introduced by a plugin may communicate with additional companies that were not part of the original approval. A tool removed from the visible marketing stack may continue operating through a tag manager or legacy page template.

On a large and frequently updated web estate, these changes can be difficult to identify through manual reviews alone.

Visibility is the foundation of control

Healthcare organizations do not have to abandon digital analytics, advertising, or website personalization in order to comply with HIPAA and other federal and state privacy regulations. These technologies can provide meaningful value by helping patients find services and allowing organizations to understand whether their communications are effective.

The essential requirement is visibility.

A healthcare organization cannot assess a technology it does not know is present, enforce a policy it cannot test, or control a disclosure it cannot see. Understanding what operates across the organization’s websites, where information is sent, and whether those activities match the organization’s privacy policy is necessary for compliant use of many digital marketing capabilities.

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_58549 { margin-bottom: 18px; } .inpage_banner_58549 a { max-width: 510px; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } .inpage_banner_58549 { margin-bottom: 18px; } .inpage_banner_58549 a { max-width: 300px; display: block; margin: 0 auto; } }

What information can website technologies collect?

The information disclosed to a third party will depend on the technology, its configuration, and the page on which it operates. It can potentially include:

  • The URL and title of the page visited
  • The visitor’s IP address and approximate location
  • Device and browser information
  • Cookie identifier
  • Advertising identifiers
  • Buttons, links, or menu options selected
  • Search terms
  • Form field activity
  • Appointment-related events
  • Information used to identify or recognize returning visitors

The presence of a third-party script does not automatically mean that Protected Health Information has been disclosed or that a law has been violated. The organization must examine the information involved, the context in which it was collected, the purpose of the disclosure, the recipient, and the applicable legal authority.

However, it is impossible to perform that assessment if the organization does not know the technology is present.

10-point website privacy governance checklist

A health system should treat its public website environment as part of its wider privacy and security program. A practical governance process should include:

Identify the complete web estate. Document websites, subdomains, microsites, mobile applications, landing pages, portals, and inherited digital properties.

Inventory third-party technologies. Identify scripts, cookies, pixels, plugins, embedded content, and the external domains with which each property communicates.

Prioritize higher-risk pages. Focus on scheduling, registration, provider search, symptom, portal, payment, and form pages.

Document purpose and ownership. Every technology should have a defined business purpose and an internal owner.

Assess the information involved. Determine what data is collected, when it is transmitted, and whether it may include PHI or other sensitive information.

Review vendors and agreements. Establish whether the recipient is a business associate, whether a BAA is required, and whether the proposed use is permitted.

Compare behavior with published promises. Website activity, consent choices, privacy policies, and notices should be consistent.

Control future changes. New tracking technologies should require appropriate marketing, privacy, security, and legal approval before deployment.

Monitor continuously. Repeat scans and investigate material changes instead of relying solely on periodic manual audits.

Document decisions and remediation. Maintain evidence of findings, approvals, risk assessments, corrective actions, and ongoing oversight.

A one-time website audit provides only a snapshot

Large healthcare websites change continually. New pages are published, campaigns launch, vendors update code, plugins change, and acquired organizations introduce additional domains.

A review conducted today may not reflect the organization’s website in practice next month.

Effective oversight therefore requires both an initial inventory and continuous monitoring. The organization should be able to quickly identify and act on:

  • New scripts and external domains
  • Changes to cookies and tracking behavior
  • New pages handling potentially sensitive information
  • Differences between locations, brands, or subdomains
  • Technologies that reappear after they were removed
  • Changes that create conflicts with the privacy policy
  • Unapproved additions made through a tag manager or plugin

Historical records can also help an organization determine when a technology first appeared, which pages were affected, and whether remedial or breach assessment work may be necessary.

Protecting your organization with a web scanner

A website scanner can monitor your sites automatically and keep a historical record of changes. Depending on the tool, it may also offer accessibility checks against WCAG 2.2 AA, Content Security Policy (CSP) and privacy policy scanning, AI-generated summaries, exportable reports, and other features.

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_58549 { margin-bottom: 18px; } .inpage_banner_58549 a { max-width: 510px; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } .inpage_banner_58549 { margin-bottom: 18px; } .inpage_banner_58549 a { max-width: 300px; display: block; margin: 0 auto; } }

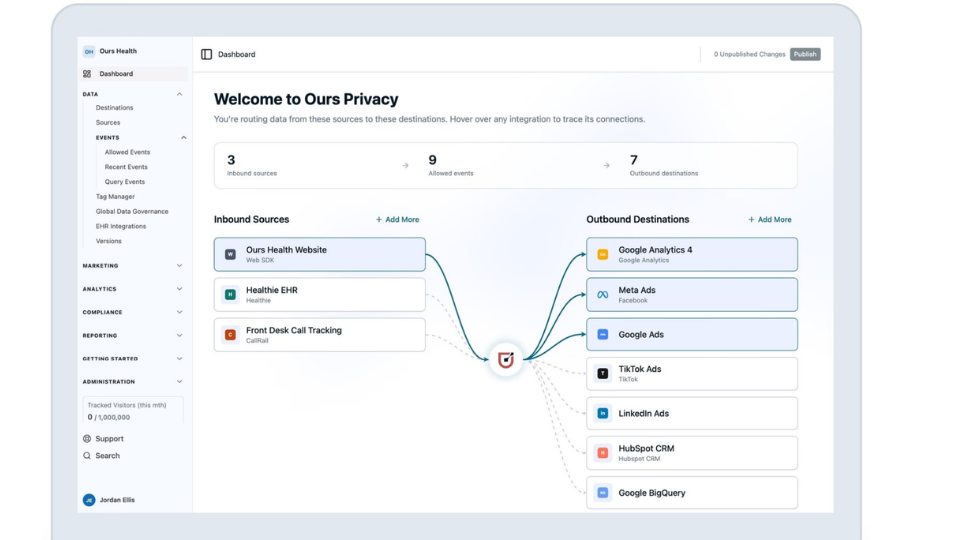
              *Web Scan report provided using Ours Privacy technology

Ours Privacy CDP Dashboard

The post Is Your Website Sharing Patient Data With Trackers? How to do a Web Scan appeared first on The HIPAA Journal.

Free Webinar Today: Is AI Putting Your Practice at Risk?

HIPAA Rusk analysis security risk assessment toolAI tools are already in your practice. The question is whether you know about them and whether they are HIPAA-compliant. 

Most practices are using AI in some form already, whether it’s an EHR feature, a note-taking assistant, or a chatbot tool; however, they may not be aware of all locations where AI is used.

Join Ryan Boudreau, Senior VP of Operations at the healthcare compliance company Abyde, as he walks you through where AI may already be hiding in your practice, the HIPAA and privacy risks it creates, and a simple framework for using AI while remaining HIPAA-compliant. 


Live Webinar: Wednesday, Sept 30 

12:00-1:00 PM ET | 11:00 AM-12:00 PM CT | 10:00-11:00 AM MT | 9:00-10:00 AM PT

 A recording will be made available to anyone who registers but is unable to attend the live event.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy


Attendees will discover:

  • Where AI is most likely already in use in your practice, including the places you didn’t realize
  • A simple, four-question framework for evaluating any AI tool before you use it
  • The fine print that matters in vendor agreements to help avoid risk
  • Real-world cautionary tales on improper AI use in healthcare

Speaker: 

Ryan BoudreauRyan Boudreau – Senior Vice President of Operations 

Ryan Boudreau is the Senior Vice President of Operations at Abyde, where he leads a team of HIPAA and OSHA compliance experts. A cybersecurity and risk management veteran with nearly 15 years of experience, his team that has successfully navigated hundreds of OCR investigations on behalf of their clients.

Abyde is a leader in the compliance software industry, streamlining HIPAA & OSHA requirements for thousands of practices across the United States.


Live Webinar

Wednesday, Sept 30  | 12:00–1:00 PM ET | 11:00 AM–12:00 PM CT | 10:00–11:00 AM MT | 9:00–10:00 AM PT

 A recording will be made available to anyone who registers but is unable to attend the live event.

The post Free Webinar Today: Is AI Putting Your Practice at Risk? appeared first on The HIPAA Journal.

Free Webinar Recording: Inside 250 HIPAA Investigations – What You Need to Know

Free Webinar Inside a HIPAA InvestigationLearn exactly what happens during a HIPAA investigation. Understand where organizations fail so you can avoid government fines and drawn-out investigations.

Based on real experience from over 250 actual OCR investigations.

When it comes to HIPAA investigations, many organizations lean on the hope that they will never be implicated. But, with the rise of ransomware breaches and patient complaints, your organization is much more likely to end up in the crosshairs of the Office for Civil Rights (OCR) than you might expect. 

While you can’t always prevent breaches from occurring, you can control your preparedness for everything that follows when it comes to your HIPAA compliance posture. 

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

Join Jake Dewberry, Chief Legal Officer, and Ryan Boudreau, Senior Vice President of Operations from Abyde, as they walk through the details of what an investigation actually looks like and where organizations fail based on their experience in over 250 OCR investigations. They will be sharing real (redacted) examples from past investigations, detailing what the OCR asks for, how to respond safely, and how others failed so you can avoid government fines and drawn-out investigations. 


On Demand Webinar Recording

August 19th Event Ended – Available on Demand 


 A recording will be made available to anyone who registers but is unable to attend the live event.


Attendees discover:

  • What triggers an investigation
  • What to do immediately after receiving an investigation letter
  • A breakdown of what the OCR is really asking for, including the most commonly missed requirement
  • Best practices for building your response
  • The possible results of an investigation
  • Real examples of investigation letters

Speakers: 

Jake Dewberry Jake Dewberry – Chief Legal Officer

Jake Dewberry serves as the Chief Legal Officer at Abyde. With over 14 years of experience in the healthcare industry, Jake has worked closely with hospitals and small to mid-sized practices across the country, helping them navigate the evolving world of healthcare technology and regulatory requirements. Jake is also a licensed attorney based in Florida. At Abyde, he wears multiple legal hats — from advising clients during breach responses and audits, to managing the company’s day-to-day legal operations, and staying on top of federal and state regulatory changes impacting HIPAA and OSHA compliance.


Ryan BoudreauRyan Boudreau – Senior Vice President of Operations 

Ryan Boudreau is the Senior Vice President of Operations at Abyde, where he leads a team of HIPAA and OSHA compliance experts. A cybersecurity and risk management veteran with nearly 15 years of experience, his team has successfully navigated hundreds of OCR investigations on behalf of their clients.

Abyde is a leader in the compliance software industry, streamlining HIPAA & OSHA requirements for thousands of practices across the United States.


On Demand Webinar Recording

August 19th Event Ended – Available on Demand

 A recording will be made available to anyone who registers but is unable to attend the live event.

The post Free Webinar Recording: Inside 250 HIPAA Investigations – What You Need to Know appeared first on The HIPAA Journal.

Free Webinar Tomorrow: Inside 250 HIPAA Investigations – What You Need to Know

Free Webinar Inside a HIPAA InvestigationLearn exactly what happens during a HIPAA investigation. Understand where organizations fail so you can avoid government fines and drawn-out investigations.

Based on real experience from over 250 actual OCR investigations.

When it comes to HIPAA investigations, many organizations lean on the hope that they will never be implicated. But, with the rise of ransomware breaches and patient complaints, your organization is much more likely to end up in the crosshairs of the Office for Civil Rights (OCR) than you might expect. 

While you can’t always prevent breaches from occurring, you can control your preparedness for everything that follows when it comes to your HIPAA compliance posture. 

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

Join Jake Dewberry, Chief Legal Officer, and Ryan Boudreau, Senior Vice President of Operations from Abyde, as they walk through the details of what an investigation actually looks like and where organizations fail based on their experience in over 250 OCR investigations. They will be sharing real (redacted) examples from past investigations, detailing what the OCR asks for, how to respond safely, and how others failed so you can avoid government fines and drawn-out investigations. 


Live Webinar: Wednesday, August 19

12-1 pm ET | 11-12 am CT | 10-11 am MT | 9-10 am PT


 A recording will be made available to anyone who registers but is unable to attend the live event.


Attendees will discover:

  • What triggers an investigation
  • What to do immediately after receiving an investigation letter
  • A breakdown of what the OCR is really asking for, including the most commonly missed requirement
  • Best practices for building your response
  • The possible results of an investigation
  • Real examples of investigation letters

Speakers: 

Jake Dewberry Jake Dewberry – Chief Legal Officer

Jake Dewberry serves as the Chief Legal Officer at Abyde. With over 14 years of experience in the healthcare industry, Jake has worked closely with hospitals and small to mid-sized practices across the country, helping them navigate the evolving world of healthcare technology and regulatory requirements. Jake is also a licensed attorney based in Florida. At Abyde, he wears multiple legal hats — from advising clients during breach responses and audits, to managing the company’s day-to-day legal operations, and staying on top of federal and state regulatory changes impacting HIPAA and OSHA compliance.


Ryan BoudreauRyan Boudreau – Senior Vice President of Operations 

Ryan Boudreau is the Senior Vice President of Operations at Abyde, where he leads a team of HIPAA and OSHA compliance experts. A cybersecurity and risk management veteran with nearly 15 years of experience, his team has successfully navigated hundreds of OCR investigations on behalf of their clients.

Abyde is a leader in the compliance software industry, streamlining HIPAA & OSHA requirements for thousands of practices across the United States.


Live Webinar: Wednesday, August 19

12-1 pm ET | 11-12 am CT | 10-11 am MT | 9-10 am PT

 A recording will be made available to anyone who registers but is unable to attend the live event.

The post Free Webinar Tomorrow: Inside 250 HIPAA Investigations – What You Need to Know appeared first on The HIPAA Journal.

What is a HIPAA Audit Checklist?

A HIPAA audit checklist is a document covered entities and business associates should use to audit compliance with the standards of the HIPAA Administrative Simplification Regulations applicable to their operations.

HIPAA Audit ChecklistAn internal HIPAA audit checklist differs from an external HIPAA audit checklist inasmuch as an external HIPAA audit checklist is designed to meet specific criteria of the OCR audit protocol, CMS’ compliance review program, or a third-party’s certification requirements.

By comparison, an internal HIPAA audit checklist is a comprehensive document that covers all areas of an organization’s compliance obligations. However, as different organizations have different compliance obligations, there is no “one-size-fits-all” internal HIPAA audit checklist.

Covered entities and business associates should review the following content, determine which standards of the HIPAA Administrative Simplification Regulations apply to their operations, and develop a HIPAA internal audit checklist that meets their requirements. The checklist should then be used as a HIPAA compliance audit checklist to identify gaps in compliance and implement measures to fill gaps.

hipaa audit checklist - thehipaajournal.com

Administrative Requirements Audit Checklist

The Administrative Requirements of HIPAA (Part 162) cover areas such as Unique Health Identifiers, Transaction Rules, and Code Set Standards. Covered entities that conduct claims processing or administration in-house, and business associates that provide billing and claims management services for covered entities, are required to comply with the standards of this Part.

Generally, there are only three areas of compliance organizations may need to include on an internal HIPAA audit checklist – the operating rules, the transaction rules, and documentation.

  • Verify compliance with the operating rules for eligibility, claims status, and electronic funds transfer/remittance advice.
  • Test transactions for compliance using the Administrative Simplification Enforcement and Testing Tool (ASETT).
  • Document policies, procedures, and test results for when the documentation is required for a compliance review.

While violations of the Administrative Requirements have never yet resulted in a civil monetary penalty, CMS has the authority to fine covered entities and business associates for noncompliance with Part 162 if an organization fails a CMS HIPAA audit and subsequently fails to comply with a corrective action plan. In the year to May 2023, 51% of organizations failed compliance reviews and were issued with a corrective action plan. (Reports for 2024 and 2025 have not been published).

HIPAA Privacy Rule Audit Checklist

The HIPAA Privacy Rule only has two basic HIPAA audit requirements – to protect individually identifiable health information from impermissible uses and disclosures, and to give individuals rights over their protected health information. To comply with these two requirements, organizations subject to the HIPAA Privacy Rule must comply with up to fourteen sets of standards depending on the nature of their operations.

Why “up to” fourteen? This is because, while all covered entities are required to comply with the HIPAA Privacy Rule, some standards do not apply to all types of organizations – for example, some standards apply to only health plans. Some business associates may be required to comply with specific HIPAA Privacy Rule standards depending on the service being provided for or on behalf of a covered entity and/or on the terms of their Business Associate Agreement with the covered entity.

All organizations subject to HIPAA compliance should review the following list, determine which applies to their operations, and add the relevant items to a HIPAA compliance audit checklist.

1. Designate a HIPAA Privacy Officer

Although most organizations will be familiar with this requirement, it is essential a member of the workforce is designated the role of Privacy Officer to be the point of contact for patients/plan members, workforce members, and regulatory agencies. The HIPAA Privacy Officer also has the responsibility to develop and implement HIPAA-compliant policies and procedures.

2. Understand What Constitutes PHI

There is a lot of misunderstanding about PHI, due to which some organizations can be unnecessarily overprotective with data, while others can be a little too carefree. Not only is it important to understand what constitutes PHI; but, for the sake of security and efficiency, to develop procedures for securing PHI in the minimum number of designated record sets practical.

3. Permissible Uses and Disclosures

Make sure all members of your organization´s workforce understand the difference between required, permissible, and attestable uses and disclosures of PHI, uses and disclosures of PHI for which an individual should be given an opportunity to consent or object, and uses and disclosures of PHI for which an individual´s written HIPAA authorization is required.

4. Procedures for Obtaining Authorizations

Every covered entity should have procedures for obtaining and managing authorizations so that if an individual exercises the right to revoke an authorization, the revocation can be actioned without delay. Procedures should also exist for (for example) withdrawing any information about the patient that has been used in fundraising or marketing material.

5. Notices of Privacy Practices

Every patient or plan member must be given a Notice of Privacy Practices when first attending a healthcare facility or enrolling in a health plan. The Notice must contain details of how PHI may be used or disclosed without an authorization, when it may only be used with the individual´s authorization, the rights of the individual to request privacy protection or copies of PHI.

6. Procedures for Responding to Requests for Privacy Protection

Individuals have the right to request restrictions on certain uses and disclosures – which can be situation-specific – and request to restrict how they are contacted by a covered entity or business associate. Organizations must have procedures in place to respond to requests for privacy protection, manage requests, and document oral terminations of requests.

7. Procedures for Responding to Requests for Access, Correction, and Transfer

The failure to provide access to health information, correct it when necessary, and transfer it to other providers when requested is one of the leading causes of complaints to HHS’ Office for Civil Rights. In an attempt to reduce the number of complaints, the agency is increasing its enforcement action against organizations that fail to respond to requests in a timely manner.

8. Procedures for Maintaining an Accounting of Disclosures

Individuals have the right to request an accounting of disclosures of their PHI for the six years prior to the request being made. However, not all disclosures have to be accounted for. It is important that covered entities understand which disclosures have to be accounted for and adopt procedures for maintaining an accounting of disclosures for each individual.

9. Workforce Training

Under the Privacy Rule, the training requirements are limited in scope to members of the workforce to whom HIPAA policies and procedures apply. However, basic HIPAA training should be provided to all members of the workforce in order to mitigate the risk of impermissible disclosures due to a lack of knowledge and reduce the risk of human error.

10. Documentation

Documentation is a requirement of nearly every standard in the HIPAA Privacy Rule, and organizations required to comply with the standards must put procedures in place for documenting policies and procedures, Notices of Privacy Practices, individual authorizations, workforce training, etc., and retaining policies and procedures for at least six years since they were last in force.

Organizations subject to the HIPAA Privacy Rule should also review the General Provisions of Part 164 – a section of the Administrative Simplification Regulations not covered by a “Rule”. These provisions primarily apply to Hybrid Entities, Affiliated Entities, and Organized Health Care Arrangements, and cover restricting access to PHI to only those who are authorized to access it within their roles and safeguarding PHI from non-covered areas of the organization.

HIPAA Security Rule Audit Checklist

Compared to the potential complexity of a HIPAA Privacy Rule audit checklist, a HIPAA Security Rule audit checklist is relatively straightforward. Not only does the HIPAA Security Rule contain far fewer standards than the HIPAA Privacy Rule, but the standards within the HIPAA Security Rule are less open to interpretation. The Security Standards General Rules also allow covered entities and business associates a “flexibility of approach” about how the standards are implemented.

To help organizations compile a HIPAA audit checklist for the HIPAA Security Rule, the Office of the National Coordinator for Health Information Technology (ONC) and HHS’ Office for Civil Rights have jointly produced a HIPAA Security Risk Assessment (SRA) Tool. Organizations can use the tool online or download as an Excel document to fulfill the risk assessment requirements of the Security Rule. However, this tool may not be suitable for all organizations; and before using it, it is advisable to consider the following questions:

1. Has your organization designated a HIPAA Security Officer?

This can be the same person as the HIPAA Privacy Officer but they need to be qualified for the position inasmuch as they have to design, implement, and enforce security policies and procedures. Ideally, it is best to designate this role to a senior member of the IT team.

2. Have you identified from where ePHI originates?

In order to protect ePHI from unauthorized access, disclosure, alteration, or deletion, you have to know from where ePHI originates, where it is maintained, and to where it is transmitted. Effectively, you need to create an audit trail for all ePHI in your organization´s possession.

3. Do you know how users access ePHI?

Before using the ONC/OCR Security Risk Assessment Tool, you need to conduct an inventory of devices used to access ePHI and the media on which it is stored. This not only includes onsite devices and servers, but also devices used to access ePHI remotely.

4. What security software is already in place?

As a covered entity or business associate, you are required to implement measures to mitigate threats from malware, ransomware, and phishing. Many organizations already have security measures – such as email and web filters – in place to mitigate threats.

5. What role-based access controls are already in place?

Similar to the previous item, many organizations already utilize role-based access controls to control what information users can access. It is far easier to adjust existing controls to comply with the Security Rule standards than start from scratch.

6. What other security mechanisms do you already use?

Due to the “flexibility of approach” clause and the fact that some implementation specifications are addressable, it may be possible to comply with many HIPAA Security Rule standards by enforcing the use of existing security mechanisms – i.e., PIN lock, automatic log-off, password managers, etc.

7. What processes already exist for reporting security incidents?

Most organizations should already have processes in place to flag suspect emails, malware, and other anomalies. These are usually sufficient for internal compliance with the HIPAA Security Rule – not forgetting that business associates are required to report all security incidents to covered entities.

8. Does the organization already have a security awareness training program?

The likelihood is that most organizations will have some form of security awareness training, and all that may be necessary for the training to meet the General Requirements of the HIPAA Security Rule (§164.406) is to tweak it to be more HIPAA-centric and ensure the training is documented.

9. Does the organization enforce a scaled sanctions policy?

Enforcing a scaled sanctions policy is an important step toward HIPAA compliance because it serves as a reminder to members of the workforce that minor or repeated violations of HIPAA can have consequences.

10. Does the organization have a contingency or emergency action plan?

Developing a contingency plan for foreseeable emergency events that may threaten the confidentiality, integrity, and availability of ePHI is a requirement of HIPAA. You may need to review the SRA Tool to ensure you have every type of emergency covered.

Although this HIPAA Security Rule HIPAA audit checklist is relatively basic with regards to the questions it asks, it is advisable to start a journey to HIPAA compliance by assuming zero knowledge – rather than assuming an existing degree of knowledge as the SRA Tool does. In addition, when implementing new measures, it is a best practice to test members of the workforce on what information they have absorbed rather than assume they have understood the new measures in one explanation.

HIPAA Audit Log Requirements

Whether you use a HIPAA Security Rule Audit Checklist or the SRA Tool, it is important not to overlook the HIPAA audit log requirements. The HIPAA Security Rule requires covered entities and business associates to implement hardware, software, and/or procedural mechanisms that record and examine activity in information systems that contain or use electronic Protected Health Information.

Audit logs enable covered entities and business associates to identify risks associated with events such as unauthorized access, impermissible disclosures, application flaws, and suspicious activities. They can also be used to provide forensic evidence following a security incident or data breach so measures can be put in place to prevent a reoccurrence.

The HIPAA Security Rule does not specify what data needs to be collected by audit logs or how frequently logs should be reviewed. HHS also acknowledges that different software solutions and applications record and examine system activity in different ways. For this reason, it can be beneficial for covered entities and business associates to implement HIPAA compliance software that can monitor all system activity and flag issues for further investigation.

Breach Notification Rule Audit Checklist

As business associates are required to notify covered entities of all security incidents (not just those that result in a breach of unsecured ePHI), business associates will need to use a different Breach Notification Rule audit checklist than a covered entity – who can use a HIPAA breach notification tool to determine whether a security incident is reportable or not. However, both Breach Notification Rule audit checklists will share some common items – for example:

  • How did the breach/security incident occur?
  • How has the impact of the breach/security incident been mitigated?
  • What should be done to prevent the breach/security incident from happening again?

It is also the case that procedures should be in place and responsibilities assigned for notifying covered entities of a security incident or for covered entities notifying HHS’ Office for Civil Rights and impacted individuals of a breach of unsecured ePHI. As with all other areas of HIPAA compliance, the procedures, all breaches/security incidents, and their outcomes must be documented and the documentation retained for a minimum of six years.

Advice for Developing and Completing HIPAA Audit Checklists

Integrating every element of HIPAA compliance into a single HIPAA audit checklist can be challenging and – due to the checklist’s comprehensiveness – potentially leave gaps that lead to compliance failures. There are two ways to overcome this challenge. Either divide the HIPAA audit checklist into smaller, more manageable units, or engage the services of a compliance professional to help you with both the development and the completion of the checklist.

One of the advantages of choosing the latter option is that compliance professionals have the experience to assess an existing checklist, determine how much help you need, and provide as much help as necessary to produce an accurate and comprehensive checklist. This approach has the benefit of preventing the scenario in which you are looking for threats that do not exist in standards that do not apply to your organization – saving your time and your organization’s money.

FAQs

What are the HIPAA Administrative Simplification Regulations?

The HIPAA Administrative Simplification Regulations are the “Administrative Data Standards and Other Requirements” that were developed as a result of the passage of HIPAA (Title 45, Subtitle A, Subchapter C of the Code of Federal Regulations).

The Regulations not only include the standards for the Administrative Requirements and the HIPAA Privacy, Security, and Breach Notification Rules, but also the General Administrative Provisions, the General Security and Privacy Provisions, and the Enforcement Rule.

Could CMS issue a civil monetary penalty for noncompliance?

The Centers for Medicare and Medicaid Services (CMS) has the same authority to impose sanctions on noncompliant organizations as HHS’ Office for Civil Rights. In theory, CMS could impose a fine of up to $2,134,831 on a covered entity or business associate who repeatedly failed to comply with the Administrative Requirements due to willful neglect.

Why are business associates required to comply with the Privacy Rule?

The applicability standard of the HIPAA Privacy Rule (§164.104) was amended via the Final Omnibus Rule in 2013 to read “Where provided, the standards, requirements, and implementation specifications adopted under this part [the HIPAA Privacy Rule] apply to a business associate.”

This means that a business associate may need to develop policies and procedures relating to permissible uses and disclosures and for managing access requests if an individual’s ePHI is maintained in a separate designated record set from that of the covered entity.

Does a business associate have to designate a Privacy Officer?

This depends on the nature of the business associate’s operations and the potential for interactions with the public and regulatory authorities. If there is likely to only be minimal interaction, the role of Privacy Officer could be designated to a Security Officer.

What is considered PHI under HIPAA?

This is possibly the most frequently asked question relating to HIPAA compliance because what is considered PHI under HIPAA is complicated – so complicated that we have dedicated a full-page article to answering this question.

Why is the ONC/OCR Security Risk Assessment Tool not suitable for all organizations?

According to the OCR’s website, “the tool’s features make it useful in assisting small and medium-sized health care practices and business associates”. This implies that it is not suitable for health plans, healthcare clearinghouses, and larger organizations.

In addition, the tool assumes a certain level of knowledge and that a number of measures have already been implemented to comply with HIPAA Security Rule standards. If your organization is taking its first steps towards HIPAA compliance, you may find the tool too advanced for your needs.

How might an organization already have role-based access controls in place?

Many organizations use identity and access management services such as Microsoft AD, Okta Lifecycle Management, or Open LDAP (etc.) to control who in the organization has access to systems and databases. These services can often be used to comply with the HIPAA Security Rule access requirements.

What is the difference between a HIPAA compliance audit checklist and a healthcare compliance audit checklist?

The difference between a HIPAA compliance audit checklist and a healthcare compliance audit checklist is that a HIPAA compliance checklist helps organizations audit their compliance with HIPAA, while a healthcare compliance checklist helps organizations audit their compliance with all applicable federal, state, and local regulations related to their healthcare activities (i.e., CMS’ Medicare regulations, OSHA workplace regulations, and state licensing requirements).

What are 3 important components of a HIPAA security audit?

All components of a HIPAA security audit are important. However, the 3 elements of a HIPAA security audit most organizations should focus on include:

  • An inventory and audit trail of ePHI. If you do not know where ePHI originates, where it is stored, how it is used, and how it is disclosed, it will be impossible to implement measures to safeguard the confidentiality, integrity, and availability of health information.
  • The implementation and configuration of software. It is often not sufficient to implement software described as “HIPAA compliant” to comply with the HIPAA Security Rule. The software also has to be configured to mitigate threats to health information.
  • Workforce training and compliance monitoring. All members of the workforce must receive security awareness training even when they do not have access to ePHI. It is also important to monitor compliance with the security awareness training.

The post What is a HIPAA Audit Checklist? appeared first on The HIPAA Journal.
Free Webinar TODAY: AI + HIPAA: Innovating in Healthcare Without Leaving Compliance Behind

Artificial intelligence has tremendous potential in healthcare, and healthcare organizations have embraced AI tools in all areas of their operation; however, there are compliance risks associated with AI when tools engage with health information protected under the Health Insurance Portability and Accountability Act (HIPAA). Incorporating AI tools while complying with all HIPAA Privacy and Security Rule implementation specifications can be challenging, especially when there is limited guidance on how HIPAA applies to AI.

Fortunately, help is at hand. On July 8, 2026, the HIPAA-compliant communication platform provider Paubox is hosting a webinar where healthcare organizations can learn from a diverse panel of experts about AI-related HIPAA compliance challenges and receive invaluable advice on how to keep innovating without leaving HIPAA compliance behind.

During the webinar, attendees will learn about how real-world healthcare teams are developing and implementing AI tools and the challenges they have faced, the specific questions you need to be asking any AI vendor before you sign and handle business associate agreements (BAAs), what responsible use of AI with PHI looks like, and what the future holds, and what you need to do right now.  At the end of the webinar, there will be time allocated for a Q&A with the panel to get answers to your questions.

Speakers:

Heather Phillips, FoXX Health

Heather Phillips – Advisory Committee Member, FoXX Health
Tim Gutwald - Partner, Elevare Law Tim Gutwald – Partner, Elevare Law
Brittany Sigler - DrPH, Founder & Product Leader, Bright Signal Consulting Brittany Sigler – DrPH, Founder & Product Leader, Bright Signal Consulting
Mike Maseda - Head of Sales & Ops, GenHealth.ai Mike Maseda – Head of Sales & Ops, GenHealth.ai

Webinar Details

AI + HIPAA: Innovating in Healthcare Without Leaving Compliance Behind

July 8, 2026

1.00 p.m. ET | 12.00 p.m. CT | 11.00 a.m. MT | 10:00 a.m. PT

Click Here to Register for the Webinar

Can’t attend on the day? Register to receive a link to the recording!

This webinar is eligible for 1 self-reported CPE

The post Free Webinar TODAY: AI + HIPAA: Innovating in Healthcare Without Leaving Compliance Behind appeared first on The HIPAA Journal.

Free Webinar: How to Stop Phishing Attacks Before They Reach Your Team

webinar - how to stop healthcare phishing attacksPhishing has long been a leading cause of healthcare data breaches. Hackers target employees as they are a weak link in the security chain, and many healthcare ransomware attacks start with credentials stolen in phishing attacks.
Phishing attacks are often blamed on the employees who respond to phishing attempts. A survey of healthcare IT leaders found 85% of respondents believe employee negligence is a top email security risk, yet despite that, only 16% of respondents said they train their workforce on how to recognize phishing attempts quarterly or more frequently. The majority of healthcare organizations only provide training to their workforce once a year, and hope that the training sticks and employees will remain vigilant throughout the year, which is seldom the case.

Unfortunately, the risk from phishing is getting worse as AI-generated phishing campaigns are difficult for employees to identify. AI-generated phishing emails are grammatically correct, free of spelling mistakes, and use advanced impersonation techniques. An analysis of phishing emails by KnowBe4 between late 2024 and early 2025 found that 83% of phishing emails were AI-generated.  Not only is AI-generated phishing outpacing training programs, the phishing emails also bypass traditional email spam filters. Further, Paubox research shows that when employees do identify phishing attempts, only 5% of attacks are reported to the security team! If you rely on employee training and a traditional email filter, your organization is at risk.

In this free webinar on April 28, 2026, discover why phishing defenses are failing and how you can improve your security posture and block attacks before they reach your team. The webinar is aimed at IT directors, CISOs, security leaders responsible for email infrastructure, compliance officers managing HIPAA email requirements, healthcare administrators who oversee PHI-handling workflows, and security teams weighing whether current controls match current threats.

Webinar attendees will learn about:

  • The evolution of AI-generated phishing and BEC attacks and why they bypass defenses
  • Why healthcare organizations are targeted
  • The findings of a Paubox analysis of 170 email-related data breaches in 2025 and common authentication gaps
  • How the “training plus spam filter” model leaves measurable security gaps
  • How inbound email security at the technical layer catches what training and traditional filters miss
  • How to assess where your organization’s email security actually stands today

WEBINAR DETAILS

How to Stop Phishing Attacks Before They Reach Your Team

Tuesday, April 28, 2026

10 a.m. PT | 11 a.m. MT | 12 p.m. CT | 1 p.m. ET | 6 p.m. BST

Register for the Webinar


Speaker: Dawn Halpin, Demand Generation Manager, Paubox

Dawn Halpin, Paubox

Dawn Halpin, a Marquette University and University of Wisconsin-Milwaukee graduate, is the Demand Generation Manager at the email security firm Paubox. Paubox is a leader in HIPAA-compliant email security for the healthcare industry and is trusted by more than 8,000 organizations, including Cost Plus Drugs, Rippling, and Covenant Health.

The post Free Webinar: How to Stop Phishing Attacks Before They Reach Your Team appeared first on The HIPAA Journal.