Healthcare Cybersecurity

Cybersecurity Awareness Month 2026: Critical Infrastructure Urged to Adopt Cybersecurity 3Rs

October is Cybersecurity Awareness Month, a global effort to promote online safety and digital security. Launched in 2024 by the National Cybersecurity Alliance and the Cybersecurity and Infrastructure Security Agency (CISA), the aim is to teach individuals and organizations practical steps to improve resilience to cyber threats. The general theme this year is Don’t Make It Easy for Them, which focuses on everyday digital safety habits that everyone should adopt to improve online safety and security, such as using strong, unique passwords, implementing multifactor authentication (MFA), learning to recognize and avoid phishing, and keeping operating systems, software, applications, and devices up to date.

A dual theme of this year’s Cybersecurity Awareness Month is strengthening critical infrastructure cybersecurity. Securing the nation’s critical infrastructure is a top national security priority under the White House March 2026 Cyber Strategy for America. As the United States celebrates the semiquincentennial anniversary of the nation’s founding, a rallying cry has been issued to future-proof the nation’s critical infrastructure and secure it for the next 250 years.

Critical infrastructure relies heavily on internet-connected systems and devices. Internet access improves efficiency, but it also introduces risks, as Internet-exposed systems, software, and devices can potentially be remotely attacked by cybercriminal actors, hacktivists, and hostile nation-states. Financially motivated criminal threat actors attack vulnerable systems and hold systems and data to ransom; hacktivists may target critical infrastructure in response to governmental policies; and nation-state actors steal intellectual property to accelerate their own economic growth and technological dominance, and conduct destructive attacks to further their nations’ political priorities. Critical infrastructure owners and operators need to defend against these attacks and ensure they can recover quickly should an attack succeed.

The 3Rs of Cybersecurity – Reduce, Replace, Recover

This Cybersecurity Awareness Month, critical infrastructure owners and operators have been requested to practice the 3Rs of cybersecurity – Reduce, Replace, Recover – to improve cyber resilience. Critical infrastructure should improve their efforts to reduce the attack surface by ensuring that systems are kept up to date, patches are applied promptly, and obsolete software and devices are upgraded or replaced before they reach end of life. Plans also need to be developed, implemented, maintained, and practiced to ensure operations can be sustained in the event of a cyber incident and that they can recover quickly from a successful attack.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

While the threat landscape is constantly evolving, CISA points out that it isn’t fundamentally changing; rather, it is scaling. Threat actors constantly search for vulnerabilities to exploit, as has been the case for many years; however, vulnerabilities are being discovered in record numbers. Total published Common Vulnerabilities and Exposures (CVE) this year exceeded last year’s total by the end of August 2026.

Artificial intelligence is accelerating the discovery of software vulnerabilities and is helping threat actors to exploit vulnerabilities far more quickly, including mass exploitation through automation. Since defenders can easily get overwhelmed with the sheer number of vulnerabilities that require remediation, the key approach is to patch smarter, not harder. Vulnerabilities need to be assessed, and remediation efforts prioritized, ensuring that the most critical vulnerabilities are addressed first, such as those listed in the Known Exploited Vulnerability (KEV) Catalog.

When software and devices reach end-of-life, security updates and patches come to an end. Continued use of end-of-life software and devices presents threat actors with opportunities to exploit unaddressed vulnerabilities to gain access to networks and sensitive data. Critical infrastructure owners and operators need to know when support will end for their software and devices and plan to upgrade or replace software, firmware, and hardware devices before support comes to an end. This is especially important for any technology devices or software on the boundary of the network that are accessible from the public internet. Guidance on mitigating risk for end-of-life software and devices is available in BOD 26-02.

It is essential that operations can be sustained in the event of a cyber incident and that a rapid and full recovery is possible. Critical infrastructure owners and operators need to fortify their systems and invest in isolation and recovery capabilities. Vital systems must be isolated from harm and must be capable of continuing to operate in an isolated state, while compromised systems are recovered. CI Fortify is an allied initiative designed to ensure that critical infrastructure entities can continue to operate in the event of geopolitical cyber conflict, through the implementation of resilient OT environments capable of surviving extended isolation and cyber compromise.

All Businesses Should Take Steps to Improve Their Security Posture

Critical infrastructure is supported by a diverse range of businesses, and vendors in the supply chain that are directly or indirectly involved with critical infrastructure are often targeted by threat actors, as they are often a weak link in the security chain. This Cybersecurity Awareness Month, CISA is encouraging all businesses to assess their security posture and implement key cybersecurity best practices, starting with basic, high-impact measures to defend their networks and data:

  • Provide phishing education to the workforce
  • Strengthen password requirements
  • Implement multifactor authentication
  • Update business software and patch promptly

With those foundational security requirements in place, businesses should expand their security capabilities by implementing the following measures:

  • Log system activity on all business systems
  • Back up business data
  • Encrypt data at rest and in transit
  • Develop and implement an incident response plan
  • Report all cyber incidents to CISA
  • Prepare for system disruptions

The post Cybersecurity Awareness Month 2026: Critical Infrastructure Urged to Adopt Cybersecurity 3Rs appeared first on The HIPAA Journal.

Democratic Senators Reintroduce the Health Infrastructure Security and Accountability Act

On September 17, 2026, two Democratic Senators reintroduced the Health Infrastructure Security and Accountability Act, which seeks to improve cybersecurity standards for the U.S. healthcare system and make funds available to help rural and underserved hospitals invest in essential cybersecurity measures.

The bill was reintroduced by Sens. Mark R. Warner (D-VA) and Ron Wyden (D-OR), following its initial introduction in the 118th Congress 2D Session on September 25, 2024. When the bill was first introduced, 394 large hacking-related healthcare data breaches had been reported to the Department of Health and Human Services Office for Civil Rights (OCR), involving the protected health information of 43 million Americans.

At the time, the senators explained that cyberattacks are delaying and disrupting patient care, harming patient health and national security, and putting Americans at risk of identity theft and fraud. “These hacks are entirely preventable and are the direct result of lax cybersecurity practices by health care providers and their business partners,” explained the Senators.

The situation has only worsened in the two years since the bill was first introduced. The OCR breach portal lists year-to-date figures (Jan 1 – Aug 31) of 426 hacking-related breaches, involving the protected health information of 73 million Americans. That’s an 8% increase in hacking-related data breaches and a 70% increase in affected individuals.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

On January 24, 2024, OCR published two sets of voluntary cybersecurity performance goals (CPGs) for the healthcare and public health (HPH) sector – Essential and Enhanced – that consist of high-impact measures that should be adopted by healthcare organizations to strengthen and mature their cybersecurity programs. As predicted by OCR at the time, voluntary goals alone would not be enough to drive the behavioral changes needed across the sector to improve cybersecurity.

The CPGs were followed by a proposed update to the HIPAA Security Rule, which mandates significant additional cybersecurity requirements. The proposed update has proven hugely unpopular, with industry groups and health systems calling for the proposed rule to be scrapped. A final rule has been delayed until July 2027, although a final decision about whether a final rule will actually be released has yet to be made by the Trump administration. Part of the problem, especially for rural and other low-resource healthcare providers, is a lack of funding to make the necessary cybersecurity improvements, which is something that the Health Infrastructure Security and Accountability Act seeks to address.

“As cybercriminals ramp up their attacks on hospitals and health care providers, it’s becoming increasingly clear that voluntary standards are not enough to protect Americans’ health, safety, and privacy,” explained Sen. Warner. “This legislation would establish strong, commonsense cybersecurity protocols for health care entities, while also getting resources to rural and underserved hospitals to strengthen their defenses and protect the patients who depend on them.”

As the Senators explained, the U.S. health care system is particularly at risk for cyberattacks due to its size, technological dependence, collection of sensitive personal information, and unique vulnerability to disruptions. Healthcare organizations are viewed as low-hanging fruit, and attacks can be highly profitable for cybercriminals. “The frequency and sophistication of cyberattacks has dramatically increased in every part of the health care system, and will only grow,” said Sen. Wyden. “Our bill creates national cybersecurity standards for health care providers and devotes resources, especially in rural and underserved areas, to ensure every American’s medical information is secure. Congress cannot wait to act until another catastrophic cyberattack compromises the safety and privacy of American families’ most personal information.”

The 2026 Health Infrastructure Security and Accountability Act remains largely unchanged from the 2024 version, other than shifting the timeline forward by two years. The key requirements of the bill are:

  • Mandatory minimum cybersecurity standards for covered entities and business associates, established, enforced, and updated by the HHS. Updates are required at least every two years.
  • Heightened cybersecurity standards for systemically important entities and entities critical to national security.
  • Continuity/recovery plans for all covered entities for technical failures, disruptive cyber events, and natural disasters, and stress tests to evaluate whether the entity has the capabilities to recover essential functions.
  • Written annual statements signed by the chief executive officer and chief information security officer attesting that the company is compliant with applicable security standards.
  • Mandatory annual security risk analyses, including specific assessments of the extent to which the entity is exposed to risk through its business associates.
  • Independent audits of covered entities’ security measures to assess compliance with the HHS’s CPGs.
  • Annual HHS audits of at least 20 HIPAA-regulated entities to assess data security practices, focused on those of systemic importance.
  • Increased financial penalties under HIPAA for failing to meet security requirements – A minimum $500 penalty for no knowledge; $5,000 for reasonable cause; $50,000 for willful neglect (corrected); and $250,000 for willful neglect (uncorrected).
  • A government investment of $1.3 billion to help hospitals strengthen cybersecurity: $800 million in up-front investment for hospitals in rural and underserved urban communities to adopt the essential cybersecurity goals, and $500 million in incentives available to all hospitals to adopt the enhanced CPGs.
  • Medicare accelerated and advanced payments in response to cybersecurity incidents.

The post Democratic Senators Reintroduce the Health Infrastructure Security and Accountability Act appeared first on The HIPAA Journal.

Conti Ransomware Member Sentenced to 4 Years in Jail

A Ukrainian national who deployed Conti ransomware on the networks of at least 12 organizations in the United States and other countries has been sentenced to four years in jail for his role in the attacks. The Conti ransomware group was a major ransomware operation that engaged in double extortion tactics, breaching victims’ networks, stealing sensitive data, and encrypting devices for financial gain. The Conti ransomware operation emerged after the shutdown of the Ryuk ransomware group in 2020 and was active until 2022. During that time, the group conducted ransomware attacks on an estimated 1,000 entities in 31 foreign countries, 47 U.S. states, the District of Columbia, and Puerto Rico.

While some ransomware groups prohibited attacks on healthcare providers, Conti had no such restrictions and actively targeted healthcare organizations. The group reached peak activity in 2021, when many critical infrastructure entities were attacked, including the Health Service Executive in Ireland and many U.S. hospitals, such as Scripps Health in San Diego. According to the U.S. Department of Justice (DoJ), the Conti ransomware group collected an estimated $150 million in ransom payments as of January 2022.

Oleksii Oleksiyovych Lytvynenko, 44, formerly of Cork, Ireland, was arrested in Ireland in July 2023 by the Irish national police and was extradited to the United States last year to face trial. Lytvynenko was accused of being a developer of malicious tools used by the Conti ransomware operation, breaching the networks of at least 12 companies, and exfiltrating and storing stolen data.

Lytvynenko admitted to being a member of the Conti ransomware operation since September 2021, controlling stolen data from eight victims in the United States and four victims in foreign countries, and issuing ransom demands. Lytvynenko was a member of a team run by a co-conspirator and developed loader malware, which was used by the group to load malicious software on victims’ networks. In June 2026, Lytvynenko pleaded guilty to one count of conspiracy to commit wire fraud and has been awaiting sentencing, which could have been a maximum of 20 years in jail. On September 10, 2026, Lytvynenko was sentenced to four years in federal prison.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

“Ransomware attacks like Conti cause real harm to businesses, institutions, and families here at home and around the world,” said U.S. Attorney Braden H. Boucek for the Middle District of Tennessee. “Today’s sentence demonstrates that cybercriminals cannot hide behind borders or a keyboard to escape justice. We are grateful to our law enforcement and international partners whose work made this result possible.”

Four other Conti co-conspirators – Russian nationals Maksim Galochkin, Maksim Rudenskiy, Mikhail Mikhailovich Tsarev, and Andrey Yuryevich Zhuykov – have also been indicted for their role in Conti ransomware attacks and have criminal charges pending in the Middle District of Tennessee.

The post Conti Ransomware Member Sentenced to 4 Years in Jail appeared first on The HIPAA Journal.

Orthanc DICOM Server Vulnerability Can Lead to Denial of Service

A high-severity vulnerability has been identified in Orthanc DICOM Server that could be exploited by an authenticated remote attacker to write past the end of a heap allocation and crash an Orthanc process in a denial-of-service attack.

Orthanc DICOM Server is a free-to-use, standalone, open-source, lightweight DICOM server that is used in both clinical and research environments. It can complement or act as a gateway to existing PACS systems, and was developed to improve interoperability and workflow efficiency.

An integer overflow in a specified pitch and buffer-size computation results in a heap out-of-bounds write when Orthanc decodes a specially crafted PNG or JPEG image file, causing a crash and denial-of-service condition.

The vulnerability is tracked as CVE-2026-87020 and has been assigned a CVSS v3.1 base score of 8.1 and a CVSS v4.0 base score of 7.2. The vulnerability was identified by penetration tester Andrej Tomci, who reported the issue to the Cybersecurity and Infrastructure Security Agency.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The vulnerability affects all Orthanc DICOM Server prior to 1.13.0. Orthanc has fixed the vulnerability in version 1.13.0. and later versions.  Users are advised to verify the installed Orthanc DICOM Server version and download the latest version if a vulnerable version is in use. It is also recommended to restrict network access to Orthanc instances to trusted hosts only.

The post Orthanc DICOM Server Vulnerability Can Lead to Denial of Service appeared first on The HIPAA Journal.

High Severity Vulnerabilities Identified in NextGen Healthcare Mirth Connect

Three high-severity vulnerabilities have been identified in NextGen Healthcare Mirth Connect (Mirth Connect), a cross-platform healthcare integration engine for connecting, routing, transforming, and exchanging clinical and administrative data between different healthcare systems. The vulnerabilities are due to improper neutralization of special elements used in SQL commands and improper restriction of XML External Entity Reference. Successful exploitation of the vulnerabilities could allow denial-of-service attacks and data exfiltration.

CVE-2026-82583 could be exploited by an authenticated user to execute arbitrary SQL through a Database Connector API, which could result in the disclosure of stored credentials for connected systems, allow arbitrary file write, and trigger a denial-of-service condition. The vulnerability has been assigned a CVSS v3.1 severity score of 8.3 (v4:0: 7.2)

CVE-2026-78224 is due to the XSLT Transformer Step building a bare TransformerFactory without the proper security options set, which could allow data exfiltration and denial-of-service attacks via XXE injection. The vulnerability has a CVSS v3.1 severity score of 8.2 (v4.0: 8.8)

CVE-2026-82578 can also allow data exfiltration and denial-of-service attacks via XXE injection. When XML batch processing is turned on and the XPath option is selected, the raw batch input goes through a default XPath/JAXP setup with no entity restrictions. The vulnerability has a CVSS v3.1 severity score of 7.5 (v4.0: 8.7)

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

All three vulnerabilities affect v4.7.1 and earlier versions. NextGen has fixed all three vulnerabilities in Mirth Connect v4.7.2. Customers have been advised to update to the latest fixed version as soon as possible. The latest version can be downloaded from the NextGen Healthcare customer portal.

The post High Severity Vulnerabilities Identified in NextGen Healthcare Mirth Connect appeared first on The HIPAA Journal.

FBI Raises Alarm About OAuth Consent Phishing Activity

The Federal Bureau of Investigation (FBI) has issued a warning about ongoing phishing activity involving a sophisticated technique known as OAuth consent phishing. Since late 2025, the FBI has observed malicious cyber actors using OAuth consent phishing in targeted attacks on prominent individuals, their family members, and personal acquaintances to gain persistent access to their accounts.

Similar to other forms of targeted phishing, the campaign involves impersonation of a trusted entity and tricks the victim into granting access to their account; however, this approach does not require the victim to disclose their username and password. The technique relies on OAuth, a commonly used authorization framework that allows websites and web applications to request access to a user’s account on another application, without exposing their login credentials.

With OAuth consent phishing, an attacker creates a malicious application and registers it with a legitimate OAuth provider. The application is configured with high-level privileges, such as the ability to access contacts, read and write emails, send emails on the user’s behalf, and more. The attacker then contacts the targeted individual via email or text and attempts to trick them into initiating the consent process.

In this campaign, the attackers typically impersonate publicly known personalities, government officials, journalists, and other high-profile individuals via a commercial messaging application (CMA). For instance, the individual is invited to take part in an event and must first verify their identity using the malicious but seemingly legitimate application.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

If the victim responds, they are presented with a legitimate permission request screen, such as for Microsoft 365, Google, or another legitimate cloud service. If the victim approves the request by clicking Allow, they provide their consent to the legitimate cloud service, which authorizes the malicious application to have the stated permissions through the provider’s authorization mechanism. The attacker is able to perform a range of malicious activities and access sensitive data without having to obtain the user’s password, and the technique bypasses multifactor authentication controls.

In practice, many users will not be aware that they have been successfully phished and will take no action. Should the victim smell a rat and change their password after granting access, the OAuth authentication token remains valid after the password change and will continue to provide the attacker with the previously granted permissions. The permissions must be revoked by removing the malicious app via the victim’s security settings.

The FBI advises users to be wary of this form of phishing and of any communications from unfamiliar phone numbers, accounts, or senders not in their contact list. Before taking any action in response to an unsolicited communication, users should first verify the identity of the sender and should only grant authorization to trusted applications. Even when the application is trusted, the requested permissions should be carefully assessed.

The post FBI Raises Alarm About OAuth Consent Phishing Activity appeared first on The HIPAA Journal.

June 2026 Healthcare Data Breach Report

In June 2026, 66 large healthcare data breaches – data breaches involving the protected health information of 500 or more individuals – were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) – a slight increase from the 64 data breaches reported in May. More than two large data breaches a day is the new normal. Over the past 12 months, an average of 65 large healthcare data breaches have been reported per day; eight years ago in 2018, large healthcare data breaches occurred at a rate of around one per day.
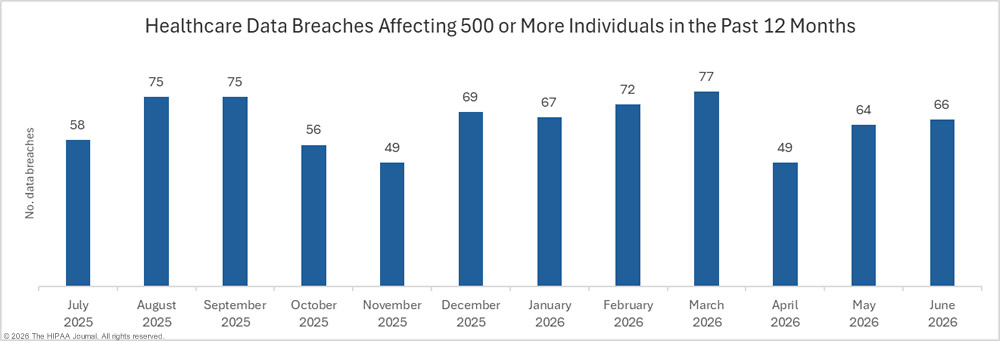
Large Healthcare data breaches in the past 12 months - June 2026

The year-to-date figures (Jan 1-Jun 30) show that healthcare data breaches are down 3.2% from the corresponding period in 2024 and down 6.4% from the corresponding period last year, although they are still occurring in significantly higher numbers than in 2022 and 2023.
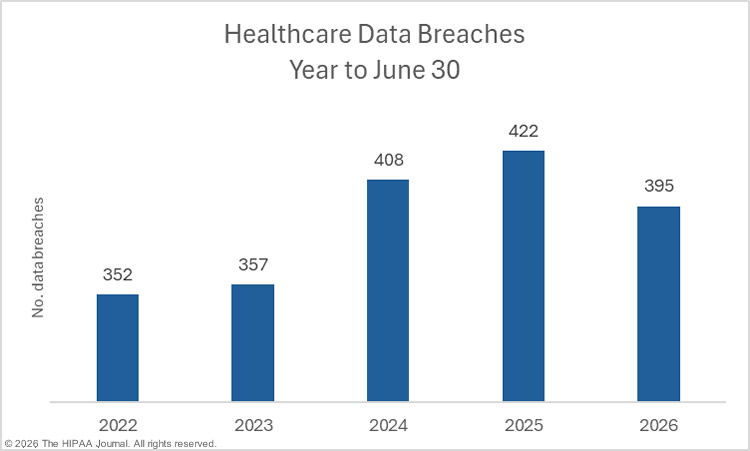
Year to date figures for large healthcare data breaches - June 2026

Across June’s 66 large healthcare data breaches, the protected health information of at least 4,499,972 individuals was exposed, stolen, or impermissibly disclosed. As data breach investigations continue, that figure is likely to increase. Based on current data, on average, 68,181 individuals were affected by each breach. The median data breach size was 6,306 individuals. While June’s victim total is substantial, the victim count is down 36.3% month-over-month, and 58.7% lower than the 12-month average of 10,906,096 individuals per month. It should be noted that the 12-month average is skewed by an unusually high total for October 2025.
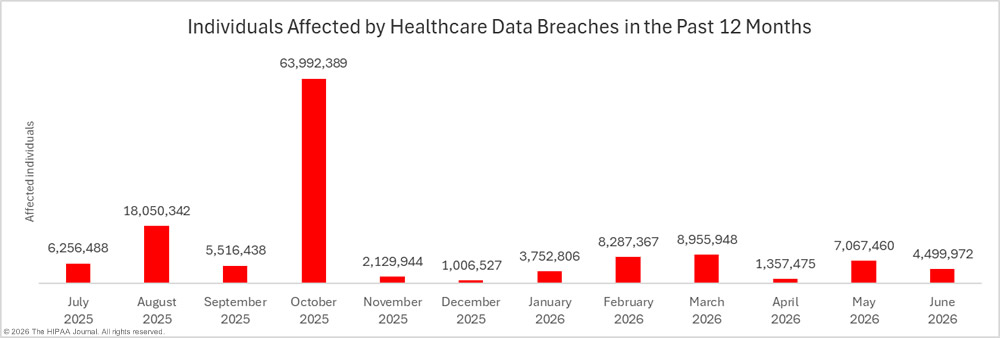
Individuals affected by large healthcare data breaches in the past 12 months - June 2026

The year-to-date figures for 2026 show a substantial improvement compared to recent years, and while almost 34 million individuals have had their protected health information exposed, stolen, or impermissibly disclosed so far in 2026, the victim count is down 37.7% from a high of 54.4 million individuals in 2024, and down 22.1% from 2025.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy
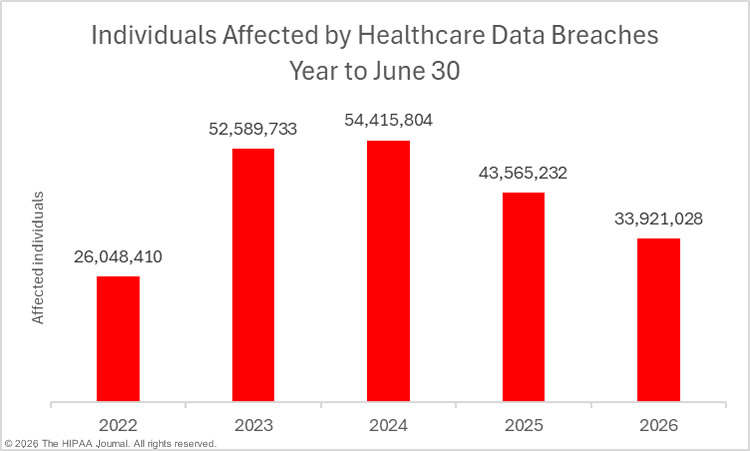
Year to date figures for individuals affected by healthcare data breaches - June 2026

The Biggest Healthcare Data Breaches Reported in June 2026

In June, 25 healthcare data breaches affecting 10,000 or more individuals were reported to the HHS. The two largest data breaches of the month occurred at business associates of HIPAA-covered entities, the largest of which was reported by Xsolis and affected almost 1.4 million individuals. Xsolis is a technology company that provides healthcare organizations with AI-powered solutions for case and utilization management. The incident occurred in January 2026 and started with a phishing email. The phishing attack provided the threat actor with access to systems and data for four days. Files exposed in the incident contained names, dates of birth, Social Security numbers, health insurance information, and medical treatment information.

The second-largest data breach of the month occurred at MCBS (Medical Computer Business Services) and affected more than 1.25 million individuals. MCBS is a healthcare billing, management, and revenue cycle management company. A data theft and extortion group called PEAR breached its network, exfiltrated files, and demanded a ransom to prevent the publication of the data. The threat group had access to the network for four days in September 2025 and stole files containing names, addresses, dates of birth, Social Security numbers, medical histories, health insurance information, and other sensitive data.

A significant breach was reported by the New Jersey-based Centers Lab NJ, a diagnostic testing laboratory for hospitals and other healthcare providers. This was also a data theft and extortion incident, involving the protected health information of more than 542,000 individuals. A threat group called Worldleaks claimed responsibility for the incident and had access to its network for 5 days in August 2025. Data stolen in the incident included names, dates of birth, Social Security numbers, passport numbers, driver’s license number/state ID numbers, medical information, and health insurance information.

HIPAA-Regulated Entity State Covered Entity Type Individuals Affected Cause of Breach
Xsolis, Inc. TN Business Associate 1,396,519 Network server hacking incident
MCBS, LLC GA Business Associate 1,261,464 Data theft and extortion incident (PEAR)
Centers Lab NJ LLC NJ Healthcare Provider 542,377 Data theft and extortion incident (Worldleaks)
Anatomic and Clinical Laboratory Associates, P.C. TN Healthcare Provider 169,626 Network server hacking incident
Operation PAR, Inc. FL Business Associate 145,714 Data theft and extortion incident (Worldleaks)
Chicago Family Health Center IL Healthcare Provider 90,000 Network server hacking incident
Aitkin County Health and Human Services MN Business Associate 83,114 Phishing incident
Minnesota Epilepsy Group, P.A. MN Healthcare Provider 80,061 Network server hacking incident
Gay & Lesbian Community Services Center of Orange County, Inc. CA Healthcare Provider 75,532 Network server hacking incident
Colorado Health Network Inc. CO Healthcare Provider 68,212 Network server hacking incident – data theft confirmed
Women’s Center for Radiology FL Healthcare Provider 66,422 Network server hacking incident
Blue Fish Pediatrics TX Healthcare Provider 62,150 Network server hacking incident
NYC Health + Hospitals NY Healthcare Provider 58,778 Hacking incident at business associate
UnitedHealth Care Services, Inc. Single Affiliated Covered Entity CT Health Plan 37,384 Phishing incident at business associate
UnitedHealth Care Services, Inc. Single Affiliated Covered Entity CT Health Plan 34,574 Network server hacking incident
Kentucky Mountain Health Alliance KY Healthcare Provider 30,830 Network server hacking incident – data theft confirmed
Center for Hearing and Speech dba Texas Hearing Institute TX Healthcare Provider 29,774 Ransomware attack (Interlock) – data theft confirmed
Waveny LifeCare Network, Inc. CT Healthcare Provider 27,113 Network server hacking incident
Elara Caring TX Healthcare Provider 22,172 Hacking incident at third party vendor – data theft confirmed
Minidoka Memorial Hospital ID Healthcare Provider 22,000 Data theft and extortion incident (Blackwater)
Meridian Health Plan of Illinois IL Health Plan 21,027 Employee errors – Impermissible granting certain providers access to its network
City of Middletown OH Healthcare Provider 20,608 Ransomware attack – data theft confirmed
McLeod Physician Associates II SC Healthcare Provider 19,553 Malware identified on network server awaiting decommissioning
Optalis Management Solutions MI Healthcare Provider 13,723 Network server hacking incident
All About Women’s Care CO Healthcare Provider 12,000 Hacking incident via an employee VPN account – data theft confirmed

In June, nine healthcare data breaches were reported to HHS with totals of 500 or 501 affected individuals. These totals are often used as placeholder figures when data reviews are ongoing and the 60-day reporting deadline under the HIPAA Breach Notification Rule is reached. HIPAA requires an estimate to be provided if the total number of affected individuals has yet to be determined. The data breaches in the table below may prove to be far larger than the initial breach report indicates. It may be several weeks or even months before the total number of affected individuals is confirmed.

HIPAA Regulated Entity State Covered Entity Type Individuals Affected Cause of Breach
Gail J May Ltd d/b/a/ Insight Optical IL Healthcare Provider 501 Network server hacking incident at business associate
Community Health Center of Buffalo Inc. NY Healthcare Provider 501 Network server hacking incident
Cherry Street Services, Inc. MI Healthcare Provider 501 Network server hacking incident
Northeast Professional Caregivers OH Healthcare Provider 500 Email compromise
Columbia Orthopaedic Group MO Healthcare Provider 500 Network server hacking incident
Decatur Diagnostic Laboratory Inc. AL Healthcare Provider 500 Network server hacking incident
Ohio Living OH Healthcare Provider 500 Network server hacking incident
Signature Healthcare Corporation MA Healthcare Provider 500 Network server hacking incident
MVP VIP Holdco dba Heart of America Eye Care MO Healthcare Provider 500 Network server hacking incident

Causes of June 2026 Healthcare Data Breaches

Out of the 25 data breaches affecting 10,000 or more individuals, all but one was due to hacking. Across all of June’s reported data breaches, 81.8% of the breaches were hacking/IT incidents, and 1,481,468 individuals were affected by those incidents – 89.7% of all individuals affected by data breaches in June. The average breach size was 81,091 individuals, and the median breach size was 6,504 individuals.
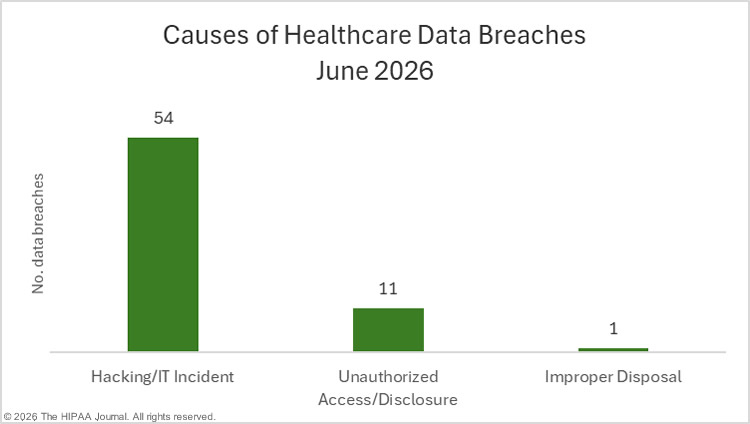
Causes of June 2026 healthcare data breaches

The largest unauthorized access/disclosure incident of the month – Meridian Health Plan of Illinois – affected 21,027 individuals and was due to employees granting healthcare providers access to a portal for managing patient information and processing claims that should not have been given access. There were 11 unauthorized access/disclosure incidents in June, accounting for 16.7% of the month’s data breaches, and 10,914 individuals were affected – 2.7% of the month’s affected individuals. The average breach size was 10,914 individuals, and the median breach size was 6,721 individuals. One improper disposal incident was reported affecting an estimated 1,000 patients. Paper records were disposed of along with regular trash, rather than being sent for shredding. No loss or theft incidents were reported in June.

Location of Breached Protected Health Information

The bar chart below shows the locations of breached protected health information in June 2026 healthcare data breaches. Network servers were the most common location of breached protected health information, followed by email accounts and electronic health records.
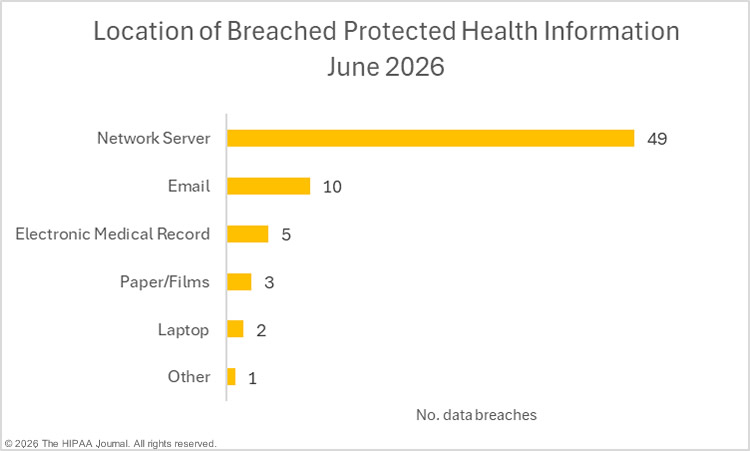
Location of breached protected health information - June 2026

Data Breaches at HIPAA Regulated Entities

When a data breach occurs at a HIPAA-covered entity – healthcare provider, health plan, or healthcare clearinghouse – the HIPAA Breach Notification Rule requires them to report the breach within 60 days of discovery. When a data breach occurs at a business associate of a HIPAA-covered entity, the business associate must notify each affected covered entity within the same time frame.

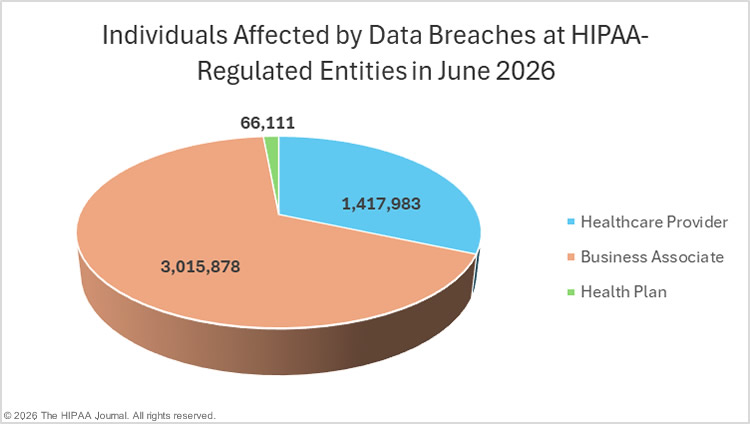
The affected covered entities are ultimately responsible for ensuring that notifications are issued to the HHS, individuals, and in some cases the media, within 60 days of being notified. A HIPAA-covered entity may delegate the notification responsibilities to the business associate. Some choose to issue notifications themselves. The raw breach data on the OCR breach portal shows data breaches based on the reporting entity, not where the data breach occurred. In June, healthcare providers reported 45 breaches, business associates reported 14 breaches, and 7 breaches were reported by health plans. The pie charts below show where the breach actually occurred rather than the reporting entity to better reflect breaches at business associates.
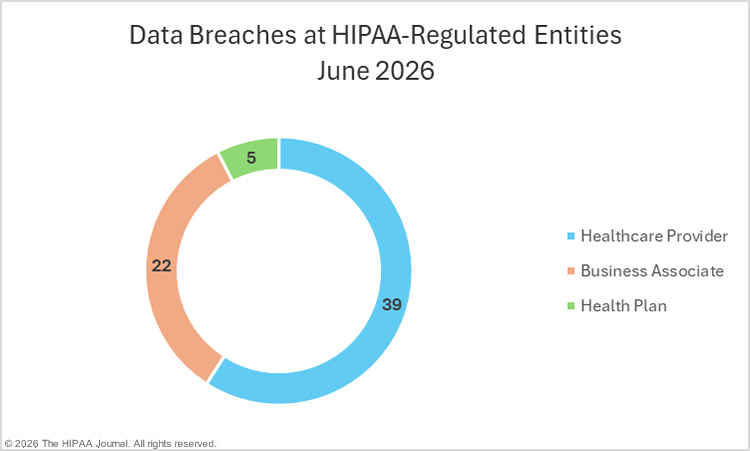
June 2026 data breaches at HIPAA-regulated entities

Individuals affected by June 2026 data breaches at HIPAA-regulated entities

Geographical Distribution of Healthcare Data Breaches

In June, HIPAA-regulated entities based in 24 U.S. states reported large healthcare data breaches. Florida and Texas were the worst affected states with seven reported breaches per state.

State Breaches
Florida & Texas 7
Illinois 5
Colorado, Michigan & New York 4
California, Connecticut, Minnesota, Missouri, Ohio & Tennessee 3
Idaho, Kentucky, Massachusetts, South Carolina & Washington 2
Alabama, Georgia, Indiana, Kansas, New Jersey, Oklahoma & Pennsylvania 1

While Florida and Texas ranked top for breaches, they ranked 4th and 6th in terms of the number of affected individuals. Tennessee, Georgia, and New Jersey topped the list for affected individuals, with each state only registering one large data breach.

State Individuals Affected State Individuals Affected
Tennessee 1,567,038 Michigan 24,396
Georgia 1,261,464 Idaho 22,750
New Jersey 542,377 Ohio 21,608
Florida 233,367 South Carolina 20,690
Minnesota 164,893 Washington 9,825
Texas 124,459 Missouri 3,311
Illinois 120,089 Indiana 3,070
Connecticut 99,071 Pennsylvania 2,720
Colorado 87,814 Oklahoma 1,607
California 80,783 Massachusetts 1,506
New York 74,733 Kansas 534
Kentucky 31,367 Alabama 500

HIPAA Enforcement Activity in June 2026

In June, OCR announced a single enforcement action to resolve potential violations of the HIPAA Rules by the American mall-based retailer, Spencer Gifts. Retailers are not typically HIPAA-covered entities, but Spencer Gifts is a health plan under HIPAA as it sponsors employee benefits and welfare benefit plans. Spencer Gifts was investigated after OCR received a report about a breach of the protected health information of 10,023 members of its flexible benefits and welfare benefit plans. The OCR investigation determined that Spencer Gifts failed to conduct a HIPAA-compliant risk analysis and failed to implement HIPAA Privacy, Security, and Breach Notification Rule policies and procedures. The alleged HIPAA violations were resolved with a settlement that includes a $450,000 financial penalty and a corrective action plan.

In the year to June 30, 2026, OCR resolved seven HIPAA investigations with financial penalties with penalties totaling $1,728,000. All seven of the investigations found risk analysis failures, and two involved breach notification failures. State attorneys general may also investigate data breaches and impose financial penalties for HIPAA violations, although no cases were announced in June 2026.

About this Report

The HIPAA Journal monthly data breach reports are based on data obtained from the HHS Office for Civil Rights and have been combined with breach report data from other sources. The data breaches included in this report were reported in June 2026 but occurred weeks or months previously. The figures in this report may increase or decrease as HIPAA-regulated entities complete their breach investigations, and will be reflected in our healthcare data breach statistics page and our annual HIPAA data breach reports. Further information about HIPAA enforcement actions can be found in our HIPAA violations cases page.

The post June 2026 Healthcare Data Breach Report appeared first on The HIPAA Journal.
Survey Reveals Patients Want to Know When and How AI is Used in Healthcare

A recent survey has revealed that patients are concerned about the use of AI tools by doctors’ offices and other healthcare providers, and the vast majority of patients believe that they should be informed if their healthcare provider is using AI tools in connection with their healthcare. The survey also indicates that more than half of patients are unaware whether AI is currently being used in relation to their healthcare.

The survey was conducted on almost 5,000 U.S. adults in late June 2026 by the Pew Research Center. The survey revealed that 72% of patients believe it is extremely important or very important for their healthcare providers to disclose whether they are using AI tools in connection with healthcare, with 16% of respondents believing that it is somewhat important. Only 7% of respondents said they are not too bothered or not at all bothered about being informed about the use of AI.

Concern varied across different uses of AI, with the greatest concern expressed about AI being used to make diagnostic decisions (81%), analyze medical scans (81%), explain medical test results (80%), and take notes during a medical appointment (72%).  More than half of patients believe that they should be informed about behind-the-scenes administrative services such as getting prescription refills (64%) and scheduling medical appointments (56%), although the latter had the largest percentage of patients who do not feel that disclosure is needed (33%). Across all areas of questioning, 9% or 10% of patients were not sure if they should be informed, potentially indicating they are unaware of any risks involved.

While most patients believe that they should be informed about the use of AI in healthcare, almost half of all surveyed patients (46%) said they were unaware whether their doctor’s office and other healthcare providers were using AI solutions, with only 16% of patients saying a doctor has actually told them that AI was used in their care. Adoption of AI in healthcare has grown considerably, with ONC’s figures showing that 71% of hospitals were using AI tools in 2024, up from 66% in 2023. Despite the high level of AI adoption, 33% of respondents believe their healthcare providers are not using AI tools, which suggests a lack of transparency.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

While patients want to be informed and have a say in how AI is used in healthcare, many Americans do not believe they have control over how AI is used. The survey revealed that more than half of respondents (53%) believe they either have no say or not much say in the use of AI in healthcare, with 16% believing they have some say. 63% of respondents to the survey would like more say in how AI is used, and only 21% of respondents said they are comfortable with how much say they currently have.

As AI adoption grows, it is important for healthcare providers to explain to patients how the tools are used and to obtain patient consent in order to maintain trust. It is also important for the tools, including transcription tools and chatbots, to be continuously evaluated to ensure they are fit for purpose and are generating accurate results.

The post Survey Reveals Patients Want to Know When and How AI is Used in Healthcare appeared first on The HIPAA Journal.

SonicWall Warns of Actively Exploited Vulnerabilities in SMA1000 Appliances

Two remotely exploitable zero-day vulnerabilities in SonicWall SMA1000 appliances are being chained together to achieve remote code execution, according to a recent SonicWall security alert. SMA1000 appliances are used for secure remote access and VPN connections and, as such, are commonly exposed to the Internet.

One of the vulnerabilities, tracked as CVE-2026-83548, is a critical pre-authentication server-side request forgery issue in the Appliance Work Place interface that allows command injection. The vulnerability has been assigned a maximum CVSS v 3.1 severity score of 10. Successful exploitation allows a remote attacker to access sensitive functions and perform unauthorized actions.

The vulnerability is being chained with an exploit for a high-severity (CVSS v3.1: 7.8) OS command injection vulnerability – CVE-2026-83549 – in the Appliance Management Console. Attackers with admin privileges can exploit the vulnerability and execute OS commands. The vulnerability is due to improper neutralization of special elements used in an OS command.

The SonicWall PSIRT has investigated a case where the threat actor chained the two vulnerabilities in an attack on a customer. The Cybersecurity and Infrastructure Security Agency (CISA) has added both vulnerabilities to its Known Exploited Vulnerability (KEV) Catalog, and federal civilian Executive Branch agencies have been given until Saturday to upgrade to the latest hotfix.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The vulnerabilities affect SMA1000 6210, 7210, and 8200v models, but not SSL-VPN running on SonicWall firewalls or SMA 100 Series products. The affected software versions are 12.4.3-03453 (platform-hotfix) and older versions, and 12.5.0-02835 (platform-hotfix) and older versions.

The extent to which the vulnerabilities are being exploited is unclear. The latest attack(s) come just two months after a different pair of vulnerabilities in SMA1000 appliances were exploited to install malware, enabling ransomware attacks. Since threat actors actively target vulnerabilities in remote access and VPN appliances, users of vulnerable devices are strongly advised to upgrade to the latest hotfix as soon as possible. Currently, there are approximately 400 SMA1000 devices worldwide that are exposed online, the majority of which are in the United States.

The post SonicWall Warns of Actively Exploited Vulnerabilities in SMA1000 Appliances appeared first on The HIPAA Journal.