Healthcare Cybersecurity

Lack of Security Awareness Training Leaves Healthcare Organizations Exposed to Cyberattacks

A recent study conducted by the Ponemon Institute on behalf of Merlin International has revealed healthcare organizations are failing to provide sufficient security awareness training to their employees, which is hampering efforts to improve security posture.

Phishing is a major security threat and the healthcare industry is being heavily targeted. Phishing offers threat actors an easy way to bypass healthcare organizations’ security defenses. Threat actors are now using sophisticated tactics to evade detection by security solutions and get their emails delivered. Social engineering techniques are used to fool employees into responding to phishing emails and disclose their login credentials or install malware.

Phishing is used in a high percentage of cyberattacks on healthcare organizations. Research conducted by Cofense (formerly PhishMe) suggests as many as 91% of cyberattacks start with a phishing email. While security solutions can be implemented to block the majority of phishing emails from being delivered to end users’ inboxes, it is not possible to block 100% of malicious emails. Security awareness training is therefore essential.

Healthcare employees should be trained how to recognize phishing emails and how to respond when potentially malicious messages are received. Training should be provided to help eliminate risky behaviors and teach cybersecurity best practices. The failure to provide sufficient training leaves healthcare organizations at risk of attack.

The Ponemon/Merlin International study on 627 healthcare executives in the United States suggests healthcare organizations are not doing enough to improve security awareness and develop a security culture.  More than half of respondents (52%) said the lack of security awareness was affecting their organization’s security posture.

The Merlin International report, 2018 Impact of Cyber Insecurity on Healthcare Organizations, revealed 62% of respondents have experienced a cyberattack in the past 12 months, with half of those incidents resulting in the loss of healthcare data. Poor security awareness is contributing to a high percentage of those breaches.

When asked about the biggest concerns, there was an equal split between external attacks by hackers and internal breaches due to errors and employee negligence – 63% and 64% respectively.

The main threats to the confidentiality, integrity, and availability of healthcare data were perceived to be unsecured medical devices (78%), BYOD (76%) and insecure mobile devices (72%).

57% of respondents felt use of the cloud, mobile, and IoT technologies has increased the number of vulnerabilities that could be exploited to gain access to healthcare data. 55% of respondents said medical devices were not included in their cybersecurity strategy and the continued use of legacy systems was seen to be a security issue by 58% of respondents.

Even though 62% of organizations have experienced a data breach in the last year and it is a requirement for HIPAA compliance, 51% of organizations have not developed an incident response program that allows them to rapidly respond and remediate breaches.

Staffing was seen to be the biggest roadblock preventing organizations from improving their security posture. 74% believed a lack of suitable staff was a major issue hampering efforts to improve cybersecurity. 60% of respondents do not believe they have the right cybersecurity qualifications in house and only 51% of surveyed organizations have appointed a CISO.

“Healthcare organizations must get even more serious about cybersecurity to protect themselves and their patients from losing access to or control of the proprietary and personal information and systems the industry depends on to provide essential care,” said Brian Wells, Director of Healthcare Strategy at Merlin International.

The post Lack of Security Awareness Training Leaves Healthcare Organizations Exposed to Cyberattacks appeared first on HIPAA Journal.
Study Reveals Poor Patching Practices in Healthcare

A recent survey conducted by the Ponemon Institute on behalf of ServiceNow has revealed the healthcare and pharmaceutical industries are struggling to keep on top of patching. Vulnerabilities are not being patched promptly leaving organizations open to attack.

The survey was conducted on 3,000 security professionals from organizations with more than 1,000 employees across a broad range of industry sectors and countries. The results of the survey were published in the report: Today’s State of Vulnerability Response: Patch Work Demands Attention.

The report revealed 57% of respondents had experienced at least one data breach where access to the network was gained by exploiting a vulnerability for which a patch had previously been released. A third of respondents said that they were aware that the vulnerability existed and a patch was available prior to the breach. More alarming was two third of organizations did not know they were vulnerable to attack.

Even though there is a considerable risk of vulnerabilities being exploited, 37% of respondents said they do not scan for vulnerabilities and therefore cannot be sure all vulnerabilities are identified and addressed. The healthcare and pharmaceutical industries were slightly better than average, although 28% of IT security professionals from those industries said vulnerability scanning was not performed.

65% of cybersecurity professionals said they find it difficult to prioritize patching and determine what software should be patched first. 61% said manual processes were putting them at a disadvantage when patching vulnerabilities, and an average of 12 days were being lost coordinating patching activities across teams.

More than three quarters of IT security professionals felt the delay in patching vulnerabilities was due to a shortage of staff. They simply did not have enough employees to keep on top of patching. On average, 321 hours a week are being spent on vulnerability management, but even so, medium to low priority patches are still taking eight weeks or longer to be applied.

60% of respondents saying they were recruiting more staff in the next 12 months to help speed up the patching of vulnerabilities. On average, organizations are looking to hire four new employees solely for vulnerability response.

Deciding to hire more staff is one thing. Recruiting staff is another. There is a shortage of skilled IT staff and the problem is getting worse. According to a recent survey conducted by the advocacy group ISACA, by 2019 there will be 2 million unfilled cybersecurity positions.

Even if staff can be recruited, there is no guarantee that security posture can be significantly improved. While additional staff could certainly help some companies, the report suggests there is a patching paradox – hiring more staff does not mean better security.

“Adding more talent alone won’t address the core issue plaguing today’s security teams,” said ServiceNow Security and Risk Vice President and General Manager Sean Convery. “Automating routine processes and prioritizing vulnerabilities helps organizations avoid the ‘patching paradox,’ instead focusing their people on critical work to dramatically reduce the likelihood of a breach.”

The Ponemon Institute/ServiceNow report offers five recommendations that can help organizations develop a roadmap to a better security posture.

  • Take an unbiased inventory of vulnerability response capabilities.
  • Accelerate time-to-benefit by tackling low-hanging fruit first.
  • Break down data barriers between security and IT to regain lost time spend coordinating between the two
  • Define and optimize end-to-end vulnerability response processes and then automate as much as you can.
  • Retain talent by focusing on culture and environment.

The post Study Reveals Poor Patching Practices in Healthcare appeared first on HIPAA Journal.

Verizon PHI Breach Report Confirms Healthcare Has Major Problem with Insider Breaches

Verizon has released its annual Protected Health Information Breach Report which delves deep into the main causes of breaches, why they occur, the motivations of internal and external threat actors, and the main threats to the confidentiality, integrity, and availability of PHI.

For the report, Verizon analyzed 1,368 healthcare data breaches and incidents where protected health information (PHI) was exposed but not necessarily compromised. The data came from 27 countries, although three quarters of the breached entities were based in the United States where there are stricter requirements for reporting PHI incidents.

In contrast to all other industry sectors, the healthcare industry is unique as the biggest security threat comes from within. Insiders were responsible for almost 58% of all breaches with external actors confirmed as responsible for just 42% of incidents.

The main reason for insider breaches is financial gain. PHI is stolen to commit identity theft, credit card fraud, insurance fraud, and tax fraud. Verizon determined that 48% of all internal incidents were conducted for financial gain. 31% involved accessing medical data out of curiosity or for fun, 10% of incidents were attributed to easy access to data, with 3% of incidents occurring due to a grudge and a further 3% for espionage. External attacks are primarily conducted for financial gain – extortion and the theft and sale of data.

Verizon also looked at the actions that lead to PHI incidents and data branches, with the most common problem being errors. Errors were behind 33.5% of incidents within this category, which included the misdelivery of emails and mailings, errors made disposing of PHI, publishing errors, loss of PHI, misconfigurations, programming mistakes and data entry errors. The main incident cause was misdelivery of documents, which accounted for 20% of all incidents in the error category.

The second biggest breach category is misuse, accounting for 29.5% of all incidents. 66% of incidents in this category were attributed to privilege abuse – accessing records without authorization. Data mishandling was behind 21.6% of incidents and possession abuse – the misuse of access to physical records – was behind 16.9% of incidents in the misuse category.

The physical category includes theft of records and devices, snooping, tampering, disabled controls, and surveillance. 16.3% of all healthcare PHI incidents were placed in this category, with theft accounting for 95.2% of all incidents. The theft of laptops was the main incident type. Almost half (47%) of laptop theft incidents involved the devices being taken from employees’ vehicles. The use of encryption would prevent the majority of these incidents from exposing PHI.

Hacking may make the headlines, but it accounted for relatively few breaches – just 14.8% of all healthcare PHI incidents were placed in this category. The main cause of breaches in the hacking category was the use of stolen credentials (49.3% of incidents), with credentials often stolen via phishing attacks. Brute force attacks taking advantage of weak passwords were behind 20.9% of incidents. 17.9% of hacking breaches involved the use of backdoors.

Malware was involved in 10.8% of all PHI incidents. While there were a wide range of malware types and variants used in attacks, by far the biggest category was ransomware, which accounted for 70.5% of attacks.

Social attacks accounted for 8% of all incidents. This category involves attacks on employees. Phishing was involved in 69.9% of incidents in this category, followed by pretexting (11.7%), and bribery (7.8%). Pretexting is the next stage on from phishing, when access to email accounts is used to send further emails – BEC attacks for example.

Verizon offers three suggestions which in the short term will help to reduce the number of PHI related incidents and data breaches.

Full disk encryption should be deployed on all portable electronic devices used to store PHI. This simple measure would prevent PHI from being accessed in the event of loss or theft of an electronic device.

The routine monitoring of medical record access – a requirement of HIPAA – will not prevent breaches, but it will reduce the severity of insider incidents and allow healthcare organizations to take corrective action quickly. When employees are aware that records are routinely monitored it can also act as a deterrent and reduce theft and unauthorized access incidents.

The final course of action is to implement solutions to combat ransomware and malware. While defenses can and should involve the use of spam filters and web filters, simple measures can also be taken such as not allowing laptops to access the Internet if they are used to store large quantities of PHI.

The post Verizon PHI Breach Report Confirms Healthcare Has Major Problem with Insider Breaches appeared first on HIPAA Journal.
Security Breaches in Healthcare in the Last Three Years

There have been 955 major security breaches in healthcare in the last three years that have resulted in the exposure/theft of 135,060,443 healthcare records. More than 41% of the population of the United States have had some of their protected health information exposed as a result of those breaches, which have been occurring at a rate of almost one a day over the past three years.

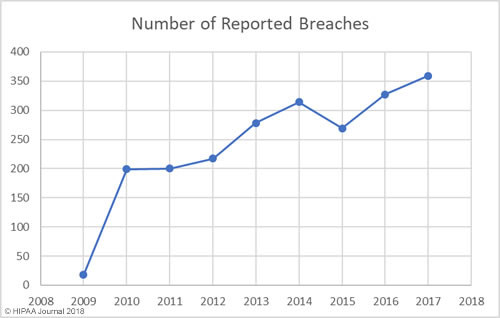
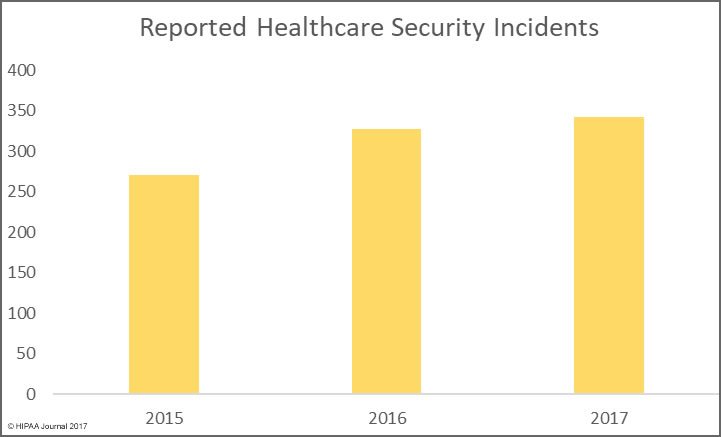
There has been a steady rise in reported security beaches in healthcare in the last three years. In 2015 there were 270 data breaches involving more than 500 records reported to the Department of Health and Human Services’ Office for Civil Rights. The figure rose to 327 security breaches in 2016, and 342 security breaches in 2017.

reported healthcare data breaches in 2017

More healthcare security breaches are being reported than at any other time since HIPAA required covered entities to disclose data breaches, although the number of individuals affected by healthcare data breaches has been declining year-over year for the past three years.

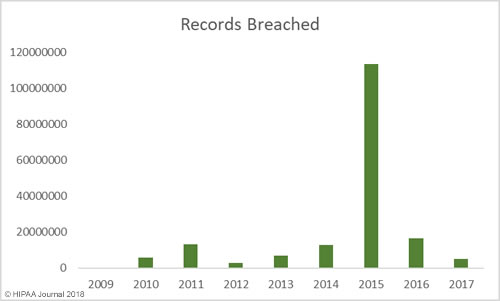
In 2015, a particularly bad year for healthcare industry data breaches, 112,107,579 healthcare records were exposed or stolen. The majority of those records were exposed in three data breaches. The 78.8 million-record data breach at Anthem Inc., the 11 million-record breach at Premera Blue Cross, and the 10 million-record breach at Excellus Health Plan.

Other major security breaches in 2015 include the University of California Los Angeles Health breach of 4.5 million records and Medical Informatics Engineering breach of 3.9 million records.

In 2016, 14,679,461 healthcare records were exposed or stolen, with three incidents involving more than 1 million records: The 3.62 million-record breach at Banner Health, the 3.46 million-record breach at Newkirk Products, Inc., and the 2.21 million-record breach at 21st Century Oncology.

In 2017, the worst year for healthcare security incidents in terms of the number of breaches reported, there were 3,286,498 healthcare records exposed or stolen. There were two breaches involving more than half a million records. The 500,000-record breach at Airway Oxygen, Inc., and the 697800-record breach at Commonwealth Health Corporation

15 Largest Security Breaches in Healthcare in the Last Three Years


Rank Year Covered Entity Entity Type Records Exposed/Stolen Breach Cause
1 2015 Anthem, Inc. Affiliated Covered Entity Health Plan 78800000 Hacking/IT Incident
2 2015 Premera Blue Cross Health Plan 11000000 Hacking/IT Incident
3 2015 Excellus Health Plan, Inc. Health Plan 10000000 Hacking/IT Incident
4 2015 University of California, Los Angeles Health Healthcare Provider 4500000 Hacking/IT Incident
5 2015 Medical Informatics Engineering Business Associate 3900000 Hacking/IT Incident
6 2016 Banner Health Healthcare Provider 3620000 Hacking/IT Incident
7 2016 Newkirk Products, Inc. Business Associate 3466120 Hacking/IT Incident
8 2016 21st Century Oncology Healthcare Provider 2213597 Hacking/IT Incident
9 2015 CareFirst BlueCross BlueShield Health Plan 1100000 Hacking/IT Incident
10 2016 Valley Anesthesiology Consultants, Inc. d/b/a Valley Anesthesiology and Pain Consultants Healthcare Provider 882590 Hacking/IT Incident
11 2016 County of Los Angeles Departments of Health and Mental Health Healthcare Provider 749017 Hacking/IT Incident
12 2017 Commonwealth Health Corporation Healthcare Provider 697800 Theft
13 2015 Virginia Department of Medical Assistance Services (VA-DMAS) Health Plan 697586 Hacking/IT Incident
14 2016 Bon Secours Health System Incorporated Healthcare Provider 651971 Unauthorized Access/Disclosure
15 2015 Georgia Department of Community Health Health Plan 557779 Hacking/IT Incident


Main Causes of Security Breaches in Healthcare in the Last Three Years

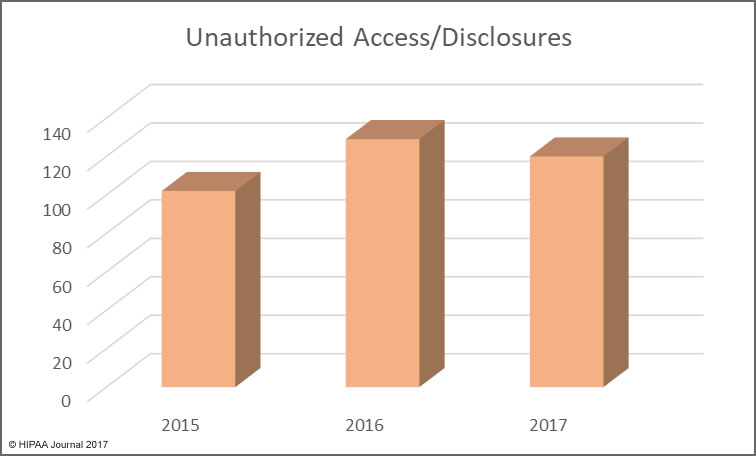
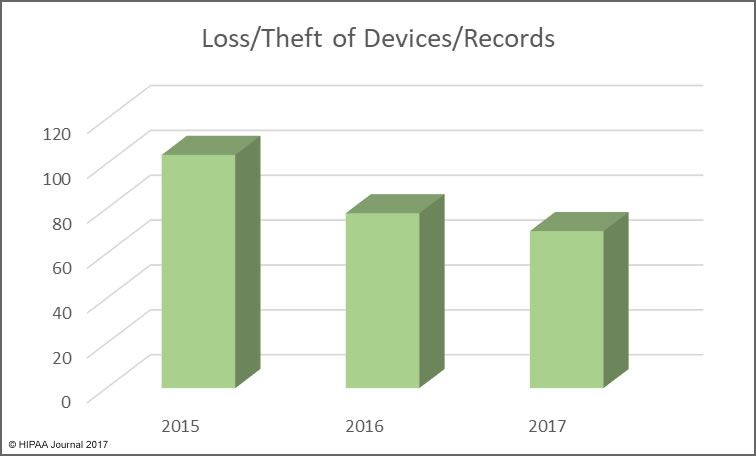
The three main causes of security breaches in healthcare in the last three years were hacking/IT incidents, unauthorized access and disclosure incidents, and the loss/theft of physical records and unencrypted electronic devices containing ePHI.

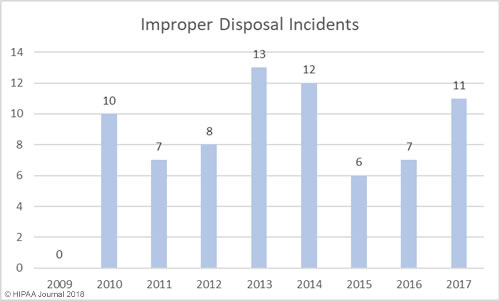
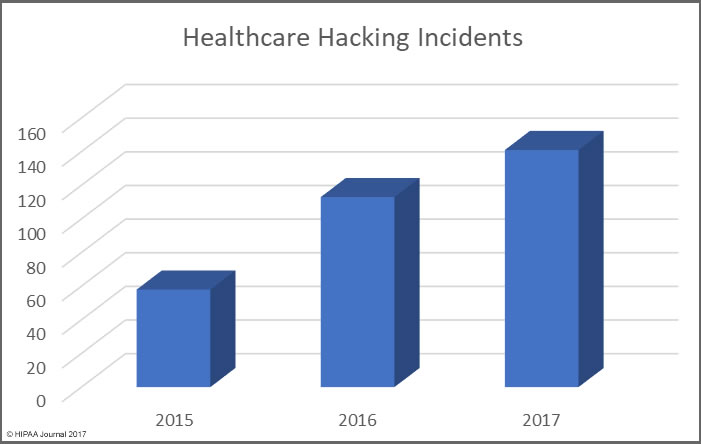
There has been a downward trend in the number of theft/loss incidents over the past three years as healthcare organizations have started encrypting records on portable electronic devices. However, improper disposal incidents have risen year over year as have hacking incidents. In 2017, hacking/IT incidents were the main cause of healthcare data breaches.

healthcare data breaches in 2017 (hacking)

healthcare data breaches in 2017 (Unauthorized access/disclosures)

Healthcare Data Breaches in 2017 (loss/theft)

Financial Penalties for Security Breaches in Healthcare in the Last Three Years

In addition to annual increases in data breaches, financial penalties for HIPAA violations have also been increasing, both in terms of number of settlements and civil monetary penalties issued and the penalty amounts.

The HHS’ Office for Civil Rights is now enforcing HIPAA Rules far more aggressively and multi-million-dollar fines are regularly issued. The last three years have seen 29 HIPAA covered entities and business associates financially penalized for data breaches that have occurred as a result of noncompliance with HIPAA Rules.

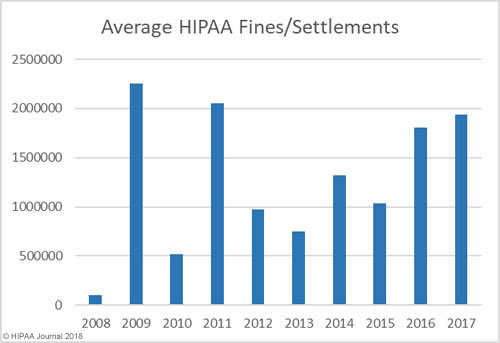
In the last three years, the HHS’ Office for Civil Rights has collected $49,091,700 in financial penalties from its enforcement actions. The average settlement amount in 2017 was $1.94 million.

The post Security Breaches in Healthcare in the Last Three Years appeared first on HIPAA Journal.
Research Suggests Healthcare Data Breaches Cause 2,100 Deaths a Year

A researcher at Vanderbilt University has conducted a study that suggests mortality rates at hospitals increase following a data breach as a result of a drop in the standard of care. The researcher estimates healthcare data breaches may cause as many as 2,100 deaths a year in the United States.

The study was conducted by Owen Graduate School of Management researcher, Dr. Sung Choi. The findings of the study were presented at a recent cyberrisk quantification conference at Philadelphia’s Drexel University LeBow College of Business.

Cyberattacks can have a direct impact on patient care, which has been clearly highlighted on numerous occasions over the past 12 months. Ransomware and wiper malware attacks have crippled information systems and have forced healthcare providers to cancel appointments, while the lack of access to patient health records can cause treatment delays. Notable attacks that caused major disruption were the NotPetya wiper and WannaCry ransomware attacks last year, with the latter causing major problems for the National Health Service in the UK.

Choi explained that data breaches can be a distraction for physicians and the after affects of breaches can last for years. HIPAA covered entities face investigations and litigation which Choi suggests could result in disruption to medical services and delays in providing treatment. The cost of mitigating attacks, including purchasing additional security solutions and dealing with the fallout from data breaches can see resources diverted away from patient care.

For the study, Choi compared mortality rates at hospitals before and immediately after a data breach had occurred. One of the metrics used to assess a potential fall in the quality of care was the percentage of heart attack patients who died within 30 days of admission to hospital.

Choi notes that the control group and breached hospitals had similar mortality rates, although after a data breach, the mortality rate for the control group remained the same but increased at hospitals that had experienced a breach. Choi’s analysis showed there was a 0.23% increase in the mortality rate one year following a data breach and an increase of 0.36% two years after a breach. That equates to 2,160 deaths a year.

Choi also noted that the time taken to administer electrocardiographs was longer for newly admitted patients after a hospital had experienced a data breach.

The study was presented just a few days before the Department of Health and Human Services’ Office for Civil Rights issued a reminder to HIPAA covered entities about the need to develop contingency plans for emergencies such as cyberattacks and ransomware incidents. OCR explained that HIPAA Rules on contingency planning help to ensure a fast recovery from a natural disaster, cyberattack, or other emergency situation.

This research suggests that the development of an effective contingency plan and a rapid response to data breaches can save lives.

The post Research Suggests Healthcare Data Breaches Cause 2,100 Deaths a Year appeared first on HIPAA Journal.
HIPAA Rules on Contingency Planning

In its March 2018 cybersecurity newsletter, OCR explained HIPAA Rules on contingency planning and urged healthcare organizations to plan for emergencies to ensure a return to normal operations can be achieved in the shortest possible time frame.

A contingency plan is required to ensure that when disaster strikes, organizations know exactly what steps must be taken and in what order.

Contingency plans should cover all types of emergencies, such as natural disasters, fires, vandalism, system failures, cyberattacks, and ransomware incidents. The steps that must be taken for each scenario could well be different, especially in the case of cyberattacks vs. natural disasters. The plan should incorporate procedures to follow for specific types of disasters.

Contingency planning is not simply a best practice. It is a requirement of the HIPAA Security Rule. Contingency planning should not be considered a onetime checkbox item necessary for HIPAA compliance. It should be an ongoing process with plans regularly checked, updated, and tested to ensure any deficiencies are identified and addressed.

What are the HIPAA Rules on Contingency Planning?

HIPAA Rules on contingency planning are concerned with ensuring healthcare organizations return to normal operations as quickly as possible and the confidentiality, integrity, and availability of PHI is safeguarded.

HIPAA Rules on contingency planning can be found in the Security Rule administrative safeguards -45 CFR § 164.308(a)(7)(ii)(A-E).

  • Develop and Implement a Data Backup Plan – 308(a)(7)(ii)(A)
  • Develop a Disaster Recovery Plan – 308(a)(7)(ii)(B)
  • Develop and Emergency Mode Operation Plan – 308(a)(7)(ii)(C)
  • Develop and Implement Procedures for Testing and Revision of Contingency Plans – 308(a)(7)(ii)(D)
  • Perform an Application and Data Criticality Analysis – 308(a)(7)(ii)(E)

A data backup plan ensures that when disaster strikes, PHI is not lost or destroyed. A viable copy of all ePHI must be created that allows exact copies of ePHI to be restored, which includes all forms of ePHI such as medical records, diagnostic images, test results, case management information, and accounting systems.  It is a good best practice to adopt a 3-2-1 approach for backups: Create three copies of data, store them on at least two different media, and have one copy stored securely offsite. Backups must also be tested to ensure the recovery of data is possible.

A disaster recovery plan should establish the procedures that must be followed to restore access to data, including how files should be restored from backups. A copy of the plan should be readily available and stored in more than one location.

The emergency mode operation plan must ensure critical business processes continue to maintain the security of ePHI when operating in emergency mode, for example when there is a technical failure or power outage.

All elements of the contingency plan must be regularly tested and revised as necessary. OCR recommends conducting scenario-based walkthroughs and live tests of the complete plan.

Covered entities should “assess the relative criticality of specific applications and data in support of other contingency plan components.” All software applications that are used to store, maintain, or transmit ePHI must be assessed to determine the level of criticality to business functions as it will be necessary to prioritize each when data is restored.

Summary of Key Elements of Contingency Planning

OCR has provided a summary of the key elements of contingency planning:

  • The primary goal is to maintain critical operations and minimize loss.
  • Define time periods – What must be done during the first hour, day, or week?
  • Establish Plan Activation – What event(s) will cause the activation of the contingency plan?  Who has the authority to activate the contingency plan?
  • Ensure the contingency plan can be understood by all types of employees.
  • Communicate and share the plan and roles and responsibilities with the organization.
  • Establish a testing schedule for the plan to identify gaps.
  • Ensure updates for plan effectiveness and increase organizational awareness.
  • Review the plan on a regular basis and situationally when there are technical, operational, environmental, or personnel changes in the organization.

The post HIPAA Rules on Contingency Planning appeared first on HIPAA Journal.
Healthcare Data Breach Statistics

We have compiled healthcare data breach statistics from October 2009 when the Department of Health and Human Services’ Office for Civil Rights first started publishing summaries of healthcare data breaches on its website.

The healthcare data breach statistics below only include data breaches of 500 or more records as smaller breaches are not published by OCR. The breaches include closed cases and breaches still being investigated by OCR.

Our healthcare data breach statistics clearly show there has been an upward trend in data breaches over the past 9 years, with 2017 seeing more data breaches reported than any other year since records first started being published.

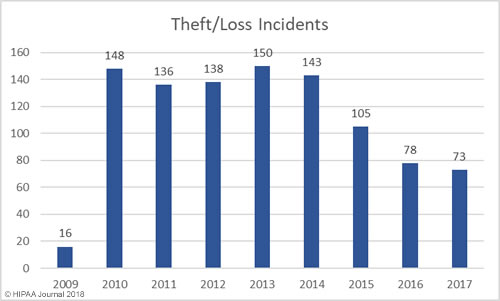
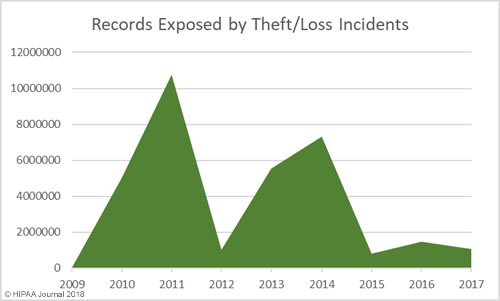
There have also been notable changes over the years in the main causes of breaches. The loss/theft of healthcare records and electronic protected health information dominated the breach reports between 2009 and 2015, although better policies and procedures and the use of encryption has helped reduce these easily preventable breaches. Our healthcare data breach statistics show the main causes of healthcare data breaches is now hacking/IT incidents, with unauthorized access/disclosures also commonplace.

Healthcare Data Breaches by Year

Between 2009 and 2017 there have been 2,181 healthcare data breaches involving more than 500 records. Those breaches have resulted in the theft/exposure of 176,709,305 healthcare records.  That equates to more than 50% of the population of the United States (54.25%). Healthcare data breaches are now being reported at a rate of more than one per day.

Healthcare data breaches 2019-2017

Healthcare Records Exposed by Year

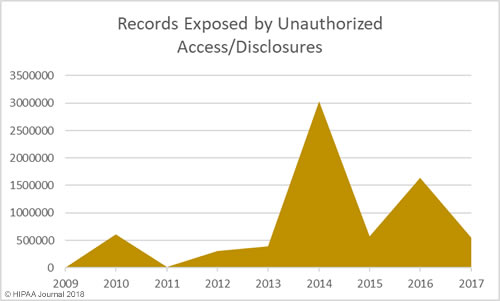
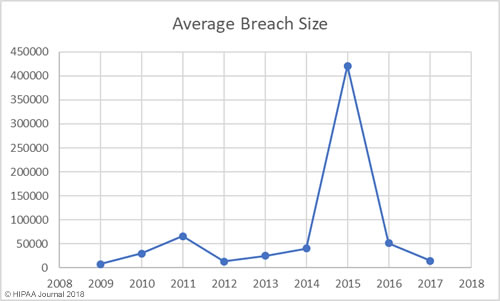
While there has been a general upward trend in the number of records exposed each year, there was a massive improvement in 2017 – the best year since 2012 in terms of the number of records exposed. However, while breaches were smaller in 2017, it was a record breaking year in terms of the number of healthcare data breaches reported – 359 incidents.

Records Exposed in Healthcare data breaches

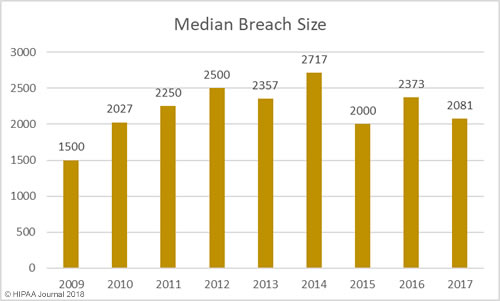
Average/Median Healthcare Data Breach Size by Year

Average Size of Healthcare Data Breaches


Median Size of Healthcare Data Breaches


Largest Healthcare Data Breaches (2009-2017)

Rank Year Entity Entity Type Records Exposed/Stolen Cause of Breach
1 2015 Anthem, Inc. Affiliated Covered Entity Health Plan 78800000 Hacking/IT Incident
2 2015 Premera Blue Cross Health Plan 11000000 Hacking/IT Incident
3 2015 Excellus Health Plan, Inc. Health Plan 10000000 Hacking/IT Incident
4 2011 Science Applications International Corporation Business Associate 4900000 Loss
5 2014 Community Health Systems Professional Services Corporation Business Associate 4500000 Theft
6 2015 University of California, Los Angeles Health Healthcare Provider 4500000 Hacking/IT Incident
7 2013 Advocate Medical Group Healthcare Provider 4029530 Theft
8 2015 Medical Informatics Engineering Business Associate 3900000 Hacking/IT Incident
9 2016 Banner Health Healthcare Provider 3620000 Hacking/IT Incident
10 2016 Newkirk Products, Inc. Business Associate 3466120 Hacking/IT Incident
11 2016 21st Century Oncology Healthcare Provider 2213597 Hacking/IT Incident
12 2014 Xerox State Healthcare, LLC Business Associate 2000000 Unauthorized Access/Disclosure
13 2011 IBM Business Associate 1900000 Unknown
14 2011 GRM Information Management Services Business Associate 1700000 Theft
15 2010 AvMed, Inc. Health Plan 1220000 Theft
16 2015 CareFirst BlueCross BlueShield Health Plan 1100000 Hacking/IT Incident
17 2014 Montana Department of Public Health & Human Services Health Plan 1062509 Hacking/IT Incident
18 2011 The Nemours Foundation Healthcare Provider 1055489 Loss
19 2010 BlueCross BlueShield of Tennessee, Inc. Health Plan 1023209 Theft
20 2011 Sutter Medical Foundation Healthcare Provider 943434 Theft

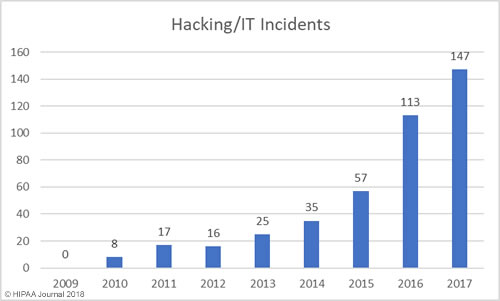
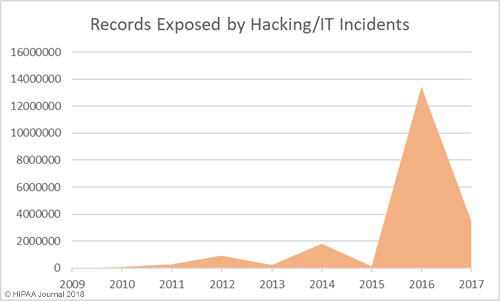
Healthcare Hacking Incidents by Year

Our healthcare data breach statistics show hacking is now the leading cause of healthcare data breaches, although healthcare organizations are now much better at detecting breaches when they do occur. The low hacking/IT incidents in the earlier years is likely to be due, in part, to the failure to detected hacking incidents and malware infections quickly. Many of the hacking incidents in 2014-2017 occurred many months, and in come cases years, before they were detected.

Healthcare Data Breaches - Hacking


Records Exposed in Healthcare Data Breaches - Hacking

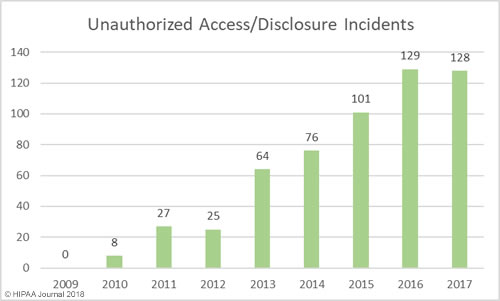
Unauthorized Access/Disclosures by Year

As with hacking, healthcare organizations are getting better at detecting internal breaches and also reporting those breaches to the Office for Civil Rights. While hacking is the main cause of breaches, unauthorized access/disclosure incidents are in close second.

Healthcare Data Breaches - unauthorized access/disclosures


records exposed in authorized access/disclosures

Loss/Theft of PHI and Unencrypted ePHI by Year

Our healthcare data breach statistics show HIPAA covered entities and business associates have got significantly better at protecting healthcare records with administrative, physical, and technical controls such as encryption, although unencrypted laptops and other electronic devices are still being left unsecured in vehicles and locations accessible by the public.

healthcare theft/loss data breaches


records exposed by healthcare theft/loss data breaches

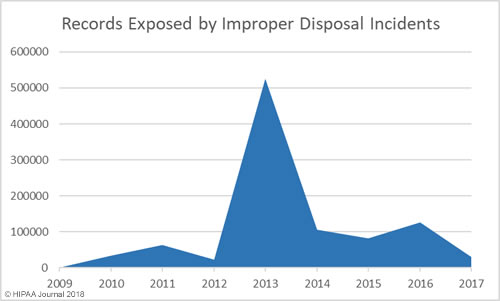
Improper Disposal of PHI/ePHI by Year

healthcare data breaches - improper disposal incidents


records exposed in healthcare improper disposal incidents


Breaches by Entity Type

Year Provider Health Plan Business Associate Other Total
2009 14 1 3 0 18
2010 134 21 44 0 199
2011 137 20 42 1 200
2012 155 22 36 4 217
2013 199 18 56 5 278
2014 202 71 41 0 314
2015 196 62 11 0 269
2016 257 51 19 0 327
2017 288 52 19 0 359
Total 1582 318 271 10 2181

OCR Settlements and Fines for HIPAA Violations

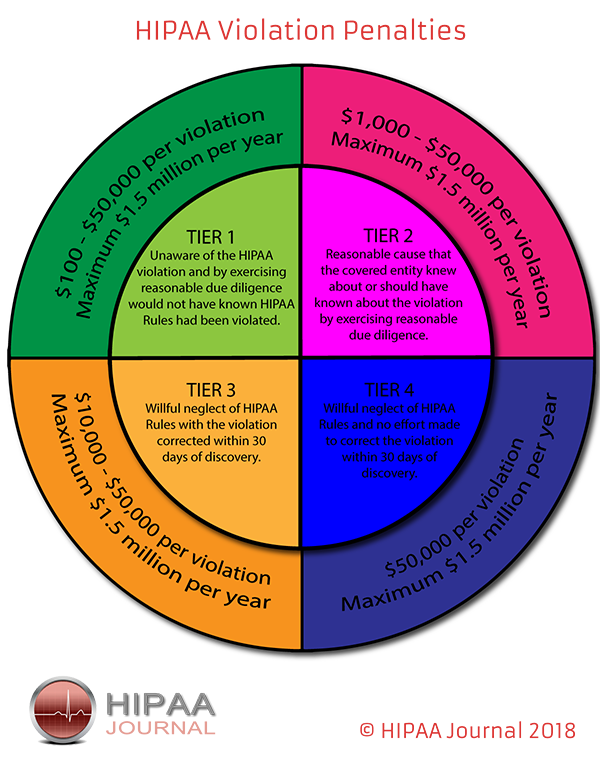
The penalties for HIPAA violations can be severe with multi-million-dollar fines possible when violations have been allowed to persist for several years or when multiple violations of HIPAA Rules have been allowed to occur.

The penalty structure for HIPAA violations is detailed in the infographic below:

Penalty Structure for HIPAA Violations

OCR Settlements and Fines Over the Years

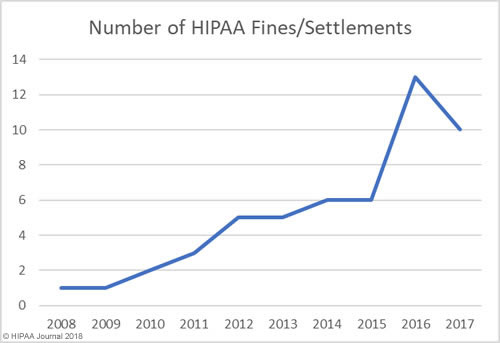
The data for the healthcare data breach statistics on fines and settlements can be viewed on our HIPAA violation fines page, which details all HIPAA violation fines issued by OCR between 2008 and 2018. As the graph below shows, there has been a steady increase in HIPAA enforcement over the past 9 years.

HIPAA Fines and Settlements 2008-2017


How Much Has OCR Fined HIPAA Covered Entities and Business Associates?

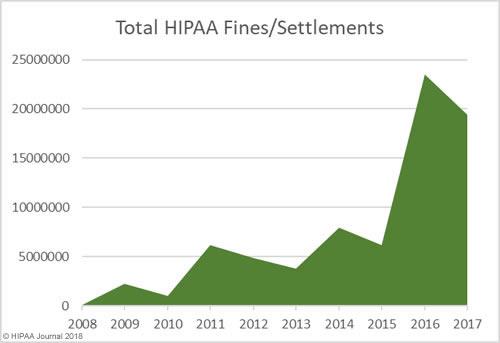
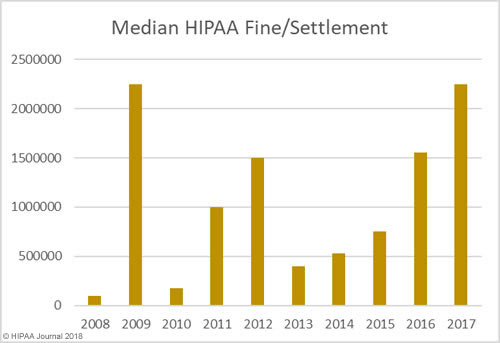
In addition to an increase in fines and settlements, the level of fines has increased substantially. Multi-million-dollar fines for HIPAA violations are now the norm.

HIPAA Fine and Settlement Amounts 2008-2017


average HIPAA Fines and Settlements 2008-2017


Median HIPAA Fines and Settlements 2008-2017

As the graphs above show, there has been a sizable increase in both the number of settlements and civil monetary penalties and the fine amounts in recent years. OCR’s budget has been cut so there are fewer resources to put into pursuing financial penalties in HIPAA violation cases. 2018 is likely to see fewer fines for HIPAA covered entities than the past two years, although settlement amounts are likely to remain high and even increase in 2018.OCR Director Roger Severino has indicated financial penalties are most likely to be pursued for particularly egregious HIPAA violations.

State Attorneys General HIPAA Fines and Other Financial Penalties for Healthcare Organizations

State attorneys general can issue fines ranging from $100 per HIPAA violation up to a maximum of $25,000 per violation category, per year.

Even when action is taken by state attorneys general over potential HIPAA violations, healthcare organizations are typically fined for violations of state laws. Only a handful of U.S. states have issued fines solely for HIPAA violations

Some of the major fines issued by state attorneys general for HIPAA violations and violations of state laws are listed below.


Year State Covered Entity Amount Individuals affected Settlement/CMP Reason
2018 NY EmblemHealth $575,000 81,122 Settlement Mailing error
2018 NY Aetna $1,150,000 12,000 Settlement Mailing error
2017 CA Cottage Health System $2,000,000 More than 54,000 Settlement Failure to adequately protect medical records
2017 MA Multi-State Billing Services $100,000 2,600 Settlement Theft of unencrypted laptop containing PHI
2017 NJ Horizon Healthcare Services Inc., $1,100,000 3.7 million Settlement Loss of unencrypted laptop computers
2017 VT SAManage USA, Inc. $264,000 660 Settlement Spreadsheet indexed by search engines and PHI viewable
2017 NY CoPilot Provider Support Services, Inc $130,000 221,178 Settlement Delayed breach notification
2015 NY University of Rochester Medical Center $15,000 3,403 Settlement List of patients provided to nurse who took it to a new employer
2015 CT Hartford Hospital/ EMC Corporation $90,000 8,883 Settlement Theft of unencrypted laptop containing PHI
2014 MA Women & Infants Hospital of Rhode Island $150,000 12,000 Settlement Loss of backup tapes containing PHI
2014 MA Boston Children’s Hospital $40,000 2,159 Settlement Loss of laptop containing PHI
2014 MA Beth Israel Deaconess Medical Center $100,000 3,796 Settlement Loss of laptop containing PHI
2013 MA Goldthwait Associates $140,000 67,000 Settlement Improper disposal
2012 MN Accretive Health $2,500,000 24,000 Settlement Mishandling of PHI
2012 MA South Shore Hospital $750,000 800,000 Settlement Loss of backup tapes containing PHI
2011 VT Health Net Inc. $55,000 1,500,000 Settlement Loss of unencrypted hard drive/delayed breach notifications
2011 IN WellPoint Inc. $100,000 32,000 Settlement Failure to report breach in a reasonable timeframe
2010 CT Health Net Inc. $250,000 1,500,000 Settlement Loss of unencrypted hard drive/delayed breach notifications

The post Healthcare Data Breach Statistics appeared first on HIPAA Journal.
Analysis of February 2018 Healthcare Data Breaches

Our February 2018 healthcare data breach report details the major data breaches reported by healthcare providers, health plans, and business associates in February 2018.

Summary of February 2018 Healthcare Data Breaches

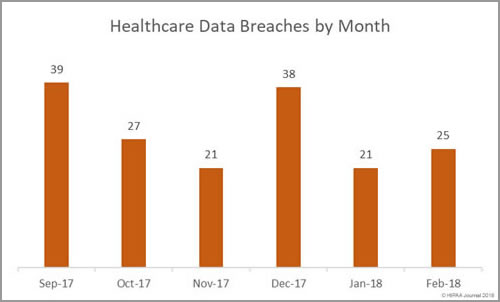
February may have been a shorter month, but there was an increase in the number of healthcare data breaches reported to the Department of Health and Human Services’ Office for Civil Rights. In February, HIPAA covered entities and business associates reported 25 breaches – a 19% month on month increase in breaches.

Healthcare Data Breaches by Month

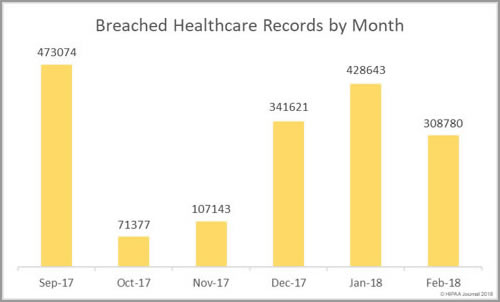
While there was a higher breach tally this month, the number of healthcare records exposed as a result of healthcare data breaches fell by more than 100,000. In January 428,643 healthcare records were exposed. February 2018 healthcare data breaches saw 308,780 healthcare records exposed.

Records exposed in Healthcare Data Breaches

Largest Healthcare Data Breaches of February 2018

The largest healthcare data breaches reported to the Office for Civil Rights in February are listed below.

Covered Entity Covered Entity Type Individuals Affected Type of Breach Location of PHI
St. Peter’s Surgery & Endoscopy Center Healthcare Provider 134,512 Hacking/IT Incident Network Server
Tufts Associated Health Maintenance Organization, Inc. Health Plan 70,320 Unauthorized Access/Disclosure Paper/Films
Triple-S Advantage, Inc. Health Plan 36,305 Unauthorized Access/Disclosure Paper/Films
CarePlus Health Plan Health Plan 11,248 Unauthorized Access/Disclosure Paper/Films
Union Lake Supermarket, LLC Healthcare Provider 9,956 Improper Disposal Other Portable Electronic Device

The top five data breaches were responsible for 85% of all exposed healthcare records in February. The largest data breach – a malware-related incident at St. Peter’s Surgery & Endoscopy Center – accounted for 43.6% of the exposed healthcare records in February.

Main Causes of February 2018 Healthcare Data Breaches

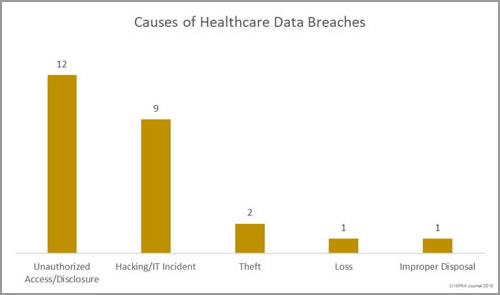
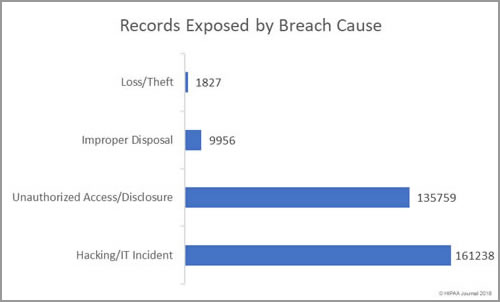
Unauthorized access/disclosures topped the list of the main causes of healthcare data breaches in February 2018 with 12 incidents and included three of the most serious breaches. Hacking incidents were in close second with 9 breaches, followed by three loss/theft incidents and one case of improper disposal of ePHI.

Causes of February 2018 Healthcare Data Breaches

Records Exposed by Breach Type

Hacking/IT incidents were the second biggest cause of healthcare data breaches in February, but the incidents resulted in the exposure/theft of the largest amount of healthcare data.

Records Exposed by Breach Type

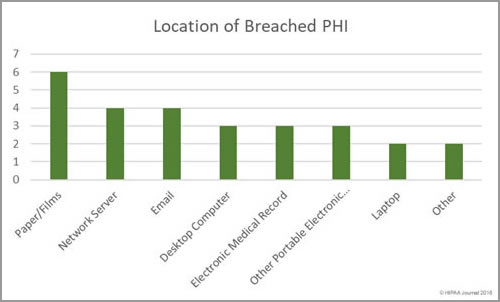
Location of Breached Records

Overall, there were more breaches involving electronic health data than physical records, although breaches involving paper/films were the most numerous with 6 incidents. The breach reports show that while technological controls are essential to prevent hacks and unauthorized access/disclosures of electronic records, physical security is important for paper records and administrative safeguards are necessary to prevent unauthorized access. All six of the breaches involving paper/films were unauthorized access/disclosures.

Location of breached healthcare records (February 2018)

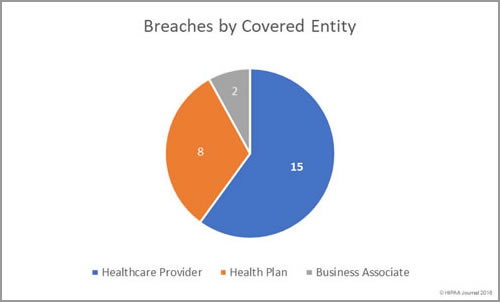
Data Breaches by Covered Entity

Healthcare providers were the worst affected by data breaches in February with 15 incidents (reported by 14 healthcare providers). There were three breaches reported by pharmacies in February. 8 data breaches were reported by 7 health plans and two security incidents were reported by business associates.

Data Breaches by Covered Entity (February 2018)

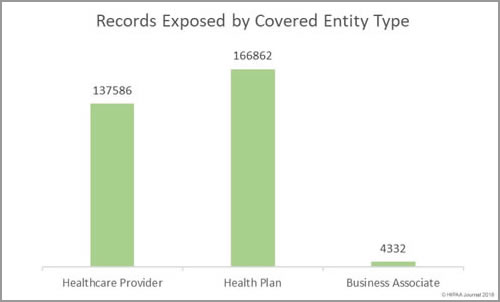
Healthcare provider breaches exposed the most health records in February. 168,732 records were exposed by healthcare providers. The mean breach size was 11,248 records and the median breach size was 1,670 records.

Health plans experienced fewer breaches, but the incidents were more severe. 133,580 records were exposed by health plans. The mean breach size was 16,698 records and the median breach size was 6,075 records. The mean and median breach size for business associate data breaches was 3,234 records.

Records exposed by covered entity (February 2018)

February 2018 Healthcare Data Breaches by State

Healthcare organizations based in 18 states reported data breaches in February 2018. There were six states that experienced 2 data breaches– Alabama, California, Massachusetts, Mississippi, Rhode Island, and Wisconsin.

Arkansas, Connecticut, Illinois, Kentucky, Maine, Michigan, Missouri, North Carolina, New Jersey, New York, Tennessee, and Virginia each had one data breach reported.

Financial Penalties for HIPAA Covered Entities in February 2018

The Office for Civil Rights settled one HIPAA violation case in February. Filefax Inc, agreed to settle potential HIPAA violations with OCR for $100,000. The financial penalty sent a message to HIPAA-covered entities and their business associates that HIPAA responsibilities do not end when a business ceases trading. The fine relates to HIPAA violations that occurred after the business closed – the improper disposal of paperwork containing protected health information.

The post Analysis of February 2018 Healthcare Data Breaches appeared first on HIPAA Journal.
NH-ISAC Partnership with Anomali Helps Accelerate Threat Detection and Information Sharing in Healthcare

Anomali has partnered with the National Health Information Sharing and Analysis Center (NH-ISAC) and will be providing threat intelligence to healthcare organizations through NH-ISAC. Anomali will be providing NH-ISAC with the required tools and infrastructure to allow its members to collaborate and share threat intelligence with other members.

Anomali will be providing up to date threat intelligence on new and current external threats specific to the healthcare industry allowing NH-ISAC members to take proactive steps to minimize risk. Anomali’s early warning system helps healthcare organizations respond to threats quickly when suspicious activity is detected on a network.

NH-ISAC members include hospitals, health insurers, medical research institutions, pharma companies, ambulatory providers, medical device manufacturers and other healthcare stakeholders. NH-ISAC community members help each other use physical and cyber threat intelligence to inform security decisions and mitigate threats.

The new collaboration between NH-ISAC and Anomali will help empower the healthcare community to identify and respond to cyber threats. Anomali provides actionable threat intelligence that can be consumed by healthcare organizations and used to compliment internal security threat monitoring programs

The Anomali platform automates collection, normalization, and integration of threat intelligence from a wide range of different sources. The platform allows seamless collaboration with peers in other organizations through Anomali Trusted Circles and gives healthcare organizations complete visibility into attacks that threaten the confidentiality of protected health information and the security of the networks on which the information is stored. A threat detection by one member helps other organizations take preventative steps to block attacks before they occur.

“Sharing threat intelligence among member firms is one of the most essential services of any ISAC. The NH-ISAC Board is pleased with the opportunity to work with the Threatstream platform to enhance threat intelligence sharing for the healthcare sector,” said Jim Routh, NH-ISAC board member.

The post NH-ISAC Partnership with Anomali Helps Accelerate Threat Detection and Information Sharing in Healthcare appeared first on HIPAA Journal.