Healthcare Cybersecurity

How to Defend Against Insider Threats in Healthcare

One of the biggest data security challenges is how to defend against insider threats in healthcare. Insiders are responsible for more healthcare data breaches than hackers, making the industry unique.

Verizon’s Protected Health Information Data Breach Report highlights the extent of the problem. The report shows 58% of all healthcare data breaches and security incidents are the result of insiders.

Healthcare organizations also struggle to detect insider breaches, with many breaches going undetected for months or even years. One healthcare employee at a Massachusetts hospital was discovered to have been accessing healthcare records without authorization for 14 years before the privacy violations were detected, during which time the records of more than 1,000 patients had been viewed.

Healthcare organizations must not only take steps to reduce the potential for insider breaches, they should also implement technological solutions, policies, and procedures that allow breaches to be detected rapidly when they do occur.

What are Insider Threats?

Before explaining how healthcare organizations can protected against insider threats, it is worthwhile covering the main insider threats in healthcare.

An insider threat is one that comes from within an organization. That means an individual who has authorization to access healthcare resources, which includes EMRs, healthcare networks, email accounts, or documents containing PHI. Resources can be accessed with malicious intent, but oftentimes mistakes are made that can equally result in harm being caused to the organization, its employees, or its patients.

Insider threats are not limited to employees. Any individual who is given access to networks, email accounts, or sensitive information in order to complete certain tasks could deliberately or accidentally take actions that could negatively affect an organization. That includes business associates, subcontractors of business associates, researchers, volunteers, and former employees.

The consequences of insider breaches can be severe. Healthcare organizations can receive heavy fines for breaches of HIPAA Rules and violations of patient privacy, insider breaches can damage an organization’s reputation, cause a loss of patient confidence, and leave organizations open to lawsuits.

According to the CERT Insider Threat Center, insider breaches are twice as costly and damaging as external threats. To make matters worse, 75% of insider threats go unnoticed.

Insider threats in healthcare can be split into two main categories based on the intentions of the insider: Malicious and non-malicious.

Malicious Insider Threats in Healthcare

Malicious insider threats in healthcare are those which involve deliberate attempts to cause harm, either to the organization, employees, patients, or other individuals. These include the theft of protected health information such as social security numbers/personal information for identity theft and fraud, the theft of data to take to new employers, theft of intellectual property, and sabotage.

Research by Verizon indicates 48% of insider breaches are conducted for financial gain, and with healthcare data fetching a high price on the black market, employees can easily be tempted to steal data.

A 2018 Accenture survey conducted on healthcare employees revealed one in five would be prepared to access and sell confidential data if the price was right. 18% of the 912 employees surveyed said they would steal data for between $500 and $1,000.

Alarmingly, the survey revealed that almost a quarter (24%) of surveyed healthcare employees knew of someone who had stolen data or sold their login credentials to an unauthorized outsider.

Disgruntled employees may attempt to sabotage IT systems or steal and hold data in case they are terminated. However, not all acts of sabotage are directed against employers. One notable example comes from Texas, where a healthcare worker used hospital devices to create a botnet that was used to attack a hacking group.

Non-Malicious Insider Threats in Healthcare

The Breach Barometer reports from Protenus/databreaches.net break down monthly data breaches by breach cause, including the number of breaches caused by insiders. All too often, insiders are responsible for more breaches than outsiders.

Snooping on medical records is all too common. When a celebrity is admitted to hospital, employees may be tempted to sneak a look at their medical records, or those of friends, family members, and ex-partners. The motivations of the employees are diverse. The Verizon report suggests 31% of insider breaches were employees accessing records out of curiosity, and a further 10% were because employees simply had access to patient records.

Other non-malicious threats include the accidental loss/disclosure of sensitive information, such as disclosing sensitive patient information to others, sharing login credentials, writing down login credentials, or responding to phishing messages.

The largest healthcare data breach in history – the theft of 78 million healthcare records from Anthem Inc.- is believed to have been made possible because of stolen credentials.

The failure to ensure PHI is emailed to the correct recipient, the misdirection of fax messages, or leaving portable electronic devices containing ePHI unattended causes many breaches each year. The Department of Health and Human Services’ Office for Civil Rights’ breach portal or ‘Wall of Shame’ is littered with incidents involving laptops, portable hard drives, smartphones, and zip drives that have stolen after being left unattended.

How to Defend Against Insider Threats in Healthcare

The standard approach to mitigating insider threats can be broken down into four stages: Educate, Deter, Detect, and Investigate.

Educate: The workforce must be educated on allowable uses and disclosures of PHI, the risk associated with certain behaviors, patient privacy, and data security.

Deter: Policies must be developed to reduce risk and those policies enforced. The repercussions of HIPAA violations and privacy breaches should be clearly explained to employees.

Detect: Healthcare organizations should implement technological solutions that allow them to detect breaches rapidly and access logs should be regularly checked.

Investigate: When potential privacy and security breaches are detected they must be investigated promptly to limit the harm caused. When the cause of the breach is determined, steps should be taken to prevent a recurrence.

Some of the specific steps that can be taken to defend against insider threats in healthcare are detailed below:

Perform Background Checks

It should be standard practice to conduct a background check before any individual is employed. Checks should include contacting previous employers, Google searches, and a check of a potential employee’s social media accounts.

HIPAA training

All healthcare employees should be made aware of their responsibilities under HIPAA. Training should be provided as soon as possible, and ideally before network or PHI access is provided. Employees should be trained on HIPAA Privacy and Security Rules and informed of the consequences of violations, including loss of employment, possible fines, and potential criminal penalties for HIPAA violations.

Implement anti-phishing defenses

Phishing is the number one cause of data breaches. Healthcare employees are targeted as it is far easier to gain access to healthcare data if an employee provides login credentials than attempting to find software vulnerabilities to exploit. Strong anti-phishing defenses will prevent the majority of phishing emails from reaching inboxes. Advanced spam filtering software is now essential.

Security awareness training

Since no technological solution will prevent all phishing emails from reaching inboxes, it is essential – from a security and compliance perspective – to teach employees the necessary skills that will allow them to identify phishing attempts and other email/web-based threats.

Employees cannot be expected to know what actions place data and networks at risk. These must be explained if organizations want to eradicate risky behavior. Security awareness training should also be assessed. Phishing simulation exercises can help to reinforce training and identify areas of weakness that can be tackled with further training.

Encourage employees to report suspicious activity

Employees are often best placed to identify potential threats, such as changes in the behavior of co-workers. Employees should be encouraged to report potentially suspicious behavior and violations of HIPAA Rules.

While Edward Snowden did not work in healthcare, his actions illustrate this well. The NSA breach could have been avoided if his requests for co-workers’ credentials were reported.

Controlling access to sensitive information

The fewer privileges employees have, the easier it is to prevent insider breaches in healthcare. Limiting data access to the minimum necessary amount will limit the harm caused in the event of a breach. You should be implementing the principle of least privilege. Give employees access to the least amount of data as possible. This will limit the data that can be viewed or stolen by employees or hackers that manage to obtain login credentials.

Encrypt PHI on all portable devices

Portable electronic devices can easily be stolen, but the theft of a device need not result in the exposure of PHI. If full disk encryption is used, the theft of the device would not be a reportable incident and patients’ privacy would be protected.

Enforce the use of strong passwords

Employees can be told to use strong passwords or long passphrases, but unless password policies are enforced, there will always be one employee that chooses to ignore those policies and set a weak password. You should ensure that commonly used passwords and weak passwords cannot be set.

Use two-factor authentication

Two-factor authentication requires the use of a password for account access along with a security token. These controls prevent unauthorized access by outsiders, as well as limiting the potential for an employee to use another employee’s credentials.

Terminate access when no longer required

You should have a policy in place that requires logins to be deleted when an employee is terminated, a contract is completed, or employees leave to work for another organization. There have been many data breaches caused by delays in deleting data access rights. Data access should not be possible from the second an employee walks out the door for the last time.

Monitor Employee Activity

If employees require access to sensitive data for work purposes it can be difficult to differentiate between legitimate data access and harmful actions. HIPAA requires PHI access logs to be maintained and regularly checked. Since this is a labor-intensive task, it is often conducted far too infrequently. The easiest way to ensure inappropriate accessing of medical records is detected quickly is to implement action monitoring software and other software tools that can detect anomalies in user activity and suspicious changes in data access patterns.

The post How to Defend Against Insider Threats in Healthcare appeared first on HIPAA Journal.
House Committee Seeks Advice from Industry Stakeholders on Fixing Cybersecurity Flaws

The continued use of outdated software and the failure to patch vulnerabilities promptly is making cyberattacks on healthcare organizations too easy. This was clearly highlighted by the WannaCry ransomware attacks in May 2017. U.S healthcare providers may have escaped relatively unscathed, but that was not the case across the Atlantic in the UK. The NHS was hit particularly badly by WannaCry. Were it not for the discovery of a kill switch by a security researcher, it could have been a similar story in the U.S.

This week, Symantec published a report on a recently discovered threat group that has been attacking healthcare organizations for three years and accessing highly sensitive information. Lateral movement within a network has been made easy due to the continued use of outdated operating systems.

These are just two examples of several over the past couple of years and the attacks will continue unless action is taken to address the issue.

In the UK, a post-WannaCry assessment by the health industry’s governing body revealed the NHS is still badly prepared for similar attacks. Many vulnerabilities remain unpatched and outdated and unsupported operating systems are still widely used.

Healthcare organizations on both sides of the Atlantic have upgraded some systems but many healthcare providers still rely on legacy software and equipment. All too often there is a lack of visibility into all devices connected to healthcare networks which hampers the remediation of vulnerabilities. Patching all systems promptly remains a major challenge in healthcare.

Action is being taken to address medical device security although progress is slow. Recently, the U.S Food and Drug Administration announced a new plan which will require all medical device manufacturers to incorporate the capability to update their devices throughout the entire life cycle of the products. While such measures will certainly help to keep new medical devices secure, it will do nothing to address the problem with older devices.

The use of legacy software and outdated equipment will continue to leave healthcare organizations vulnerable, but all too often there is little alternative. Aging devices and outdated software continue to be used because there are currently no viable alternatives. Even when it is possible to update devices and operating systems, identifying and managing vulnerabilities is a major challenge, and one that comes at a considerable cost.

Healthcare providers are often forced to conduct a cost-benefit analysis to determine the value of continued use of certain technologies and the cost of remediating vulnerabilities. If the cost of updating and maintaining the devices is too high and there are no viable alternatives that provide the same benefits, the risks associated with the devices have to be accepted.

Even if manufacturers were forced to continue to provide updates to legacy software and equipment, the time and resources that would need to be devoted to cybersecurity would undoubtedly have a negative impact on the ability of manufacturer to develop new devices and more advanced treatments, which would have a negative impact on patients. Unfortunately, there does not appear to be an easy solution.

The U.S. House Energy and Commerce Committee is well aware of the problem and is now seeking help from industry stakeholders on how best to tackle the issue and improve cybersecurity.

“Though hard data about the exact costs are difficult to determine, one cybersecurity professional estimated that fixing a single vulnerability may cost an organization anywhere from $400 to $4,000,” wrote the Committee in its recent Supported Lifetimes Request for Information. “Considering the fact that many popular medical technologies leverage software and hardware with hundreds to thousands of known vulnerabilities, let alone unknown ones, vulnerability identification and management can quickly become a daunting task.”

“To understand the full scope of the challenge and potential paths to address it, we require insight from stakeholders of all sizes, from all parts of the health care sector.”  Input from industry stakeholders and others has been requested by May 31, 2018.

The House Committee on Energy and Commerce Request for Information on Supported Lifetimes can be viewed on this link.

The post House Committee Seeks Advice from Industry Stakeholders on Fixing Cybersecurity Flaws appeared first on HIPAA Journal.

Report: Healthcare Data Breaches in Q1, 2018

The first three months of 2018 have seen 77 healthcare data breaches reported to the Department of Health and Human Services’ Office for Civil Rights (OCR). Those breaches have impacted more than one million patients and health plan members – Almost twice the number of individuals that were impacted by healthcare data breaches in Q4, 2017.

There was a 10.5% fall in the number of data breaches reported quarter over quarter, but the severity of breaches increased. The mean breach size increased by 130.57% and there was a 15.37% increase in the median breach size.

In Q4, 2017, the mean breach size was 6,048 healthcare records and the median breach size was 1,666 records. In Q1, 2018, the mean breach size was 13,945 records and the median breach size was 1,922 records.

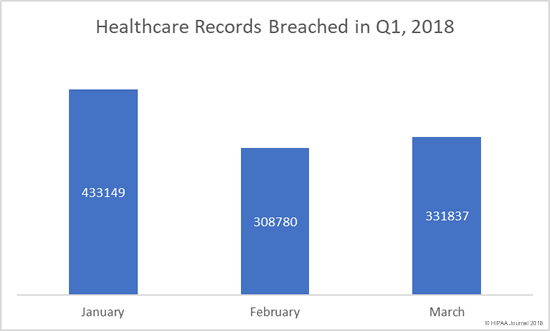
Between January 1 and March 31, 2018, 1,073,766 individuals had their PHI exposed, viewed, or stolen compared to 520,141 individuals in Q4, 2017.

Individuals Impacted by Healthcare Data Breaches in Q1, 2018

Healthcare Records Breached in Q1, 2018

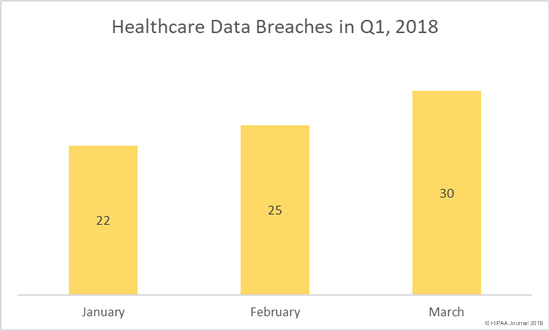
Throughout 2017, healthcare data breaches were occurring at a rate of more than one per day. Compared to 2017, January was a relatively good month for the healthcare industry, with just 22 security incidents reported to the HHS’ Office for Civil Rights.

However, January also saw the largest healthcare data breach of the quarter reported – A hacking incident that potentially resulted in the theft of almost 280,000 records. That incident made January the worst month in terms of the number of healthcare records exposed.

The number of reported data breaches also increased each month, In March, breaches were being reported at the typical rate of one per day.

Q1, 2018 Healthcare Data Breaches

Healthcare Data Breaches in Q1, 2018

Main Causes of Healthcare Data Breaches in Q1, 2018

The healthcare industry is something of an anomaly when it comes to data breaches. In other industries, hacking/IT incidents dominate the breach reports; however, the healthcare industry is unique as insiders cause the most data breaches.

Once again, insiders were behind the majority of breaches. Unauthorized access/disclosure incidents, loss of physical records and devices containing ePHI, and improper disposal incidents accounted for 59.74% of the 77 breaches reported in Q1.

The main cause of breaches in Q1, 2018 was unauthorized access/disclosures – 35 incidents and 45.45% of the total breaches reported in Q1. There were 15 breaches involving the loss or theft of electronic devices containing ePHI, all of which could have been prevented had encryption been used.

Causes of Healthcare Data Breaches, Q1, 2018

Healthcare Records Exposed in Q1, 2018 by Breach Cause

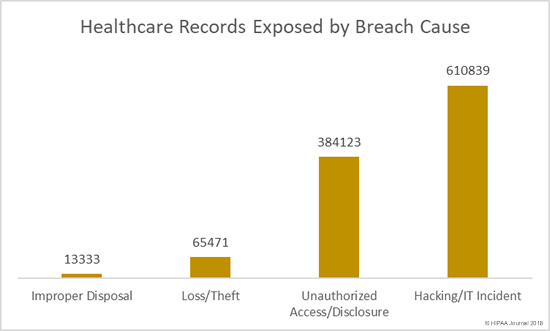
Unauthorized access/disclosure incidents were more numerous than hacking incidents in Q1, although more healthcare records were exposed/stolen in hacking/IT incidents than all other causes of breaches combined.

Healthcare Records Exposed by Breach Cause

Location of Breached PHI in Q1, 2018

Healthcare security teams may be focused on securing the perimeter and preventing hackers from accessing and stealing electronic health information, but it is important not to neglect physical records.  As was the case in Q4, 2017, physical records were the top location of breached PHI in Q1, 2018.

Email, which includes social engineering, phishing attacks and misdirected emails, was the second most common location of breached PHI followed by network servers.

Location of Breached PHI - Q1, 2018

Largest Healthcare Data Breaches of Q1, 2018

In Q1, 2018, there were 18 healthcare security breaches that impacted more than 10,000 individuals. Hacking/IT incidents tend to involve more records than any other breach cause, although in Q1, 2018, there were several large-scale unauthorized access/disclosure incidents, including five of the top ten breaches of the quarter.

The two largest breaches of the year to date affected Oklahoma State University Center for Health Sciences and St. Peter’s Surgery & Endoscopy Center. In both cases a hacker gained access to the network and potentially viewed/obtained patients’ PHI.

The five largest breaches of the quarter accounted for 57% of all records exposed in the quarter. The top 18 data breaches accounted for 87% of all records exposed in the quarter.

Name of Covered Entity Covered Entity Type Individuals Affected Type of Breach
Oklahoma State University Center for Health Sciences Healthcare Provider 279865 Hacking/IT Incident
St. Peter’s Surgery & Endoscopy Center Healthcare Provider 134512 Hacking/IT Incident
Tufts Associated Health Maintenance Organization, Inc. Health Plan 70320 Unauthorized Access/Disclosure
Florida Agency Persons for Disabilities Health Plan 63627 Unauthorized Access/Disclosure
Middletown Medical P.C. Healthcare Provider 63551 Unauthorized Access/Disclosure
Onco360 and CareMed Specialty Pharmacy Healthcare Provider 53173 Hacking/IT Incident
Triple-S Advantage, Inc. Health Plan 36305 Unauthorized Access/Disclosure
ATI Holdings, LLC and its subsidiaries Healthcare Provider 35136 Hacking/IT Incident
City of Houston Medical Plan Health Plan 34637 Theft
Mississippi State Department of Health Healthcare Provider 30799 Unauthorized Access/Disclosure
Agency for Health Care Administration Health Plan 30000 Hacking/IT Incident
Decatur County General Hospital Healthcare Provider 24000 Hacking/IT Incident
Barnes-Jewish Hospital Healthcare Provider 18436 Unauthorized Access/Disclosure
Barnes-Jewish St. Peters Hospital Healthcare Provider 15046 Unauthorized Access/Disclosure
Special Agents Mutual Benefit Association Health Plan 13942 Unauthorized Access/Disclosure
Guardian Pharmacy of Jacksonville Healthcare Provider 11521 Hacking/IT Incident
CarePlus Health Plan Health Plan 11248 Unauthorized Access/Disclosure
Primary Health Care, Inc. Healthcare Provider 10313 Unauthorized Access/Disclosure

Healthcare Data Breaches in Q1, 2018 by Covered Entity

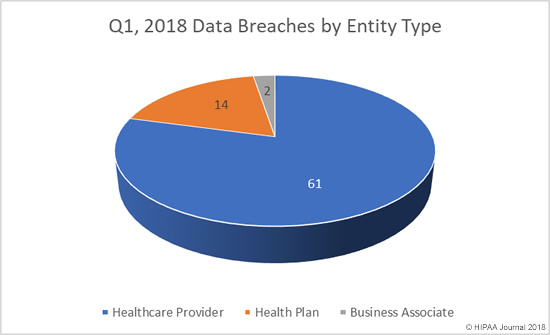
Healthcare providers were the worst affected by healthcare data breaches in Q1, 2018. As was the case in Q4, 2017, 14 health plans experienced a breach of more than 500 records. There were half the number of business associate breaches in Q1, 2018 as there were in Q4, 2017.

Q1, 2018 Healthcare Data Breaches by Entity Type

Healthcare Data Breaches in Q1, 2018 by State

In Q1, healthcare organizations based in 35 states reported breaches of more than 500 records. The worst affected state was California with 11 reported breaches, followed by Massachusetts with 8 security incidents.

There were four security incidents in both Missouri and New York, and three breaches reported by healthcare organizations based in Florida, Illinois, Maryland, Mississippi, Tennessee, and Wisconsin.

Healthcare organizations based in Alabama, Arkansas, Kentucky, Rhode Island, Texas, and Wyoming reported two breaches.

There was one breach experienced in Colorado, Connecticut, District of Columbia, Georgia, Iowa, Maine, Michigan, Minnesota, North Carolina, New Jersey, New Mexico, Nevada, Ohio, Oklahoma, Pennsylvania, Utah, Virginia, Washington and West Virginia.

The post Report: Healthcare Data Breaches in Q1, 2018 appeared first on HIPAA Journal.
Kwampirs Backdoor Used in Targeted Attacks on Healthcare Industry

A relatively recently identified threat group known as Orangeworm is conducting targeted attacks on large healthcare organizations in the United States according to Symantec.

The threat group was first identified in January 2015 and has been conducting supply chain attacks with the aim of installing backdoors on devices used by large healthcare firms. Already, several healthcare providers, IT solution providers, pharmaceutical firms, and medical equipment manufacturers have been attacked.

The Orangeworm threat group has conducted attacks on a wide range of industries, including manufacturing, agriculture, IT, and logistics. Even though these attacks have taken place on companies in seemingly unrelated industries, many targeted companies in these sectors have links to healthcare organizations, such as logistics firms that deliver medical supplies, IT firms that have contracts with healthcare providers, and manufacturers of medical imaging devices. 39% of all confirmed attacks have been on firms operating in the healthcare sector.

Rather than use the spray and pray tactics of ransomware gangs, the Orangeworm attacks appear to be highly targeted. Companies are carefully researched before the attacks take place.

Symantec notes that while attacks have taken place in several countries, the U.S is the most targeted country accounting for 17% of attacks. Large firms operating in the healthcare sector, in particular those with large international operations, appear to be the primary targets.

A common denominator in many of the attacks is the devices on which the backdoor has been installed are used in conjunction with medical imaging devices, such as MRI and X-Ray machines. Several attacks have targeted machines used to help patients complete consent forms for medical procedures.

Once access is gained to a machine and the attackers have determined the device is of value, the Kwampirs backdoor is deployed. Using that device, the threat actors gather information on the device, network shares, mapped drives, and files stored on the infected machine. The Kwampirs backdoor is then aggressively copied onto other machines via network shares. Windows XP machines are most susceptible to this type of attack, which could suggest why machines linked to imaging devices are commonly infected – many of which still run on Windows XP.

Symantec has not discovered any evidence that points to this being a nation-state sponsored attack and suggests this could be the work of an individual or a small group of hackers. It is currently unclear why the attacks are taking place and what the ultimate aim of the attackers is. It is possible that the backdoor is being installed for future attacks on healthcare organizations or to steal patient data, although Symantec suggests the threat group is attacking healthcare firms for corporate espionage purposes.

Fortunately, the attackers do not appear to be overly concerned with being detected. The method used to spread the backdoor laterally is particularly noisy and relatively easy to identify, although some attempts have been made to avoid hash-based detection, such as inserting a random string into the middle of the decrypted payload before it is written to the disk.

Healthcare organizations are being encouraged to analyze their networks and machines for signs of infection using Symantec’s Orangeworm indicators of compromise (PDF).

The post Kwampirs Backdoor Used in Targeted Attacks on Healthcare Industry appeared first on HIPAA Journal.
FDA Develops Five-Point Action Plan for Improving Medical Device Cybersecurity

The past few years have seen an explosion in the number of medical devices that have come to market. While those devices have allowed healthcare providers and patients to monitor and manage health in more ways that has ever been possible, concerns have been raised about medical device cybersecurity.

Medical devices collect, store, receive, and transmit sensitive information either directly or indirectly through the systems to which they connect. While there are clear health benefits to be gained from using these devices, any device that collects, receives, stores, or transmits protected health information introduces a risk of that information being exposed.

The FDA reports that in the past year, a record number of novel devices have been approved for use in the United States and that we are currently enjoying “an unparalleled period of invention in medical devices.” The FDA is encouraging the development of novel devices to address health needs, while balancing the risks and benefits.

The FDA has been working closely with healthcare providers, patients, and device manufacturers to understand and address any risks associated with the devices. Part of the FDA’s efforts in this area involve the development of new frameworks for identifying risks and protecting consumers.

To further protect patients and help reduce risks to a minimal level, the FDA has developed a five-point action plan (PDF). Under the plan the FDA will continue to encourage the development of new devices to address unmet health needs, while also enhancing security controls to ensure patient data remains private and confidential.

Improving Medical Device Cybersecurity

The FDA will be reorganizing its medical device center and will consolidate its premarket and postmarket offices. By leveraging the expert knowledge of staff in both offices and adopting a more integrated approach the FDA will be able to optimize decision-making. The FDA is also adopting a ‘Total Product Life Cycle’ (TPLC) approach to ensure device safety for the entire lifespan of the products.

While risks can be evaluated before the devices come to market, oftentimes those risks are not fully understood until the devices have been released and are being used by a wide range of patients and providers in different settings.

Naturally, when risks are identified in postmarket devices there needs to be a mechanism in place that allows the devices to be updated. The FDA will be exploring various regulatory options to ensure timely mitigations can be implemented, including the ability for all devices to receive updates and security patches to address newly discovered vulnerabilities.

While the FDA can ensure medical device labelling is improved to make providers aware of the safety and effectiveness of the devices, the FDA is considering additional training for providers and further education of users of the devices. The FDA also plans to develop scientific tool kits that can be used by manufacturers to ensure their premarket devices meet safety standards.

To encourage manufacturers to incorporate advanced medical device cybersecurity controls, the FDA is looking into ways it can streamline and speed up the reviewing of devices that meet and exceed safety standards.

The FDA is already promoting “a multi-stakeholder, multi-faceted approach of vigilance, responsiveness, recovery, and resilience” to ensure devices remain safe throughout their entire life cycle. The FDA is also seeking additional funding and authority to develop a public-private CyberMed Safety Analysis Board to assist with medical device cybersecurity issues, vulnerability coordination, and response mechanisms.

Members of the board would include biomedical engineers, clinicians, and cybersecurity experts who would advise both the FDA and device manufacturers on cybersecurity issues and provide assistance with adjudicating disputes.

The post FDA Develops Five-Point Action Plan for Improving Medical Device Cybersecurity appeared first on HIPAA Journal.
Version 1.1 of the NIST Cybersecurity Framework Released

On April 16, 2018, The National Institute of Standards and Technology released an updated version of its Framework for Improving Critical Infrastructure Cybersecurity (Cybersecurity Framework).

The Cybersecurity Framework was first issued in February 2014 and has been widely adopted by critical infrastructure owners and public and private sector organizations to guide their cybersecurity programs. While intended for use by critical infrastructure industries, the flexibility of the framework means it can also be adopted by a wide range of businesses, large and small, including healthcare organizations.

The Cybersecurity Framework incorporates guidelines, standards, and best practices and offers a flexible approach to cybersecurity. There are several ways that the Framework can be used with ample scope for customization. The Framework helps organizations address different threats and vulnerabilities and matches various levels of risk tolerance.

The Framework was intended to be a living document that can be updated and improved over time in response to feedback from users, changing best practices, new threats, and advances in technology. The new version is the first major update to the framework since 2014 and the result of two years of development.

NIST’s Matt Barrett, program manager for the Cybersecurity Framework, explained that the latest version “refines, clarifies and enhances version 1.0.” While several changes have been made in version 1.1, Barrett explained, “It is still flexible to meet an individual organization’s business or mission needs and applies to a wide range of technology environments such as information technology, industrial control systems and the Internet of Things.”

Version 1.1 of the Cybersecurity Framework includes several updates in response to comments and feedback received in 2016 and 2017 from organizations that have already adopted the Framework.

Version 1.1 sees refinements to the guidelines on authentication, authorization and identity proofing and a better explanation of the relationship between implementation tiers and profiles. The Framework for Cyber Supply Chain Risk Management has been significantly expanded and there is a new section on self-assessment of cybersecurity risk. The section on disclosure of vulnerabilities as also been expanded with a new subcategory added related to the vulnerability disclosure lifecycle.

“Cybersecurity is critical for national and economic security,” said Secretary of Commerce Wilbur Ross. “The voluntary NIST Cybersecurity Framework should be every company’s first line of defense. Adopting version 1.1 is a must do for all CEO’s.”

NIST is also planning to release a companion ‘Roadmap for Improving Critical Infrastructure Cybersecurity’ later this year and will be hosting a webinar later this month to explain and discuss the version 1.1 updates to the Framework.

The post Version 1.1 of the NIST Cybersecurity Framework Released appeared first on HIPAA Journal.
Analysis of March 2018 Healthcare Data Breaches

There has been a month-over-month increase in healthcare data breaches. In March 2018, 29 security incidents were reported by HIPAA covered entities compared to 25 incidents in February.

March 2018 Healthcare Data Breaches

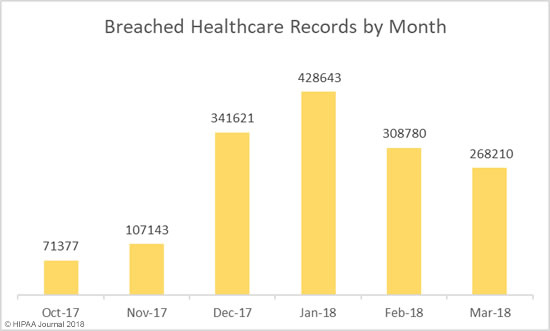
Even though more data breaches were reported in March, there was a fall in the number of individuals impacted by breaches. March 2018 healthcare data breaches saw 268,210 healthcare records exposed – a 13.13% decrease from the 308,780 records exposed in incidents in February.

Records exposed by Healthcare Data Breaches (March 2018)

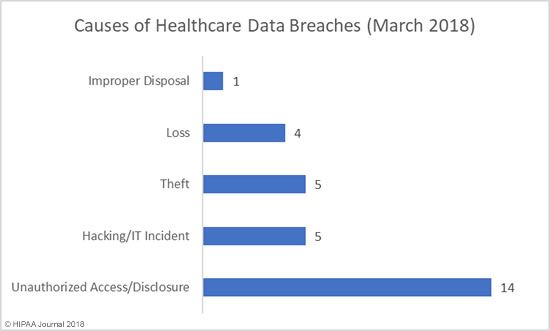
Causes of March 2018 Healthcare Data Breaches

March saw the publication of the Verizon Data Breach Investigations Report which confirmed the healthcare industry is the only vertical where more data breaches are caused by insiders than hackers. That trend continued in March. Unauthorized access/disclosures, loss of devices/records, and improper disposal incidents were behind 19 of the 29 incidents reported – 65.5% of all incidents reported in March.

The main cause of healthcare data breaches in March 2018 was unauthorized access/disclosure incidents. 14 incidents were reported, with theft/loss incidents the second main cause with 9 incidents, followed by hacking/IT incidents with 5 breaches reported.

Severity of Breaches by Breach Cause

Breach Cause Total Records Exposed in March Median Records Exposed Mean Records Exposed
Unauthorized Access/Disclosure 166,859 3,551 11,919
Hacking/IT Incident 54,814 5,207 10,963
Theft 40,018 1,424 8,004
Loss 5,107 1,096 1,277
Improper Disposal 1,412 1,412 1,412

Largest Healthcare Data Breaches Reported in March 2018

There were ten healthcare data breaches reported in March that impacted more than 10,000 individuals. The largest data breach resulted in the exposure of 63,551 individuals’ PHI. That incident occurred and was discovered in December 2016, although the incident has only just been reported to the HHS’ Office for Civil Rights.

While hacking incidents usually result in the highest number of exposed/compromised records, in March it was unauthorized access/disclosure incidents that dominated the breach reports.

Name of Covered Entity Covered Entity Type Individuals Affected Type of Breach
Middletown Medical P.C. Healthcare Provider 63,551 Unauthorized Access/Disclosure
ATI Holdings, LLC and its subsidiaries Healthcare Provider 35,136 Hacking/IT Incident
City of Houston Medical Plan Health Plan 34,637 Theft
Mississippi State Department of Health Healthcare Provider 30,799 Unauthorized Access/Disclosure
Barnes-Jewish Hospital Healthcare Provider 18,436 Unauthorized Access/Disclosure
Barnes-Jewish St. Peters Hospital Healthcare Provider 15,046 Unauthorized Access/Disclosure
Special Agents Mutual Benefit Association Health Plan 13,942 Unauthorized Access/Disclosure
Guardian Pharmacy of Jacksonville Healthcare Provider 11,521 Hacking/IT Incident
Primary Health Care, Inc. Healthcare Provider 10,313 Unauthorized Access/Disclosure

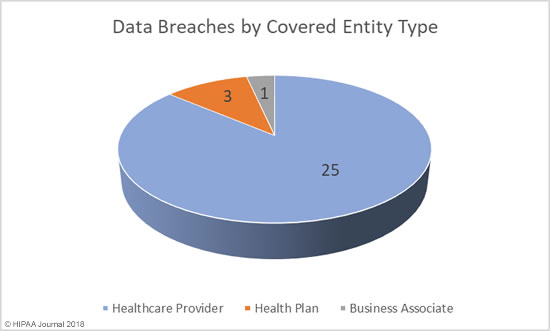
March 2018 Healthcare Data Breaches by Covered Entity Type

No data breaches were reported by business associates of HIPAA-covered entities in March. The breach summaries published by the HHS’ Office for Civil Rights suggest there was no business associate involvement in any of the 29 incidents reported.

However, the largest reported incident – the breach at Middletown Medical – is marked as having no business associate involvement, when the breach notice uploaded to the provider’s website indicates the incident was caused by a subcontractor of a business associate. It is possible there were more security breaches in March that had some business associate involvement.

March 2018 Healthcare Data Breaches by Covered Entity Type

Records Exposed by Covered Entity Type

Unsurprisingly, given the number of incidents reported by healthcare providers, these incidents resulted in the highest number of exposed records – 154,325 records – followed by breaches at business associates/subcontractors – 63,551 records – and health plans – 50,334 records.

Breaches at business associates/subcontractors saw the highest number of records exposed per incident (Median & Mean = 63,551 records), followed by health plans (Median=13,943 records / Mean = 16,778 records), and healthcare providers (Median = 1,843 records / Mean = 6,173 records).

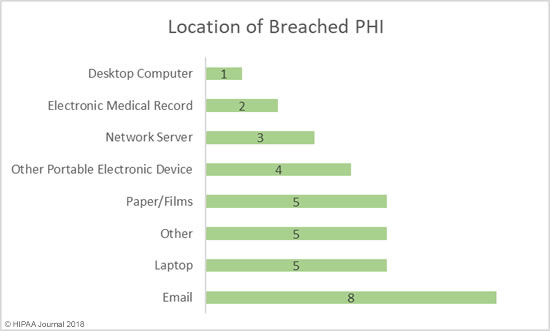
Location of Breached Protected Health Information

The main location of breached protected health information in March was portable electronic devices (laptops /other portable devices) with 9 incidents reported. Had encryption been used to protect ePHI on these devices, a breach of PHI could have easily been avoided.

The second biggest problem area was email with 8 reported incidents. These breaches include misdirected emails and phishing incidents.

Securing physical records continues to be a problem. There were five incidents reported in March that involved physical records such as paper and films.

Location of Breached Protected Health Information

March 2018 Healthcare Data Breaches by State

In March 2018, six states experienced multiple healthcare data breaches. While California usually tops the list for the most number of breaches, this month it was Massachusetts-based healthcare organizations that were the hardest hit, with 5 incidents reported.

California was in second place with four security incidents, followed by Missouri and New York with three, and Maryland and Texas with two. The 10 other states where breaches occurred were Arkansas, Colorado, District of Columbia, Florida, Georgia, Iowa, Illinois, Minnesota, Mississippi, and West Virginia.

Financial Penalties for Breaches and HIPAA Violations

There were no civil monetary penalties issued by the Department of Health and Human Services’ Office for Civil Rights in March, and no settlements with HIPAA-covered entities or business associates to resolve HIPAA violations.

The New York attorney general’s office has continued to take a hard line on companies discovered to have violated HIPAA Rules and suffered data breaches as a result with one further settlement reached in March.

Virtua Medical Group agreed to settle violations of HIPAA and state laws for $417,816. That penalty relates to the failure to secure an FTP server, although it was not the healthcare provider that was directly responsible. The error was made by a business associate of Virtua Medical Group.

The post Analysis of March 2018 Healthcare Data Breaches appeared first on HIPAA Journal.

HHS Report Offers Tips to Prevent and Block SamSam Ransomware Attacks

The high volume of SamSam ransomware attacks on healthcare and government organizations in recent months has prompted the Department of Health and Human Services’ Healthcare Cybersecurity and Communications Integration Center (HCCIC) to issue a report of ongoing SamSam ransomware campaigns. The report includes tips to help organizations detect and block SamSam ransomware attacks.

There Have Been 10 Major SamSam Ransomware Attacks in the Past 4 Months

Since December 2017, there have been 10 major attacks, mostly on government and healthcare organizations in the United States. Additional attacks have been reported in Canada and India.

In January 2018, the EHR provider AllScripts experienced an attack that saw its systems taken out of action for several days, preventing around 1,500 medical practices from accessing patient data. In some cases, those practices were prevented from accessing patient data for as long as a week.

In March 2018, the City of Atlanta was forced to shut down its IT systems to halt the spread of the ransomware. In that case, the attack leveraged a Windows Server Message Block V1 vulnerability on a public-facing server to install the ransomware – the same vulnerability that was exploited in the global WannaCry and NotPetya in May and June 2017.

Hancock Health was attacked and chose to pay the ransom as it was seen to be preferable to the ongoing disruption that would have been caused by recovering files from backups. Hancock Health was one of two hospitals in Indiana to experience an attack. The Colorado Department of Transportation suffered two separate SamSam ransomware attacks in February and March.

Other healthcare organizations to be attacked include Erie County Medical Center which saw an unpatched vulnerability exploited. In that case, the ransom was not paid, although it took six weeks for the medical center to fully recover at a cost of several million dollars.

While the healthcare industry appears to have been targeted, that is not necessarily the case. The HHS and Cisco Talos suggest several of the attacks have been opportunistic in nature. However, ransomware gangs have been known to target the government, healthcare, and education sectors. The major disruption to services and the cost of mitigating attacks in these industries makes it far more likely that the ransom payment will be made.

Different attack methods have been used by the threat actors behind SamSam ransomware, although the group is known to exploit vulnerabilities on public-facing servers. Compromised RDP/VNC servers (Remote Desktop Protocol/Virtual Network Computing) are a common denominator in several of the attacks.

The threat actors also scan for open RDP connections and conduct brute force attacks which take advantage of weak passwords.

Once access to a server is gained, ransomware is installed and spread laterally. The goal of the attack is to cause massive disruption. Even though backups exist in most cases and data can be recovered, the continued disruption to business operations while files are recovered makes payment of the ransom preferable. Even if the ransom is paid the cost is considerable. The City of Atlanta was reportedly issued a ransom demand of $6,800 per infected endpoint.

Tips to Prevent and Block SamSam Ransomware Attacks

Several vulnerabilities have been exploited to gain access to servers including JBoss, SMBv1, RDP, and others. It is therefore strongly recommended to conduct regular vulnerability scans and ensure good patch management practices are adopted. Strong passwords should be used, and controls implemented to enforce password policies.

HCCIC offers the following advice to prevent and block SamSam ransomware attacks:

  • Conduct an organization-wide risk analysis to identify risks to ePHI and implement security measures to remediate those risks – A requirement of the HIPAA Security Rule
  • Train end users to help them detect malicious software
  • Implement procedures to protect against malicious software and use software solutions that can rapidly identify an attack in progress to ensure rapid action can be taken to prevent the spread of the infection
  • Ensure all data is backed up regularly – A good backup strategy is the 3-2-1 approach – Ensure 3 backups are made, on two different media, with one copy stored securely off site.
  • Develop contingency plans to minimize business disruption in the event of a cyberattack
  • Develop procedures for responding to security incidents, including procedures specifically for ransomware attacks.

As for payment of the ransom, that carries a risk. There are no guarantees that the attackers will make good on their promise to send keys to unlock the data or that the keys supplied will work. It is essential to ensure that recovery is possible without paying the ransom.

The HCCIC report, which includes indicators of compromise, can be downloaded from the American Hospital Association on this link (PDF).

The post HHS Report Offers Tips to Prevent and Block SamSam Ransomware Attacks appeared first on HIPAA Journal.

How Long Does It Take to Breach a Healthcare Network?

A recent survey of hackers, incident responders, and penetration testers has revealed the majority can gain access to a targeted system within 15 hours, but more than half of hackers (54%) take less than five hours to gain access to a system, identify sensitive data, and exfiltrate the data.

61% of Surveyed Hackers Took Less than 15 Hours to Obtain Healthcare Data

The data comes from the second annual Nuix Black Report and its survey of 112 hackers and penetration testers, 79% of which were based in the United States.

Respondents were asked about the time it takes to conduct attacks and steal data, the motivations for attacks, the techniques used, and the industries that offered the least resistance.

While the least protected industries were hospitality, retail, and the food and beverage industry, healthcare organizations were viewed as particularly soft targets. Healthcare, along with law firms, manufacturers, and sports and entertainment companies had below average results and were relatively easy to attack. As Nuix points out, many of the industries that were rated as soft targets are required to comply with industry standards for cybersecurity.

The retail and food and beverage industries are required to comply with Payment Card Industry Data Security Standard (PCI DSS) and healthcare organizations must comply with HITECH Act requirements and the HIPAA Security Rule, with the latter requiring safeguards to be implemented to ensure the confidentiality, integrity, and availability of healthcare data. As far as hackers are concerned, the data is certainly available. When asked how long it takes to breach the perimeter of a hospital or healthcare provider and exfiltrate useful data, 18% said less than 5 hours, 23% said 5-10 hours, and 20% said 10 to 15 hours. ‘Large numbers’ of hackers said they were able to identify and exfiltrate sensitive data within an hour of breaching the network perimeter.

Even though organizations are required to comply with certain standards for cybersecurity, that does not mean that appropriate safeguards are implemented, or that they are implemented correctly and are providing the required level of protection.

“Most organizations invest heavily in perimeter defenses such as firewalls and antivirus, and these are mandatory in many compliance regimes, but most of the hackers we surveyed found these countermeasures trivially easy to bypass,” said Chris Pogue, Head of Services, Security and Partner Integration at Nuix and lead author of the report.

How Are Hackers Gaining Access to Networks and Data?

The most popular types of attacks are social engineering (27%) and phishing attacks (22%), preferred by 49% of hackers. 28% preferred network attacks.  The popularity of ransomware has soared in recent years, yet it was not a preferred attack method, favored by only 3% of respondents to the survey.

Social engineering is used sometimes or always by 50% of attackers, with phishing emails by far the most popular social engineering method. 62% of hackers who use social engineering use phishing emails, physical social engineering on employees is used by 22%, and 16% obtain the information they need over the telephone.

The most commonly used tools for attacks were open source hacking tools and exploit packs, which combined are used by 80% of surveyed hackers.

Interestingly, while the threat landscape is constantly changing, hackers do not appear to change their tactics that often. Almost a quarter of hackers only change their attack methods once a year and 20% said they update their methods twice a year.

As for the motivation for the attacks, it is not always financial. 86% hack for the challenge, 35% for entertainment/mischief, and only 21% attack organizations for financial gain.

One take home message from the survey is just how important it is to implement security awareness programs and train staff cybersecurity best practices and to be alert to the threat from social engineering and phishing attacks. With almost half of hackers preferring these tactics, ensuring the workforce can identify phishing and social engineering attacks will greatly improve organizations’ security posture.

The post How Long Does It Take to Breach a Healthcare Network? appeared first on HIPAA Journal.