Healthcare Cybersecurity

AI Agent Conducts First Fully Autonomous Ransomware Attack

Researchers have identified what they believe to be the first agentic ransomware attack. An autonomous large language model (LLM) agent conducted an entire attack without human involvement, including vulnerability exploitation, credential theft, lateral movement and file encryption.

The attack was identified by researchers at the cloud security company Sysdig, who linked the attack to the JadePuffer ransomware operation. JadePuffer used a fully autonomous AI agent to conduct reconnaissance on the targeted company, exploit a vulnerability (CVE-2025-3248), steal credentials, move laterally within the victim’s network, establish persistence, escalate privileges, encrypt data, and drop a ransom note, adapting to failures on the fly without human intervention.

The vulnerability exploited for initial access was an unauthenticated remote code execution vulnerability in the Langflow open source framework. The researchers explained that this is an attractive entry point as Langflow servers are AI-adjacent, often hold provider API keys and cloud credentials, and are commonly stood up quickly without network controls. While a patch had been issued to fix the vulnerability on April 1, 2025, and the flaw was known to be actively exploited, the vulnerability had not been patched.

The AI agent was able to adjust its approach in a similar way to a human attacker. For instance, when an API request returned XML instead of JSON, the next payload adjusted its parsing logic accordingly, and when certain steps failed, the AI agent retried those steps using refined parameters. “In one sequence, it went from a failed login to a working fix in 31 seconds,” explained the researchers.

The AI agent gained access to a production MySQL server running Alibaba Nacos by exploiting a 2021 authentication bypass vulnerability, then encrypted all 1,342 Nacos service configuration items and deleted the originals. The AES encryption key was not transmitted to the attacker’s infrastructure, so even if the ransom was paid, recovery would not have been possible.

According to a recent statement from the Five Eyes cybersecurity agencies,  advances in artificial intelligence have accelerated the speed, scale, and sophistication of cyber threats. The agencies warned that “frontier AI models are anticipated to exceed current industry expectations, fundamentally transforming both offensive and defensive cyber capabilities. The timeline is not years; it is months.” The Sysdig researchers say the age of agentic threat actors has arrived.

While the attack was fully automated, it did not involve the exploitation of any zero-day vulnerabilities or novel techniques, therefore defending against automated attacks is no different to defending against hands-on- keyboard attacks. As recommended by the Five Eyes agencies, organizations should take steps now to combat threats by reducing their attack surface, accelerating patching processes, addressing legacy systems, reviewing and strengthening identity and access controls, and ensuring they develop and test incident response plans, which should be focused on fast containment and recovery.

The post AI Agent Conducts First Fully Autonomous Ransomware Attack appeared first on The HIPAA Journal.

ANCHOR-CI Framework Strengthens Partnerships and Information Sharing to Secure Critical Infrastructure

The Department of Homeland Security (DHS) Cybersecurity and Infrastructure Security Agency (CISA) has announced the formation of the Alliance of National Councils for Homeland Operational Resilience–Critical Infrastructure, or ANCHOR-CI for short. ANCHOR-CI will operate for two years initially but may be extended by DHS Secretary under the authority provided by Section 871 of the Homeland Security Act.

ANCHOR-CI is the successor to the Critical Infrastructure Partnership Advisory Council (CIPAC), which enabled critical infrastructure entities to exchange sensitive information with the federal government about physical and cyber risks. CIPAC was established by the DHS in March 2006 and served as the framework for public collaboration on security for almost two decades, until it was eliminated by then DHS Secretary Kristi Noem in March 2025. There has been no formal framework for government-industry coordination on critical infrastructure cybersecurity for more than a year, and without the legal protections provided by CIPAC or an equivalent framework, some critical infrastructure sectors stopped sharing cybersecurity data with the federal government.

ANCHOR-CI retains the legal protections of CIPAC and creates a new framework to strengthen information sharing and broaden partnerships across government and industry to better secure the nation’s critical infrastructure. “The new and innovative ANCHOR-CI framework will be a game changer in how the public and private sectors collaborate and share information,” said DHS Secretary Markwayne Mullin. “In a rapidly evolving threat environment, ANCHOR-CI will ensure we have the right people in the room working together to keep the critical infrastructure Americans rely on secure and resilient. This is just another example of the partnership needed to confront the threats of today and tomorrow.”

ANCHOR-CI allows the establishment of four council types: critical infrastructure sector councils, cross-sector councils, critical infrastructure industry councils, and regional coordinating councils, which will advise and provide strategic and actionable recommendations to ensure a coordinated national effort to strengthen critical infrastructure cybersecurity. The councils will recruit members from four groups: critical infrastructure owners, operators and their trade associations; federal, state, local, tribal and territorial government agencies; organizations with direct responsibility for cybersecurity and infrastructure resilience; and other private sector entities.

The new framework is more flexible than its predecessor, supports open and candid discussions of sensitive information, strengthens collaboration between the government and industry, and will ensure more critical infrastructure stakeholders participate. One key feature of CIPAC that has been dropped in ANCHOR-CI is liability protection for participants. This was an important feature that allowed executives to discuss incidents in group settings without antitrust or regulatory exposure.

Under the new framework, CISA will approve proposed council members and may appoint additional participants. Under CIPAC, private sector councils chose their own representatives. While some meetings can be opened to the public, sensitive discussions are shielded, as ANCHOR-CI is exempted from the Federal Advisory Committee Act.

Governance of the ANCHOR-CI councils will be managed by the DHS and CISA, and it will be housed by CISA, which will provide the necessary funding and administrative support. The HHS Office of Cybersecurity and Infrastructure Protection (CIP) will work closely with DHS and CISA to advance collaboration and ensure that the Healthcare and Public Health (HPH) sector priorities are elevated.  The ANCHOR-CI councils will help strengthen partnerships within the HPH sector, as well as across interdependent critical infrastructure sectors, including water and communications.

The post ANCHOR-CI Framework Strengthens Partnerships and Information Sharing to Secure Critical Infrastructure appeared first on The HIPAA Journal.

ClickFix Social Engineering Technique is the Leading Method for Malware Delivery

The ClickFix social engineering technique is the leading method of malware delivery, according to an analysis by researchers at ReliaQuest. The researchers analyzed cyberattacks between March 1 and March 31, 2026, and found that attackers were most commonly exploiting trusted identities, devices, and tools in their attacks. This approach allows the attackers to hide their activities, which resemble normal user behavior, and bypass traditional perimeter and file scanning defenses.

The leading technique was ClickFix, which involves tricking users into pasting the attacker’s commands and scripts into trusted system dialogs, such as the Windows Run dialog. Pressing the Windows Key + R, launches the Run dialog, and the user is convinced to copy the supplied code into the dialog and execute it, having been tricked into thinking that the command will resolve an IT issue.

For instance, a user visits a website that triggers a pop-up, warning them that their browser contains a vulnerability or an image failed to load. They are told to click a button, which copies code, and then paste that command into the Run dialog and press Enter, thus executing the command. Other methods involve generating a fake CAPTCHA page, informing the user that they need to complete the test to verify they are human by pasting and running the command. That command launches PowerShell code that delivers the malware payload.

ReliaQuest researchers report that this technique is commonly used to deliver the NetSupport RAT, a remote access Trojan, and Deepload fileless malware, although they observed this technique being used to deliver a range of malware variants. This approach has also been used against MacOS users for the first time, delivering Atomic Stealer (AMOS), which can steal browser credentials, session cookies, cryptocurrency wallets, and keychain data.

ReliaQuest recommends companies add this method of attack to their security awareness training programs, warning employees not to paste commands into dialog boxes, such as Run, Terminal, or Script Editor, to consider restricting the use of the Run feature, restrict users from executing executable files, and use web filters to block pop-ups and prevent access to malicious websites.

The post ClickFix Social Engineering Technique is the Leading Method for Malware Delivery appeared first on The HIPAA Journal.

Verizon Releases Inaugural Breach Impact Study

Verizon Business has released the findings from its inaugural Breach Impact Study, which focuses on the financial impact of data breaches. The BIS report is from the same authoring team as the Verizon Data Breach Investigations Report and was produced in partnership with CyberAcuView. The report is based on an analysis of around 70,000 U.S. cyber insurance claims, including 38,000 claims where the policies paid out. The data spans from January 2019 to October 2025.

In contrast to many data breach cost reports, the report is based on median claim amounts rather than averages, which are susceptible to skewing. In 2019, the median financial impact was around $60,000, rising by 80% to $110,000 in 2025, with data breach costs outpacing inflation, which was around 23% over the period of the study. More than half of paid-out claims exceeded $83,000, with 10% having an impact of $920,000 or more. The most extreme 2.5% of cases exceeded $5 million in losses.

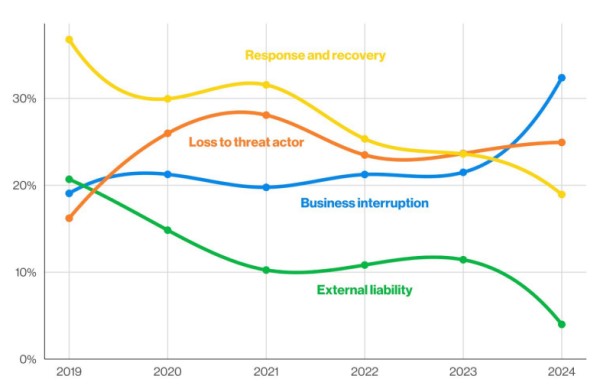
The report shows that data breach costs almost doubled between 2019 and 2025, with business interruption the single largest loss driver, followed by loss to threat actor and response and recovery.

Known breach losses over time: 2019 to 2025

Known losses over time. Source: Verizon 2026 Breach Impact Study.

For software supply chain and third-party incidents, business interruption accounted for 50% of all losses. Software supply chain incidents and third-party breaches are relatively rare, accounting for around 2% of claims in the dataset, but when they occur, they can be catastrophic, with costs more than double the overall dataset. In the most extreme cases, losses exceeded $100 million.

The median impact was around $38,000 in the SMB segment, rising to $96,000 in the mid-market segment, and $238,000 for large enterprises, with the top 2.5% of large enterprise claims exceeding $22 million per claim. While breach costs were relatively low in the SMB segment, the ratio of impact amounts to insured revenue was as high as 3% in the top 10% of cases, and was 7% in the most extreme cases. Without an insurance policy, these incidents could have been extremely damaging. In the mid-market and large enterprise segments, the ratio did not go above 2% in the top 2.5% of extreme cases.

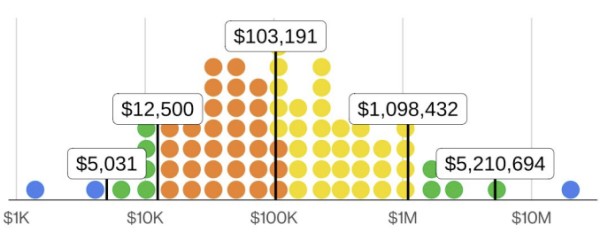
Healthcare had relatively high external liability costs compared to other sectors. The dataset included more than 8,640 claims with 5,100 recorded losses. Healthcare accounted for 23% of total losses, with a median liability loss 57% higher than the overall dataset.  Response and recovery accounted for 29% of total losses, followed by business interruption (24%) and external liability (23%).

Distribution of healthcare breach claim costs 2019-2026

Distribution of the economic impact of breaches in healthcare. Source: Verizon 2026 Breach Impact Study

The most common incident type in healthcare that prompted a claim was a ransomware attack (39%), which represented 60% of the total cost with a median cost of $77,051. Business email compromise (BEC) was involved in 22% of cases, accounting for 10% of the costs, with a median cost of $94,924.

The post Verizon Releases Inaugural Breach Impact Study appeared first on The HIPAA Journal.

Security Researcher Identifies Quintet of Bugs in Toolkit Used in DICOM Medical Imaging Software

A quintet of vulnerabilities has been identified in a DICOM toolkit – OFFIS DCMTK – that is extensively used in medical imaging software. DICOM (Digital Imaging and Communications in Medicine) is the universal technical standard used to store, transmit, print, and display medical imaging data and is used by virtually all medical imaging devices. Since the toolkit is used in many medical imaging software solutions, the vulnerabilities are significant.

Successful exploitation of the vulnerabilities could expose patient information, disrupt DICOM storage or worklist services, exhaust service memory, crash imaging services, or cause DCMTK-based clients to write files outside the intended output directory. The vulnerabilities were identified by independent security researcher Abhinav Agarwal, who reported them to the U.S. Cybersecurity and Infrastructure Agency (CISA) and the vendor in May 2026. Agarwal identified the vulnerabilities using standard subscriptions to Claude and ChatGPT, then manually reviewed and confirmed the findings.

One of the vulnerabilities is rated critical with a CVSS v 3.1 base score of 9.8 (critical), and the other four vulnerabilities are rated high severity, with CVSS base scores ranging from 7.5 to 8.2 (v4.0: 8.7 to 8.8). CISA published a security advisory about the vulnerabilities on June 30, 2026.

The vulnerabilities affect OFFIS DCMTK versions prior to v3.7.0 and are tracked under the following CVEs:

CVE Severity CVSS v3.1 CVSS v4.0 Vulnerability
CVE-2026-50003 Critical 9.8 9.3 Improper limitation of a pathname to a restricted directory (path traversal)
CVE-2026-52868 High 8.2 8.8 Improper limitation of a pathname to a restricted directory (path traversal)
CVE-2026-50254 High 7.5 8.7 Missing release of memory after effective lifetime
CVE-2026-35505 High 7.5 8.7 Missing release of memory after effective lifetime


CVE-2026-44628 High 7.5 8.7 Access of resource using incompatible type (Type confusion)

According to CISA, the maintainer of the toolkit was informed about the vulnerabilities and has issued a fix; however, Agarwal contacted The HIPAA Journal to warn that the vendor has applied the fix upstream in the master branch, which means downstream libraries and operators will be unable to release with the fix to upgrade to it. Users will need a fixed release or a vendor-provided update path.

One of the problems with vulnerabilities in DICOM toolkits is that many end users may be using DICOM software with known, disclosed vulnerabilities and be unaware that their software is vulnerable, unless they are provided with a Software Bill of Materials (SBoM) and routinely check for vulnerabilities in all components. Agarwal suggested that healthcare entities should ask their imaging vendors whether DCMTK is present, what versions are used, whether the CISA advisories apply, and when patched builds will ship.

The post Security Researcher Identifies Quintet of Bugs in Toolkit Used in DICOM Medical Imaging Software appeared first on The HIPAA Journal.

Remote Desktop Tools are the Front Door in Healthcare, and Hackers are Walking Through

There is some positive news from the data collected by cybersecurity firm SonicWall, as cyberattacks have declined by up to 57% in some sectors; however, the healthcare industry has seen the smallest decline out of all tracked verticals, registering just a 17% year-over-year decline, compared to -23% for professional services, -42% for education, -46% for retail and -57% for manufacturing. Healthcare is still persistently targeted by cyber actors, and the gap between healthcare and other sectors is growing, according to the SonicWall 2026 Healthcare Protect Brief.

There are more active ransomware groups (10) attacking healthcare organizations than any other sector, indicating the industry is being actively targeted rather than falling victim to spray-and-pray attacks, and in H1 2026, there were four times as many malware hits per firewall in healthcare as the next most attacked sector. UltraVNC buffer overflow attacks generated 13.3 million hits in just 5 months, as hackers primarily targeted remote desktop tools to attack healthcare organizations – no other vertical experienced remote desktop exploitation at that scale.

Healthcare organizations rely on remote desktop tools to support their distributed clinical environments, telemedicine platforms, and third-party vendor access. If remote access credentials are compromised, it gives threat actors a path to clinical systems and patient data, which can be exfiltrated and held to ransom. While network-level controls can limit data access, and multifactor authentication (MFA) can prevent compromised credentials from providing access, MFA is often not implemented, and a single set of credentials does not just unlock one application; they often grant access to the full network.

SonicWall also identified 243 unique attack methods targeting connected medical devices, with the Internet of Things (IoT) the fastest-growing and hardest-to-patch exposure. Healthcare organizations have a huge range of deployed connected devices, including infusion pumps, patient monitors, imaging systems and more, which means a huge attack surface to defend. Unfortunately, the attack surface is growing faster than security teams can govern it. IoT devices are often not routinely patched, cannot run endpoint agents, and often share network segments with clinical systems that contain protected health information.

“Healthcare does not have a cybersecurity problem. It has three of them,” explained Michael Crean, SonicWall SVP of Managed Services. Remote desktop tools without layered controls and MFA; a huge IoT footprint containing vulnerable devices; and targeted ransomware attacks. “Attackers have figured out how to use all of them at the same time.”

Hackers continue to target the sector as the returns are too reliable and the defenses too predictable. “What our research makes clear is that attackers have done the math. Hospitals cannot go dark, downtime is measured in patient outcomes, and the pressure to pay is unlike anything in any other sector. None of that changes until healthcare stops relying on security architectures built for a world that no longer exists, and starts treating Zero Trust not as a future initiative, but as the baseline they needed yesterday.”

The immediate steps recommended by SonicWall are to restrict UltraVNC and RDP to internal VLANS and ensure that MFA is implemented for all remote access, with no exceptions for vendors and no break-glass credentials. Connected medical IoT devices must be placed on isolated networks, away from clinical systems. Healthcare organizations need to implement application-level Zero Trust and ensure that legacy vulnerability exposure is addressed. SonicWall recommends conducting a comprehensive inventory of clinical middleware and IoT firmware and then ensuring that vulnerabilities are patched or devices isolated on a defined schedule.

The post Remote Desktop Tools are the Front Door in Healthcare, and Hackers are Walking Through appeared first on The HIPAA Journal.

High-Severity Vulnerability Identified in OHIF Viewers DICOM

A high-severity vulnerability has been identified in OHIF (Open Health Imaging Foundation) Viewers DICOM, which could be exploited to steal an authenticated clinician’s token via a crafted link.

The Server-Side Request Forgery (SSRF) vulnerability is tracked as CVE-2026-12473 and has a CVSS base score of 8.2 (v3.1) and 8.3 (v4.0). The vulnerability is due to two data sources – DICOMWebProxy and DICOMJSON –  shipped in the default configuration fetching an arbitrary URL parameter without validation.

A global authentication service in OHIF injects the authenticated user’s OIDC Bearer token into the resulting requests, which could be sent to an attacker-controlled server, allowing the OIDC Bearer token to be obtained. The vulnerability does not impact DICOMweb data sources.

The vulnerability affects OHIF DICOM Web Viewer Framework prior to v3.12.0. The vulnerability has been fixed by the maintainer in version 3.12.2, which was released on May 18, 2026. The fix is located at OHIF/Viewers#5985 (master), OHIF/Viewers#5978 (release/3.12).

Users are advised to update to the fixed version as soon as possible. There are additional requirements for users running OHIF with authentication and those that need dicomwebproxy or dicomjson in authenticated deployments, as detailed in the CISA security advisory.

The post High-Severity Vulnerability Identified in OHIF Viewers DICOM appeared first on The HIPAA Journal.

Healthcare Report Highlights Growing Vendor Risk and Lack of Cyberattack Readiness

Cybersecurity risk is growing, and healthcare organizations are struggling to defend a rapidly increasing attack surface. AI tools are being implemented without the secure infrastructure to support them. Most healthcare practices have meaningful gaps in cyberattack recovery readiness, face ongoing and regular third-party vendor disruptions, and there is growing concern that a cyberattack will result in a patient fatality. The current state of cybersecurity in healthcare is far from rosy.

These were some of the findings from the 2026 Healthcare IT Landscape Report from Omega Systems, a leading provider of managed IT and security services to the healthcare and financial services industries. The report is based on a survey of 200 healthcare business leaders in the United States, including CEOs, CISOs, CIOs, CFOs, and COOs, at healthcare organizations with between 50 and 600 employees. The healthcare organizations represented in the report include medical practices, clinics, ambulatory care centers, specialty services, and long-term care facilities.

In 2025, when the study was last conducted, 52% of healthcare organizations said it is inevitable that a cyberattack on a healthcare facility will result in a patient fatality in the next five years. There has been a relative 17% increase in just 12 months, with 61% now expressing that concern. The increase is unsurprising given the lack of cyberattack recovery readiness. In the event of a cyberattack that prevents access to the electronic medical record (EMR) system, 47% said loss of access to patient records would create an immediate patient safety issue and malpractice liabilities, 53% say billing, claims, and scheduling would instantly stop, freezing cash flow at the moment when clinical operations are most compromised, and 25% said they would be unable to maintain baseline care standards, resulting in temporary or even permanent closure.

Omega Systems said 82% of providers acknowledged meaningful gaps in their recovery readiness. Almost one-third (31%) of respondents lack the ability to contain and resolve data breaches quickly; almost one-quarter (24%) do not regularly train teams on incident response; one-fifth (21%) have no independent EMR recovery path or access to a 24/7 SOC team, and 13% have no documented recovery plan at all. AI adoption is almost universal, with 93% of healthcare practices already having adopted AI tools, yet they lack the secure infrastructure to support it safely.

The risk of cyberattacks has never been greater. According to OCR data, 2025 saw more large data breaches reported than any year since records of data breaches have been published, fueled in part by an increase in cyberattacks on vendors, which usually impact multiple healthcare clients and cause considerable disruption.

Omega Systems found that 85% of healthcare practices experienced at least one operational disruption in the past 12 months due to a third-party vendor or vendor of a vendor, and 24% experienced a third-party or vendor breach that directly affected their data or operations.

While vendor incidents are increasing, a concerningly high percentage of respondents – 70% – said they were confident or very confident in their vendors’ cybersecurity posture. Vendors have been engaged and are trusted, and are no longer being questioned about their cybersecurity posture.

OCR is due to issue a final rule implementing proposed changes to the HIPAA Security Rule, one of the requirements of which is annual reverification of cybersecurity measures of their business associates, which will force practices to continually verify vendor cybersecurity. According to Omega Systems reports, currently, 63% of practices are not continuously monitoring their networks and digital supply chains, while 70% say they are confident in the vendors connected to them. “A practice can’t be confident in what they aren’t watching,” warns Omega Systems. “Trust is a natural byproduct of long-term vendor relationships. And that’s precisely what attackers count on. They target vendors because their healthcare clients trust them – and rarely verify the controls behind that trust.”

Omega Systems identified a single root cause of the cybersecurity problem in healthcare – Cybersecurity is a patient safety issue, yet healthcare organizations are still treating cybersecurity as a technical expense. “Sixty-two percent (62%) of healthcare leaders still treat cybersecurity as a technical expense rather than a clinical or fiduciary risk,” explained Omega Systems in the report. “That posture determines what gets funded, what gets deferred, and what gets ignored. It is why the gaps documented in this report persist despite years of escalating threat data.”

OCR investigates all reported data breaches affecting 500 or more individuals, and data breaches are being reported in record numbers. OCR currently has an initiative targeting noncompliance with the risk analysis provision of the HIPAA Security Rule, which has been expanded to also cover risk management. The survey revealed that six in ten leaders have self-attested to HIPAA-compliance, when they know that their risk analyses identified unresolved vulnerabilities. According to the report, 23% of practices have already filed a breach report with OCR.

“For many, that filing was not the result of negligence. It was the result of a gap that grew faster than their resources could close it,” explained Omega Systems. “Small practice leaders are not ignoring compliance. They are managing it with teams that are stretched thin, budgets that do not go far enough, and requirements that keep changing. The breach notification is often the moment they find out how serious that gap had become.”

When the HIPAA Security Rule update is released, practices will have a lot of ground to cover in a short space of time. Only 24% of practices report that they are fully prepared for the proposed changes; many lack the required in-house staff and have cybersecurity and compliance programs that have been built for a simpler threat landscape.

More than one-third (35%) say their cybersecurity/IT team is understaffed, one-third (33%) underestimate the severity and frequency of cyberattacks, one-quarter (26%) say their cybersecurity/IT team is underfunded and has antiquated cybersecurity technology (23%), and one-fifth (21%) deliberately downplays cyberattack risk to avoid reputational damage.

With the HIPAA Security Rule final rule expected this year (the proposed release date was May 2026), healthcare cybersecurity and compliance programs will have to be overhauled. Omega Systems explains that the leaders will not be the healthcare organizations with the most advanced technology. They will be the ones who have made a governance-level commitment to treating security, compliance, vendor risk, and AI not as separate problems requiring separate solutions, but as one, with a partner accountable for the whole picture.

The post Healthcare Report Highlights Growing Vendor Risk and Lack of Cyberattack Readiness appeared first on The HIPAA Journal.
VA OIG Identifies Lack of Oversight of VA GenAI Chat Tools

A review of the use of generative artificial intelligence (GenAI) tools by Department of Veterans Affairs (VA) staff has identified potential patient safety risks from a lack of safeguards and oversight. The review was conducted by the VA Office of Inspector General (OIG) between October 2025 and January 2026 and found that more than 15,000 VA staff members were using general-purpose GenAI chat tools authorized for use by the Veterans Health Administration (VHA) – VA GPT and Microsoft 365 Copilot Chat.

The reviewers identified broad staff engagement with the AI chat tools. An analysis of an internal prompt‑sharing application identified 135 prompts for the GenAI chat tools, 79 of which were clinical. The drafting of clinical notes and summarization of patient care were among the most common uses of the tools. The VA OIG notes that the tools were not specifically developed for clinical use, and while the VA provides clinical users with general training and resources, the VA does not centrally curate or evaluate prompts or the generative output, which may be applied to clinical decision making. The VA OIG notes that studies of genAI usage in medical settings found that prompt techniques can play a critical role in output errors that could impact diagnoses and care management if not corrected.

The Office of Management and Budget’s 2025 memorandum (Accelerating Federal Use of AI through Innovation, Governance, and Public Trust) requires all agencies to identify high-impact AI use and implement safeguards to manage risk. The VA did not identify the use of VA GPT and Copilot Chat as high-impact, and therefore, the required risk management actions did not apply.

The VHA had determined that Ambient AI Scribe was high-impact, which triggered safety requirements such as pre-deployment testing of the AI tool and providing human oversight before use. Ambient AI Scribe is a targeted clinical documentation tool that listens to clinical visits and drafts medical record notes. The VA-OIG said the tool had functionality similar to the clinical documentation prompts VA staff were using with VA GPT and Copilot Chat, which were not considered high-impact.

The VA OIG made three recommendations to the VHA regarding the use and assessment of GenAI chat tools: Evaluating these tools as high-impact, implementing the required safeguards, and integrating monitoring of AI-related risks into existing patient safety programs. The VHA concurred in principle with the recommendation to evaluate the tools as high -impact and concurred with the other two recommendations. The VHA has provided the VA OIG with an action plan, will develop guidance on the use of the GenAI chat tools, and is working on addressing the recommendations by April 2027.

As the use of GenAI tools in healthcare accelerates, concern is growing that sensitive patient data may be shared with publicly accessible chatbots, and that AI tools could generate output that puts patients at risk of harm or even death. Earlier this year, Health-ISAC and the Health Sector Coordinating Council Cybersecurity Working Group issued guidance on developing effective AI governance frameworks – Health-ISAC’s White Paper: Policies and Safeguards for a Safe Use of AI and the HSCC Health Industry AI Cyber Governance Framework Implementation Guide to help healthcare organizations create an effective AI governance and safeguards framework and responsibly use GenAI and LLMs while minimizing risk.

The post VA OIG Identifies Lack of Oversight of VA GenAI Chat Tools appeared first on The HIPAA Journal.