HIPAA Breach News

Healthcare Providers Discover Unauthorized PHI Disclosures to AI Tools

Two data privacy incidents have recently been announced that involved patient data uploaded to artificial intelligence (AI) tools without authorization.

Weill Cornell Medicine, New York

Weill Cornell Medicine, Cornell University’s school of medicine and biomedical research institution in New York City, has alerted certain patients about a privacy incident involving patient information being used in an unauthorized capacity related to a radiology research study. On September 6, 2026, Weill Cornell Medicine discovered that certain patients’ protected health information used in connection with the study had been entered into AI and machine learning tools without authorization and in violation of its policies.

The data was uploaded to the tools between June 10 and June 20, 2026, and included the information of patients who received medical imaging services at NewYork-Presbyterian (WCINYP) or NewYork-Presbyterian Hospital. The data uploaded to the tools did not include patient names, contact information, Social Security numbers, or financial information. The uploaded information was limited to medical record numbers, radiology accession numbers assigned to radiology images, dates and times of radiology services, facility names, healthcare provider names, and clinical information relating to radiological examinations, which may have included diagnoses, treatment information, surgical and procedural histories, and medication information.

Weill Cornell Medicine said it has not identified any misuse of patient data as a result of the incident, has suspended the research activity, and submitted a request to have the data deleted. Additional education has been provided to appropriate individuals regarding appropriate use of AI tools and the importance of protecting patient information. The number of affected individuals has not yet been publicly disclosed.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please enable JavaScript in your browser to complete this form.

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { margin-bottom: 18px; } .inpage_banner_12838 a { max-width: 80%; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } } .hj_co_m_12838 { margin-bottom: 30px; } .hj_co_m_12838 .sbwf-main-form-container { max-width: 340px; margin: 0 auto; box-shadow: 0 4px 6px rgba(0,0,0,0.05),0 6px 6px rgba(0,0,0,0.05); padding: 30px; box-sizing: border-box; border: 1px solid #f4f4f4; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 200px; margin: 0 auto; display: block; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { text-align: center; border-top: 1px dashed #c8c8c8; padding: 20px 0 0; margin: 30px 0 20px; color: #753043; font-weight: 600; line-height: 30px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { text-align: center; font-size: 16px; color: #3B3B3B; line-height: 24px; font-weight: 600; margin: 0; padding: 0; } #sidebar .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 span { font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container p.terms, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms { text-align: center; font-size: 11px; padding-bottom: 0; line-height: 19px; margin: 10px 0 10px; } .hj_co_m_12838 .sbwf-main-form-container p.terms a { color: #753044; text-decoration: none; } .hj_co_m_12838 .sbwf-main-form-container p.terms a:hover { text-decoration: underline; } .hj_co_m_12838 .sbwf-main-form-container p.terms_title, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms_title { text-align: center; font-size: 11px; font-weight: 600; color: #752f43; padding-bottom: 0; line-height: 19px; } .hj_co_m_12838 .sbwf-main-form-container p.info, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.info { text-align: center; color: #727272; font-size: 14px; line-height: 20px; padding-bottom: 20px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input.wpforms-field-medium { width: 100%; max-width: 100%; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form .wpforms-field { padding-top: 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="text"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="email"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="tel"] { border: 2px solid #f4f3f3; font-size: 14px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full { margin: 24px 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 260px; height: 61px; font-size: 16px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_co_m_12838 .sbwf-main-form-container { padding: 20px; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 170px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { font-size: 22px; line-height: 28px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { font-size: 18px; line-height: 24px; } .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="text"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="email"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="tel"] { height: 36px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 220px; height: 52px; font-size: 15px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_sb_m_12838 div.wpforms-container-full .wpforms-form .wpforms-field-row.wpforms-field-medium { max-width: 100%; } form[data-zi-mapped-form] #wpforms-28160-field_1, form[data-zi-mapped-form] #wpforms-28160-field_1-last, form[data-zi-mapped-form] #wpforms-28160-field_3-container, form[data-zi-mapped-form] #wpforms-28160-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28160-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_6-container[data-zi-field-enriched="false"] { display: block !important; } form[data-zi-mapped-form] #wpforms-28155-field_1, form[data-zi-mapped-form] #wpforms-28155-field_1-last, form[data-zi-mapped-form] #wpforms-28155-field_3-container, form[data-zi-mapped-form] #wpforms-28155-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28155-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_6-container[data-zi-field-enriched="false"] { display: block !important; }

Lake Burien Transitional Care Facility & Western State Hospital, Washington

The protected health information of a small number of patients of two mental health facilities operated by the Washington Department of Social and Health Services has been impermissibly uploaded to ChatGPT. A Lake Burien Transitional Care Facility staff member used their personal ChatGPT account to draft summaries for client case notes, which included the patients’ personal health information.

The Department of Social and Health Services identified one instance where the tool had been impermissibly used. Further investigation identified multiple previous instances where the employee had used the tool to generate case summaries. The case notes included information such as names, diagnoses, and medications.  The state has written to 12 families of patients who were affected. A similar incident was identified affecting four Western State Hospital patients. The employees were instructed to delete all ChatGPT prompts before deleting their accounts.

A Growing Privacy Risk

A survey conducted by the clinical technology company Wolters Kluwer Health earlier this year suggests many healthcare employees are using AI tools that have not been authorized for use by their IT department. According to the survey, 40% of hospital workers said they were aware of colleagues using unauthorized AI tools, and 20% admitted to using the tools themselves.

AI tools have tremendous potential in healthcare and can greatly improve efficiency, and employees often turn to these tools to get more done in less time. While many AI tools can be used in healthcare in compliance with the HIPAA Rules, consumer versions of AI tools lack the necessary safeguards to comply with the HIPAA Rules and must not be used by healthcare staff in connection with any protected health information.

In addition to the privacy risks, these tools can also pose a risk to patient safety, as they can generate responses containing misleading or inaccurate information. In one recent case, a woman with epilepsy took the advice of ChatGPT while attempting to wean herself off her anti-seizure prescription medication. She suffered a fatal seizure after following the medication reduction regimen suggested by ChatGPT. A lawsuit has been filed against OpenAI in response, that alleges that ChatGPT effectively practiced medicine without a license.

The post Healthcare Providers Discover Unauthorized PHI Disclosures to AI Tools appeared first on The HIPAA Journal.

Security Incident at EHR Vendor Affects Patients of New York Counselling Practices

Hispanic Counseling Center and Brooklyn Counseling Services in New York have notified patients that some of their personal and health information was compromised in a data security incident at their electronic medical record vendor.

Hispanic Counseling Center

Long Island, New York-based Hispanic Counseling Center operates a mental health clinic and a substance use disorder clinic and provides bilingual counselling services. According to recently mailed notification letters, its electronic medical record vendor, Accumedic Computer Systems, informed Hispanic Counseling Center that it detected suspicious activity within its network on June 8, 2026.

Third-party cybersecurity experts were engaged to investigate the activity, and on August 7, 2026, the EHR vendor concluded that an unauthorized third party first accessed the Accumedic Computer Systems network on April 8, 2026, and potentially obtained customer information between June 4, 2026, and June 8, 2026. The impacted data was reviewed, and on September 1, 2026, Accumedic Computer Systems confirmed that patient health information had been exposed and was potentially obtained. The types of data involved included names, dates of birth, Social Security numbers, medical information, and health insurance information.

The EHR vendor has confirmed that additional technical safeguards have been implemented to prevent similar incidents in the future. Hispanic Counseling Center started notifying the affected individuals on October 30, 2026. The notification letters state that complimentary credit monitoring services are available to the affected individuals. The number of affected individuals has not been publicly disclosed as of the date of this article.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please enable JavaScript in your browser to complete this form.

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { margin-bottom: 18px; } .inpage_banner_12838 a { max-width: 80%; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } } .hj_co_m_12838 { margin-bottom: 30px; } .hj_co_m_12838 .sbwf-main-form-container { max-width: 340px; margin: 0 auto; box-shadow: 0 4px 6px rgba(0,0,0,0.05),0 6px 6px rgba(0,0,0,0.05); padding: 30px; box-sizing: border-box; border: 1px solid #f4f4f4; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 200px; margin: 0 auto; display: block; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { text-align: center; border-top: 1px dashed #c8c8c8; padding: 20px 0 0; margin: 30px 0 20px; color: #753043; font-weight: 600; line-height: 30px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { text-align: center; font-size: 16px; color: #3B3B3B; line-height: 24px; font-weight: 600; margin: 0; padding: 0; } #sidebar .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 span { font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container p.terms, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms { text-align: center; font-size: 11px; padding-bottom: 0; line-height: 19px; margin: 10px 0 10px; } .hj_co_m_12838 .sbwf-main-form-container p.terms a { color: #753044; text-decoration: none; } .hj_co_m_12838 .sbwf-main-form-container p.terms a:hover { text-decoration: underline; } .hj_co_m_12838 .sbwf-main-form-container p.terms_title, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms_title { text-align: center; font-size: 11px; font-weight: 600; color: #752f43; padding-bottom: 0; line-height: 19px; } .hj_co_m_12838 .sbwf-main-form-container p.info, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.info { text-align: center; color: #727272; font-size: 14px; line-height: 20px; padding-bottom: 20px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input.wpforms-field-medium { width: 100%; max-width: 100%; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form .wpforms-field { padding-top: 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="text"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="email"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="tel"] { border: 2px solid #f4f3f3; font-size: 14px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full { margin: 24px 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 260px; height: 61px; font-size: 16px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_co_m_12838 .sbwf-main-form-container { padding: 20px; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 170px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { font-size: 22px; line-height: 28px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { font-size: 18px; line-height: 24px; } .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="text"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="email"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="tel"] { height: 36px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 220px; height: 52px; font-size: 15px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_sb_m_12838 div.wpforms-container-full .wpforms-form .wpforms-field-row.wpforms-field-medium { max-width: 100%; } form[data-zi-mapped-form] #wpforms-28160-field_1, form[data-zi-mapped-form] #wpforms-28160-field_1-last, form[data-zi-mapped-form] #wpforms-28160-field_3-container, form[data-zi-mapped-form] #wpforms-28160-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28160-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_6-container[data-zi-field-enriched="false"] { display: block !important; } form[data-zi-mapped-form] #wpforms-28155-field_1, form[data-zi-mapped-form] #wpforms-28155-field_1-last, form[data-zi-mapped-form] #wpforms-28155-field_3-container, form[data-zi-mapped-form] #wpforms-28155-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28155-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_6-container[data-zi-field-enriched="false"] { display: block !important; }

Brooklyn Counseling Services

Brooklyn Counseling Services, a Brooklyn, New York-based provider of psychological and emotional care and support, has also notified certain patients about a recent security incident that exposed some of their personal data. The company, which operates formally as BCS Group and is also known as BCS Counselling Group, said the incident affected one of its electronic medical records vendors.

State Attorneys general have been notified about the incident; however, the total number of affected individuals has yet to be publicly disclosed. The incident affected one Massachusetts resident and two Vermont residents; however, the vast majority of individuals are likely to reside in Brooklyn, and the New York Attorney General does not publicly disclose the number of individuals affected by data breaches.

The individual notification letters state the types of information involved for each individual, which include names, email addresses, phone numbers, dates of birth, Social Security Numbers, and health records. The breach notification letter seen by The HIPAA Journal does not state when the incident occurred and does not name the vendor; however, the timing of the letters suggests the incident involved the same vendor, Accumedic Computer Systems, which offers EHR software specifically for behavioral health services providers.

The post Security Incident at EHR Vendor Affects Patients of New York Counselling Practices appeared first on The HIPAA Journal.

Data Breaches Announced by HCA Healthcare; Blossom Health

Data breaches have been announced by HCA Healthcare, Blossom Health, El Camino Health, and University of Mississippi Medical Center.

HCA Healthcare Inc.

Nashville, Tennessee-based HCA Healthcare Inc., the operator of 189 hospitals and approximately 2,600 ambulatory sites of care in 19 U.S. states, has disclosed a cybersecurity incident that was first identified on August 12, 2026. Patient and employee data were compromised in the incident.

Suspicious activity was identified within certain IT systems, and the forensic investigation confirmed unauthorized access to those systems on August 12, 2026. HCA Healthcare confirmed that the threat actor obtained copies of certain HR files containing medical resident personal information. The review of the impacted files confirmed that they contained information related to employment, including name, date of birth, email address, phone number, Social Security number, and immigration information.

Patient data was also compromised related to certain affiliated facilities and physician offices. Patient data exposed in the incident included names, email addresses, phone numbers, dates of birth, Social Security numbers, medical information, and health insurance information.  The number of affected patients has yet to be disclosed, although 15,096 Texas residents are known to have been affected. The affected individuals have been offered two years of complimentary credit monitoring services.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please enable JavaScript in your browser to complete this form.

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { margin-bottom: 18px; } .inpage_banner_12838 a { max-width: 80%; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } } .hj_co_m_12838 { margin-bottom: 30px; } .hj_co_m_12838 .sbwf-main-form-container { max-width: 340px; margin: 0 auto; box-shadow: 0 4px 6px rgba(0,0,0,0.05),0 6px 6px rgba(0,0,0,0.05); padding: 30px; box-sizing: border-box; border: 1px solid #f4f4f4; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 200px; margin: 0 auto; display: block; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { text-align: center; border-top: 1px dashed #c8c8c8; padding: 20px 0 0; margin: 30px 0 20px; color: #753043; font-weight: 600; line-height: 30px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { text-align: center; font-size: 16px; color: #3B3B3B; line-height: 24px; font-weight: 600; margin: 0; padding: 0; } #sidebar .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 span { font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container p.terms, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms { text-align: center; font-size: 11px; padding-bottom: 0; line-height: 19px; margin: 10px 0 10px; } .hj_co_m_12838 .sbwf-main-form-container p.terms a { color: #753044; text-decoration: none; } .hj_co_m_12838 .sbwf-main-form-container p.terms a:hover { text-decoration: underline; } .hj_co_m_12838 .sbwf-main-form-container p.terms_title, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms_title { text-align: center; font-size: 11px; font-weight: 600; color: #752f43; padding-bottom: 0; line-height: 19px; } .hj_co_m_12838 .sbwf-main-form-container p.info, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.info { text-align: center; color: #727272; font-size: 14px; line-height: 20px; padding-bottom: 20px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input.wpforms-field-medium { width: 100%; max-width: 100%; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form .wpforms-field { padding-top: 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="text"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="email"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="tel"] { border: 2px solid #f4f3f3; font-size: 14px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full { margin: 24px 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 260px; height: 61px; font-size: 16px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_co_m_12838 .sbwf-main-form-container { padding: 20px; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 170px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { font-size: 22px; line-height: 28px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { font-size: 18px; line-height: 24px; } .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="text"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="email"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="tel"] { height: 36px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 220px; height: 52px; font-size: 15px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_sb_m_12838 div.wpforms-container-full .wpforms-form .wpforms-field-row.wpforms-field-medium { max-width: 100%; } form[data-zi-mapped-form] #wpforms-28160-field_1, form[data-zi-mapped-form] #wpforms-28160-field_1-last, form[data-zi-mapped-form] #wpforms-28160-field_3-container, form[data-zi-mapped-form] #wpforms-28160-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28160-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_6-container[data-zi-field-enriched="false"] { display: block !important; } form[data-zi-mapped-form] #wpforms-28155-field_1, form[data-zi-mapped-form] #wpforms-28155-field_1-last, form[data-zi-mapped-form] #wpforms-28155-field_3-container, form[data-zi-mapped-form] #wpforms-28155-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28155-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_6-container[data-zi-field-enriched="false"] { display: block !important; }

Blossom Health

Blossom BH Opco Inc., an online telepsychiatry and virtual mental health provider that does business as Blossom Health, has started notifying certain patients about an August 2026 data security incident involving unauthorized access to its electronic health record (EHR) software. According to its October 29, 2026, notification letters, an unauthorized actor gained access to the EHR software and patient data via a phishing attack on a non-employee contractor.

The incident has been investigated, and Blossom Health confirmed that the exposed information included names, contact information, and health insurance information. Blossom Health said financial information and Social Security numbers were not accessible. In its website regulatory disclosure, Blossom Health confirmed that the threat actor downloaded a limited number of patient medical records and a user spreadsheet containing patient information.

The unauthorized access has been blocked, user passwords have been changed, and additional technical security measures have been deployed to reduce the risk of similar incidents in the future.  As a precaution against identity theft and fraud, the affected individuals have been offered complimentary single-bureau credit report, credit score, and credit monitoring services. The Texas Attorney General was informed that 2,103 Texas residents have been affected, although the total number of affected individuals has yet to be disclosed.

El Camino Health

El Camino Health, a non-profit health system serving Santa Clara County and the Bay Area in California, has confirmed that an unauthorized individual gained access to its Microsoft 365 environment. Suspicious activity was identified on September 1, 2026, and the forensic investigation confirmed unauthorized access to four Microsoft 365 accounts, which were intermittently accessed between August 26, 2026, and September 2, 2026. Certain documents within those accounts were copied or downloaded.

The review of the affected files has been completed, and they were found to contain contact information, demographic information, Social Security numbers, driver’s license numbers, dates of birth, medical record numbers, patient account numbers, diagnoses, treatment information, prescription information, provider names, dates of service, and health insurance information. A subset of patients also had financial account and routing numbers compromised in the incident.

El Camino Health has implemented additional protection and monitoring measures to reduce the risk of similar incidents in the future, and the affected individuals have been offered complimentary credit monitoring and identity theft protection services. The number of affected individuals has not yet been publicly disclosed.

University of Mississippi Medical Center

University of Mississippi Medical Center (UMMC) has started notifying certain patients about unauthorized access to its computer systems. The unauthorized access was identified on February 19, 2026. Third-party cybersecurity experts were engaged to assist with the investigation, and on October 20, 2026, it was confirmed that its network was subject to unauthorized access between February 11, 2026, and February 19, 2026.

UMMC has reviewed the exposed files, but its notice to the California Attorney General does not include details of the types of data involved or the number of affected individuals. There is currently no substitute data breach notice on the UMMC website. This appears to have been a ransomware attack. The Medusa ransomware group claimed responsibility for the attack in March 2026 and demanded payment to prevent the sale or release of the stolen data. The ransom was not paid.

The post Data Breaches Announced by HCA Healthcare; Blossom Health appeared first on The HIPAA Journal.

University Hospitals Working on Restoring Systems After Cyberattack

University Hospitals is working on restoring systems after an October 22 cyberattack. Cybersecurity incidents have also been announced by EyeMed Vision Care and Facial Surgery Group.

University Hospitals

Cleveland, Ohio-based University Hospitals, a 21-hospital health system, is dealing with a cybersecurity incident that was identified on October 22, 2026. University Hospitals activated its incident response protocols and implemented containment measures, which included taking digital services offline, including its MyChart patient portal, while the incident is investigated and mitigated. University Hospitals is still working on safely restoring the affected systems, and in a November 2, 2026, update, confirmed that systems remained offline. A timeline for the restoration of normal business operations cannot be provided.

The health system confirmed that its hospitals, emergency departments, and physician offices remain open, but the incident has disrupted pre-authorizations, and some appointments and elective procedures have had to be rescheduled. The nature of the cyberattack, such as if ransomware was involved, has not been publicly disclosed. No ransomware group appears to have claimed responsibility for the incident. The investigation is ongoing, and University Hospitals has not yet determined the extent to which patient data was involved.

EyeMed Vision Care

EyeMed Vision Care, a Cincinnati, Ohio-based vision insurance provider, has started notifying certain individuals about an email error that resulted in an impermissible disclosure of members’ sensitive information. On September 22, 2026, EyeMed Vision Care sent an email containing member information to an incorrect email address. The incident was the result of human error, was not malicious in nature, and involved a single misdirected email. The email contained information about individuals enrolled in a vision benefit plan managed by EyeMed Vision Care, including names, addresses, dates of birth, Social Security numbers, and membership identification numbers.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please enable JavaScript in your browser to complete this form.

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { margin-bottom: 18px; } .inpage_banner_12838 a { max-width: 80%; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } } .hj_co_m_12838 { margin-bottom: 30px; } .hj_co_m_12838 .sbwf-main-form-container { max-width: 340px; margin: 0 auto; box-shadow: 0 4px 6px rgba(0,0,0,0.05),0 6px 6px rgba(0,0,0,0.05); padding: 30px; box-sizing: border-box; border: 1px solid #f4f4f4; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 200px; margin: 0 auto; display: block; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { text-align: center; border-top: 1px dashed #c8c8c8; padding: 20px 0 0; margin: 30px 0 20px; color: #753043; font-weight: 600; line-height: 30px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { text-align: center; font-size: 16px; color: #3B3B3B; line-height: 24px; font-weight: 600; margin: 0; padding: 0; } #sidebar .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 span { font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container p.terms, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms { text-align: center; font-size: 11px; padding-bottom: 0; line-height: 19px; margin: 10px 0 10px; } .hj_co_m_12838 .sbwf-main-form-container p.terms a { color: #753044; text-decoration: none; } .hj_co_m_12838 .sbwf-main-form-container p.terms a:hover { text-decoration: underline; } .hj_co_m_12838 .sbwf-main-form-container p.terms_title, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms_title { text-align: center; font-size: 11px; font-weight: 600; color: #752f43; padding-bottom: 0; line-height: 19px; } .hj_co_m_12838 .sbwf-main-form-container p.info, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.info { text-align: center; color: #727272; font-size: 14px; line-height: 20px; padding-bottom: 20px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input.wpforms-field-medium { width: 100%; max-width: 100%; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form .wpforms-field { padding-top: 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="text"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="email"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="tel"] { border: 2px solid #f4f3f3; font-size: 14px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full { margin: 24px 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 260px; height: 61px; font-size: 16px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_co_m_12838 .sbwf-main-form-container { padding: 20px; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 170px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { font-size: 22px; line-height: 28px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { font-size: 18px; line-height: 24px; } .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="text"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="email"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="tel"] { height: 36px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 220px; height: 52px; font-size: 15px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_sb_m_12838 div.wpforms-container-full .wpforms-form .wpforms-field-row.wpforms-field-medium { max-width: 100%; } form[data-zi-mapped-form] #wpforms-28160-field_1, form[data-zi-mapped-form] #wpforms-28160-field_1-last, form[data-zi-mapped-form] #wpforms-28160-field_3-container, form[data-zi-mapped-form] #wpforms-28160-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28160-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_6-container[data-zi-field-enriched="false"] { display: block !important; } form[data-zi-mapped-form] #wpforms-28155-field_1, form[data-zi-mapped-form] #wpforms-28155-field_1-last, form[data-zi-mapped-form] #wpforms-28155-field_3-container, form[data-zi-mapped-form] #wpforms-28155-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28155-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_6-container[data-zi-field-enriched="false"] { display: block !important; }

The number of affected individuals has not yet been publicly disclosed; however, since the California Attorney General was notified about the data breach, at least 500 California residents have been affected. EyeMed said it has taken steps to prevent similar incidents in the future, including revising its privacy and operations policies and procedures, updating its training program, and retraining appropriate members of its workforce. As a precaution against data misuse, the affected individuals have been offered complimentary credit monitoring and identity theft protection services.

Facial Surgery Group

Facial Surgery Group, the operator of five oral and maxillofacial surgery centers in Kansas City, Liberty, Overland Park, and Blue Springs, Missouri, has confirmed that the personal and protected health information of 11,407 individuals has been exposed in an email security incident. On September 16, 2026, a notice was added to the Facial Surgery Group website providing further information on the incident. Suspicious activity was identified within its email system on November 24, 2025. Third-party cybersecurity experts were engaged to investigate the incident and confirmed that a single email account had been accessed by an unauthorized individual.

A data mining company was engaged to review the affected account, and that process was completed on September 9, 2026. The account contained names, birth dates, demographic information, Social Security numbers, financial account numbers, and health information. The affected individuals were notified about the incident on October 9, 2025. Steps have been taken to prevent similar incidents in the future, and the affected individuals have been offered complimentary credit monitoring and identity theft restoration services.

The post University Hospitals Working on Restoring Systems After Cyberattack appeared first on The HIPAA Journal.

Marathon Health Data Breach Reportedly Affects 5.7 Million Individuals

State attorneys general have been informed about a substantial Marathon Health data breach that reportedly involved the personal and protected health information of almost 5.7 million individuals. Indianapolis, Indiana-based Marathon Health is an employer-sponsored healthcare provider. The company partners with employers, labor unions, and public sector organizations and provides advanced primary care through onsite and near-site health centers across the United States. According to its website, the company serves more than 600 self-funded employers, labor unions, and public sector organizations, operates more than 720 health centers in 41 U.S. states, has around 1,600 providers, and offers virtual care to individuals in all 50 states. Marathon Health has a patient base of around 3 million individuals.

Only a handful of state attorneys general publish information on the number of state residents affected by data breaches. The Massachusetts Attorney General was informed that 29,075 state residents were affected, and the Vermont Attorney General was notified that 8,858 state residents were impacted. While the website of the Texas Attorney General states that 234,534 Texas residents were affected, law firm Emery Reddy reports that the Texas Attorney General was informed that 5,684,735 individuals are being notified. As a HIPAA-covered entity, the data breach must be reported to the HHS’ Office for Civil Rights (OCR); however, it is not currently listed on the OCR data breach portal. If that total is confirmed, the Marathon Health data breach will rank as the fourth-largest healthcare data breach to be reported by a HIPAA-regulated entity this year.

A copy of the data breach notification letter is available on the website of the California Attorney General. The notice states that on August 24, 2026, suspicious activity was identified related to one of its employee accounts. The affected account was immediately disabled, and an investigation was launched to determine the nature and scope of the activity. Marathon Health learned that an unauthorized individual posed as a Marathon IT worker and tricked the employee into disclosing their credentials. The credentials provided access to a cloud-hosted application, and the unauthorized individual exported information from that application in the space of a few hours on August 24, 2026.

The social engineering tactics – impersonating an IT worker to steal credentials – are used by initial access brokers and several different cybercriminal groups, including the ShinyHunters and Scattered Spider threat groups. Neither group appears to have claimed responsibility for the attack, nor has any ransomware group.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please enable JavaScript in your browser to complete this form.

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { margin-bottom: 18px; } .inpage_banner_12838 a { max-width: 80%; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } } .hj_co_m_12838 { margin-bottom: 30px; } .hj_co_m_12838 .sbwf-main-form-container { max-width: 340px; margin: 0 auto; box-shadow: 0 4px 6px rgba(0,0,0,0.05),0 6px 6px rgba(0,0,0,0.05); padding: 30px; box-sizing: border-box; border: 1px solid #f4f4f4; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 200px; margin: 0 auto; display: block; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { text-align: center; border-top: 1px dashed #c8c8c8; padding: 20px 0 0; margin: 30px 0 20px; color: #753043; font-weight: 600; line-height: 30px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { text-align: center; font-size: 16px; color: #3B3B3B; line-height: 24px; font-weight: 600; margin: 0; padding: 0; } #sidebar .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 span { font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container p.terms, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms { text-align: center; font-size: 11px; padding-bottom: 0; line-height: 19px; margin: 10px 0 10px; } .hj_co_m_12838 .sbwf-main-form-container p.terms a { color: #753044; text-decoration: none; } .hj_co_m_12838 .sbwf-main-form-container p.terms a:hover { text-decoration: underline; } .hj_co_m_12838 .sbwf-main-form-container p.terms_title, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms_title { text-align: center; font-size: 11px; font-weight: 600; color: #752f43; padding-bottom: 0; line-height: 19px; } .hj_co_m_12838 .sbwf-main-form-container p.info, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.info { text-align: center; color: #727272; font-size: 14px; line-height: 20px; padding-bottom: 20px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input.wpforms-field-medium { width: 100%; max-width: 100%; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form .wpforms-field { padding-top: 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="text"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="email"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="tel"] { border: 2px solid #f4f3f3; font-size: 14px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full { margin: 24px 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 260px; height: 61px; font-size: 16px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_co_m_12838 .sbwf-main-form-container { padding: 20px; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 170px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { font-size: 22px; line-height: 28px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { font-size: 18px; line-height: 24px; } .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="text"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="email"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="tel"] { height: 36px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 220px; height: 52px; font-size: 15px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_sb_m_12838 div.wpforms-container-full .wpforms-form .wpforms-field-row.wpforms-field-medium { max-width: 100%; } form[data-zi-mapped-form] #wpforms-28160-field_1, form[data-zi-mapped-form] #wpforms-28160-field_1-last, form[data-zi-mapped-form] #wpforms-28160-field_3-container, form[data-zi-mapped-form] #wpforms-28160-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28160-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_6-container[data-zi-field-enriched="false"] { display: block !important; } form[data-zi-mapped-form] #wpforms-28155-field_1, form[data-zi-mapped-form] #wpforms-28155-field_1-last, form[data-zi-mapped-form] #wpforms-28155-field_3-container, form[data-zi-mapped-form] #wpforms-28155-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28155-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_6-container[data-zi-field-enriched="false"] { display: block !important; }

Marathon Health’s review of the impacted data was completed on September 9, 2026. According to the notification letters to California residents, the impacted data included names, contact information, dates of birth, and Social Security numbers. The websites of the Texas and Vermont Attorneys General also state that medical information and health insurance information were compromised. Marathon Health has taken steps to prevent similar incidents in the future and is offering the affected individuals 12 or 24 months of complimentary credit monitoring services. Notification letters started to be mailed to the affected individuals on October 20, 2026.

Due to how Marathon Health operates, some individuals are likely to receive notification letters informing them that some of their data was compromised, when they have not received any healthcare services from the company. They may not be aware of Marathon Health or why the company has their data. The reason is that Marathon Health is provided with information on all enrolled plan members to allow it to verify coverage, communicate benefits, bill insurance companies, and schedule appointments. One of the affected clients is Indiana University, which informed employees and family members enrolled in the Anthem PPO HDHP or Anthem PPO $500 Deductible Plan that they are eligible to use Marathon Health centers, and as such, Marathon Health was provided with some of their information.

The post Marathon Health Data Breach Reportedly Affects 5.7 Million Individuals appeared first on The HIPAA Journal.

Cognitive Health Technologies Data Breach Affects 49,500 Individuals

Data breaches have been announced by Cognitive Health Technologies in New York, City Ambulance Service in Texas, Baraga County Memorial Hospital in Michigan, The Speech Clinic in Georgia, and Innovative Alternatives in Texas.

Cognitive Health Technologies, New York

Cognitive Health Technologies LLC, a New York-based healthcare technology and IT consulting company, has disclosed a data security incident involving the protected health information of 49,467 individuals. According to its substitute data breach notice, suspicious network activity was identified on April 27, 2026. A forensic investigation was initiated to determine the nature and scope of the activity, which confirmed that its network had been accessed by an unauthorized third party between February 5, 2026, and April 28, 2026. During that time, there was unauthorized access and acquisition of files and folders containing protected health information.

The data review confirmed that the information compromised in the incident included names, dates of birth, health insurance information, medical histories, and treatment information. While patient data was compromised in the incident, no misuse of that information has been identified. Cognitive Health Technologies said it has reviewed its security policies and has implemented additional measures to protect against similar incidents in the future.

Viking Enterprises (City Ambulance Service), Texas

Viking Enterprises, doing business as City Ambulance Service in Spring, Texas, has notified the HHS Office for Civil Rights about a hacking incident affecting 14,324 individuals. The breach was reported to OCR on August 31, 2026, as an email-related incident. Little information has been released about the incident, although based on the report submitted to the Texas Attorney General, the compromised data includes names, addresses, dates of birth, medical information, health insurance information, and Social Security numbers.
Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please enable JavaScript in your browser to complete this form.

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { margin-bottom: 18px; } .inpage_banner_12838 a { max-width: 80%; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } } .hj_co_m_12838 { margin-bottom: 30px; } .hj_co_m_12838 .sbwf-main-form-container { max-width: 340px; margin: 0 auto; box-shadow: 0 4px 6px rgba(0,0,0,0.05),0 6px 6px rgba(0,0,0,0.05); padding: 30px; box-sizing: border-box; border: 1px solid #f4f4f4; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 200px; margin: 0 auto; display: block; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { text-align: center; border-top: 1px dashed #c8c8c8; padding: 20px 0 0; margin: 30px 0 20px; color: #753043; font-weight: 600; line-height: 30px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { text-align: center; font-size: 16px; color: #3B3B3B; line-height: 24px; font-weight: 600; margin: 0; padding: 0; } #sidebar .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 span { font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container p.terms, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms { text-align: center; font-size: 11px; padding-bottom: 0; line-height: 19px; margin: 10px 0 10px; } .hj_co_m_12838 .sbwf-main-form-container p.terms a { color: #753044; text-decoration: none; } .hj_co_m_12838 .sbwf-main-form-container p.terms a:hover { text-decoration: underline; } .hj_co_m_12838 .sbwf-main-form-container p.terms_title, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms_title { text-align: center; font-size: 11px; font-weight: 600; color: #752f43; padding-bottom: 0; line-height: 19px; } .hj_co_m_12838 .sbwf-main-form-container p.info, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.info { text-align: center; color: #727272; font-size: 14px; line-height: 20px; padding-bottom: 20px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input.wpforms-field-medium { width: 100%; max-width: 100%; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form .wpforms-field { padding-top: 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="text"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="email"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="tel"] { border: 2px solid #f4f3f3; font-size: 14px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full { margin: 24px 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 260px; height: 61px; font-size: 16px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_co_m_12838 .sbwf-main-form-container { padding: 20px; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 170px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { font-size: 22px; line-height: 28px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { font-size: 18px; line-height: 24px; } .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="text"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="email"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="tel"] { height: 36px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 220px; height: 52px; font-size: 15px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_sb_m_12838 div.wpforms-container-full .wpforms-form .wpforms-field-row.wpforms-field-medium { max-width: 100%; } form[data-zi-mapped-form] #wpforms-28160-field_1, form[data-zi-mapped-form] #wpforms-28160-field_1-last, form[data-zi-mapped-form] #wpforms-28160-field_3-container, form[data-zi-mapped-form] #wpforms-28160-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28160-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_6-container[data-zi-field-enriched="false"] { display: block !important; } form[data-zi-mapped-form] #wpforms-28155-field_1, form[data-zi-mapped-form] #wpforms-28155-field_1-last, form[data-zi-mapped-form] #wpforms-28155-field_3-container, form[data-zi-mapped-form] #wpforms-28155-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28155-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_6-container[data-zi-field-enriched="false"] { display: block !important; }

The Qilin ransomware and data theft/extortion group claimed responsibility for the attack and maintains that sensitive data was stolen. It is unclear if ransomware was used in the attack. The July 19, 2026, listing on its dark web data leak site states that 14 GB of data was exfiltrated, and the stolen data has been published.  The HIPAA Journal has not downloaded any of the data, so it cannot verify the claim; however, the screenshots uploaded as proof of compromise include some patient data.

Baraga County Memorial Hospital, Michigan

Baraga County Memorial Hospital in L’Anse, Michigan, has reported a data breach to the HHS’ Office for Civil Rights that involved unauthorized access to systems containing the protected health information of patients. At the time of publication, the number of affected individuals has yet to be determined. The breach has been reported using a placeholder figure of at least 501 affected individuals.

The hospital has not yet disclosed details of the incident or the information involved, other than the report to OCR that states this was a hacking/IT incident. A cybercriminal group claimed responsibility for the incident on July 4, 2026. The Wallstreet ransomware group added Baraga County Memorial Hospital to its dark web data leak site and claims to have exfiltrated data in the attack. The group leaked the stolen data when the ransom was not paid.

Innovative Alternatives, Texas

Innovative Alternatives, Inc., a Houston, Texas-based nonprofit mental health and counselling service provider, has disclosed a data security incident involving the personal and protected health information of approximately 1,500 current and former clients, employees, and donors. On August 2, 2026, Innovative Alternatives learned that a criminal cyber actor had accessed its network and used ransomware to encrypt files. Third-party cybersecurity and digital forensics experts were engaged to investigate the incident, and it was confirmed that data was accessed and may have been acquired. The electronic medical record system was not involved.

The data review confirmed that the compromised information included names, contact information, clinical counselling notes, and, for employees, contact and employment information. Innovative Alternatives has changed all system and user passwords, conducted additional security scans, and worked with third-party cybersecurity experts to strengthen its security measures to reduce the risk of similar incidents in the future. Notification letters were mailed to the affected individuals on October 2, 2026.

The Speech Clinic, Georgia

The Speech Clinic, a Waycross, Georgia-based speech-language pathology, occupational therapy, and physical therapy service provider, has experienced a data security incident. On August 10, 2026, the practice began experiencing difficulties accessing a computer at its Waycross location. The forensic investigation confirmed on August 17, 2026, that the computer had been remotely accessed by an unauthorized third party, as well as an older server containing pre-2017 patient records of 2,168 patients.

The forensic investigation could not confirm whether patient data was accessed, but unauthorized access could not be ruled out. For some patients, only their name was exposed, while others had a combination of name, date of birth, Social Security number, diagnosis, and other medical information.

The post Cognitive Health Technologies Data Breach Affects 49,500 Individuals appeared first on The HIPAA Journal.

41,000 Connecticut Medicaid Recipients Affected by DHS Data Incident

Data breaches have been announced by the Connecticut Department of Social Services, Public Partnerships LLC, Hattiesburg Eye Clinic, and the Eye Care Center of Snohomish.

Connecticut Department of Social Services

The  Connecticut Department of Social Services (DSS) has reported a data breach involving the protected health information of 41,000 individuals. The incident involved claims and payment information related to the Connecticut Medicaid (HUSKY) program, which was exposed after an unauthorized user gained access to a Connecticut Medicaid provider reimbursement account. DSS was informed about the data breach by its fiscal agent and account administrator, Gainwell Technologies, on June 25, 2026. The investigation determined that the unauthorized access was most likely financially motivated, rather than to obtain patient data; however, data theft could not be ruled out.

The provider portal has been secured, and the affected individuals have been offered complimentary credit monitoring and identity theft protection services. Electronic medical records, financial information, and Social Security numbers were not involved. The breach involved a combination of names, identification numbers associated with Medicare claims or provider payment accounts, dates of service, payment information, information about the services received, amounts paid, and information related to non-Medicaid health insurance.

This is the second such incident to be announced this year. An earlier breach in March 2026 affected approximately 22,500 individuals and involved unauthorized access to the HUSKY system using the compromised credentials of a Hartford Healthcare employee.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please enable JavaScript in your browser to complete this form.

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

@media only screen and (min-width: 961px) { .inpage_mobile { display: none; } .inpage_banner_12838 { margin-bottom: 18px; } .inpage_banner_12838 a { max-width: 80%; display: block; margin: 0 auto; } } @media only screen and (max-width: 960px) { .inpage_desktop { display: none; } } .hj_co_m_12838 { margin-bottom: 30px; } .hj_co_m_12838 .sbwf-main-form-container { max-width: 340px; margin: 0 auto; box-shadow: 0 4px 6px rgba(0,0,0,0.05),0 6px 6px rgba(0,0,0,0.05); padding: 30px; box-sizing: border-box; border: 1px solid #f4f4f4; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 200px; margin: 0 auto; display: block; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { text-align: center; border-top: 1px dashed #c8c8c8; padding: 20px 0 0; margin: 30px 0 20px; color: #753043; font-weight: 600; line-height: 30px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { text-align: center; font-size: 16px; color: #3B3B3B; line-height: 24px; font-weight: 600; margin: 0; padding: 0; } #sidebar .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 span { font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container p.terms, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms { text-align: center; font-size: 11px; padding-bottom: 0; line-height: 19px; margin: 10px 0 10px; } .hj_co_m_12838 .sbwf-main-form-container p.terms a { color: #753044; text-decoration: none; } .hj_co_m_12838 .sbwf-main-form-container p.terms a:hover { text-decoration: underline; } .hj_co_m_12838 .sbwf-main-form-container p.terms_title, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.terms_title { text-align: center; font-size: 11px; font-weight: 600; color: #752f43; padding-bottom: 0; line-height: 19px; } .hj_co_m_12838 .sbwf-main-form-container p.info, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.info { text-align: center; color: #727272; font-size: 14px; line-height: 20px; padding-bottom: 20px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input.wpforms-field-medium { width: 100%; max-width: 100%; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form .wpforms-field { padding-top: 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="text"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="email"], .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form input[type="tel"] { border: 2px solid #f4f3f3; font-size: 14px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full { margin: 24px 0; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 260px; height: 61px; font-size: 16px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_co_m_12838 .sbwf-main-form-container { padding: 20px; } .hj_co_m_12838 .sbwf-main-form-container img { max-width: 170px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 { font-size: 22px; line-height: 28px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title1 span { font-weight: 700; color: #000; padding-top: 4px; display: block; line-height: 34px; } .hj_co_m_12838 .sbwf-main-form-container p.cl_title2, article.entry-content .lp-main .lp-main-content .hj_co_m_12838 .sbwf-main-form-container p.cl_title2 { font-size: 18px; line-height: 24px; } .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="text"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="email"], .hj_co_m_12838 div.wpforms-container-full .wpforms-form input.wpforms-field-medium[type="tel"] { height: 36px; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"] { border: 0; color: #fff; margin: 0 auto; display: flex; align-items: center; justify-content: center; box-sizing: border-box; padding: 0 65px 0 30px; background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn.png); background-color: unset; background-size: cover; background-repeat: no-repeat; width: 220px; height: 52px; font-size: 15px; font-weight: 600; } .hj_co_m_12838 .sbwf-main-form-container div.wpforms-container-full .wpforms-form button[type="submit"]:hover { background-image: url(https://www.hipaajournal.com/wp-content/uploads/2026/08/btn_hover.png); background-color: unset; border: 0; } .hj_sb_m_12838 div.wpforms-container-full .wpforms-form .wpforms-field-row.wpforms-field-medium { max-width: 100%; } form[data-zi-mapped-form] #wpforms-28160-field_1, form[data-zi-mapped-form] #wpforms-28160-field_1-last, form[data-zi-mapped-form] #wpforms-28160-field_3-container, form[data-zi-mapped-form] #wpforms-28160-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28160-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28160-field_6-container[data-zi-field-enriched="false"] { display: block !important; } form[data-zi-mapped-form] #wpforms-28155-field_1, form[data-zi-mapped-form] #wpforms-28155-field_1-last, form[data-zi-mapped-form] #wpforms-28155-field_3-container, form[data-zi-mapped-form] #wpforms-28155-field_6-container { display: none; } form[data-zi-mapped-form] #wpforms-28155-field_1[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_1-last[data-zi-input-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_3-container[data-zi-field-enriched="false"], form[data-zi-mapped-form] #wpforms-28155-field_6-container[data-zi-field-enriched="false"] { display: block !important; }

Public Partnerships LLC, New York

A data breach we had previously missed was reported by Public Partnerships LLC in early August that involved the attempted sale of the protected health information of 12,018 individuals. Public Partnerships is the single fiscal intermediary (FI) for the New York Consumer Directed Personal Assistance Program (CDPAP). CDPAP is a state Medicaid program that allows individuals who require home care to choose, hire, train, and manage their own caregivers.

In June 2026, Public Partnerships learned that a former facilitator had attempted to sell consumer data to another New York CDPAP facilitator. The former facilitator had been terminated by Public Partnerships in March 2026 for (unspecified) non-compliance with the program integrity requirements. The facilitator who was approached and offered the data refused and reported the incident to Public Partnerships.

Before Public Partnerships became the single FI for CDPAP, the state used hundreds of localized independent organizations. These legacy FIs became network facilitators or subcontractors under Public Partnerships under the single statewide contract with Public Partnerships. When it learned of the alleged sale, the former FI was contacted, informed about the allegation, and was told that offering to sell CDPAP data is unlawful and a breach of its ongoing contractual obligations. The former FI was instructed to delete all CDPAP data in its possession. Public Partnerships also notified all remaining facilitators of their contractual obligations and that the sale and purchase of CDPAP data is unlawful.

The case has been reported to the HHS Office for Civil Rights and the HHS Office of Inspector General, and all potentially impacted individuals have been notified by mail. The impacted data included names, addresses, dates of birth, Medicaid ID numbers, PPL ID numbers, and information relating to enrollment in New York Medicaid. While the sale appears not to have gone ahead, and there have been no other known cases, the affected individuals have been offered complimentary identity protection and credit monitoring services.

Hattiesburg Eye Clinic, P.A., Mississippi

Hattiesburg Eye Clinic, P.A. in Mississippi has reported a data security incident that potentially involved unauthorized access to the protected health information of 6,137 individuals. A network disruption was experienced on August 18, 2026, and third-party cybersecurity experts were engaged to investigate and determine the nature and scope of the activity. The review of the incident concluded on September 16, 2026, and confirmed that patient data had been exposed and may have been acquired. The affected data varied from individual to individual and may have included first and last names, phone numbers, Social Security numbers, and medical diagnoses/conditions.

Additional technical safeguards have been implemented to prevent similar incidents in the future, and notification letters have been mailed to all potentially affected individuals. A ransomware and data theft/extortion group called The Gentlemen claimed responsibility for the incident and maintains that patient data was stolen.

Anup K. Deol, OD PS (Eye Care Center of Snohomish), Washington

Anup K. Deol, OD PS, doing business as Eye Care Center of Snohomish in Washington, has identified unauthorized access to parts of its network containing the protected health information of 3,059 patients. The unauthorized access was identified on August 12, 2026, and third-party cybersecurity experts were engaged to investigate the activity. The investigation confirmed that an unauthorized third party gained access to limited files on its network on or around July 28, 2026.

The review of the affected files was completed on September 28, 2026. The data involved varied from individual to individual and may have included names, addresses, birth dates, and medical information, which may have included lab results, diagnoses, medications, and treatment information. The incident was reported to law enforcement, and additional safeguards have been implemented to prevent similar incidents in the future.

The post 41,000 Connecticut Medicaid Recipients Affected by DHS Data Incident appeared first on The HIPAA Journal.
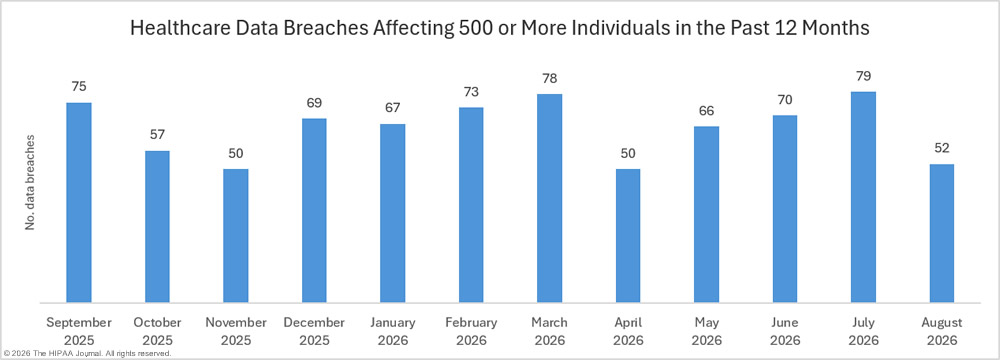
August 2026 Healthcare Data Breach Report

An analysis of data breaches affecting 500 or more individuals reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) in August 2026 shows a considerable improvement from the previous month. Data breaches are down 34% month-over-month, with August’s total of 52 data breaches, the second-lowest monthly total in the past 12 months, well below the 12-month average of 66 data breaches per month.

Healthcare data breaches in the past 12 months - August 2026

While August was a relatively good month for healthcare data breaches, the year-to-date figures show that 2026 is turning out to be another bad year for healthcare data breaches. Last year was the worst-ever year for healthcare data breaches, with 807 incidents reported. So far this year, 593 large healthcare data breaches have been reported to OCR. At this time last year, the total stood at 556 data breaches. That’s a 6.7% year-over-year increase.

YEar to date healthcare data breaches - August 2026

Across the 52 data breaches, the protected health information of at least 8,377,327 individuals was exposed or impermissibly accessed or disclosed. While that represents a 75% month-over-month decrease in affected individuals, July was one of the worst months in recent history for breached healthcare records, with more than 33 million affected individuals.

Individuals affected by healthcare data breaches in the past 12 months - august 2026

This year has already seen the protected health information of 78.6 million individuals exposed or impermissibly accessed or disclosed. That represents a 14.8% year-over-year increase in affected individuals.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

Year to date figures for individuals affected by healthcare data breaches - august 2026

The Biggest Healthcare Data Breaches in August 2026

Two data breaches stand out in August in terms of scale. The largest data breach of the month, and the fourth largest data breach to be reported by a HIPAA-regulated entity so far this year, involved unauthorized access to the protected health information of more than 4.1 million individuals. The incident occurred at AdaptHealth, a healthcare company that provides home medical equipment, diabetes supplies, and sleep therapy products. AdaptHealth was contacted by a member of the ShinyHunters data theft and extortion group in June and was informed that its network had been accessed and sensitive data exfiltrated. Data theft was later confirmed.

The second largest data breach was reported by the clinical genomics company Baylor Genetics. An unknown hacker accessed parts of its network that contained the protected health information of more than 2.8 million patients. These were two of 17 data breaches affecting more than 10,000 individuals, and all but two of those incidents were hacking incidents. No information has been released on one of the non-hacking incidents. The other involved data theft by a former facilitator who stole data and attempted to sell it to another individual.

Regulated Entity State Covered Entity Type Individuals Affected Type of Breach Location of Breached Information Cause of Breach
AdaptHealth, LLC PA Healthcare Provider 4,115,802 Hacking/IT Incident Network Server Hacking incident involving data theft
Baylor Genetics TX Healthcare Provider 2,810,878 Hacking/IT Incident Network Server Hacking incident
American Addiction Centers TN Business Associate 327,754 Hacking/IT Incident Network Server Hacking incident involving theft of data from its Salesforce environment
Premier Medical Group of the Hudson Valley P.C. NY Healthcare Provider 282,075 Hacking/IT Incident Network Server Hacking incident
Boston Healthcare for the Homeless Program MA Healthcare Provider 201,260 Hacking/IT Incident Network Server Hacking incident
Midwest Spine & Brain Institute MN Healthcare Provider 108,487 Unauthorized Access/Disclosure Network Server, Other Hacking incident at business associate (3C Care Systems)
Oakdale Ear Nose & Throat PA d/b/a Minnesota ENT MN Healthcare Provider 99,714 Hacking/IT Incident Email Unauthorized access to six employee email accounts
Osceola Mental Health Inc. dba Park Place Behavioral Healthcare FL Healthcare Provider 71,702 Hacking/IT Incident Network Server Hacking incident
Kern Psychiatric Health and Wellness Center, Inc CA Healthcare Provider 51,352 Hacking/IT Incident Network Server Hacking incident at its management company (Genesis Healthcare Management)
NFI North, Inc. NH Healthcare Provider 49,540 Hacking/IT Incident Network Server Hacking incident
Hawaii Dental Group, Inc DBA Hawaii Family Dental HI Healthcare Provider 45,853 Hacking/IT Incident Email Hacking incident involving a compromised email account
Connecticut Department of Social Services CT Health Plan 41,000 Hacking/IT Incident Network Server Hacking incident involving a provider reimbursement account
Advantage Home Health Care IN Healthcare Provider 19,851 Hacking/IT Incident Network Server Hacking incident involving data exfiltration
Viking Enterprises, Inc. d/b/a City Ambulance Service TX Healthcare Provider 14,324 Hacking/IT Incident Email Ransomware attack (Qilin)
Public Partnerships LLC NY Business Associate 12,018 Unauthorized Access/Disclosure Network Server Insider data theft incident involving a former network facilitator
Kim Knobbe MO Business Associate 11,927 Unauthorized Access/Disclosure Network Server, Other Unauthorized access/disclosure incident – no information available
Silver Summit Medical Corporation CA Healthcare Provider 11,349 Hacking/IT Incident Network Server, Other Hacking incident at an unnamed vendor. Data theft confirmed

When the breach notification deadline is reached, and the number of affected individuals has yet to be determined, data breaches need to be reported to OCR using an estimate of the number of affected individuals. Most regulated entities choose to report these breaches using a figure of 500 or 501 affected individuals, then update the breach report when the data review is concluded. In August, 7 such incidents were reported using these placeholder figures. These incidents are likely to have affected substantially more individuals than the initial breach report suggests.

Regulated Entity State Covered Entity Type Individuals Affected Type of Breach
AnMed Health SC Healthcare Provider 501 Ransomware attack (The Gentlemen)
Baraga County Memorial Hospital MI Healthcare Provider 501 Ransomware attack (Wallstreet)
Longview ER Operations, LLC TX Healthcare Provider 501 Hacking incident
Horizon Eye Care Laser & Eye Surgery Center NJ Healthcare Provider 501 Hacking incident
Vista Del Mar Child and Family Services CA Healthcare Provider 500 Hacking incident
WellDyneRX, LLC FL Healthcare Provider 500 Hacking incident
Well Child, Inc. TN Healthcare Provider 500 Hacking incident – data theft confirmed

Causes of August 2026 Healthcare Data Breaches

The majority of the month’s data breaches were hacking and other IT incidents, which accounted for 78.8% of the month’s data breaches and 98% of the affected individuals (8,215,959). On average, these incidents involved the exposure or theft of the protected health information of 205,399 individuals, with a median breach size of 5,258 individuals.

Causes of august 2026 healthcare data breaches

The year-to-date figures show a slight year-over-year increase in hacking/IT incidents. Between January 1 and August 30, 2026, 457 hacking/IT incidents have been reported, compared to 453 incidents for the corresponding period in 2025. While hacking incidents are only up by 0.9% year-over-year, 74,315,731 individuals have been affected, which is an 18.7% increase compared to this time last year.

There were 12 unauthorized access/disclosure incidents in August, involving the protected health information of 161,368 individuals. The average breach size was 13,447 individuals, and the median breach size was 4,024 individuals. The year-to-date figures show a 21.2% decrease in unauthorized access/disclosure incidents compared to this time last year, with incidents dropping from 94 for the period from January 1 to August 31 to 74 this year. So far this year, 1,651,788 individuals have been affected by these incidents, 71.7% fewer individuals than this time last year.

No loss, theft, or improper disposal incidents were reported in August.  The year-to-date figures show a 75% year-over-year decrease in loss/theft incidents, with only two such incidents reported so far this year compared to 8 last year. There have been two unauthorized disposal incidents reported this year, compared to one such incident for the corresponding period in 2025.

Location of Breached Protected Health Information

In August, the most common location of breached protected health information was network servers, with email accounts the next most common location of breached data.

Location of breached protected health information in August 2026 data breaches

Data Breaches at HIPAA Regulated Entities

The HIPAA Breach Notification Rule requires HIPAA-covered entities to report data breaches to OCR and notify the affected individuals. Notifications must also be issued when there is a data breach at a business associate of a HIPAA-covered entity; however, it is ultimately the responsibility of each affected HIPAA-covered entity to ensure that notifications are issued. A covered entity may delegate the reporting requirements to the business associate that experienced the data breach or may choose to issue notifications themselves. The raw breach data on the OCR breach portal shows data breaches based on the reporting entity, not where the data breach occurred.

In August, healthcare providers reported 41 data breaches, business associates reported 8 breaches, and 3 breaches were reported by health plans. The pie charts below show where the breach actually occurred rather than the reporting entity to better reflect data breaches at business associates.

August 2026 data breaches at HIPAA regulated entities

Individuals affected by August 2026 data breaches at HIPAA-regulated entities

Geographical Distribution of Healthcare Data Breaches

In August, large healthcare data breaches were reported by HIPAA-regulated entities in 29 states. Texas was the worst affected with 7 large data breaches, with California and Florida taking joint second spot with 4 breaches each.

State Breaches State Breaches
Texas 7 Idaho 1
California 4 Indiana 1
Florida 4 Kansas 1
Illinois 3 Maine 1
New York 3 Michigan 1
Pennsylvania 3 Missouri 1
Tennessee 3 North Dakota 1
Hawaii 2 New Hampshire 1
Massachusetts 2 New Jersey 1
Minnesota 2 Ohio 1
Arkansas 1 Oklahoma 1
Arizona 1 South Carolina 1
Colorado 1 Vermont 1
Connecticut 1 West Virginia 1
Georgia 1

While only three HIPAA-regulated entities in Pennsylvania reported data breaches, the state ranked top in terms of affected individuals, with Texas taking second spot and Tennessee in third.

State Individuals Affected State Individuals Affected
Pennsylvania 4,121,776 Colorado 5,378
Texas 2,838,764 Maine 5,000
Tennessee 333,448 Kansas 4,649
New York 295,031 Arizona 3,000
Minnesota 208,201 Georgia 2,750
Massachusetts 206,100 North Dakota 1,750
Florida 79,588 Arkansas 1,500
California 69,251 Vermont 1,408
Hawaii 54,172 West Virginia 1,215
New Hampshire 49,540 Ohio 808
Connecticut 41,000 Idaho 553
Indiana 19,851 Michigan 501
Illinois 13,474 New Jersey 501
Missouri 11,927 South Carolina 501
Oklahoma 5,690

HIPAA Enforcement Activity in August 2026

OCR announced one enforcement activity in August to resolve noncompliance with the HIPAA Rules. Azul Vision, Inc., a California optometry and ophthalmology service provider, agreed to settle an alleged violation of the HIPAA Privacy Rule’s right of access for $50,000. A patient was not provided with timely access to her medical records. She filed a complaint with OCR after 3 months and finally received the records two years after the initial request was made. State Attorneys General may also impose penalties for HIPAA violations, although no HIPAA violation cases were announced in August.

About this Report

The HIPAA Journal monthly data breach reports are based on data obtained from the HHS Office for Civil Rights and have been combined with breach report data from other sources. The data breaches included in this report were reported in August 2026 but occurred weeks or months previously. The data was obtained from OCR on October 23, 2026. The figures in this report may increase or decrease as HIPAA-regulated entities complete their breach investigations, and those changes will be reflected in our healthcare data breach statistics page and our annual HIPAA data breach reports. Further information about HIPAA enforcement actions can be found in our HIPAA violations cases page.

The post August 2026 Healthcare Data Breach Report appeared first on The HIPAA Journal.
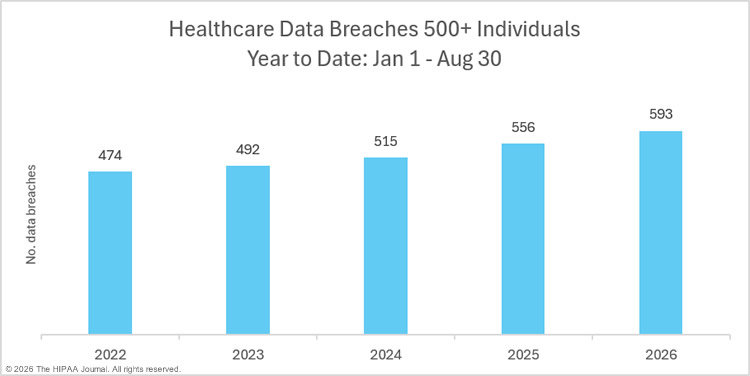
Lehigh Valley Health Network Pays $800K Penalty to Resolve HIPAA Violations

Lehigh Valley Health Network has agreed to settle alleged violations of the HIPAA Rules with the HHS’ Office for Civil Rights (OCR) and will pay an $800,000 financial penalty and adopt a corrective action plan to address identified areas of noncompliance. This is OCR’s 22nd investigation of a ransomware attack to result in a financial penalty for noncompliance with the HIPAA Rules.

OCR launched an investigation after receiving a breach report on May 15, 2026, from Lehigh Valley Health Network about a cybersecurity incident that exposed the protected health information (PHI) of 248,359 individuals. Lehigh Valley Health Network identified suspicious activity within its network in early February 2023 and later confirmed that ransomware was involved. The ALPHV/BlackCat ransomware group breached parts of its network, specifically IT systems related to Delta Medix, a company acquired by Lehigh Valley Health Network in 2021. The ransomware group exfiltrated files containing patient information and issued a ransom demand. The ransom was not paid, and the stolen data was leaked on the ransomware group’s dark web data leak site.

Data stolen and leaked in the incident included names, addresses, dates of birth, Social Security numbers, driver’s license numbers, financial information, diagnoses and conditions, lab results, medications, and treatment information. In addition, photographs of cancer patients receiving radiation oncology treatment were stolen in the incident and leaked online, including photographs of patients who were naked from the waist up. Lehigh Valley Health Network was sued over the data breach and settled the class action litigation for $65 million.

OCR’s investigation identified multiple potential violations of the HIPAA Rules, including two violations of the HIPAA Security Rule. Lehigh Valley Health Network was determined to have failed to conduct a comprehensive and accurate risk analysis to identify risks and vulnerabilities to electronic PHI, and failed to implement policies and procedures for regularly reviewing records of activity in information systems containing ePHI, such as audit logs, access reports, and security incident tracking reports. These failures led to the impermissible disclosure of the ePHI of 248,359 individuals, in violation of the HIPAA Privacy Rule.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

OCR also determined that Lehigh Valley Health Network failed to issue timely notifications to the affected individuals to alert them to the theft of their personal and health information and did not issue a timely notification to the Secretary of the Department of Health and Human Services, in violation of the HIPAA Breach Notification Rule. According to OCR, the intrusion was detected on February 4, 2026, and OCR was notified about the incident on May 15, 2026. The HHS Secretary must be notified about a breach of unsecured protected health information within 60 days of discovery of a breach. While OCR has not stated that it has an active enforcement initiative targeting noncompliance with the HIPAA Breach Notification Rule, a significant number of recent settlements have involved penalties for breach notification failures, including five of the 12 HIPAA settlements announced this year and five settlements last year.

Under the terms of the settlement agreement, in addition to the financial penalty, Lehigh Valley Health Network has agreed to adopt a corrective action plan that includes the requirements to conduct a comprehensive and accurate risk analysis, develop a risk management plan, review and revise its policies and procedures to ensure compliance with the HIPAA Rules, and develop training materials and provide training to its workforce on the HIPAA Rules relative to the performance of individuals’ job duties. OCR will monitor Lehigh Valley Health Network for compliance for a period of three years.

“Failure to conduct an accurate and thorough risk analysis and to undertake regular review of information system activity makes regulated entities attractive targets for cyberattacks,” said OCR Director Paula M. Stannard. “The best defense against cyberattacks is full implementation of the HIPAA Security Rule.”

The post Lehigh Valley Health Network Pays $800K Penalty to Resolve HIPAA Violations appeared first on The HIPAA Journal.