HIPAA Compliance News

Lehigh Valley Health Network Pays $800K Penalty to Resolve HIPAA Violations

Lehigh Valley Health Network has agreed to settle alleged violations of the HIPAA Rules with the HHS’ Office for Civil Rights (OCR) and will pay an $800,000 financial penalty and adopt a corrective action plan to address identified areas of noncompliance. This is OCR’s 22nd investigation of a ransomware attack to result in a financial penalty for noncompliance with the HIPAA Rules.

OCR launched an investigation after receiving a breach report on May 15, 2026, from Lehigh Valley Health Network about a cybersecurity incident that exposed the protected health information (PHI) of 248,359 individuals. Lehigh Valley Health Network identified suspicious activity within its network in early February 2023 and later confirmed that ransomware was involved. The ALPHV/BlackCat ransomware group breached parts of its network, specifically IT systems related to Delta Medix, a company acquired by Lehigh Valley Health Network in 2021. The ransomware group exfiltrated files containing patient information and issued a ransom demand. The ransom was not paid, and the stolen data was leaked on the ransomware group’s dark web data leak site.

Data stolen and leaked in the incident included names, addresses, dates of birth, Social Security numbers, driver’s license numbers, financial information, diagnoses and conditions, lab results, medications, and treatment information. In addition, photographs of cancer patients receiving radiation oncology treatment were stolen in the incident and leaked online, including photographs of patients who were naked from the waist up. Lehigh Valley Health Network was sued over the data breach and settled the class action litigation for $65 million.

OCR’s investigation identified multiple potential violations of the HIPAA Rules, including two violations of the HIPAA Security Rule. Lehigh Valley Health Network was determined to have failed to conduct a comprehensive and accurate risk analysis to identify risks and vulnerabilities to electronic PHI, and failed to implement policies and procedures for regularly reviewing records of activity in information systems containing ePHI, such as audit logs, access reports, and security incident tracking reports. These failures led to the impermissible disclosure of the ePHI of 248,359 individuals, in violation of the HIPAA Privacy Rule.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

OCR also determined that Lehigh Valley Health Network failed to issue timely notifications to the affected individuals to alert them to the theft of their personal and health information and did not issue a timely notification to the Secretary of the Department of Health and Human Services, in violation of the HIPAA Breach Notification Rule. According to OCR, the intrusion was detected on February 4, 2026, and OCR was notified about the incident on May 15, 2026. The HHS Secretary must be notified about a breach of unsecured protected health information within 60 days of discovery of a breach. While OCR has not stated that it has an active enforcement initiative targeting noncompliance with the HIPAA Breach Notification Rule, a significant number of recent settlements have involved penalties for breach notification failures, including five of the 12 HIPAA settlements announced this year and five settlements last year.

Under the terms of the settlement agreement, in addition to the financial penalty, Lehigh Valley Health Network has agreed to adopt a corrective action plan that includes the requirements to conduct a comprehensive and accurate risk analysis, develop a risk management plan, review and revise its policies and procedures to ensure compliance with the HIPAA Rules, and develop training materials and provide training to its workforce on the HIPAA Rules relative to the performance of individuals’ job duties. OCR will monitor Lehigh Valley Health Network for compliance for a period of three years.

“Failure to conduct an accurate and thorough risk analysis and to undertake regular review of information system activity makes regulated entities attractive targets for cyberattacks,” said OCR Director Paula M. Stannard. “The best defense against cyberattacks is full implementation of the HIPAA Security Rule.”

The post Lehigh Valley Health Network Pays $800K Penalty to Resolve HIPAA Violations appeared first on The HIPAA Journal.

HHS Confirms HIPAA Penalties Will Not Be Adjusted for Inflation This Year

This week, the Department of Health and Human Services (HHS) has confirmed via the Federal Register that it will not be applying an annual inflation multiplier in 2026 and will continue to use the civil monetary penalty levels for 2025.

The Federal Civil Penalties Inflation Adjustment Act of 1990, later amended by the Federal Civil Penalties Inflation Adjustment Act Improvement Act of 2015, requires federal agencies to apply annual increases to their penalty structures in line with inflation to ensure that civil monetary penalties continue to serve as an effective deterrent. The annual inflation multiplier is set by the Office of Management and Budget (OMB).

With respect to HIPAA, penalties were established by the HITECH Act of 2009, which set a maximum penalty of $1,500,000 per violation, per year. Were it not for the annual increases, the penalty amounts would become less effective over time. Currently, the maximum penalty for a HIPAA violation is $2,190,294, an increase of 46% from the level set by the HITECH Act 17 years ago.

The decision was not made by the HHS; rather, it is due to the lengthy government shutdown last Fall. As a result of that extended shutdown, the Bureau of Labor Statistics (BLS) was unable to produce the necessary data to calculate an inflation multiplier for 2026. The government shutdown occurred due to partisan deadlock in Congress, which resulted in a lapse in fiscal year 2026 appropriations ahead of the October 1 deadline. The Bureau of Labor Statistics was unable to produce the necessary Consumer Price Index (CPI-U) data for October 2025, which is required to calculate the 2026 cost-of-living adjustment multiplier. The OMB Director issued a memorandum in April 2026, informing federal agencies that the annual inflation adjustment for 2026 had been cancelled, and federal agencies should continue to use their current penalty structures.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The HHS Office for Civil Rights has been pushing Congress to increase the civil monetary penalties for HIPAA violations from the levels set by the HITECH Act. While the lack of an inflation adjustment this year may weaken the deterrent effect, the inflation multiplier for 2027 will take into account the cost-of-living increases from 2025 to 2027.

The post HHS Confirms HIPAA Penalties Will Not Be Adjusted for Inflation This Year appeared first on The HIPAA Journal.

Massachusetts AG Settles HIPAA & MassHealth Fraud Allegations with Transformative Healthcare

The Massachusetts Attorney General has agreed to settle alleged violations of the Health Insurance Portability and Accountability Act (HIPAA) and Massachusetts Data Security Law with the former medical transportation provider Transformative Healthcare, LLC, and its subsidiaries, Lifeline Ambulance Services, LLC and Lifeline Healthcare Solutions, LLC (Lifeline), and Fallon Service, LLC and Fallon Emergency Medical Services, LLC (Fallon). Lifeline and Fallon were acquired by another Massachusetts operator in 2022, when Transformative Healthcare ceased operations.

The settlement agreement also resolves allegations that Fallon and Lifeline upcoded claims to MassHealth by billing for more expensive levels of service than they provided, including billing for emergency services when nonemergency level services were provided, and submitting false claims for Advanced Life Support services when the services provided did not meet the criteria for Advanced Life Support services. Under the proposed consent judgment, the combined allegations have been resolved with a $1,000,000 financial penalty, which will be paid over five years.

The data security incident was first identified by Fallon on April 21, 2023. The forensic investigation confirmed that systems containing the data of Transformative Healthcare patients and employees were accessed by an unauthorized third party between February 17, 2023, and April 21, 2023, during an archiving process. During that time, the personal and protected health information of 750,116 Massachusetts residents was exposed and potentially stolen. The impacted data included names, contact information, dates of birth, driver’s license numbers, state identification numbers, Social Security numbers, medical information, and health insurance information.

The Massachusetts Attorney General launched an investigation into the data breach to assess compliance with the Massachusetts Consumer Protection Act, Massachusetts Data Security Law, and HIPAA. The fraud investigation was handled separately. The Massachusetts Attorney General determined that Transformative Healthcare had failed to maintain an appropriate written information security program, and concluded that Transformative Healthcare and Fallon violated the Massachusetts Data Security Regulations and HIPAA 45 CFR Part 164, Subpart A (General Provisions of HIPAA), Subpart C (Security Standards for the Protection of Electronic Protected Health Information of the HIPAA Security Rule), and Subpart E (Privacy of Individually Identifiable Health Information of the HIPAA Privacy Rule).

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

In addition to the financial penalty, the settlement requires Transformative Healthcare and Fallon to ensure compliance with the Massachusetts Consumer Protection Act, Data Breach Notification Law, Data Security Regulations, Dispositions and Destruction of Records Law, and the HIPAA Privacy and Security Rules, and includes the requirement to destroy personal information and protected health information within 45 days of the effective date of the consent judgment.

“Healthcare companies have a responsibility to protect the sensitive patient data they are entrusted with and to bill MassHealth only for the services they provide,” said Massachusetts Attorney General Andrea Joy Campbell. “My office will continue to hold companies accountable when they defraud MassHealth and put residents’ personal information at risk.”

The post Massachusetts AG Settles HIPAA & MassHealth Fraud Allegations with Transformative Healthcare appeared first on The HIPAA Journal.

Boston Children’s Health Physicians; XTIUM Settle Alleged HIPAA Violations for $2.7M

Boston Children’s Health Physicians (BCHP) and the managed IT service provider XTIUM have agreed to settle an investigation by the New York and Connecticut Attorneys General into a 2024 data breach that affected almost 890,000 individuals. The settlement includes a $4 million financial penalty, $2,700,000 of which will be paid to the states, and $1,300,000 has been suspended. New York will receive $2.1 million, and Connecticut will receive $540,000. The settlement agreement requires a series of measures to be implemented to improve cybersecurity. The suspended $1,300,000 will be payable ($1,040,000 to New York and $260,000 to Connecticut) if there is a failure to comply with the requirements of the settlement agreement.

The attorneys general launched an investigation in response to an August 2024 cybersecurity incident at XTIUM, a New York-based IT management company that provides network security services to BCHP and other companies. BCHP is a New York-based medical practice that provides medical services to young patients at 60 locations in New York and five in Connecticut.

At the time of the security incident, BCHP used two managed service providers for its IT functions, one of which involved the management and security of its active patient record system, which was unaffected. The second IT company, Axispoint Technology Solutions Group, Inc. (now XTIUM), was responsible for the management of other IT systems, but not security functions. The cybersecurity incident involved the IT systems managed by XTIUM.

In August 2024, XTIUM discovered that a threat actor had infiltrated its systems and those of 18 of its clients, including BCHP. XTIUM notified BCHP about the incident on September 6, 2024, and on September 7, 2024, BCHP performed a user password reset; however, it did not reset system or administrator passwords, and did not isolate the BCHP system from the internet. BCHP identified unauthorized activity within its own network on September 10, 2024, and isolated its systems from the internet. The incident was remediated, and systems were brought back online on September 13, 2024.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The forensic investigation determined that the threat actor exploited a remote access tool used by XTIUM and exfiltrated an unencrypted database containing patient billing records, which included the names of patients and guarantors, along with their contact information, dates of birth, Social Security numbers, driver’s license numbers, health insurance information, treatment information, and billing information. The data related to approximately 825,000 New York residents and 62,871 Connecticut residents, and included the Social Security numbers and/or driver’s license numbers of approximately 170,000 New York residents. The records of approximately 1,000 XTIUM employees were also compromised in the incident.

The investigation, led by the New York Attorney General, determined that XTIUM failed to implement reasonable safeguards to protect private information on its network. All recommended security settings for the remote access tool had not been implemented by XTIUM, and there was a lack of logging/monitoring for the remote access tool.

BCHP failed to enforce common standard security policies, and XTIUM did not request security policies; as such, it used a single shared administrative account with unrestricted access and unlimited privileges. Logging and monitoring were so poor that it was not possible to determine exactly how the attackers gained access, and it prevented meaningful analysis of the attack. After breaching BCHP systems, the attackers were able to compromise a further four unrestricted administrative accounts and gained access to BCHP’s entire system.

Security deficiencies included a lack of appropriate account permissions and restrictions, insufficient network segmentation, a failure to apply the principle of least privilege, and insufficient access controls, account monitoring, privileged account management, governance, and vendor assessments. Further, BCHP had undergone a third-party information security audit in 2023 that flagged a range of security issues; however, action was not taken to address the security gaps. For two years prior to the security incident, BCHP executives were aware that an archive containing over 1 million billing records was not encrypted. The unencrypted data was exfiltrated in the attack.

The New York Attorney General determined that there had been violations of the HIPAA Security Rule and New York Executive Law. In addition to the financial penalty, both entities are required to make improvements to their information security programs. Those measures include maintaining an accurate and up-to-date inventory of private information and ensuring the information is protected, implementing and maintaining reasonable authentication procedures for access to private information, implementing a logging and monitoring system, and enhancing threat response procedures.

“Institutions trusted with sensitive private health data have a critical responsibility to protect it from bad actors, said New York Attorney General Letitia James. “BCHP knew its data security features were inadequate but did not fix them, exposing the information of hundreds of thousands of New Yorkers to hackers. As a result of our investigation, we are holding BCHP accountable and ensuring they implement new measures to protect New Yorkers’ personal information.”

The post Boston Children’s Health Physicians; XTIUM Settle Alleged HIPAA Violations for $2.7M appeared first on The HIPAA Journal.

July 2026 Healthcare Data Breach Report

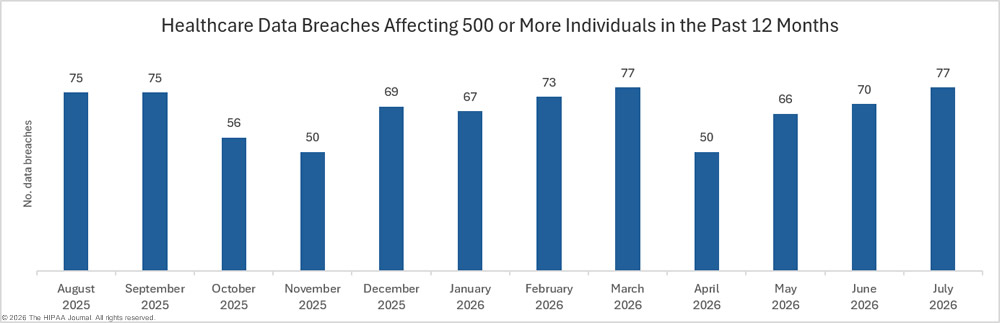
In July 2026, 77 healthcare data breaches affecting 500 or more individuals were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights. July was the third consecutive month in which large healthcare data breaches increased, with a month-over-month increase of 10%.

Large U.S. Healthcare data breaches in the past 12 months - July 2026

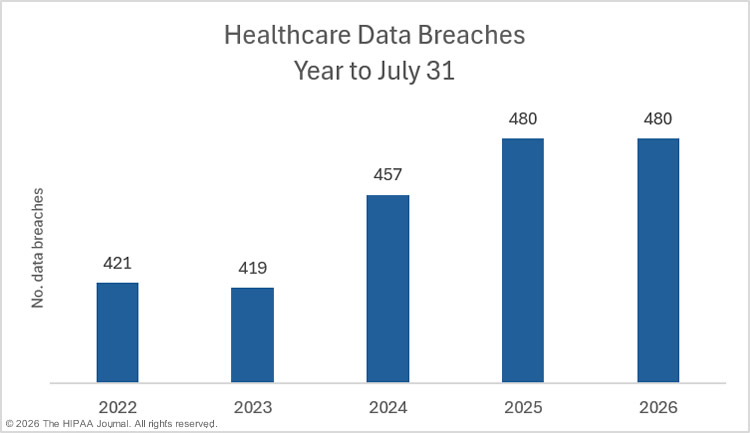
Last year was a record-breaking year for healthcare data breaches. The OCR data breach portal currently shows 806 large healthcare data breaches in 2025 – an increase of 8.6% from 2024. While 2026 was looking like there would be a fall in large healthcare data breaches, the year-to-date figures now suggest otherwise. The exact same number of data breaches are listed on the OCR data breach portal for January to July as this time in 2025, and it is likely that some breaches have yet to be added to the portal.

Year-to-date large healthcare data breaches - July 31, 2026

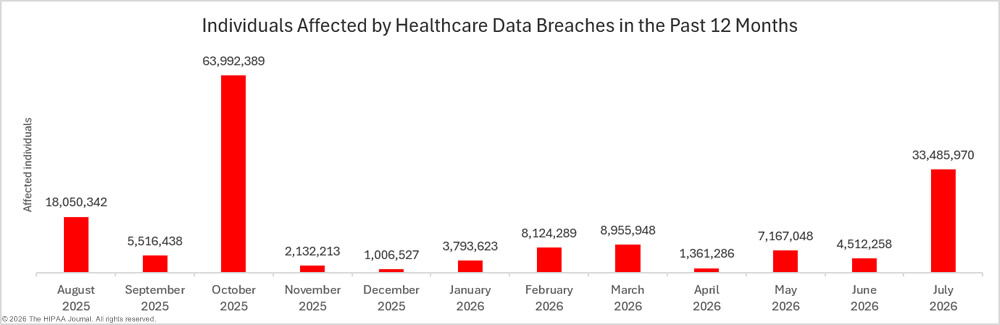
July was the worst month since October 2025 in terms of individuals affected by healthcare data breaches. Across the 77 large data breaches, the protected health information of at least 33,485,970 individuals was exposed or impermissibly disclosed – an increase of 642% from June 2026, and 154% higher than the 12-month average of 13.2 million individuals per month.

Individuals affected by large U.S. healthcare data breaches in the past 12 months - July 2026

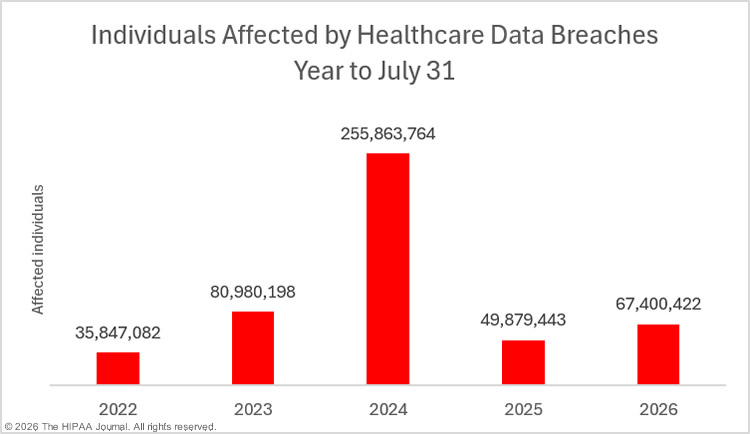
The year-to-date figures show an increase in breach severity year-over-year. Between January and July 2026, the protected health information of 67,400,422 individuals was exposed or impermissibly disclosed; an increase of 35.1% from this time last year.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

Year to date individuals affected by large U.S. healthcare data breaches - July 31, 2026

Biggest Healthcare Data Breaches in July 2026

In July, 23 security incidents were reported to OCR involving the protected health information of 10,000 or more individuals, including four very large data breaches that each affected more than 1 million individuals. One of the incidents was the 4th largest healthcare data breach of all time to be reported by a single HIPAA-regulated entity, affecting an estimated 15 million individuals. The four biggest healthcare data breaches in July affected more than 32 million individuals – more than 9% of the population of the United States.

The largest data breach occurred at DentaQuest, a Sun Life U.S-owned dental and vision benefits administrator, which fell victim to a cyberattack by the notorious data theft and extortion group ShinyHunters. In early June 2026, DentaQuest announced that it was investigating a cybersecurity incident involving a limited part of its computer network. The threat group had access to its network for around 3 days in May 2026. ShinyHunters claimed responsibility and said 234 GB of data was exfiltrated in the incident, then started leaking the stolen data as it failed to reach an agreement with DentaQuest on a ransom payment. The leak included around 2.6 million unique email addresses, and the breach was reported to OCR as affecting an estimated 15 million individuals. That total may increase as the investigation progresses.

The next three largest data breaches all occurred at business associates of HIPAA-covered entities. Aesto Health, a healthcare technology company that offers secure data migration, legacy data archiving, and electronic health record (EHR) exchanges, experienced a hacking incident that affected at least 39 of its healthcare clients and involved the protected health information of more than 9.5 million individuals. The incident occurred in December 2025 and involved unauthorized access to its AWS environment. No threat group appears to have claimed responsibility.

Unlimited Technology Systems, an Ohio-based revenue cycle management and practice management software company, discovered its network had been accessed by an unauthorized third party for five days in October 2025, and potentially obtained the protected health information of more than 3.8 million individuals. A similar-sized data breach was reported by CareCloud, a provider of cloud-based and AI-powered EHR, RCM, PM, and clinical documentation solutions, which discovered that a threat actor accessed its AWS environment over 6 days in March 2026, and likely exfiltrated databases containing the protected health information of more than 3.7 million individuals. As with the incident at Unlimited Technology Systems, no threat group appears to have claimed responsibility.

Regulated Entity State Covered Entity Type Individuals Affected Cause of Breach
DentaQuest, LLC MA Health Plan 15,000,000 Hacking incident (ShinyHunters data theft and extortion group)
Aesto, LLC AL Business Associate 9,540,683 Hacking incident
Unlimited Technology Systems, LLC OH Business Associate 3,803,750 Hacking incident
CareCloud, Inc. NJ Business Associate 3,756,469 Hacking incident
Lifespan Physician Group of Massachusetts, Inc. d/b/a Brown Health Medical Group-MA MA Healthcare Provider 311,760 Hacking incident
One Medical Group, Inc. CA Healthcare Provider 153,174 Hacking incident (ShinyHunters data theft and extortion group)
Madera Community Hospital CA Healthcare Provider 150,810 Hacking incident
zHealth, Inc. CA Business Associate 118,563 Ransomware attack (Kazu ransomware group)
Boundary Regional Community Health Center dba Kaniksu Community Health ID Healthcare Provider 88,000 Hacking incident at business associate Aesto (see above)
A-O-M-S, P.L.L.C. d/b/a Arkansas Oral & Maxillofacial Surgeons AR Healthcare Provider 64,831 Hacking incident (PEAR data theft and extortion group)
Casper Orthopedic Associates, PC DC Healthcare Provider 56,197 Hacking incident
Heart Care Centers of Illinois IL Healthcare Provider 52,562 Email phishing incident
Sunshine Health FL Health Plan 41,569 Vishing (voice phishing) incident
Brookhaven ENT Allergy and Facial Surgery MS Healthcare Provider 30,403 Hacking incident at vendor CloudCare
Alta Orthopaedics Medical Group, Inc. PA Healthcare Provider 24,496 Ransomware attack (INC Ransom ransomware group)
Nephrology Associates, M.D., P.A. KS Healthcare Provider 24,088 Ransomware attack (The Gentlemen ransomware group)
Jeffrey David Reuben, M.D. TX Healthcare Provider 17,017 Hacking incident
Regional Center of Orange County CA Business Associate 16,545 Improper disposal of paper records by janitorial service provider
ZenPatient, Inc. CA Healthcare Provider 15,749 Hacking incident (data theft confirmed)
Cornerstone Behavioral Healthcare ME Healthcare Provider 14,830 Ransomware attack (Group unknown)
Resource Center of Dallas, Inc. TX Healthcare Provider 12,490 Hacking incident
Agave Dental-Floresville TX Healthcare Provider 11,790 Ransomware attack (The Gentlemen ransomware group)
Any-Time Home Care, Inc. NY Healthcare Provider 11,753 Hacking/IT Incident

When the number of affected individuals is not known by the HIPAA Breach Notification Rule reporting deadline, OCR should be provided with an estimate. The total can then be amended when the data review is completed. It is common for regulated entities to provide an “estimate” of 500 or 501 individuals, as appears to be the case with seven of the breaches reported in July.

Regulated Entity State Covered Entity Type Individuals Affected Type of Breach
Open Door Health Center of Illinois WA Healthcare Provider 501 Network server hacking incident (INC Ransom ransomware group)
Champaign-Urbana Public Health District IL Healthcare Provider 501 Network server hacking incident
The Medical Imaging Partnership dba Precision Imaging Center FL Healthcare Provider 501 Network server hacking incident
Interim HealthCare of Oklahoma City, Inc. OK Healthcare Provider 500 Email/network server hacking incident (Genesis & Anubis ransomware groups)
Pennsylvania Dermatology Partners MD Healthcare Provider 500 Network server hacking incident
Alpine Agency of the Midlands, LLC SC Business Associate 500 Email hacking incident
Family Medical Associates of Raleigh, PA NC Healthcare Provider 500 Network server hacking incident

Causes of June 2026 Healthcare Data Breaches

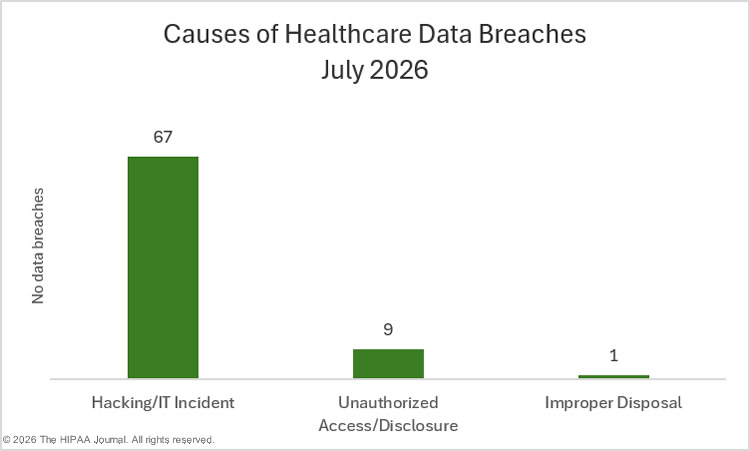
A majority of the data breaches reported in July were due to hacking and other IT-related incidents, including all but one of the 23 data breaches affecting 10,000 or more individuals. In July, 67 of the month’s data breaches (87%) were reported as hacking/IT-related incidents, involving the protected health information of 33,446,371 of the month’s affected individuals (99.9%). The average breach size was 499,200 individuals, and the median breach size was 4,851 individuals.

Causes of July 2026 large healthcare data breaches

Between January 1 and July 31, 414 hacking/IT incidents were reported – 86% of all data breaches – and they accounted for 97.8% of all affected individuals (65,89,1098 individuals). While the same number of healthcare data breaches have been reported as this time last year, hacking/IT incidents have increased by 7.3% year-over-year.

In July 2026, 9 of the month’s data breaches were reported as unauthorized access/disclosure incidents (11.7% of incidents), involving the protected health information of 23,054 of the month’s affected individuals (0.07%). The average breach size was 2,562 individuals, and the median breach size was 1,680 individuals. Between January 1 and July 31, 62 unauthorized access/disclosure incidents were reported – 12.9% of all data breaches – and they accounted for 2.2% of all affected individuals (1,490,420 individuals). Unauthorized access/disclosure incidents have decreased by 27% year-over-year.

In July 2026, only one of the month’s data breaches was due to the improper disposal of protected health information (1.3%), and that incident affected 16,545 individuals (0.05%). Between January 1 and July 31, 2 improper disposal incidents were reported – 2.6% of all data breaches – and they accounted for 0.03% of all affected individuals (17,545 individuals). Improper disposal incidents have doubled year-over-year.

No loss/theft incidents were reported in July. Between January 1 and July 31, only 2 loss/theft incidents were reported – 0.4% of all data breaches – and they accounted for 0.002% of all affected individuals (1,359 individuals). Loss/theft incidents have decreased by 400% year-over-year.

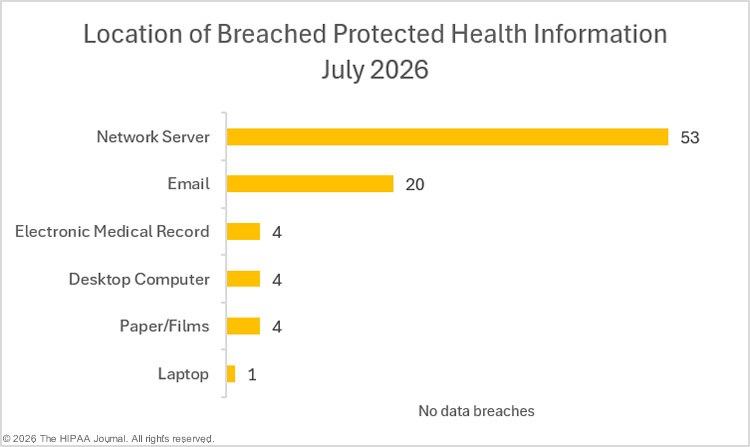
Location of Breached Protected Health Information

In July, network servers were the most common location of breached protected health information, followed by email systems.

Location of breached PHI in July 2026 healthcare data breaches

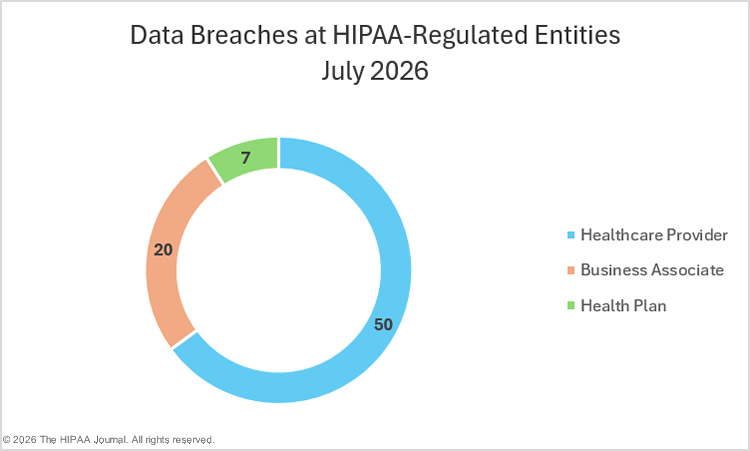
Data Breaches at HIPAA Regulated Entities

The HIPAA Breach Notification Rule requires HIPAA-covered entities to report data breaches to OCR and notify the affected individuals. Notifications must also be issued when there is a data breach at a business associate of a HIPAA-covered entity; however, it is ultimately the responsibility of each affected HIPAA-covered entity to ensure that notifications are issued. A covered entity may delegate the reporting requirements to the business associate that experienced the data breach, or may choose to issue notifications themselves. The raw breach data on the OCR breach portal shows data breaches based on the reporting entity, not where the data breach occurred.

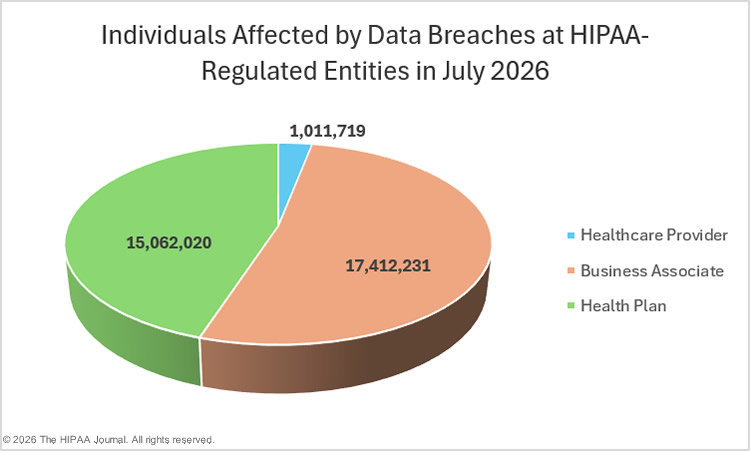
In July, healthcare providers reported 56 data breaches, business associates reported 12 breaches, and 9 breaches were reported by health plans. The pie charts below show where the breach actually occurred rather than the reporting entity to better reflect data breaches at business associates.

July 2026 large U.S. healthcare data breaches - regulated entities

individuals affected by large U.S. healthcare data breaches - July 2026

Geographical Distribution of Healthcare Data Breaches

In July, large healthcare data breaches were reported to OCR by HIPAA-regulated entities in 30 U.S. states and the District of Columbia. Texas was the worst affected state with 11 large data breaches, closely followed by California with nine.

State Breaches State Breaches
Texas 11 Arizona 1
California 9 Connecticut 1
Florida 5 District of Columbia 1
Massachusetts 5 Idaho 1
Illinois 4 Indiana 1
Minnesota 4 Iowa 1
New York 4 Kansas 1
North Carolina 4 Maine 1
Tennessee 3 Maryland 1
Wisconsin 3 Mississippi 1
Arkansas 2 Oklahoma 1
Michigan 2 Pennsylvania 1
New Jersey 2 South Carolina 1
Ohio 2 Virginia 1
Alabama 1 Washington 1

Massachusetts topped the list in terms of affected individuals, with more than 18 million individuals affected across its five data breaches, followed by Alabama, which experienced one data breach that affected more than 9.5 million individuals across the United States.

State Individuals Affected State Individuals Affected
Massachusetts 15,317,249 Wisconsin 18,549
Alabama 9,540,683 Minnesota 15,398
Ohio 3,805,854 Maine 14,830
New Jersey 3,759,869 Virginia 9,909
California 478,468 Tennessee 9,835
Idaho 88,000 Michigan 5,707
Texas 71,136 North Carolina 4,493
Arkansas 65,520 West Virginia 2,173
Florida 60,164 Connecticut 1,556
Illinois 56,638 Indiana 1,530
District of Columbia 56,197 Arizona 800
Mississippi 30,403 Iowa 746
Pennsylvania 24,496 Washington 501
Kansas 24,088 Maryland 500
New York 19,678 Oklahoma 500

HIPAA Enforcement Activity in July 2026

OCR announced one HIPAA enforcement action in July to resolve alleged violations of the HIPAA Rules. OSF Healthcare System is a Peoria, Illinois-based integrated health system that serves patients at 174 locations in Illinois and Michigan, including 16 hospitals. OSF Healthcare System was investigated by OCR in response to a reported cybersecurity incident that exposed the protected health information of 53,907 individuals. A ransomware group breached its network, stole patient data, encrypted files, and demanded payment to delete the stolen data and unlock the encrypted files. The attack was discovered by OSF Healthcare System in April 2021.

OCR’s investigators determined OSF Healthcare System failed to conduct a HIPAA-compliant risk analysis, there was an impermissible disclosure of the ePHI of 53,907 individuals, and a failure to provide timely notifications to OCR and the affected individuals. The alleged HIPAA violations were settled, with OSF Healthcare System and its Affiliated Covered Entities agreeing to pay a $552,250 financial penalty and adopt a corrective action plan to address the identified areas of noncompliance.

This was another enforcement action under OCR’s risk analysis enforcement initiative. While OCR has not announced a specific enforcement initiative targeting noncompliance with the HIPAA Breach Notification Rule, OCR appears to be looking closely at HIPAA Breach Notification Rule compliance. Since the start of 2025, eight HIPAA settlements have included penalties for Breach Notification Rule failures.

About this Report

The HIPAA Journal monthly data breach reports are based on data obtained from the HHS Office for Civil Rights and have been combined with breach report data from other sources. The data breaches included in this report were reported in July 2026 but occurred weeks or months previously. The data was obtained from OCR on October 10, 2026. The figures in this report may increase or decrease as HIPAA-regulated entities complete their breach investigations, and those changes will be reflected in our healthcare data breach statistics page and our annual HIPAA data breach reports. Further information about HIPAA enforcement actions can be found in our HIPAA violations cases page.

The post July 2026 Healthcare Data Breach Report appeared first on The HIPAA Journal.

H1 2026 Healthcare Data Breach Report

There has been a 5.9% decline in healthcare breaches compared to H1 2025. Between January 1 and June 30, 2026, 397 data breaches affecting 500 or more individuals were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights – the lowest H1 total since 2023. While the year-over-year reduction in healthcare data breaches is a step in the right direction, healthcare data breaches continue to be reported in high numbers. In the first six months of the year, large healthcare data breaches were reported at a rate of more than 2.2 per day.
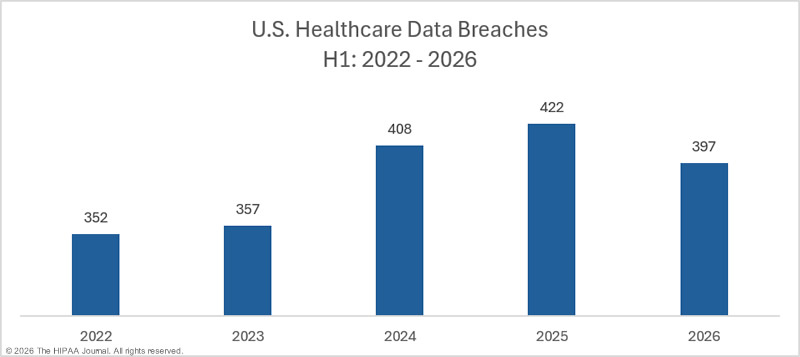
H1, 2026 Healthcare data breaches

Across the 397 reported data breaches, the protected health information of 33.77 million individuals was exposed or impermissibly disclosed. That represents a 22.6% reduction in affected individuals compared to H1 2025, and it is the lowest number of affected individuals in H1 since 2023.
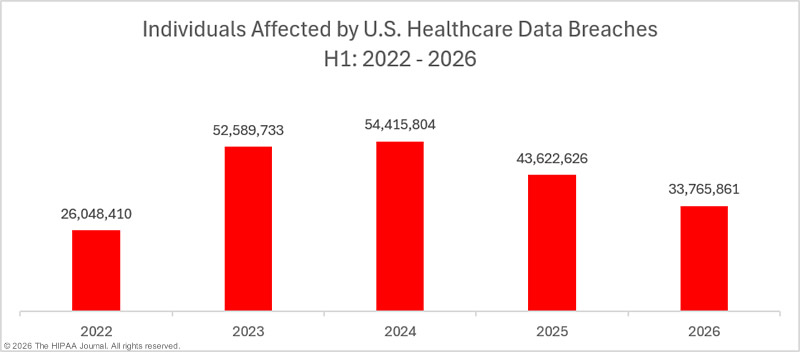
H1 2026 healthcare data breaches: individuals affected

If data breaches continue to be reported at a similar rate in the second half of the year, the end-of-year healthcare data breach total is likely to be lower than 2025, which was a record-breaking year with 804 data breaches currently listed on the OCR breach portal for 2025. The current total also suggests that this year could see a major reduction in affected individuals, as more than 140 million individuals were affected in 2025. That said, several very large data breaches have yet to be added to the OCR breach portal for this year.

The Biggest Healthcare Data Breaches in H1 2026

In the first half of the year, nine healthcare data breaches were reported that affected more than 1 million individuals, the largest breach of which affected more than 5.8 million individuals. All but two of the top twenty data breaches were due to hacking incidents or ransomware attacks. The two non-hacking breaches were unauthorized access/disclosure incidents, and both occurred at state departments of human services.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

Rank Regulated Entity State Covered Entity Type Individuals Affected Type of Breach
1 Lumexa Imaging NC Healthcare Provider 5,830,949 Hacking Incident
2 TriZetto Provider Solutions MO Business Associate 3,433,965 Hacking Incident
3 QualDerm Partners, LLC TN Healthcare Provider 2,951,318 Hacking Incident
4 Nacogdoches Memorial Hospital TX Healthcare Provider 2,507,073 Hacking Incident
5 Navia Benefit Solutions, Inc. WA Business Associate 2,151,330 Hacking Incident
6 Insightin Health, Inc. MD Business Associate 1,949,534 Hacking Incident
7 New York City Health and Hospitals Corporation NY Healthcare Provider 1,800,000 Hacking Incident
8 Xsolis, Inc. TN Business Associate 1,396,519 Hacking Incident
9 MCBS, LLC GA Business Associate 1,261,464 Hacking Incident
10 OpenLoop Health, Inc. IA Business Associate 716,000 Hacking Incident
11 Illinois Department of Human Services IL Health Plan 705,017 Unauthorized Disclosure Incident
12 ApolloMD Business Services, LLC GA Business Associate 626,540 Hacking Incident (Ransomware)
13 Erie Family Health Centers IL Healthcare Provider 570,000 Hacking Incident
14 Centers Lab NJ LLC NJ Healthcare Provider 542,377 Hacking Incident
15 Networking Technology, Inc. (RXNT) NC Business Associate 353,844 Hacking Incident
16 Minnesota Department of Human Services MN Health Plan 303,965 Unauthorized Access Incident
17 North Texas Behavioral Health Authority TX Healthcare Provider 285,086 Hacking Incident
18 Florida Physician Specialists FL Healthcare Provider 276,498 Hacking Incident
19 Radiology Associates of Richmond VA Healthcare Provider 266,183 Hacking Incident
20 Anatomic and Clinical Laboratory Associates, P.C. TN Healthcare Provider 169,626 Hacking Incident

The majority of the data breaches reported in H1 2026 were relatively small, affecting fewer than 10,000 individuals. Currently, 37 healthcare data breaches are listed as affecting 500 or 501 individuals. These are commonly used placeholder figures when data reviews are incomplete by the breach reporting deadline. The majority of those 37 data breaches are likely to see the totals increased, potentially significantly. The Change Healthcare data breach in 2024 was initially reported to OCR as affecting at least 500 individuals but was subsequently increased to 192.7 million individuals!

Scale of Breach – Affected Individuals Data Breaches
Over 1,000,000 9
100,000 – 999,999 21
10,000 – 99,999 102
1000 – 9,999 175
Under 1000 90

Causes of H1 2026 Healthcare Data Breaches

While the number of large healthcare data breaches has fallen year-over-year, the lower H1 figures this year are due to fewer unauthorized access/disclosure and loss/theft incidents, rather than hacking/IT incidents, which increased for the third consecutive year.
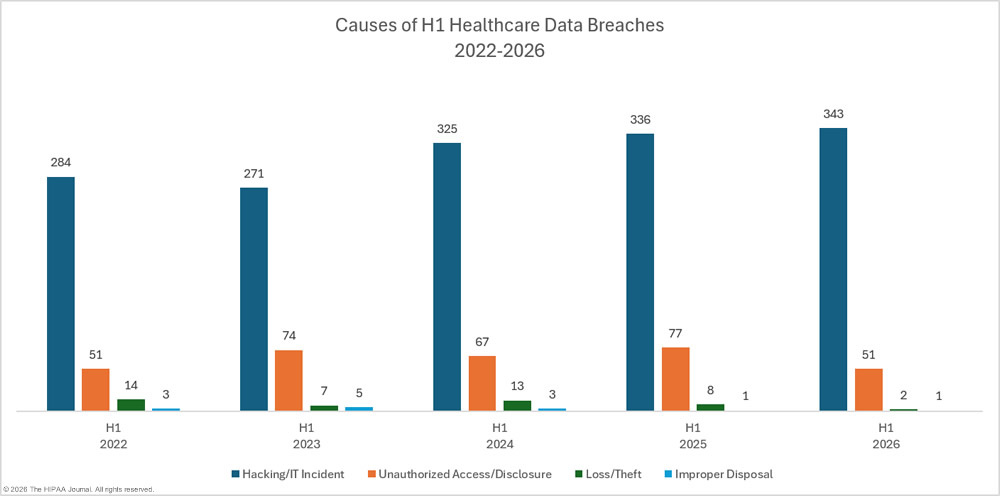
H1 Healthcare data breach causes 2022-2026

H1 2026 Hacking/IT Incidents

Hacking/IT incidents remain the leading cause of healthcare data breaches and increased again in 2026. Ransomware groups continue to attack the healthcare sector, and there has been an increasing trend of data theft and extortion incidents, where data is stolen and threats are issued to publish the stolen data, but files are not encrypted.

As also observed by the Identity Theft Resource Center, there has been a growing trend of breached entities failing to disclose the nature of data breaches, including the cause, whether ransomware was involved, and, concerningly, if data was stolen in the incident. The lack of a breach cause makes it difficult to assess trends, while the failure to disclose whether data has been stolen makes it difficult for individuals to gauge the level of risk they face.

In H1, 343 hacking/IT incidents were reported, affecting an average of 94,167 individuals (median breach size: 4,800 individuals). Hacking/IT incidents have increased by 2.1% year-over-year increase in hacking/IT incidents, although the number of affected individuals has reduced by 14.7% year-over-year.
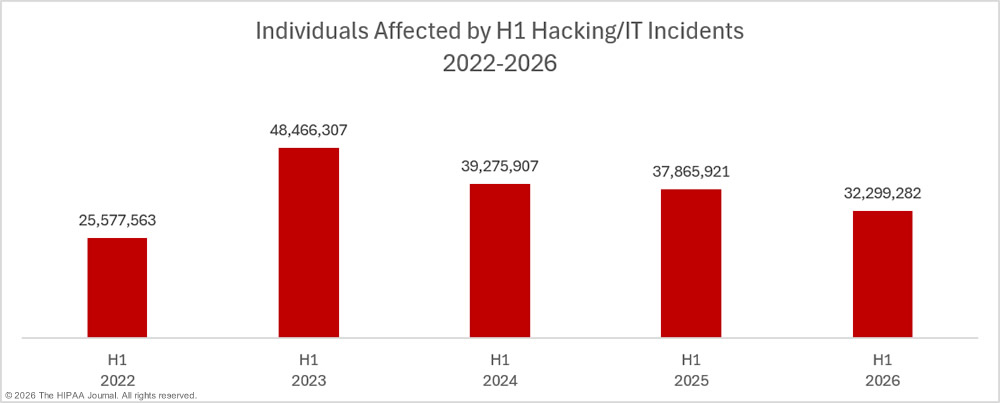
H1 2026 individuals affected by healthcare hacking/IT incidents

H1 2026 Unauthorized Access/Disclosure Incidents

Unauthorized access and disclosure incidents were the second leading cause of healthcare data breaches in H1 2026. These incidents include any unauthorized access to and disclosure of patient records that are not hacking- or IT-related. They include snooping incidents by insiders, misdirected emails and mailings, and unauthorized data sharing between HIPAA-regulated entities and third parties.

These incidents tend to affect far fewer individuals than hacking and IT incidents, although not always. Incidents involving website tracking tools such as pixels, for example, can affect millions of individuals. The two largest unauthorized access/disclosure incidents made it into the top 20 largest breaches of the first half of the year and occurred at the Illinois Department of Human Services and Minnesota Department of Human Services. The former involved data uploaded to a website for internal use that was accessible via the public internet, and the latter involved a user associated with an authorized healthcare provider accessing data without authorization.

In H1, 51 unauthorized access/disclosure incidents were reported, affecting an average of 28,710 individuals (median breach size: 2,315 individuals).  That represents a 3.8% year-over-year decline in unauthorized access/disclosure incidents, and a 74.2% decline in affected individuals.
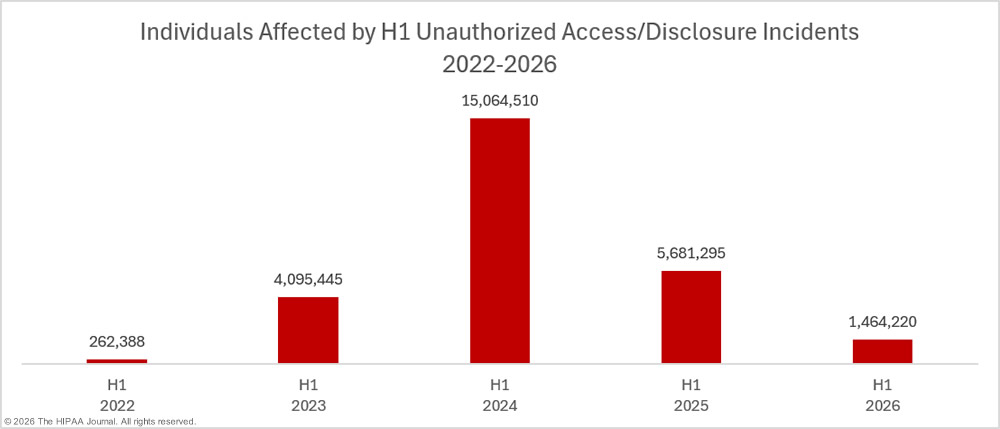
H1 2026 individuals affected by healthcare unauthorized access/disclosure

H1 2026 Loss/Theft Incidents

Loss and theft of electronic devices containing protected health information and paper records used to be a leading cause of data breaches; however, the adoption of digital records, data encryption, and cloud storage of protected health information has helped reduce these incidents. In H1 2026, only two such incidents were reported – one loss and one theft incident, both involving a relatively small number of paper records. That equates to a 75% year-over-year reduction in data breaches, and a 96.7% reduction in affected individuals.
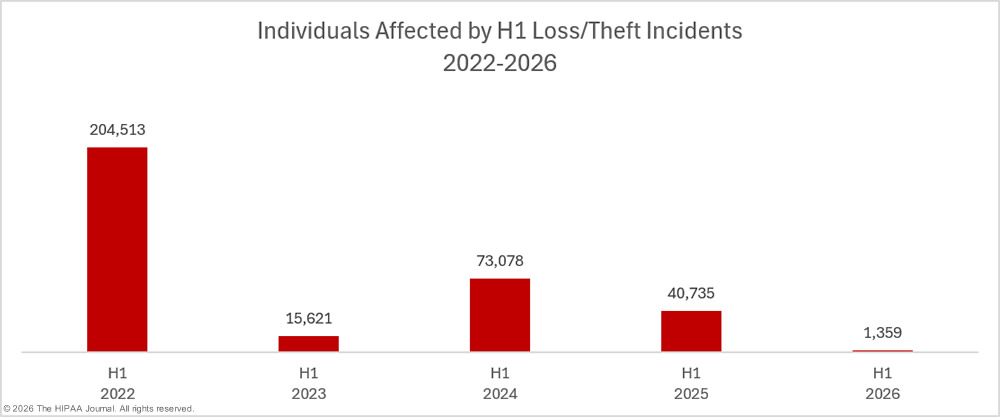
H1 2026 individuals affected by healthcare unauthorized loss/theft incidents

H1, 2026 Improper Disposal Incidents

Improper disposal incidents are rarely reported, and when they are, they almost always involve paper records inadvertently disposed of with regular trash. Only one such incident was reported by a HIPAA-regulated entity in H1 2026 – a relatively small data breach affecting an estimated 1,000 individuals. A single improper disposal incident was also reported in H1 2025, althopugh the number of affected individuals has fallen by 97% year-over-year.
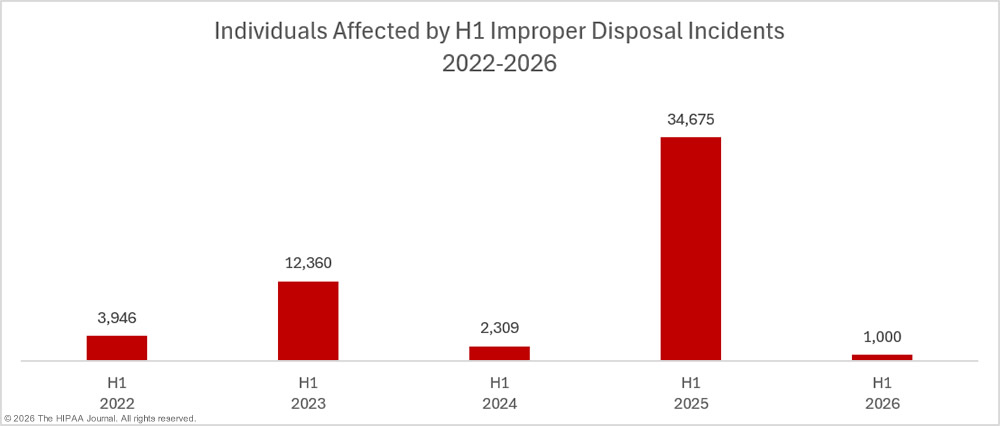
H1 2026 individuals affected by healthcare unauthorized improper disposal incidents

Data Breaches at HIPAA Regulated Entities

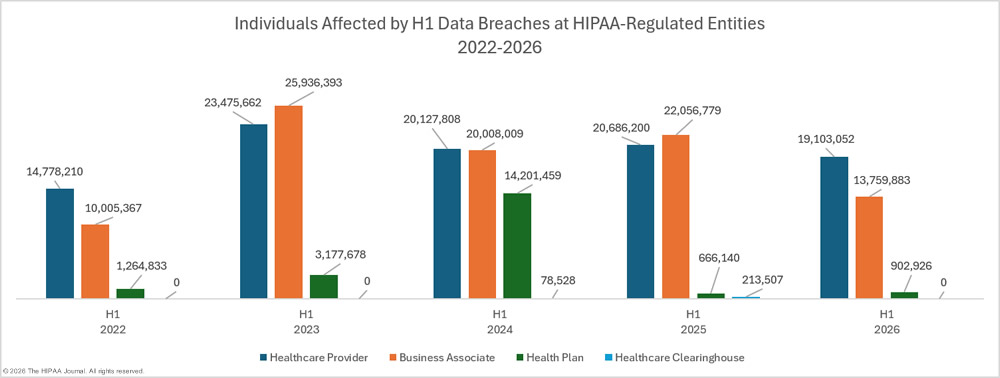
Healthcare providers were the worst affected HIPAA-regulated entities in H1 2026 (290 data breaches), followed by business associates (59 data breaches), and health plans (48 data breaches). Healthcare clearinghouses survived the first 6 months of the year without any data breaches. The same order applies in terms of individuals affected by those breaches, with healthcare providers topping the list (19,701,297 individuals), followed by business associates (12,505,090 individuals), and health plans (1,559,474 individuals).

Those figures do not tell the full story, as when a data breach occurs at a business associate, it is not always the business associate that reports the data breach. When a data breach occurs at a business associate, the business associate must notify each affected covered entity, and the covered entity may delegate the reporting and notification requirements to the business associate or may choose to report the data breach and/or send notification letters themselves. If a breach occurs at a business associate, some affected covered entities may delegate the reporting and notification responsibilities to the business associates while others may not. As such, business associate data breaches are often underrepresented in the raw breach data.

The charts below are based on where the data breach occurred, rather than the reporting entity. While the same order applies to both data breaches and affected individuals, almost 100 more breaches occurred at business associates than the raw data suggests.
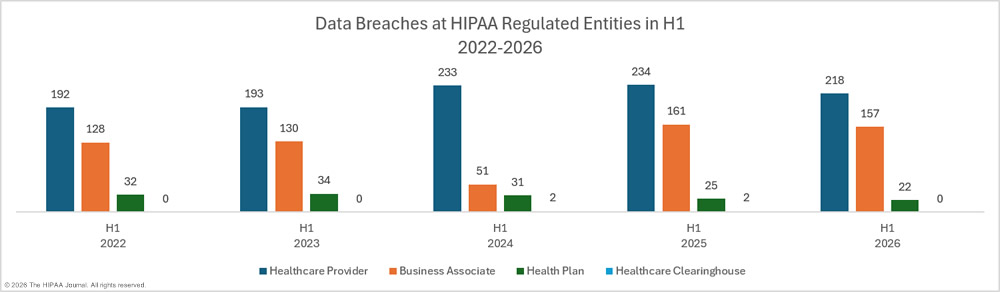
H1 2026 healthcare data breaches at HIPAA-regulated entities

H1 2026 healthcare data breaches at HIPAA-regulated entities - individuals affected

Based on the adjusted data, the average size of a data breach at a healthcare provider (87,629 individuals) and a business associate (87,643 individuals) was virtually identical, although the median size of a data breach at a healthcare provider (6,323 individuals) is twice that of a business associate (3,086 individuals). In H1 2026, health plan breaches were less severe. The average breach size was less than half the size at other entities at 41,042 individuals, and the median breach size was 2,871 individuals.

Location of Breached Protected Health Information

Given the high number of hacking incidents, it is unsurprising that the most common location of breached protected health information is network servers, as has been the case for several years. Email remains a common location of breached healthcare data due to a relatively high prevalence of phishing and social engineering incidents. While not infallible, multifactor authentication would have prevented many of these data breaches.

A small but significant number of healthcare data breaches involved paper records, although the number of incidents involving physical records is falling. Breaches of protected health information in “other” locations – including the cloud – are on the rise.  Widespread adoption of encryption and use of the cloud have helped to drastically reduce the number of loss and theft incidents.
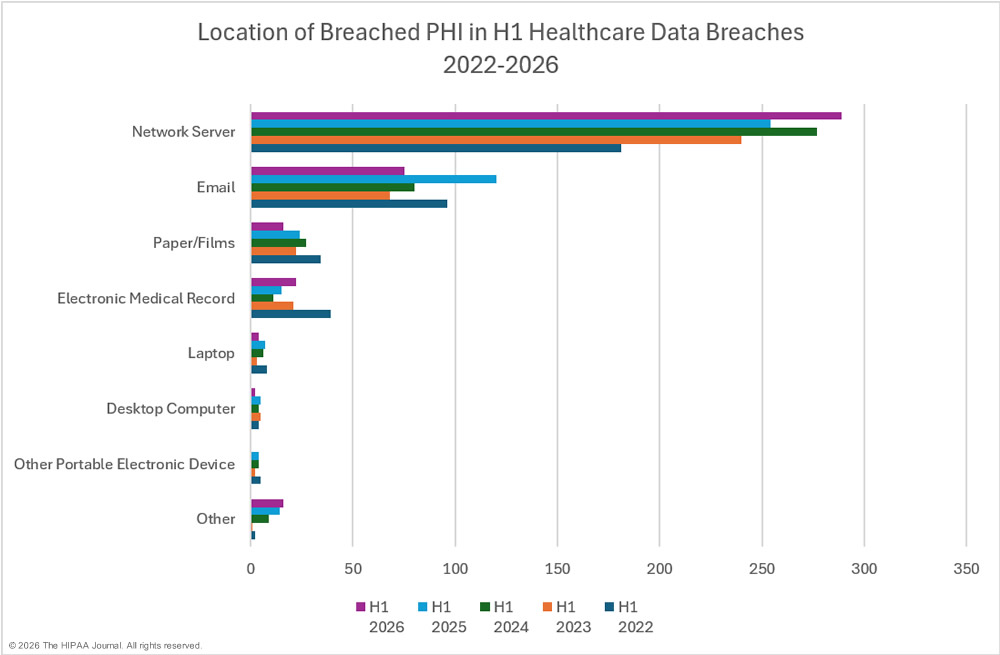
H1 2026 healthcare data breaches: location of breached protected health information

Geographic Distribution of Healthcare Data Breaches

In H1 2026, large healthcare data breaches were reported by HIPAA-regulated entities in 44 U.S. states, the District of Columbia, and Puerto Rico. The only states to escape the first half of the year unscathed were Hawaii, Montana, New Mexico, North Dakota, South Dakota, and Wyoming.

As a general rule, the states with the biggest populations experience the most data breaches, and vice versa for the states with the fewest number of breaches. California, Texas, Florida, and New York are the most heavily populated states in that order, and the same order applies in H1 2026 in terms of data breaches.

Rank State Data Breaches State Individuals Affected
1 California 38 North Carolina 6,358,110
2 Texas 36 Tennessee 4,635,531
3 Florida 24 Missouri 3,468,743
4 New York 20 Texas 3,188,111
5 Illinois 16 Washington 2,270,117
6 Michigan 15 New York 2,113,172
7 North Carolina 14 Georgia 2,005,142
8 Pennsylvania 13 Maryland 1,968,198
9 Washington 13 Illinois 1,756,341
10 Massachusetts 12 Florida 846,997
11 Colorado 11 Iowa 767,730
12 Tennessee 11 New Jersey 702,065
13 Virginia 11 Minnesota 486,202
14 Minnesota 10 Virginia 458,060
15 Ohio 10 California 430,336
16 Georgia 9 Colorado 324,483
17 Indiana 9 South Carolina 318,963
18 Kentucky 9 Pennsylvania 213,188
19 Maryland 9 Michigan 207,522
20 New Jersey 9 Ohio 139,151
21 Oklahoma 9 Connecticut 133,735
22 South Carolina 8 Puerto Rico 116,236
23 Alabama 7 Alabama 103,406
24 Connecticut 7 Kentucky 89,363
25 Missouri 7 Utah 82,335
26 Iowa 6 Arizona 76,546
27 Oregon 6 Idaho 66,625
28 Utah 6 Massachusetts 66,382
29 Idaho 5 Mississippi 60,133
30 Kansas 5 Indiana 49,271
31 Maine 5 Maine 45,932
32 Louisiana 4 Kansas 40,760
33 Arizona 3 Louisiana 37,963
34 District of Columbia 3 Nevada 37,796
35 Arkansas 2 Nebraska 26,937
36 Mississippi 2 District of Columbia 21,481
37 Puerto Rico 2 Oklahoma 18,392
38 West Virginia 2 Oregon 10,278
39 Wisconsin 2 Vermont 5,892
40 Alaska 1 Arkansas 5,800
41 Delaware 1 Rhode Island 5,630
42 Nebraska 1 Wisconsin 2,654
43 Nevada 1 West Virginia 1,500
44 New Hampshire 1 New Hampshire 1,221
45 Rhode Island 1 Delaware 908
46 Vermont 1 Alaska 523

HIPAA Enforcement Activity in H1 2026

OCR has increased the number of penalties imposed for HIPAA violations in recent years, although financial penalties are still relatively rare. OCR investigates all data breaches affecting 500 or more individuals, and when potential HIPAA violations are identified, they are typically resolved through voluntary compliance or by providing technical assistance.

Financial penalties are typically reserved for egregious or particularly impactful HIPAA violations, when there has been a history of noncompliance, and when OCR has an enforcement initiative targeting a specific aspect of the HIPAA regulations. Currently, OCR has two main enforcement initiatives, one targeting noncompliance with the HIPAA Right of Access of the HIPAA Privacy Rule, and another targeting noncompliance with the risk analysis implementation specification of the HIPAA Security Rule.

The HIPAA Right of Access enforcement initiative has been active since late 2019 and has resulted in more than 55 financial penalties. The risk analysis enforcement initiative is more recent and was formally launched in October 2024 in response to widespread noncompliance with this specific security rule provision and its importance for cybersecurity. To date, OCR has imposed 14 financial penalties under this initiative. The risk analysis enforcement initiative has been expanded this year to include risk management. In addition to demonstrating that a HIPAA-compliant risk analysis has been conducted, OCR requires evidence that the identified risks have been properly managed and reduced to a low and acceptable level in a reasonable time frame.

Between January 1 and June 30, 2026, OCR announced seven settlements to resolve alleged violations of the HIPAA Rules, all seven of which included a financial penalty for a risk analysis violation. While OCR has not announced a specific initiative targeting noncompliance with the HIPAA Breach Notification Rule, two of the seven penalties this year included a fine for breach notification failures. Five of the fourteen penalties imposed in 2025 also included penalties for breach notification failures, which suggests OCR is paying close attention to the time taken to issue breach notifications to OCR, the affected individuals, and the media.

H1 2026 HIPAA Settlements and Civil Monetary Penalties

Covered Entity Type of Entity Amount Settlement / Civil Monetary Penalty Reason
Spencer Gifts LLC Flexible Benefits and Welfare Benefit Plans Health Plan $450,000 Settlement Risk analysis failure; failure to implement Privacy, Security, and Breach Notification Rule policies and procedures.
Regional Women’s Health Group (Axia Women’s Health) Healthcare Provider $320,000 Settlement Risk analysis failure; impermissible disclosure of the ePHI of 10,023 individuals.
Assured Imaging Affiliated Covered Entities Healthcare Provider $375,000 Settlement Risk analysis failure (never conducted); breach notification failure.
Consociate, Inc. (Consociate Health) Business Associate $225,000 Settlement Risk analysis failure.
Star Group, L.P. Health Benefits Plan Health Plan $245,000 Settlement Risk analysis failure.
MMG Fusion Business Associate $10,000 Settlement Risk analysis failure; impermissible use/disclosure of PHI; breach notification rule failure.
Top of the World Ranch Treatment Center Healthcare Provider $103,000 Settlement Risk analysis failure

OCR is the main enforcer of the HIPAA Rules, although state attorneys general are also authorized to enforce HIPAA compliance and can impose financial penalties in their respective states. In H1 2026, only one penalty was announced at the state level. Massachusetts and Connecticut participated in a joint investigation of Comstar LLC over a data breach affecting 585,621 individuals (326,426 Massachusetts residents & 22,829 Connecticut residents). The investigation identified violations of the HIPAA Security Rule and the Massachusetts Data Security Regulations. The case was settled with a $515,000 financial penalty.

HIPAA Regulatory Updates

There were no new updates to the HIPAA Rules in the first half of 2026, although there are two pending final rules. During President Trump’s first term in December 2020, OCR proposed an update to the HIPAA Privacy Rule to support coordinated care and improve individual engagement in healthcare. The proposed rule was formally introduced in the Federal Register in January 2021, but a final rule stalled, as OCR had other priorities under the Biden Administration. The return of President Trump for a second term has seen the proposed rule rekindled. OCR set a target of August 2026 for the release of a final rule, although it has yet to be issued.

The other pending final rule is for proposed changes to the HIPAA Security Rule. A notice of proposed rulemaking was announced by OCR in the final days of the Biden administration in late December 2024 and was published in the Federal Register on January 6, 2025. OCR received several thousand comments from industry stakeholders about the proposed changes, including a significant amount of criticism. OCR set a target release date of May 2026 for a final rule; however, it has now been pushed back until July 2027, although a final decision about whether to issue a final rule has yet to be made by the Trump administration.

While there were no new HIPAA updates in H1 2026, the compliance date for updates to the HIPAA Notice of Privacy Practices requirements was February 16, 2026 – the only surviving part of the now vacated HIPAA update to strengthen reproductive healthcare privacy. The Notice of Privacy Practices compliance deadline aligned with the compliance deadline for changes to the 42 CFR Part 2 regulations concerning substance use disorder (SUD) patient records to align those regulations more closely with HIPAA.

About this Report

This report is based on healthcare data breaches affecting 500 or more individuals that were reported to the HHS’ Office for Civil Rights in H1 2026. The data for this report was obtained from OCR on September 10, 2026, and includes supplemental information from data breach reporting from the HIPAA Journal.

You can view more comprehensive healthcare data breach facts and statistics from 2009 to the present on our data breach statistics page, and more comprehensive and up-to-date information on HIPAA enforcement actions on our HIPAA violation cases page, both of which are regularly updated. Information on the latest regulatory changes can be found on our HIPAA Updates/HIPAA Changes page.

The post H1 2026 Healthcare Data Breach Report appeared first on The HIPAA Journal.
Labcorp Settles Multistate Data Breach Investigation for $2.3 Million

A coalition of 44 state attorneys general has agreed to settle a multistate investigation of Laboratory Corporation of America (Labcorp) regarding a 2019 data breach at its debt collection company, American Medical Collection Agency (AMCA). Labcorp has agreed to pay $2,287,455, which will be divided among the 44 states participating in the action.

AMCA is a subsidiary of the debt collection company Retrieval-Masters Creditors Bureau (RMCB) and provides small debt collection services to healthcare organizations, including laboratories and medical testing facilities. The hacking incident was identified by RMCB on March 19, 2029, and the forensic investigation determined that a hacker breached the AMCA network around 8 months before the intrusion was detected. The hacker had access to the network from August 1, 2018, until March 30, 2019, and exfiltrated sensitive data including names, personal information, Social Security numbers, financial information, medical test information, and diagnostic codes.

The AMCA data breach was the largest data breach reported in 2019 by a HIPAA-regulated entity, affecting more than 27.5 million individuals, including more than 10.2 million Labcorp patients. The high cost of remediation forced AMCA to file for bankruptcy protection. AMCA was also investigated by the coalition, led by the Indiana, Texas, Connecticut, and New York attorneys general, and received permission from the bankruptcy court to settle the multistate action, filing for dismissal of the bankruptcy on December 9, 2020.

The settlement required AMCA to develop, implement, and maintain an information security program and implement a range of data security measures, including developing an incident response plan and appointing a qualified Chief Information Security Officer (CISO). A financial penalty of $21 million was suspended due to the financial position of the company.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

The investigation of Burlington, NC-based Labcorp was led by the attorneys general of Connecticut, Florida, Indiana, Illinois, Michigan, and Texas and identified potential violations of the Health Insurance Portability and Accountability Act (HIPAA) and state consumer protection and breach notification laws. The Labcorp settlement includes a financial penalty and injunctive relief. Labcorp must ensure that it does not misrepresent the extent to which it maintains and protects the privacy, security, and confidentiality of personal information (PI) and protected health information (PHI) and must implement a range of security measures, including but not limited to the following:

  • Review, revise, and update its information security program.
  • Employ an executive or officer as a CISO to oversee the implementation and maintenance of its information security program.
  • Provide security awareness training to all personnel who have access to or responsibility for PI and/or PHI.
  • Implement an incident response plan, which must include a plan for vendor security incidents.
  • Ensure procedures are implemented for reporting vendor security incidents internally to senior management.
  • Develop policies and procedures governing the collection, use, disclosure, and retention of PI and PHI, including specific policies and procedures for PI and PHI shared with debt collectors.
  • Minimize the PI and PHI shared with debt collectors.
  • Develop, implement, and maintain a vendor risk management program; maintain a vendor risk management team; and use security assessment and management tools for vendor assessment and monitoring, with specific requirements for debt collectors.
  • Require all debt collectors to conduct risk assessments, and contractually require debt collectors to conduct penetration tests of systems containing PI and PHI, and annual SOC 2 Type 2 audits.
  • Labcorp must also engage a third-party assessor to perform an information security assessment, with a focus on vendor risk management.

Labcorp was also named as a defendant in class action litigation against AMCA and other AMCA clients, and agreed to a $35,000,000 settlement earlier this year. The class action lawsuit is ongoing against other AMCA clients.

The post Labcorp Settles Multistate Data Breach Investigation for $2.3 Million appeared first on The HIPAA Journal.

Democratic Senators Reintroduce the Health Infrastructure Security and Accountability Act

On September 17, 2026, two Democratic Senators reintroduced the Health Infrastructure Security and Accountability Act, which seeks to improve cybersecurity standards for the U.S. healthcare system and make funds available to help rural and underserved hospitals invest in essential cybersecurity measures.

The bill was reintroduced by Sens. Mark R. Warner (D-VA) and Ron Wyden (D-OR), following its initial introduction in the 118th Congress 2D Session on September 25, 2024. When the bill was first introduced, 394 large hacking-related healthcare data breaches had been reported to the Department of Health and Human Services Office for Civil Rights (OCR), involving the protected health information of 43 million Americans.

At the time, the senators explained that cyberattacks are delaying and disrupting patient care, harming patient health and national security, and putting Americans at risk of identity theft and fraud. “These hacks are entirely preventable and are the direct result of lax cybersecurity practices by health care providers and their business partners,” explained the Senators.

The situation has only worsened in the two years since the bill was first introduced. The OCR breach portal lists year-to-date figures (Jan 1 – Aug 31) of 426 hacking-related breaches, involving the protected health information of 73 million Americans. That’s an 8% increase in hacking-related data breaches and a 70% increase in affected individuals.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

On January 24, 2024, OCR published two sets of voluntary cybersecurity performance goals (CPGs) for the healthcare and public health (HPH) sector – Essential and Enhanced – that consist of high-impact measures that should be adopted by healthcare organizations to strengthen and mature their cybersecurity programs. As predicted by OCR at the time, voluntary goals alone would not be enough to drive the behavioral changes needed across the sector to improve cybersecurity.

The CPGs were followed by a proposed update to the HIPAA Security Rule, which mandates significant additional cybersecurity requirements. The proposed update has proven hugely unpopular, with industry groups and health systems calling for the proposed rule to be scrapped. A final rule has been delayed until July 2027, although a final decision about whether a final rule will actually be released has yet to be made by the Trump administration. Part of the problem, especially for rural and other low-resource healthcare providers, is a lack of funding to make the necessary cybersecurity improvements, which is something that the Health Infrastructure Security and Accountability Act seeks to address.

“As cybercriminals ramp up their attacks on hospitals and health care providers, it’s becoming increasingly clear that voluntary standards are not enough to protect Americans’ health, safety, and privacy,” explained Sen. Warner. “This legislation would establish strong, commonsense cybersecurity protocols for health care entities, while also getting resources to rural and underserved hospitals to strengthen their defenses and protect the patients who depend on them.”

As the Senators explained, the U.S. health care system is particularly at risk for cyberattacks due to its size, technological dependence, collection of sensitive personal information, and unique vulnerability to disruptions. Healthcare organizations are viewed as low-hanging fruit, and attacks can be highly profitable for cybercriminals. “The frequency and sophistication of cyberattacks has dramatically increased in every part of the health care system, and will only grow,” said Sen. Wyden. “Our bill creates national cybersecurity standards for health care providers and devotes resources, especially in rural and underserved areas, to ensure every American’s medical information is secure. Congress cannot wait to act until another catastrophic cyberattack compromises the safety and privacy of American families’ most personal information.”

The 2026 Health Infrastructure Security and Accountability Act remains largely unchanged from the 2024 version, other than shifting the timeline forward by two years. The key requirements of the bill are:

  • Mandatory minimum cybersecurity standards for covered entities and business associates, established, enforced, and updated by the HHS. Updates are required at least every two years.
  • Heightened cybersecurity standards for systemically important entities and entities critical to national security.
  • Continuity/recovery plans for all covered entities for technical failures, disruptive cyber events, and natural disasters, and stress tests to evaluate whether the entity has the capabilities to recover essential functions.
  • Written annual statements signed by the chief executive officer and chief information security officer attesting that the company is compliant with applicable security standards.
  • Mandatory annual security risk analyses, including specific assessments of the extent to which the entity is exposed to risk through its business associates.
  • Independent audits of covered entities’ security measures to assess compliance with the HHS’s CPGs.
  • Annual HHS audits of at least 20 HIPAA-regulated entities to assess data security practices, focused on those of systemic importance.
  • Increased financial penalties under HIPAA for failing to meet security requirements – A minimum $500 penalty for no knowledge; $5,000 for reasonable cause; $50,000 for willful neglect (corrected); and $250,000 for willful neglect (uncorrected).
  • A government investment of $1.3 billion to help hospitals strengthen cybersecurity: $800 million in up-front investment for hospitals in rural and underserved urban communities to adopt the essential cybersecurity goals, and $500 million in incentives available to all hospitals to adopt the enhanced CPGs.
  • Medicare accelerated and advanced payments in response to cybersecurity incidents.

The post Democratic Senators Reintroduce the Health Infrastructure Security and Accountability Act appeared first on The HIPAA Journal.
Ambry Genetics Pays $700,000 Penalty to Settle HIPAA Violations

The U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) and the Aliso Viejo, California-based genetic testing and clinical genomics company Ambry Genetics Corporation have agreed to a settlement to resolve alleged violations of the Health Insurance Portability and Accountability Act (HIPAA). Ambry Genetics has agreed to pay a $700,000 financial penalty and adopt a corrective action plan to address the areas of noncompliance identified by OCR during its investigation of a breach of the electronic protected health information (ePHI) of 225,370 individuals.

The data breach was reported to OCR on March 22, 2020, initially as involving the protected health information of 232,772 individuals, although the total was later updated to 225,370 individuals. Ambry Genetics identified suspicious activity within its email environment on January 22, 2020, and its forensic investigation determined that an unauthorized third party gained access to an employee’s email account as a result of a response to a phishing email. The account was accessed by a criminal actor between January 22 and January 24, 2020, exposing names, addresses, dates of birth, driver’s license numbers, diagnosis/condition information, medications, treatment information, and some Social Security numbers.

OCR investigates all data breaches affecting 500 or more individuals and launched an investigation after being informed about the phishing-related data breach. OCR determined that Ambry Genetics failed to conduct an accurate and thorough risk analysis to identify risks and vulnerabilities to the confidentiality, integrity, and availability of ePHI.

In addition, there was a failure to implement policies and procedures for terminating access to ePHI when the employment of members of the workforce was terminated, or access to ePHI was otherwise no longer required. Unique usernames had not been assigned to all members of the workforce who required access to ePHI to allow them to be identified and their interactions with ePHI to be tracked.

Get The FREE
HIPAA Compliance Checklist

Immediate Delivery of Checklist Link To Your Email Address

Please Enter Correct Email Address

Your Privacy Respected

HIPAA Journal Privacy Policy

OCR notified Ambry Genetics of the findings of the investigation and the intention to impose a financial penalty, along with an offer to settle the alleged HIPAA violations informally. Ambry Genetics accepted and agreed to settle the alleged HIPAA violations with a $700,000 financial penalty and a corrective action plan to ensure full compliance with the HIPAA Rules. Ambry Genetics will be monitored for compliance with the corrective action plan for a period of two years.

The corrective action plan requires Ambry Genetics to conduct a comprehensive and accurate risk analysis and develop and implement a risk management program to reduce and mitigate the risks identified by the risk analysis. Policies and procedures must be developed to ensure compliance with the HIPAA Security Rule and other HIPAA policies and procedures, and all members of the workforce must be assigned unique identification to allow their activity to be tracked in information systems containing ePHI. All workforce members must receive HIPAA training on the policies and procedures.  The phishing attack has proven costly for Ambry Genetics. Ambry Genetics faced class action litigation over the data breach and settled the lawsuit for $12.25 million.

“Email phishing is a common cyberattack that can lead to a breach of PHI and reveal HIPAA Security Rule deficiencies,” said OCR Director Paula M. Stannard. “Conducting a compliant risk analysis, engaging in risk management, and full implementation of the Security Rule provisions continue to be the foundation for effective cybersecurity and the best cyber defense.” This is the 10th financial penalty to be imposed by OCR this year to resolve alleged violations of the HIPAA Rules, and its 188th penalty to date. All but one of this year’s penalties have resolved risk analysis failures. So far this year, OCR has collected $3,030,250 in HIPAA fines.

The post Ambry Genetics Pays $700,000 Penalty to Settle HIPAA Violations appeared first on The HIPAA Journal.