Healthcare Cybersecurity

Plaintiffs in Class Action Claim Premera Blue Cross Destroyed Key Evidence

There has been a twist in the class action lawsuit filed by victims of the 2015 Premera Blue Cross data breach. The plaintiffs allege Premera Blue Cross willfully destroyed evidence of data theft.

In 2015, Premera Blue Cross announced it was the victim of a cyberattack that resulted in cybercriminals gaining access to plan members’ protected health information.

The data breach was the second largest data breach ever to be reported by a healthcare organization, behind only the 78.8 million-record Anthem Inc., data breach that was also discovered in 2015. The protected health information of 11 million individuals was exposed as a result of the hack.

The Premera data breach was detected in January 2015, although the investigation revealed hackers had gained access to its network in May 2014. The attackers potentially had access to plan members’ protected health information (PHI) and personally identifiable information (PII) for 8 months before the intrusion was detected and access to data was blocked.

Unsurprisingly, given the scale of the breach, several class action lawsuits were filed by the breach victims. As was the case with the lawsuits filed in the wake of the Anthem data breach, they were consolidated into a single class action lawsuit. Anthem settled its class action lawsuit earlier this year, but the Premera Blue Cross lawsuit is ongoing.

A resolution does not appear to be getting closer. In fact, there has been a new twist in the case which is likely to delay an outcome further still. The plaintiffs have alleged that Premera Blue Cross destroyed key evidence that would have helped their case.

Alleged Destruction of Evidence of Data Theft

A third-party computer forensics firm, Mandiant, was retained to conduct an investigation into the breach. Mandiant determined that the hackers had compromised 35 Premera computers in the attack, and through those computers the attackers potentially had access to the records of 11 million plan members.

The cyberattack was not the work of amateurs. A well-known hacking group had conducted the attack and that group had succeeded in stealing data from other entities that it had attacked in the past.

While concrete evidence was allegedly not found to confirm that data had been exfiltrated, Mandiant did find fragments of RAR files on one of the computers that had been compromised. RAR files are compressed files that are used to make data transmission easier. The presence of the file fragments, which it is alleged were created by the attackers, suggests the hackers used RAR files to exfiltrate data and deleted the files to cover their tracks.

The plaintiffs requested all evidence uncovered during the Mandiant investigation be handed over, including the hard drives and forensic images of the 35 compromised computers. Premera responded to that request but claimed that it was only able to provide images for 34 out of the 35 computers as one computer, referred to in the court documents as A23567-D, had been destroyed. The computer was destroyed on December 16, 2016 – around a year after the litigation had started.

A23567-D is alleged to have contained important evidence that could confirm that data had been exfiltrated. That computer was the only one out of the 35 to contain a type of malware referred to by Mandiant as PHOTO. The malware was capable of registry modification, executing programs, and crucially, uploading and downloading files. The attackers communicated with that computer on a daily basis from July 2014 until January 2015 when the cyberattack was discovered and remote access was blocked.

“The destroyed computer was perfectly positioned to be the one-and-only staging computer hackers needed to create vast staging files for the purpose of shipping even more data outside of Premera’s network,” wrote the plaintiffs’ attorneys in the motion. “This computer functioned as the development machine for a software programmer, and as such was pre-loaded with a vast array of legitimate utilities that could be turned to any purpose.”

The computer appears to have been sent for destruction in error. It was deemed to be of no further interest to Premera and had reached end of life.

The problem for the plaintiffs is without any evidence of data theft, the case is unlikely to succeed. According to the motion, “Essentially, Premera maintains a ‘no harm, no foul’ defense, contending there can be no damage to any plaintiff unless he or she can prove confidential information was exfiltrated from Premera’s system.”

Whether accidental or willful, the destruction of the computer is extremely damaging to the case. The motion states that “Without access to that hard drive, trying to prove that the hackers removed plaintiffs PII and PHI through that computer is impossible.”

Additionally, the motion, filed in the U.S. District Court in Portland, claims that Premera Blue Cross failed to preserve data loss logs from its Bluecoat Data Loss Prevention (DLP) system, which potentially could have confirmed that plan members’ data had been stolen. It is alleged that those files were also deleted after the lawsuit was filed.

Premera Blue Cross issued a a statement to ZDNet in which it was confirmed that Premera disagrees with the motion and does not believe the facts of the case justify the relief the plaintiffs have requested. A response to the motion will be filed by Premera’s attorneys by September 28, 2018.

If the motion is granted, a federal judge would then instruct a jury that key evidence has been destroyed and that it should be assumed that the evidence confirmed data exfiltration had occurred. It would also not be possible for Premera to call in computer experts to testify that no data had been exfiltrated.

Even a favorable ruling would be no guarantee of success nor of a settlement being reached. In order for damages to be awarded, plaintiffs in the suit would still need to establish that they have suffered losses as a result of the data breach.

The post Plaintiffs in Class Action Claim Premera Blue Cross Destroyed Key Evidence appeared first on HIPAA Journal.
Plaintiffs in Class Action Claim Premera Blue Cross Destroyed Key Evidence

There has been a twist in the class action lawsuit filed by victims of the 2015 Premera Blue Cross data breach. The plaintiffs allege Premera Blue Cross willfully destroyed evidence of data theft.

In 2015, Premera Blue Cross announced it was the victim of a cyberattack that resulted in cybercriminals gaining access to plan members’ protected health information.

The data breach was the second largest data breach ever to be reported by a healthcare organization, behind only the 78.8 million-record Anthem Inc., data breach that was also discovered in 2015. The protected health information of 11 million individuals was exposed as a result of the hack.

The Premera data breach was detected in January 2015, although the investigation revealed hackers had gained access to its network in May 2014. The attackers potentially had access to plan members’ protected health information (PHI) and personally identifiable information (PII) for 8 months before the intrusion was detected and access to data was blocked.

Unsurprisingly, given the scale of the breach, several class action lawsuits were filed by the breach victims. As was the case with the lawsuits filed in the wake of the Anthem data breach, they were consolidated into a single class action lawsuit. Anthem settled its class action lawsuit earlier this year, but the Premera Blue Cross lawsuit is ongoing.

A resolution does not appear to be getting closer. In fact, there has been a new twist in the case which is likely to delay an outcome further still. The plaintiffs have alleged that Premera Blue Cross destroyed key evidence that would have helped their case.

Alleged Destruction of Evidence of Data Theft

A third-party computer forensics firm, Mandiant, was retained to conduct an investigation into the breach. Mandiant determined that the hackers had compromised 35 Premera computers in the attack, and through those computers the attackers potentially had access to the records of 11 million plan members.

The cyberattack was not the work of amateurs. A well-known hacking group had conducted the attack and that group had succeeded in stealing data from other entities that it had attacked in the past.

While concrete evidence was allegedly not found to confirm that data had been exfiltrated, Mandiant did find fragments of RAR files on one of the computers that had been compromised. RAR files are compressed files that are used to make data transmission easier. The presence of the file fragments, which it is alleged were created by the attackers, suggests the hackers used RAR files to exfiltrate data and deleted the files to cover their tracks.

The plaintiffs requested all evidence uncovered during the Mandiant investigation be handed over, including the hard drives and forensic images of the 35 compromised computers. Premera responded to that request but claimed that it was only able to provide images for 34 out of the 35 computers as one computer, referred to in the court documents as A23567-D, had been destroyed. The computer was destroyed on December 16, 2016 – around a year after the litigation had started.

A23567-D is alleged to have contained important evidence that could confirm that data had been exfiltrated. That computer was the only one out of the 35 to contain a type of malware referred to by Mandiant as PHOTO. The malware was capable of registry modification, executing programs, and crucially, uploading and downloading files. The attackers communicated with that computer on a daily basis from July 2014 until January 2015 when the cyberattack was discovered and remote access was blocked.

“The destroyed computer was perfectly positioned to be the one-and-only staging computer hackers needed to create vast staging files for the purpose of shipping even more data outside of Premera’s network,” wrote the plaintiffs’ attorneys in the motion. “This computer functioned as the development machine for a software programmer, and as such was pre-loaded with a vast array of legitimate utilities that could be turned to any purpose.”

The computer appears to have been sent for destruction in error. It was deemed to be of no further interest to Premera and had reached end of life.

The problem for the plaintiffs is without any evidence of data theft, the case is unlikely to succeed. According to the motion, “Essentially, Premera maintains a ‘no harm, no foul’ defense, contending there can be no damage to any plaintiff unless he or she can prove confidential information was exfiltrated from Premera’s system.”

Whether accidental or willful, the destruction of the computer is extremely damaging to the case. The motion states that “Without access to that hard drive, trying to prove that the hackers removed plaintiffs PII and PHI through that computer is impossible.”

Additionally, the motion, filed in the U.S. District Court in Portland, claims that Premera Blue Cross failed to preserve data loss logs from its Bluecoat Data Loss Prevention (DLP) system, which potentially could have confirmed that plan members’ data had been stolen. It is alleged that those files were also deleted after the lawsuit was filed.

Premera Blue Cross issued a a statement to ZDNet in which it was confirmed that Premera disagrees with the motion and does not believe the facts of the case justify the relief the plaintiffs have requested. A response to the motion will be filed by Premera’s attorneys by September 28, 2018.

If the motion is granted, a federal judge would then instruct a jury that key evidence has been destroyed and that it should be assumed that the evidence confirmed data exfiltration had occurred. It would also not be possible for Premera to call in computer experts to testify that no data had been exfiltrated.

Even a favorable ruling would be no guarantee of success nor of a settlement being reached. In order for damages to be awarded, plaintiffs in the suit would still need to establish that they have suffered losses as a result of the data breach.

The post Plaintiffs in Class Action Claim Premera Blue Cross Destroyed Key Evidence appeared first on HIPAA Journal.
NY Attorney General Fines Arc of Erie County $200,000 for Security Breach

The Arc of Erie County has been fined $200,000 by the New York Attorney General for violating HIPAA Rules by failing to secure the electronic protected health information (ePHI) of its clients.

In February 2018, The Arc of Erie County, a nonprofit social services agency and chapter of the The Arc Of New York, was notified by a member of the public that some of its clients’ sensitive personal information was accessible through its website. The information could also be found through search engines.

The investigation into the security breach revealed sensitive information had been accessible online for two and a half years, from July 2015 to February 2018 when the error was corrected. The forensic investigation into the security incident revealed multiple individuals from outside the United States had accessed the information on several occasions. The webpage should only have been accessible internally by staff authorized to view ePHI and should have required a username and password to be entered before access to the data could be gained.

In total, 3,751 clients in New York had information such as their full name, address, phone number, age, date of birth, gender, race, primary diagnosis code, IQ, health insurance information, and Social Security number exposed. Those individuals were notified of the breach on March 9, 2018, the Department of Health and Human Services’ Office for Civil Rights was informed, and a breach report was submitted to the New York Attorney General’s office.

Under HIPAA, The Arc of Erie County is required to safeguard the ePHI of its clients and prevent that information from being accessed by unauthorized individuals. The investigation into the breach by the New York Attorney General’s office confirmed that HIPAA Rules had been violated as appropriate physical, technical, and administrative safeguards had not been implemented to ensure the confidentiality, integrity, and availability of ePHI. As a result of that failure, there had been an impermissible disclosure of clients ePHI.

“The Arc of Erie County’s work serves our most vulnerable New Yorkers – and that comes with the responsibility to protect them and their sensitive personal information,” said New York Attorney General Barbara. D. Underwood. “This settlement should provide a model to all charities in protecting their communities’ personal information online.”

In addition to paying a financial penalty of $200,000, The Arc of Erie County has agreed to adopt a Corrective Action Plan (CAP) that includes the requirement to conduct a thorough risk analysis to identify all security risks and vulnerabilities affecting its electronic equipment and data systems. A report of that assessment must be submitted to the New York Attorney General’s office within 180 days. Any vulnerabilities identified must be corrected through a HIPAA-compliance risk management process and policies and procedures must also be reviewed and revised, based on the findings of the risk analysis.

The post NY Attorney General Fines Arc of Erie County $200,000 for Security Breach appeared first on HIPAA Journal.

ICS-CERT Issues Advisory After Nine Vulnerabilities Discovered in Philips E-Alert Units

The Department of Homeland Security’s Industrial Control Systems Cyber Emergency Response Team (ICS-CERT) has issued a further advisory about Philips healthcare devices after nine vulnerabilities were self-reported to the National Cybersecurity & Communications Integration Center (NCCIC) by the Amsterdam-based technology company.

This is the fourth advisory issued by ICS-CERT in the past month. Previous advisories have been issued over cybersecurity vulnerabilities in its central patient monitoring system – Philips IntelliVue Information Center iX (1 vulnerability), Philips PageWriter Cardiographs (2 vulnerabilities), and Philips IntelliSpace Cardiovascular cardiac image and information management software (2 vulnerabilities).

The latest advisory concerns nine vulnerabilities discovered in Philips eAlert units – These are non-medical devices that monitor imaging systems such as MRI machines to identify issues rapidly before they escalate. The devices are used by healthcare providers around the world.

One of the vulnerabilities is rated critical, five are high severity, and three are medium severity. If exploited, an attacker on the same subnet could potentially obtain user contact details, compromise unit integrity/availability, provided unexpected input into the application and execute arbitrary code, altering display unit information or causing the device to crash. The vulnerabilities affect all versions of the software, including R2.1.

In order of severity, the vulnerabilities are:

CVE-2018-8856 (CWE-798) – Hard-Coded Credentials – CVSS v3 score: 9.8

A hard-coded cryptographic key is present in the software which is used for the encryption of internal data.

CVE-2018-8842 (CWE-319) – Cleartext Transmission of Sensitive Information – CVSS v3 score: 7.5

Sensitive and security-critical data are transmitted in cleartext which could be intercepted by individuals unauthorized to view the information. Since the Philips e-Alert communication channel is not encrypted, personal contact information and application login credentials could be obtained from within the same subnet.

CVE-2018-8854 (CWE-400) – Uncontrolled Resource Consumption – CVSS v3 score: 7.5

The size or amount of resources requested or influenced by an actor are not properly restricted, which can be used to consume more resources than intended.

CVE-2018-8850 (CWE-20) – Improper Input Validation – CVSS v3 score: 7.1

Improper validation of input that would allow an attacker to craft input in a form not expected by the application. Parts of the unit could receive unintended input potentially resulting in altered control flow, arbitrary control of a resource, or arbitrary code execution.

CVE-2018-8846 (CWE-79) – Improper Neutralization of Input During Web Page Generation – CVSS v3 score: 7.1

The software fails to neutralize or improperly neutralizes user-controlled input before being placed in output that is used as a web page which is subsequently served to other users.

CVE-2018-8848 (CWE-276) – Incorrect Default Permissions – CVSS v3 score: 7.1

When the software is installed, incorrect permissions are set for an object that exposes it to an unintended actor.

CVE-2018-8844 (CWE-352) – Cross-Site Request Forgery – CVSS v3 score: 6.8

The web application does not adequately verify whether a well-formed, valid, consistent request was intentionally provided by the user who submitted the request.

CVE-2018-8852 (CWE-384) – Session Fixation – CVSS v3 score: 6.4

When authenticating a user or establishing a new user session, an attacker is given an opportunity to steal authenticated sessions without invalidating any existing session identifier.

CVE-2018-14803 (CWE-200) – Information Exposure – CVSS v3 score: 5.3

This is a banner disclosure vulnerability that could allow an attacker to gain product information such as the OS and software components via the HTTP response header which would normally not be available to an attacker.

Four of the vulnerabilities have been addressed with the release of R2.1 (CVE-2018-8842, CVE-2018-8856, CVE-2018-8850, CVE-2018-8852) and the remaining five vulnerabilities (CVE-2018-8854, CVE-2018-8846, CVE-2018-8848, CVE-2018-14803, CVE-2018-8844) will be addressed with a software update which has been planned for the end of the year.

Users of vulnerable devices should ensure that they have upgraded to software version R2.1 which will address four of the vulnerabilities, including the critical hard-coded credential flaw.

Philips also recommends users take the following actions as an immediate mitigation to reduce the potential for exploitation of the five remaining flaws until the next software update is released:

  • Ensure that network security best practices are implemented, and
  • Limit network access to e-Alert in accordance with product documentation.

The post ICS-CERT Issues Advisory After Nine Vulnerabilities Discovered in Philips E-Alert Units appeared first on HIPAA Journal.

NIST Finalizes Guidance on Securing Wireless Infusion Pumps in Healthcare Delivery Organizations

The National Cybersecurity Center of Excellence (NCCoE) and the National Institute of Standards and Technology (NIST) have released the final version of the NIST Cybersecurity Practice Guide for Securing Wireless Infusion Pumps in healthcare delivery organizations.

Wireless infusion pumps are no longer standalone devices. They can be connected to a range of different healthcare systems, networks, and other devices and can be a major cybersecurity risk.

If malicious actors are able to gain access to the wireless infusion pump ecosystem, settings could be altered on the pumps or malware could be installed that causes the devices to malfunction, resulting in operational and safety risks.

An attack on the devices could result in patients coming to harm, protected health information could be exposed, and a compromise could result in disruption to healthcare services, reputation damage, and considerable financial costs.

Securing wireless infusion pumps is a challenge. Standard cybersecurity solutions such as anti-virus software may affect the ability of the device to function correctly and efficiently. Oftentimes, the pumps contain maintenance default passcodes which, if not changed, makes them vulnerable to attack. Many wireless infusion pumps can be accessed remotely. While this makes management easier, it is also a security weak point. The devices could potentially be accessed remotely by threat actors.

The guide helps healthcare delivery organizations manage and secure their wireless networks and infusion pumps, mitigate vulnerabilities, and protect against threats.

The guide combines standard-based commercially available technologies with industry best practices to help healthcare delivery organizations strengthen the security of the devices. The guidance includes a questionnaire-based risk assessment and maps the security characteristics of the wireless infusion pump ecosystem to the HIPAA Security Rule and the NIST Cybersecurity Framework.

By using the guide, healthcare delivery organizations can create a defense-in-depth solution that will allow them to protect their wireless infusion pumps against a wide range of different risk factors.

Braun, Baxter, BD, Cisco, Clearwater Compliance, Digicert, Hospira, Intercede, MDISS, PFP Cybersecurity, Ramparts, Smiths Medical, Symantec, and TDI Technologies all participated in the creation of the guide.

NIST Special Publication 1800-8A – Securing Wireless Infusion Pumps in Healthcare Delivery Organizations – is available for download on this link (PDF).

The 375-page document may take some time to open, depending on the speed of your Internet connection.

The post NIST Finalizes Guidance on Securing Wireless Infusion Pumps in Healthcare Delivery Organizations appeared first on HIPAA Journal.

Critical ‘Misfortune Cookie’ Flaw Identified in Qualcomm Life Capsule Datacaptor Terminal Server

A code weakness in Qualcomm Life’s Capsule Datacaptor Terminal Server (DTS) has been discovered. The flaw could be remotely exploited allowing an attacker to obtain administrator level privileges and remotely execute code.

The Qualcomm Life Capsule’s Datacaptor Terminal Server is a medical gateway device used by many U.S. hospitals to network their medical devices. The Datacaptor Terminal Server is used to connect respirators, bedside monitors, infusion pumps and other medical devices to the network. The Datacaptor Terminal Server has a web management interface which allows it to be operated and configured remotely.

The flaw affects the Allegro RomPager embedded webserver (versions 4.01 through 4.34) which is included in all versions of Capsule DTS. The flaw could be exploited by an attacker by sending a specially crafted HTTP cookie to the web management portal, allowing arbitrary data to be written to the devices’ memory, ultimately permitting remote code execution. The exploit would require little skill to perform and requires no authentication. If exploited, availability of the device could be harmed, as well as causing disruption to the network connectivity of all medical devices networked through the device.

The vulnerability, tracked as CVE-2014-9222, is classed as critical and has been assigned a CVSS v3 base score of 9.8 out of 10.

While the vulnerability in Qualcomm Life’s Capsule Datacaptor Terminal Server has only just been discovered, it dates back more than four years. The vulnerability, known as Misfortune Cookie, was identified by Checkpoint researchers in 2014, and by Allegro nine years ago. While Allegro addressed the flaw in version 4.34 of its firmware, that version was not adopted by many chipset manufacturers who continued to supply software development kits containing the vulnerable version of the firmware.

The vulnerability was recently discovered to affect the Qualcomm Life Capsule DTS by Elad Luz, Head of Research at CyberMDX, who notified Qualcomm Life allowing an update to be issued to correct the flaw prior to public disclosure. Luz also recently identified a critical flaw in certain BD Alaris Plus medical syringe pumps.

Qualcomm Life has issued a firmware upgrade for the Single Board version of DTS which can be downloaded from the customer portal of Capsule and applied to the device using standard patching processes. Unfortunately, due to technical limitations, it is not possible for the patch to be applied to other versions of DTS including Dual Board, Capsule Digi Connect ES, and Capsule Digi Connect ES converted to DTS.

To address the flaw in those versions, Capsule recommends disabling the embedded webserver. Since the embedded webserver is only required for initial configuration, and not for continued use of the device, disabling the webserver will not adversely affect functionality of the device.

“Uncovering these vulnerabilities illustrates how responsible disclosure between cybersecurity researchers and medical device vendors can work when both sides are committed to improving patient safety,” said Luz.

The post Critical ‘Misfortune Cookie’ Flaw Identified in Qualcomm Life Capsule Datacaptor Terminal Server appeared first on HIPAA Journal.

Critical Flaw Identified in BD Alaris Plus Medical Syringe Pumps

A critical remotely exploitable flaw has been detected in BD Alaris Plus medical syringe pumps. The flaw would enable a threat actor to gain access to an affected medical syringe pump when it is connected to a terminal server via the serial port. If the flaw is exploited a threat actor could alter the intended function of the pump.

The flaw is an improper authentication vulnerability. The software fails to perform authentication for functionality that requires a provable user identity.

The flaw was identified by Elad Luz of CyberMDX who notified Becton, Dickinson and Company (BD), which in turn voluntarily reported the vulnerability to the National Cybersecurity & Communications Integration Center and the Industrial Control Systems Cyber Emergency Response Team (ICS-CERT). The latter issued an advisory about the vulnerability on August 23, 2018.

The vulnerability affects version 2.3.6 of Alaris Plus medical syringe pumps and prior versions, specifically the Alaris GS, Alaris GH, Alaris CC, and Alaris TIVA products. The vulnerability has been assigned a CVSS v3 score of 9.4 out of 10 and is being tracked as CVE-2018-147.

BD has explained that the vulnerability does not affect any products that are sold in the United States. All current versions of Alaris Plus pumps do not have the vulnerability. Vulnerable devices were previously sold in the European Union.

The vulnerability cannot be exploited while the device is connected to the Alaris Gateway Workstation docking station as the remote-control feature is disabled when the device is connected to the docking station.

If the device is not switched on it cannot be turned on remotely. BD also notes that were the flaw to be exploited access to PII or PHI could not be gained.

BD has explained that an attack utilizes a known vulnerability in terminal servers. Use of the device with terminal servers is not supported. To reduce the potential for the flaw to be exploited, all users have been advised to operate the affected pumps as stand-alone devices or alternatively they should be used in a segmented network environment.

The ICS-CERT advisory claims the vulnerability would only require a low level of skill to exploit, although according to BD, “To execute this attack one would need to ensure the affected device is connected to a terminal server via the serial port, have an understanding of the device communication protocol, have access to specific driver software to implement the pump protocol communication and the ability to penetrate a customer network and gain unauthorized access to terminal server devices.”

Because of the sequence of events required to exploit the vulnerability, BD said “the probability of an unauthorized breach in network security that impacts the delivery of a patient’s IV infusion is negligible.”

The post Critical Flaw Identified in BD Alaris Plus Medical Syringe Pumps appeared first on HIPAA Journal.

July 2018 Healthcare Data Breach Report

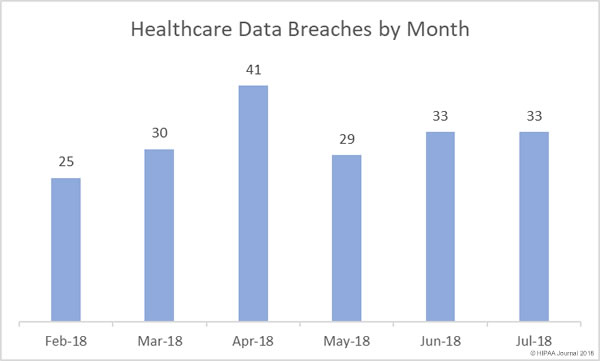
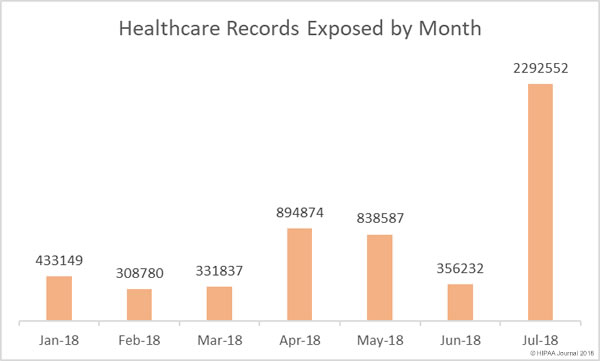
July 2018 was the worst month of 2018 for healthcare data breaches by a considerable distance. There were 33 breaches reported in July – the same number of breaches as in June – although 543.6% more records were exposed in July than the previous month.

Healthcare Data Breaches by Month (Feb-July 2018)

The breaches reported in July 2018 impacted 2,292,552 patients and health plan members, which is 202,859 more records than were exposed in April, May, and July combined.

Healthcare Records Exposed by Month

A Bad Year for Patient Privacy

So far in 2018 there have been 221 data breaches of more than 500 records reported to the Department of Health and Human Services’ Office for Civil Rights. Those breaches have resulted in the protected health information of 6,112,867 individuals being exposed, stolen, or impermissibly disclosed.

To put that figure into perspective, it is 974,688 more records than were exposed in healthcare data breaches in all of 2017 and there are still five months left of 2018.

Largest Healthcare Data Breaches of 2018 (Jan-July)

Entity Name Entity Type Records Exposed Breach Type
UnityPoint Health Business Associate 1,421,107 Hacking/IT Incident
CA Department of Developmental Services Health Plan 582,174 Theft
MSK Group Healthcare Provider 566,236 Hacking/IT Incident
LifeBridge Health, Inc Healthcare Provider 538,127 Hacking/IT Incident
SSM Health St. Mary’s Hospital – Jefferson City Healthcare Provider 301,000 Improper Disposal
Oklahoma State University Center for Health Sciences Healthcare Provider 279,865 Hacking/IT Incident
Med Associates, Inc. Business Associate 276,057 Hacking/IT Incident
MedEvolve Business Associate 205,434 Unauthorized Access/Disclosure
St. Peter’s Surgery & Endoscopy Center Healthcare Provider 134,512 Hacking/IT Incident
Boys Town National Research Hospital Healthcare Provider 105,309 Hacking/IT Incident

Causes of Healthcare Data Breaches in July 2018

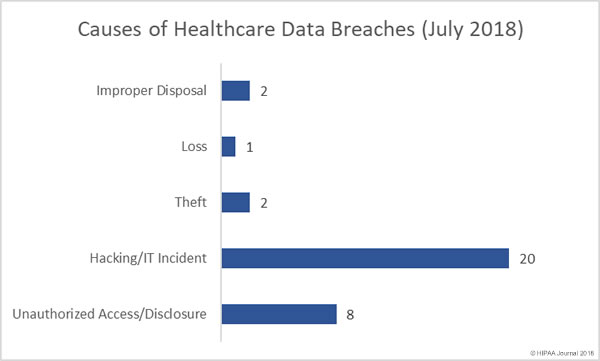
Unauthorized accessing of PHI by employees and impermissible disclosures of PHI are commonplace in healthcare, although in July there was a major reduction in these types of breaches, falling by 46.6% from July. There was also a significant drop in the number of incidents involving the loss or theft of unencrypted electronic devices and physical PHI, which fell 50% month over month.

Causes of Healthcare Data Breaches July 2018

Hacking incidents, ransomware attacks and other IT incidents such as malware infections and phishing attacks significantly increased in July. There were 66.7% more hacking/IT incidents than June. Hacking/IT incidents also resulted in the exposure of more healthcare records than all other types of breaches combined.

Healthcare Records Exposed by Breach Type (July 2018)

7 of the top 15 data breaches (46.7%) in July were phishing attacks, two were ransomware attacks, three were failures to secure electronic PHI and two were improper disposal incidents involving physical PHI. The improper disposal incidents were the second biggest cause of exposed PHI, largely due to the 301,000-record breach at SSM Health. In that breach, physical records were left behind when St. Mary’s Hospital moved to a new location.

In July, more healthcare records were exposed through phishing attacks than any other breach cause. The phishing incidents resulted in the exposure and possible theft of than 1.6 million healthcare records.

Largest Healthcare Data Breaches in July 2018

In July, there were 12 healthcare data breaches of more than 10,000 records and four breaches impacted more than 100,000 individuals. There were 14 breaches of between 1,000 and 9,999 records and 7 breaches of between 500 and 999 records. Four of the ten largest healthcare data breaches of 2018 were reported in July.

The largest healthcare data breach of July, and the largest breach of 2018 to date, was a phishing attack on Iowa Health System doing business as UnityPoint Health.

The threat actor responsible for the UnityPoint Health phishing attack spoofed an executive’s email account and sent messages to UnityPoint Health employees. Several members of staff were fooled by the emails and disclosed their login credentials giving the attacker access to their email accounts. Those email accounts contained the protected health information of more than 1.4 million patients.

Four of the ten largest healthcare data breaches of 2018 were reported in July.

Entity Name Entity Type Records Exposed Breach Type
UnityPoint Health Business Associate 1,421,107 Hacking/IT Incident
SSM Health St. Mary’s Hospital – Jefferson City Healthcare Provider 301,000 Improper Disposal
MedEvolve Business Associate 205,434 Unauthorized Access/Disclosure
Boys Town National Research Hospital Healthcare Provider 105,309 Hacking/IT Incident
Blue Springs Family Care, P.C. Healthcare Provider 44,979 Hacking/IT Incident
Golden Heart Administrative Professionals Business Associate 44,600 Hacking/IT Incident
Confluence Health Healthcare Provider 33,821 Hacking/IT Incident
NorthStar Anesthesia Healthcare Provider 19,807 Hacking/IT Incident
Orlando Orthopaedic Center Healthcare Provider 19,101 Unauthorized Access/Disclosure
New England Dermatology, P.C. Healthcare Provider 16,154 Improper Disposal
MedSpring of Texas, PA Healthcare Provider 13,034 Hacking/IT Incident
Longwood Orthopedic Associates, Inc. Healthcare Provider 10,000 Unauthorized Access/Disclosure

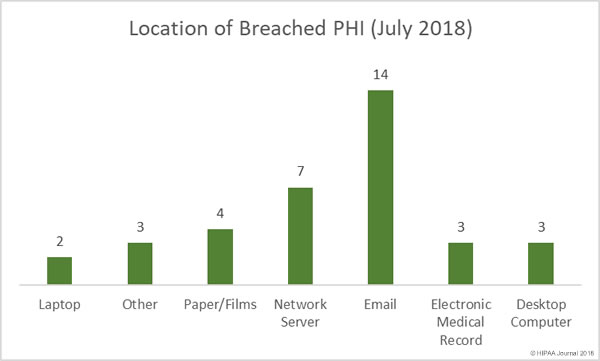
Location of Breached PHI

Unsurprisingly, given the high number of successful phishing attacks in July, email-related breached dominated the breach reports and was the main location of breached PHI, as has been the case in March, April, May and June. There were seven network server breaches in July, which were a combination of ransomware attacks, accidental removal of security protections, malware infections, and hacking incidents.

Location of Breached PHI (July 2018)

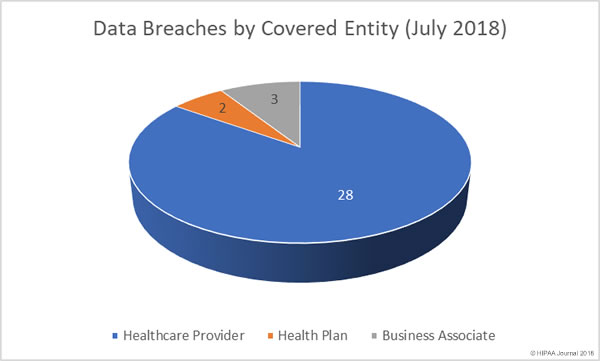
Data Breaches by Covered Entity Type

Healthcare providers were hit the hardest in July with 28 breaches reported by providers. Only two health plans reported data breaches in July. Three business associates reported breaches, although nine reported data breaches had at least some business associate involvement.

July 2018 Healthcare Data Breaches by Covered Entity

Healthcare Data Breaches by State

Healthcare organizations based in 22 states reported data breaches in July. California usually tops the list for the most data breaches each month due to the number of healthcare organizations based in the state, although in July it was Florida and Massachusetts than had the most breaches with three apiece.

Alaska, Missouri, New York, Pennsylvania, Texas, Virginia, and Washington each had two breaches reported, and there was one breach reported in each of Arkansas, California, Colorado, Idaho, Indiana, Illinois, Maryland, Michigan, Montana, Nebraska, New Jersey, New Mexico, and Tennessee.

The post July 2018 Healthcare Data Breach Report appeared first on HIPAA Journal.

Warnings Issued About Vulnerabilities in Philips PageWriter Cardiographs and IntelliVue Information Center iX

Over the past few months, several vulnerabilities have been discovered in Philips medical devices, software and systems.

This week, two further advisories have been issued by the Industrial Control Systems Cyber Emergency Team (ICS-CERT) about vulnerabilities the firm’s real-time central monitoring system, Philips IntelliVue Information Center iX, and its PageWriter cardiographs. All three of the vulnerabilities are classed as medium risk with CVSS v3 base scores ranging between 5.7 and 6.1.

CVE-1999-0103 is a denial of service vulnerability that affects the Philips IntelliVue Information Center iX version B.02. The flaw was discovered by a user of the system and was reported to Philips, which in turn reported the vulnerability to the National Cybersecurity and Communications Integration Center’s (NCCIC).

The vulnerability can be exploited remotely and does not require a high level of skill. If multiple initial UDP requests are made, it could compromise the availability of the device by causing the operating system to become unresponsive. The vulnerability has been assigned a CVSS v3 base score of 5.7.

Philips has already put mitigations in place to reduce the potential for the vulnerability to be exploited. All PIIC iX B.02 users have been advised to read the labelling, instructions for use, and service guides, which detail compensating controls. A patch will be released to correct the vulnerability by the end of September 2018.

Two vulnerabilities have been identified by Philips affecting its PageWriter TC10, TC20, TC30, TC50, TC70 Cardiographs. The flaws are present in all versions prior to May 2018.

CVE-2018-14799 is an improper input validation vulnerability. The devices do not properly sanitize data entered by users, which could result in the triggering of a buffer overflow condition. If exploited, a threat actor could access and modify device settings. The vulnerability has been assigned a CVSS v3 base score of 5.9.

CVE-2018-1480 concerns the use of hard-coded credentials. To exploit this vulnerability an attacker would need physical access to the device and would require the superuser password. With the password and physical access it would be possible to change all settings on the device and reset all existing passwords. The vulnerability has been assigned a CVSS v3 base score of 6.1.

The PageWriter vulnerabilities will be addressed by Philips via a new release, but that will not be available until the middle of 2019.

Philips notes that the WinCE5 operating system on the PageWriter TC20, TC30, TC50 and TC70 is now obsolete and is no longer supported. TC50 and TC70 can be updated to WinCE7, which users can download from InCenter.

However, TC20 and TC30 do not support WinCE7 so customers have been advised to upgrade to TC50 if they are concerned about the obsolete operating system, otherwise Philips will be issuing an update for the TC20 to a supported operating system by the end of 2019.

In the meantime, Philips suggests defense in depth, physical security controls to prevent access to the devices, controlling access to system components to protect medical devices in the system, and the use of multi-factor authentication.

The post Warnings Issued About Vulnerabilities in Philips PageWriter Cardiographs and IntelliVue Information Center iX appeared first on HIPAA Journal.