Healthcare Cybersecurity

Is Azure HIPAA Compliant?

Is Azure HIPAA compliant? Can Microsoft’s cloud services be used by HIPAA covered entities without violating HIPAA Rules?

Many healthcare organizations are considering moving some of their services to the cloud, and a large percentage already have. The cloud offers considerable benefits and can help healthcare organizations lower their IT costs, but what about HIPAA?

HIPAA does not prohibit healthcare organizations from taking advantage of cloud services; however, it does place certain restrictions on the services that can be used, at least as far as protected health information is concerned.

Most healthcare organizations will consider the three main providers of cloud services. Amazon Web Services (AWS), Google Cloud Platform (GCP), and Microsoft Azure. We have already covered AWS HIPAA compliance here, but what about Azure? Is Azure HIPAA compliant?

Is Azure HIPAA Compliant?

Before any cloud service can be used by healthcare organizations, they must first enter into a business associate agreement with the service provider.

Under HIPAA Rules, cloud service providers are considered business associates. Before any PHI can be uploaded to the cloud, HIPAA-covered entities must obtain satisfactory assurances that the service incorporates all the appropriate privacy and security safeguards to meet the requirements of the HIPAA Privacy and Security Rules.

Those assurances come in the form of a business associate agreement – essentially a contract with a vendor in which the responsibilities of the vendor are explained. The BAA must be obtained before any cloud service can be used for storing, processing, or sharing PHI. It does not matter is the service provider does not access customers’ data. A BAA is still required.

Microsoft Will Sign a BAA for Azure

Microsoft is willing to sign a BAA with healthcare organizations that covers Azure*, so does that make Azure HIPAA compliant?

Unfortunately, it is not that simple. No cloud platform can be truly HIPAA compliant. Cloud HIPAA compliance is not so much about platforms and security controls, but how those services are used. Even a cloud service such as Azure can easily be used in a way that violates HIPAA Rules. It is the responsibility of the covered entity to ensure cloud instances are configured correctly.

So Azure is not HIPAA compliant per se, but it does support HIPAA compliance, and incorporates all the necessary safeguards to ensure HIPAA requirements can be satisfied.

Access, Integrity, Audit and Security Controls

Microsoft provides a secure VPN to connect to Azure, so any data uploaded to, or downloaded from, Azure is encrypted and all data stored in its cloud instances are encrypted.

HIPAA requires access controls to be implemented to limit who can access to PHI. Azure offers these controls and uses Active Directory to allow permissions to be set. Multi-factor authentication can also be added.

Audit controls are also necessary for HIPAA compliance. Azure includes detailed logging, so administrators can see who accessed, attempted to access PHI.

So, is Azure HIPAA compliant? Azure can be used in a way that satisfies HIPAA Rules, but note that it is the responsibility of the covered entity to ensure the service is configured and used correctly and staff are trained on its use. Microsoft will accept no responsibility for HIPAA violations caused as a result of the misuse of its services.

*Not all Azure services are included in the BAA. See here for up-to-date information.

The post Is Azure HIPAA Compliant? appeared first on HIPAA Journal.

Largest Healthcare Data Breaches of 2017

This article details the largest healthcare data breaches of 2017 and compares this year’s breach tally to the past two years, which were both record-breaking years for healthcare data breaches.

2015 was a particularly bad year for the healthcare industry, with some of the largest healthcare data breaches ever discovered. There was the massive data breach at Anthem Inc., the likes of which had never been seen before. 78.8 million healthcare records were compromised in that single cyberattack, and there were also two other healthcare data breaches involving 10 million or more records. 2015 was the worst ever year in terms of the number of healthcare records exposed or stolen.

2016 was a better year for the healthcare industry in terms of the number of healthcare records exposed in data breaches. There was no repeat of the mega data breaches of the previous year. Yet, the number of incidents increased significantly. 2016 was the worst ever year in terms of the number of breaches reported by HIPAA-covered entities and their business associates. So how have healthcare organizations fared in 2017? Was 2017 another record-breaking year?

Healthcare Data Breaches Increased in 2017

The mega data breaches of 2015 were fortunately not repeated in 2017, and the decline in massive data breaches continued in 2017.

Last year, there were three breaches reported that impacted more than one million individuals and 14 breaches of more than 100,000 records.

In 2017, there was only one reported data breach that impacted more than 500,000 people and 8 breaches that impacted 100,000 or more individuals. The final total for individuals impacted by breaches last year was 14,679,461 – considerably less than the 112,107,579 total the previous year.

The final figures for 2017 cannot yet be calculated as there is still time for breaches to be reported to OCR. The HIPAA Breach Notification Rules allows covered entities up to 60 days to report data breaches of more than 500 records, so the final figures for 2017 will not be known until March 1, 2018. However, based on current data, 2017 has been a reasonably good year in terms of the number of exposed healthcare records. The current total stands at 3,286,498 records – A 347% reduction in breached records year on year.

While it is certainly good news that the severity of breaches has reduced, that only tells part of the story. Breaches of hundreds of thousands of records have reduced, but breaches of more than 10,000 records have remained fairly constant year over year. In 2015, there were 52 breaches of 10,000 or more records. That figure jumped to 82 in 2016. There were 78 healthcare data breaches in 2017 involving more than 10,000 records.

The bad news is there has been a significant rise in the number of healthcare data breaches in 2017.  As of January 4, 2017, there have been 342 healthcare security breaches listed on the OCR breach portal for 2017. It is likely more incidents will be added in the next few days.

The final total for 2015 was 270 breaches, and there were 327 breaches reported in 2016. The severity of healthcare security incidents may have fallen, but the number of incidents continues to rise year on year.
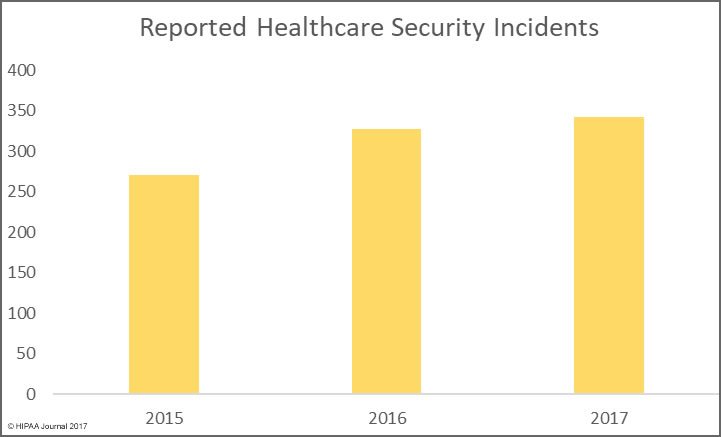
 

reported healthcare data breaches in 2017


Unfortunately, there is little evidence to suggest that the annual rise in healthcare data breaches will stop in 2018. Many cybersecurity firms have made predictions for the coming year, and they are united in the view that healthcare data breaches will continue to increase.

The 20 Largest Healthcare Breaches of 2017

The list of the 20 largest healthcare data breaches of 2017 is listed below.

Position Breached Entity Entity Type Records Exposed Cause of Breach
1 Commonwealth Health Corporation Healthcare Provider 697,800 Theft
2 Airway Oxygen, Inc. Healthcare Provider 500,000 Hacking/IT Incident
3 Women’s Health Care Group of PA, LLC Healthcare Provider 300,000 Hacking/IT Incident
4 Urology Austin, PLLC Healthcare Provider 279,663 Hacking/IT Incident
5 Pacific Alliance Medical Center Healthcare Provider 266,123 Hacking/IT Incident
6 Peachtree Neurological Clinic, P.C. Healthcare Provider 176,295 Hacking/IT Incident
7 Arkansas Oral & Facial Surgery Center Healthcare Provider 128,000 Hacking/IT Incident
8 McLaren Medical Group, Mid-Michigan Physicians Imaging Center Healthcare Provider 106,008 Hacking/IT Incident
9 Harrisburg Gastroenterology Ltd Healthcare Provider 93,323 Hacking/IT Incident
10 VisionQuest Eyecare Healthcare Provider 85,995 Hacking/IT Incident
11 Washington University School of Medicine Healthcare Provider 80,270 Hacking/IT Incident
12 Emory Healthcare Healthcare Provider 79,930 Hacking/IT Incident
13 Salina Family Healthcare Center Healthcare Provider 77,337 Hacking/IT Incident
14 Stephenville Medical & Surgical Clinic Healthcare Provider 75,000 Unauthorized Access/Disclosure
15 Morehead Memorial Hospital Healthcare Provider 66,000 Hacking/IT Incident
16 Primary Care Specialists, Inc. Healthcare Provider 65,000 Hacking/IT Incident
17 Enterprise Services LLC Business Associate 56,075 Unauthorized Access/Disclosure
18 ABCD Pediatrics, P.A. Healthcare Provider 55,447 Hacking/IT Incident
19 Network Health Health Plan 51,232 Hacking/IT Incident
20 Oklahoma Department of Human Services Health Plan 47,000 Hacking/IT Incident

The Largest Healthcare Data Breaches of 2017 Were Due to Hacking

One thing is abundantly clear from the list of the largest healthcare data breaches of 2017 is hacking/IT incidents affect more individuals than any other breach type. Hacking/IT incidents accounted for all but three of the largest healthcare data breaches of 2017.

In 2016, hacking incidents only accounted for 11 out of the top 20 data breaches and 12 of the top 20 in 2015. Hacking incidents therefore appear to be rising.
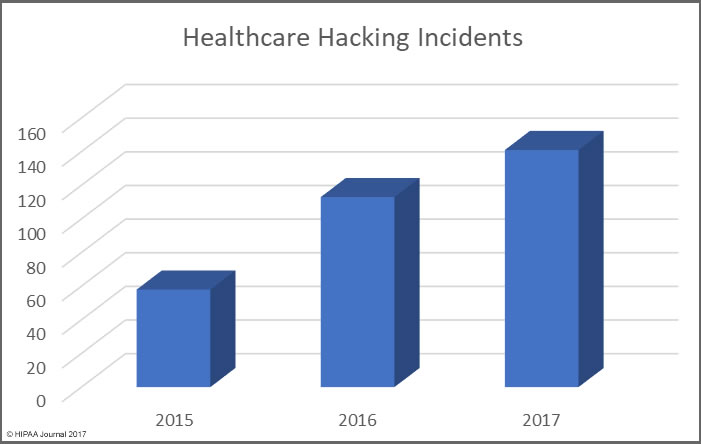
 

healthcare data breaches in 2017 (hacking)


The rise in hacking incidents can partly be explained by the increase in ransomware attacks on healthcare providers in 2017. Healthcare organizations are also getting better at discovering breaches.

Other Major Causes of Healthcare Data Breaches in 2017

Unauthorized access/disclosures continue to be a leading cause of healthcare data breaches, although there was a slight fall in numbers of these incidents in 2017. That decrease is offset by an increase in incidents involving the improper disposal of physical records and electronic devices used to store ePHI.
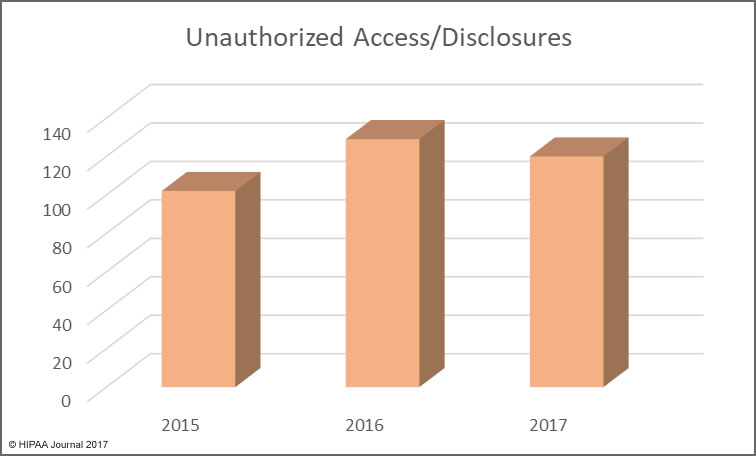
 

healthcare data breaches of 2017 (Unauthorized access/disclosures)


The use of encryption for stored data is more widespread, with many healthcare organizations having implemented encryption on all portable storage devices and laptops, which has helped to reduce the exposure of ePHI when electronic devices are stolen.
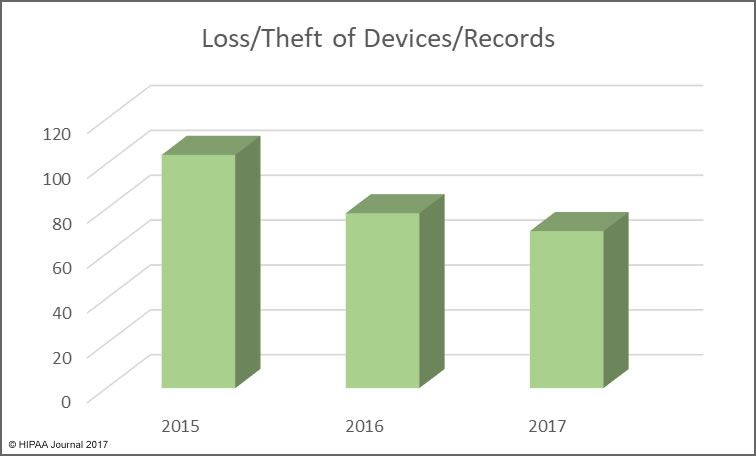
 

Healthcare Data Breaches of 2017 (loss/theft)

Minimizing the Risk of Healthcare Data Breaches

This year saw OCR publish the preliminary findings of its HIPAA compliance audits on HIPAA-covered entities. The audits revealed there is still widespread non-compliance with HIPAA Rules.

One of the biggest problems was not a lack of cybersecurity defenses, but the failure to conduct an enterprise-wide risk analysis.

Even with several layers of security, vulnerabilities are still likely to exist. Unless a comprehensive risk analysis is performed to identify security gaps, and those gaps are addressed, it will only be a matter of time before they are exploited.

Complying with HIPAA Rules will not prevent all data breaches, but it will ensure healthcare organizations achieve at least the minimum standard for data security, which will prevent the majority of healthcare data breaches.

There is a tendency to invest cybersecurity budgets in new technology, but it is important not to forget the basics. Many healthcare data breaches in 2017 could have been prevented had patches been applied promptly, if secure passwords had been chosen, and if cloud storage services and databases had been configured correctly. Many data breaches were caused as a result of employees leaving unencrypted laptops in risky locations – in unattended vehicles for instance.

Phishing remains one of the main ways that malicious actors gain access to protected health information, yet security awareness training is still not being provided frequently. As a result, employees are continuing to fall for phishing and social engineering scams. Technological solutions to block phishing emails are important, but healthcare organizations must also educate employees about the risks, teach them how to recognize scams, and reinforce training regularly. Only then will organizations be able to reduce the risk from phishing to an acceptable and appropriate level.

Insiders continue to be a major threat in healthcare. The value of data on the black market is high, and cash-strapped healthcare employees can be tempted to steal data to sell to identity thieves. Healthcare organizations can hammer the message home that data theft will be discovered and reported to law enforcement, but it is the responsibility of healthcare organizations to ensure policies and technologies are implemented to ensure that the unauthorized accessing of records – theft or snooping – is identified rapidly.  That means frequent audits of access logs and the use of automated monitoring solutions and user behavior analytics.

2017 was a bad year for ransomware attacks and extortion attempts on healthcare organizations. There is no sign that these attacks will slow in 2018, and if anything, they are likely to increase. Ensuring data is backed up will allow organizations to recover files in the event of an attack without having to pay a ransom. The rise in sabotage attacks – NotPetya for example – mean data loss is a real possibility if backups are not created.

By getting the basics right and investing in new technologies, it will be possible for the year on year rise in data breaches to be stopped. But until healthcare organizations get the basics right and comply with HIPAA Rules, healthcare data breaches are likely to continue to rise.

The post Largest Healthcare Data Breaches of 2017 appeared first on HIPAA Journal.

OIG Finds Data Security Inadequacies at North Carolina State Medicaid Agency

The Department of Health and Human Services’ Office of Inspector General (OIG) has published the findings of an audit of the North Carolina State Medicaid agency. The report shows the State agency has failed to implement sufficient controls to ensure the security of its Medicaid eligibility determination system and the security, integrity, and availability of Medicaid eligibility data.

HHS oversees the administration of several federal programs, including Medicaid. Part of its oversight of the Medicaid program involves the auditing of State agencies to determine whether appropriate system security controls have been implemented and State agencies are complying with Federal requirements.

The aim of the OIG audit was to determine whether adequate information system general controls had been implemented by the state of North Carolina to ensure its Medicaid eligibility determination system and data were secured.

The Office of North Carolina Families Accessing Services Through Technology (NC FAST) was tasked with operating North Carolina’s Medicaid eligibility determination system. NC FAST was assessed on entitywide security, access controls, configuration management, network device management, service continuity, mainframe operations, and application change control, and how those controls related to the North Carolina eligibility determination system for State fiscal year 2016.

OIG found the information security general controls were inadequate and did not meet federal requirements.

The vulnerabilities identified by OIG placed the confidentiality, integrity, and availability of North Carolina’s Medicaid eligibility data in jeopardy. The vulnerabilities could potentially be exploited by malicious actors to gain access to sensitive information. A cyberattack could also result in critical disruption of North Carolina Medicaid eligibility operations. OIG reports “the vulnerabilities are collectively and, in some cases, individually significant.”

While the vulnerabilities could be exploited, no evidence was uncovered to suggest that its system had been compromised or sensitive information had been viewed or stolen.

OIG made several recommendations to North Carolina to ensure its Medicaid eligibility determination system is appropriately secured. North Carolina must work with NC FAST to address all vulnerabilities in a timely manner and bring its information security general controls up to the required Federal standards.

North Carolina did not directly address the recommendations, but concurred with eight of the nine findings and partly agreed with one finding. North Carolina has agreed to make corrective actions that will resolve all nine security vulnerabilities identified by the auditors.

Last year, North Carolina was also found to have failed to ensure sufficient controls were implemented to ensure the security of its Medicaid claims processing systems. Those systems are managed by CRSA, Inc. OIG auditors similarly found vulnerabilities that were collectively and, in some cases, individually significant and could potentially compromise the confidentiality, integrity, or availability of data and its systems. North Carolina concurred with all recommendations and agreed to take corrective actions to address the vulnerabilities.

The post OIG Finds Data Security Inadequacies at North Carolina State Medicaid Agency appeared first on HIPAA Journal.

2017 HIPAA Enforcement Summary

Our 2017 HIPAA enforcement summary details the financial penalties paid by healthcare organizations to resolve HIPAA violation cases investigated by the Department of Health and Human Services’ Office for Civil Rights (OCR) and state attorneys general.

2017 saw OCR continue its aggressive pursuit of financial settlements for serious violations of HIPAA Rules. There have been 9 HIPAA settlements and one civil monetary penalty in 2017.

In total, OCR received $19,393,000 in financial settlements and civil monetary penalties from covered entities and business associates to resolve HIPAA violations discovered during the investigations of data breaches and complaints.

Last year, there were 12 settlements reached with HIPAA-covered entities and business associates, and one civil monetary penalty issued. In 2016, OCR received $25,505,300 from covered entities to resolve HIPAA violation cases.

Summary of 2017 HIPAA Enforcement by OCR

Listed below are the 2017 HIPAA enforcement activities of OCR that resulted in financial penalties for HIPAA-covered entities and their business associates.

Covered Entity Amount Type Violation Type
Memorial Healthcare System $5,500,000 Settlement Insufficient ePHI Access Controls
Children’s Medical Center of Dallas $3,200,000 Civil Monetary Penalty Impermissible Disclosure of ePHI
Cardionet $2,500,000 Settlement Impermissible Disclosure of PHI
Memorial Hermann Health System $2,400,000 Settlement Careless Handling of PHI
21st Century Oncology $2,300,000 Settlement Multiple HIPAA Violations
MAPFRE Life Insurance Company of Puerto Rico $2,200,000 Settlement Impermissible Disclosure of ePHI
Presense Health $475,000 Settlement Delayed Breach Notifications
Metro Community Provider Network $400,000 Settlement Lack of Security Management Process
St. Luke’s-Roosevelt Hospital Center Inc. $387,000 Settlement Unauthorized Disclosure of PHI
The Center for Children’s Digestive Health $31,000 Settlement Lack of a Business Associate Agreement

OCR’s 2017 HIPAA enforcement activities have revealed covered entities are continuing to fail to comply with HIPAA Rules in key areas: Safeguarding PHI on portable devices, conducting an organization-wide risk analysis, implementing a security risk management process, and entering into HIPAA-compliant business associate agreements with all vendors.

Throughout 2016 and 2017, many covered entities have failed to issue breach notifications promptly. In 2017, OCR took action for this common HIPAA violation and agreed its first HIPAA settlement solely for delaying breach notifications to patients.

HIPAA Desk Audits Revealed Widespread HIPAA Violations

In late 2016, OCR commenced the much-delayed second phase of its HIPAA-compliance audit program. The first stage involved desk audits of 166 HIPAA-covered entities – 103 audits on the Privacy and Breach Notification Rules, and 63 audits on the Security Rule. 41 desk audits were conducted on business associates on the Breach Notification and Security Rules.

While the full results of the compliance audits have not been released, this fall OCR announced preliminary findings from the compliance audits.

Covered entities were given a rating from 1 to 5 for the completeness of compliance efforts on each control and implementation specification. A rating of 1 signifies full compliance with goals and objectives of the standards and implementation specifications that were audited. A rating of 5 indicates there was no evidence that the covered entity had made a serious attempt to comply with HIPAA Rules.

Preliminary Findings of HIPAA Compliance Audits on Covered Entities

Listed below are the findings from the HIPAA compliance audits. A rating of 5 being the worst possible score and 1 being the best.

Preliminary HIPAA Compliance Audit Findings (2016/2017)
HIPAA Rule Compliance Controls Audited Covered Entities Given Rating of 5 Covered Entities Given Rating of 1
Breach Notification Rule (103 audits) Timeliness of Breach Notifications 15 67
Breach Notification Rule (103 audits) Content of Breach Notifications 9 14
Privacy Rule (103 audits) Right to Access PHI 11 1
Privacy Rule (103 audits) Notice of Privacy Practices 16 2
Privacy Rule (103 audits) Electronic Notice 15 59
Security Rule (63 audits) Risk Analysis 13 0
Security Rule (63 audits) Risk Management 17 1


Almost a third of covered entities failed to issue breach notifications promptly and next to no covered entities were found to be fully compliant with the HIPAA Privacy and Security Rules.

OCR has delayed the full compliance reviews until 2018. While some organizations will be randomly selected for a full review – including a site visit – OCR has stated that poor performance in the desk audits could trigger a full compliance review. Financial penalties may be deemed appropriate, especially when there has been no attempt to comply with HIPAA Rules.

Attorneys General Fines for Privacy Breaches

The HITECH Act gave state attorneys general the authority to pursue financial penalties for HIPAA violations and assist OCR with the enforcement of HIPAA Rules. Relatively few state attorneys general exercise this right. Instead they choose to pursue cases under state laws, even if HIPAA Rules have been violated.

Notable 2017 settlements with healthcare organizations and business associates of HIPAA covered entities have been listed below.

Covered Entity State Amount Individuals affected Reason
Cottage Health System California $2,000,000 More than 54,000 Failure to Safeguard Personal Information
Horizon Healthcare Services Inc., New Jersey $1,100,000 3.7 million Failure to Safeguard Personal Information
SAManage USA, Inc. Vermont $264,000 660 Exposure of PHI on Internet
CoPilot Provider Support Services, Inc. New York $130,000 221,178 Late Breach Notifications
Multi-State Billing Services Massachusetts $100,000 2,600 Failure to Safeguard Personal Information

The post 2017 HIPAA Enforcement Summary appeared first on HIPAA Journal.

Cybersecurity Best Practices for Travelling Healthcare Professionals

In its December cybersecurity newsletter, the U.S. Department of Health and Human Services’ Office for Civil Rights (OCR) offered cybersecurity best practices for travelling healthcare professionals to help them prevent malware infections and the exposure of patients’ protected health information (PHI).

Many healthcare professionals will be travelling to see their families over the holidays and will be taking work-issued devices with them on their travels, which increases the risk to the confidentiality, integrity, and availability of PHI.

Using work-issued laptops, tablets, and mobile phones in the office or at home offers some protection from cyberattacks and malware infections. Using the devices to connect to the Internet at cafes, coffee shops, hotels, and other Wi-Fi access points increases the risk of a malware infection or man-in-the-middle attack. Even charging portable devices via public USB charging points at hotels and airports can see malware transferred.

Not only will malware and cyberattacks potentially result in data on the device being exposed, login credentials can be stolen leading to a substantial data breach, or malware can be transferred to your organization’s network when you return to work.

Ensure Travel is Covered in Your Risk Analysis

HIPAA-covered entities and business associates must conduct a risk analysis to identify all risks to the confidentiality, integrity, and availability of PHI. The risk analysis must include the risks when healthcare professionals travel, be it on holiday or for business trips. Vulnerabilities and risks identified by the risk assessment must then be managed and reduced to an acceptable and appropriate level through a HIPAA-compliant risk management process.

OCR’s Suggested Cybersecurity Best Practices for Travelling Healthcare Professionals

The following cybersecurity best practices for travelling healthcare professionals are particularly relevant during the holiday season, but apply whenever work-issued devices are removed from the protection of a secured network.

Healthcare organizations that permit healthcare employees to remove work-issued devices should incorporate these cybersecurity best practices into their training programs and ensure all healthcare employees are made aware of the additional risks when travelling and how they can manage those risks.

Leave Portable Devices at the Office or at Home

If you don’t really need to take a work-issued device with you, leave it at home or at the office and make sure it is secured.

Ensure Devices are Fully Patched

All portable devices should be kept patched and up to date, although this becomes even more important when travelling and connecting to public Wi-Fi hotspots. Software, mobile apps, and operating systems should be updated to the latest versions.

Secure the Devices Using Strong Passwords

All devices should be secured with strong passwords. OCR suggests passwords should be more than 10 characters and should include numbers, letters (upper and lower case) and symbols. Passphrases can be used as they are difficult to guess but easy to remember. Multi-factor authentication should also be used if possible.

Activate Additional Security Controls

Activate additional security controls such as fingerprint readers on mobile phones to prevent data and account access in the event of loss or theft. This can buy you more time to secure accounts and change passwords if your device is stolen.

Encrypt all Sensitive Data on Your Devices

OCR suggests laptop computers should have full disk encryption to ensure data cannot be accessed in the event of loss or theft, and to remove data from portable devices if it is not required.

Create Multiple Backups of Files

It is essential that data can be recovered in the event of loss or theft of a portable device or a ransomware attack. Multiple backups should ideally be created on another device with a copy also stored securely in the cloud.

Bring Portable Chargers, Power Cords and Adaptors

Connecting to public charging points in airports and hotels can easily introduce malware. Avoid USB charging points, and charge devices using a portable charging pack or by plugging into the mains supply. If charging ports must be used, only connect after devices have been powered down.

Avoid Public Wi-Fi Hotspots

Avoid all public Wi-Fi networks as they are unlikely to be secure. If you do need to connect to Wi-Fi when travelling, always connect to the Internet via a VPN.

Turn Off Auto Connect for Bluetooth and Wi-Fi

Ensure your portable devices do not automatically connect to Wi-Fi networks and turn off Bluetooth connectivity.

Use Different PIN Numbers

Always use a unique PIN number for each of your devices. Never reuse a PIN anywhere else, such as on the hotel safe.

Never Leave Devices Unprotected

If you cannot lock a portable electronic device in a safe, take it with you. Any possible hiding spot in a hotel room will be checked by thieves. Devices should only ever be taken in hand luggage, never packed in a case that is put in the hold.

Use Geo-Location with Care

While geolocation services have their uses, they can also alert thieves that you are not at home. Consider turning off these services on social media networks when you are away, and avoid posting photos taken on your travels until you return home.

The post Cybersecurity Best Practices for Travelling Healthcare Professionals appeared first on HIPAA Journal.

HIPAA Compliant Email Providers

HIPAA-covered entities must ensure protected health information (PHI) transmitted by email is secured to prevent unauthorized individuals from intercepting messages, and many choose to use HIPAA compliant email providers to ensure appropriate controls are applied to ensure the confidentiality, integrity, and availability of PHI.

There are many HIPAA compliant email providers to choose from that provide end-to-end encryption for messages. Some of the solutions require software to be hosted on your own infrastructure; others take care of everything. Changing email provider does not necessarily mean you have to change your email addresses. Many services allow you to keep your existing email addresses and send messages as you normally would from your desktop.

All HIPAA compliant email providers must ensure their solution incorporates all of the safeguards required by the HIPAA Security Rule. The solutions need to have access controls 164.312(a)(1), audit controls 164.312(b), integrity controls 164.312(c)(1), authentication 164.312(d), and PHI must be secured in transit 164.312(e)(1).

Provided that an email service provider incorporates all of those controls, the service can be considered HIPAA-compliant. However, it is also necessary for an email service provider to enter into a contract with a HIPAA-covered entity in the form of a business associate agreement. Only then can the email service be used.

HIPAA-covered entities should bear in mind that HIPAA-compliant email is not the responsibility of the service provider. The service provider must only ensure appropriate safeguards are incorporated. It is the responsibility of the covered entity to ensure the solution is configured correctly, that staff are trained on the use of email and are made aware of the allowable uses and disclosures of PHI.

An email service alone will not satisfy all HIPAA requirements for email. Staff should also receive training on security awareness and be made aware of the threats that can arrive in inboxes. Technologies should also be implemented to reduce the risk of email-based attacks such as phishing. Some email service providers, but not all, scan inbound messages and block spam, malware and phishing emails.

Is Encryption for Email Mandatory?

That is a question asked by many healthcare organizations. While HIPAA compliant email providers encrypt all emails in transit, encryption is not mandatory. The HIPAA Security Rule only requires organizations to assess the need for encryption. A HIPAA-covered entity does not need to encrypt emails, if an alternative and equivalent control is used in its place.

One such control is the use of a secure email server located behind a firewall. In such cases, provided a risk assessment has been conducted and the reasons for not encrypting emails has been documented, encryption would not be required on all internal emails. Encryption would also not be necessary when sending emails to patients who have authorized a covered entity to communicate with them via email.

However, since most healthcare organizations need to submit payment claims via email, contact other healthcare organizations and refer patients, it is necessary to send emails outside the protection of the firewall. In such cases, encryption is necessary.

There are considerable risks sending sensitive information via email. Email is not a secure way of sending data. Emails must be created on one machine, be sent to an outbound email server, traverse the Internet, arrive at the recipient’s email server, before being delivered to the recipient’s device. Copies of emails can be on at least four different machines, and messages can easily be intercepted in transit.

The Department of Health and Human Services has already issued fines to covered entities that have used email services that are not HIPAA compliant. Phoenix Cardiac Surgery paid a $100,000 penalty for using insecure Internet-based email.

List of HIPAA Compliant Email Providers

Our list of HIPAA compliant email providers has been compiled to save you time in your search for a suitable email service provider. The list of HIPAA compliant email providers is not exhaustive. There are many other service providers that offer email services for healthcare organizations that meet the requirements of HIPAA. However, the list below is a good starting point.

All of the following providers offer a HIPAA-compliant email service and are willing to sign a business associate agreement.

  • Hushmail for Healthcare
  • VM Racks
  • NeoCertified
  • Paubox
  • Virtru
  • Atlantic
  • LuxSci
  • Apsida Mail
  • Protected Trust
  • MaxMD
  • EmailPros
  • MD OfficeMail
  • Delivery Trust from Identillect Technologies

The post HIPAA Compliant Email Providers appeared first on HIPAA Journal.

New Malware Detections at Record High: Healthcare Most Targeted Industry

Throughout 2017, the volume of new malware samples detected by McAfee Labs has been steadily rising each quarter, reaching a record high in Q3 when 57.6 million new malware samples were detected. On average, in Q3 a new malware sample was detected every quarter of a second.

In the United States, the healthcare industry continues to be the most targeted vertical, which along with the public sector accounted for more than 40% of total security incidents in Q3. In Q3, account hijacking was the main attack vector, followed by leaks, malware, DDoS, and other targeted attacks.

There were similar findings from the recent HIMSS Analytics/Mimecast survey which showed email related phishing attacks were the greatest cause of concern among healthcare IT professionals, with email the leading attack vector.

In Q3, globally there were 263 publicly disclosed security breaches – a 15% increase from last quarter – with more than 60% of those breaches occurring in the Americas. Malware attacks increased 10% since last quarter bringing the total new malware samples in the past four quarters to 781 million – a 27% increase in the space of a year.

Ransomware continues to be a favored moneymaker for cybercriminals, with the number of new ransomware samples increasing by 36% in Q3 – 14% more than the previous quarter. In total, 12.2 million samples of ransomware were detected – a 44% increase over the past four quarters.  One notable ransomware variant was Lukitus – a new form of Locky ransomware that appeared in Q3. The campaign detected by McAfee involved an astonishing 23 million spam emails in the first 24 hours alone.

While not the biggest threat in Q3, fileless malware threats are still a major cause for concern. Script-based malware – written in VBS, JavaScript, PowerShell or PHP – has been steadily increasing over the past two years. The malware is easy to obfuscate and difficult to detect, and is increasingly being used in malware campaigns, with some campaigns consisting entirely of script-based malware.

McAfee reports that while there was a 36% fall in JavaScript malware since Q2, the level is still higher than at any point in 2016 and Q3 saw a 119% increase in PowerShell malware.

“Although many cyberattacks continue to rely on the exploitation of basic security vulnerabilities, exposures, and user behaviors, fileless threats leverage the utility of our own system capabilities,” said Vincent Weafer, Vice President for McAfee Labs. “By leveraging trusted applications or gaining access to native system operating tools such as PowerShell or JavaScript, attackers have made the development leap forward to take control of computers without downloading any executable files, at least in the initial stages of the attack.”

There was also a notable rise in mobile malware, with 21.1 million samples detected – 10% higher than Q2, the increase was largely due to a major rise in Android screen-locking ransomware variants. Macro malware increased by 8% in Q3, while Mac malware saw an increase of 7%. Web-based threats also increased significantly in Q3.

While malware continues to be a major threat, the Carbon Black’s 2017 Threat Report indicates 52% of attacks are non-malware related. Non-malware attacks are now increasing at a rate of 6.8% per month.

The financial services, healthcare providers, and retail stores were the verticals most affected by malware-related cyberattacks in 2017 according to Carbon Black. The main threats are the Kryptik Trojan, Strictor ransomware, the Nemucod downloader, the Emotet banking Trojan, and the Skeeyah Trojan. Carbon Black reports a 328% increase in attacks on endpoints in 2017 alone.

While the healthcare industry has had its fair share of ransomware attacks, it is well down the list of industries targeted with ransomware, coming in 9th out of 10 industries with just 4.6% of the total. The leading targets being tech firms, government organizations/NPOs and legal firms.

Ransomware will continue to be the dominant form of cybercrime in 2018, according to the report. Carbon Black estimates revenues from ransomware will rise to $5 billion by the end of the year, compared to just $24 million in 2015.

The post New Malware Detections at Record High: Healthcare Most Targeted Industry appeared first on HIPAA Journal.

Study Reveals Cybersecurity in Healthcare is Not Being Taken Seriously Enough

A recent survey by Black Book Research indicates the healthcare industry is not doing enough to tackle the threat of cyberattacks, and that cybersecurity is still not being taken seriously enough.

The survey was conducted on 323 strategic decision makers at U.S. healthcare firms in Q4, 2017. Even though the threat of cyberattacks is greater than ever, and the healthcare industry will remain the number one target for cybercriminals in 2018, only 11% of healthcare organizations plan to appoint a cybersecurity officer in 2018 to take charge of security. Currently 84% of provider organizations do not have a dedicated leader for cybersecurity.

Payer organizations are taking cybersecurity more seriously. 31% have appointed a manager for their cybersecurity programs and 44% said they would make an appointment next year. Overall, 15% of all surveyed organizations said they have a chief information security office in charge of cybersecurity.

The survey also revealed that cybersecurity best practices are not being widely adopted in the healthcare industry. Even though HIPAA calls for regular risk assessments to be conducted, 54% of respondents said risk assessments were not conducted regularly at their organization, while 39% said they do not carry out firewall penetration tests.

Further, while there have been increases in budgets, it would appear that cybersecurity is a low priority. 89% of respondents said that in 2018, budgeted IT funds were primarily being directed to business functions with provable business cases. Only a small percentage of those budgets are being allocated to cybersecurity.

In order for cybersecurity goals to be met, there needs to be C-Suite involvement, yet 92% of respondents said that cybersecurity and data breaches were not major talking points in board meetings. “Cybersecurity has to be a top-down strategic initiative as it’s far too difficult for IT security teams to achieve their goals without the board leading the charge,” said Doug Brown, Managing Partner of Black Book.

With two weeks left in December, there have been 331 healthcare data breaches reported to the Department of Health and Human Services’ Office for Civil Rights. The total for 2016 was 327 breaches, having increased from 270 breaches in 2015. At the current rate, the milestone of 350 breaches for the year may even be reached. There is also no indication that the year on year increases in data breaches will not continue in 2018.

“The critical role of medical facilities, combined with poor security practices and lack of resources, make them vulnerable to financially and politically motivated attacks,” said Brown.

Unless more is done to ensure cybersecurity goals are met, next year is likely to be yet another record-breaking year for healthcare data breaches.

The post Study Reveals Cybersecurity in Healthcare is Not Being Taken Seriously Enough appeared first on HIPAA Journal.

More than 1,000 Lexmark Printers Open to Attack Due to Misconfiguration

Researchers at NewSky Security have discovered more than a thousand Lexmark printers have been misconfigured by users and are accessible over the Internet. Many of the printers are used businesses, universities, and even the U.S. Government, yet they can be accessed via the Internet without the need for a password.

The lack of security means unauthorized individuals can connect to the printers, which in some cases are connected to sensitive networks. Attacking those printers requires no skill and is a quick and easy process. Any individual can remotely access and take full control of the device. It would be possible for anyone to set a password for the printer, add a backdoor and capture print jobs. NewSky Security says the lack of an administrator password is gross negligence by users.

The researchers identified the misconfigured Lexmark printers by performing a search on the search engine Shodan. Of the 1,475 unique IPs found, 1,123 printers had no security at all and only 24% redirected the researchers to a login page. The researchers explained, “an attacker can take control of these poorly configured devices without any impressive hacking skills.”

One of the unsecured printers was being used by the Lafayette Consolidated Government, with the majority belonging to universities. NewSky is currently reaching out to organizations affected to alert them to the problem.

The researchers explained that they have focused on printer security because it is still largely neglected by end users.

This is not the first time printer misconfigurations have been discovered by the researchers. Similar misconfigurations were identified on Brother printers in October, which saw administrative panels accessible over ports 80 and 443.

It is possible that many other brands of Internet-enabled printers are similarly exposed. Organizations that have purchased Internet-enabled printers should ensure that the devices are configured correctly, that they are isolated from the public Internet, that default passwords are changed, and strong admin passwords set on the devices. Open ports should be closed and unnecessary services stopped.

The post More than 1,000 Lexmark Printers Open to Attack Due to Misconfiguration appeared first on HIPAA Journal.