Healthcare Cybersecurity

IT Firm Ransomware Attack Prevents Nursing Homes and Acute Care Facilities from Accessing Medical Records

Virtual Care Provider Inc. (VCP), a Wisconsin-based provider of internet and email services, data storage, cybersecurity, and other IT services has experienced a ransomware attack that has resulted in the encryption of medical records and other data the firm hosts for its clients. Its clients include 110 nursing home operators and acute care facilities throughout the United States. Those entities have been prevented from accessing critical patient data, including medical records. The company provides support for 80,000 computers, in around 2,400 facilities in 45 states.

The attack involved Ryuk ransomware, a ransomware strain that has been used to attack many healthcare organizations and managed IT service providers in the United States in recent months. The ransomware is typically deployed as a secondary payload following an initial Trojan download. The attacks often involve extensive encryption and cause major disruption and huge ransom demands are often issued. This attack is no different. A ransom demand of $14 million has reportedly been issued, which the company has said it cannot afford to pay.

According to Brian Krebs of KrebsonSecurity, who spoke to VCP owner and CEO Karen Christianson, the attack has affected virtually all of the company’s core offerings, including internet access, email, stored patient records, clients’ phone systems, billing, as well as the VCP payroll system.

The attack has meant acute care facilities and nursing homes cannot view or update patient records and order essential drugs to ensure they are delivered in time. Several small facilities are unable to bill for Medicaid, which will force them to close their doors if systems are not restored before December 5th in time for claims to be submitted. VCP has prioritized restoring its Citrix-based virtual private networking platform to allow clients to access patients’ medical records.

The attack commenced on November 17, 2019 and VCP is still struggling to restore access to client data and cannot process payroll for almost 150 employees. Christianson is concerned that the attack could potentially result in the untimely demise of some patients and may force her to permanently close her business.

KrebsonSecurity reports that the initial attack may date back to September 2018 and likely started with a TrickBot or Emotet infection, with Ryuk deployed as a secondary payload.

The post IT Firm Ransomware Attack Prevents Nursing Homes and Acute Care Facilities from Accessing Medical Records appeared first on HIPAA Journal.
House Committee Leaders Demand Answers from Google and Ascension on Project Nightingale Partnership

Leaders of the House Committee on Energy and Commerce are seeking answers from Google and Ascension on Project Nightingale. The Department of Health and Human Services’ Office for Civil Rights has also confirmed that an investigation has been launched to determine if HIPAA Rules have been followed.

The collaboration between Google and Ascension was revealed to the public last week. The Wall Street Journal reported that Ascension was transferring millions of patient health records to Google as part of an initiative called Project Nightingale.

A whistleblower at Google had contacted the WSJ to raise concerns about patient privacy. A variety of internal documents were shared with reporters on the extent of the partnership and the number of Google employees who had access to Ascension patients’ data. Under the partnership, the records of approximately 50 million patients will be provided to Google, 10 million of which have already been transferred.

According to the WSJ report, 150 Google employees are involved with the project and have access to patient data. The whistleblower stated that those individuals are able to access and download sensitive patient information and that patients had not been informed about the transfer of their data in advance. Understandably, the partnership has raised concerns about patient privacy.

Both Google and Ascension released statements about the partnership after the WSJ story was published, confirming that Google was acting as a business associate of Ascension, had signed a business associate agreement, and that it was in full compliance with HIPAA regulations. Under the terms of the BAA, which has not been made public, Google is permitted access to patient data in order to perform services on behalf of Ascension for the purpose of treatment, payment, and healthcare operations.

Google will be analyzing patient data and using its artificial intelligence and machine learning systems to develop tools to assist with the development of patient treatment plans. Google will also be helping Ascension modernize its infrastructure, electronic health record system, and improve collaboration and communication. Google has confirmed in a blog post that it is only permitted to use patient data for purposes outlined in the BAA and has stated that it will not be combining patient data with any consumer data it holds and that patient data will not be used for advertising purposes.

Democratic leaders of the House Committee on Energy and Commerce wrote to Google and Ascension on November 18, 2019 requesting further information on the partnership. The inquiry is being led by House Energy Committee Chairman, Frank Pallone Jr. (D-New Jersey). The letters have also been signed by Chairwoman of the Subcommittee on Health, Anna Eshoo (D-California), Subcommittee on Consumer Protection and Commerce Chair, Jan Schakowsky (D-Illinois), and Subcommittee on Oversight and Investigations Chair, Diana DeGette (D-Colorado).

In the letters, the Committee leaders have requested information on the “disturbing initiative” known as Project Nightingale.

“While we appreciate your efforts to provide the public with further information about Project Nightingale, this initiative raises serious privacy concerns. For example, longstanding questions related to Google’s commitment to protecting the privacy of its own users’ data raise serious concerns about whether Google can be a good steward of patients’ protected health information.”

Ascension’s decision not to inform patients prior to the transfer of protected health information has also raised privacy concerns, as has the number of Google employees given access to the data. Further, employees of Google’s parent company Alphabet also have access to Ascension data.

The Committee leaders have requested a briefing by no later than December 6, 2019 about the types of data being used, including the data being fed into its artificial intelligence tools, and the extent to which Google and Alphabet employees have access to the data. The Committee leaders also want to know what steps have been taken to protect patient information and the extent to which patients have been informed.

The Department of Health and Human Services’ Office for Civil Rights has also confirmed that it has launched an investigation into the partnership. Its investigation is primarily focused on how data is being transferred, the protections put in place to safeguard the confidentiality, integrity, and availability of protected health information, and whether HIPAA Rules are being followed. Google has stated it will be cooperating fully with the OCR investigation.

The post House Committee Leaders Demand Answers from Google and Ascension on Project Nightingale Partnership appeared first on HIPAA Journal.

Update Issued on Unsecured PACS as Exposed Medical Image Total Rises to 1.19 Billion

It has been 60 days since Greenbone Networks uncovered the extent to which medical images in Picture Archiving and Communication Systems (PACS) servers are being exposed online. In an updated report, the German vulnerability analysis and management platform provider has revealed the problem is getting worse, not better.

Picture Archiving and Communication Systems (PACS) servers are extensively used by healthcare providers for archiving medical images and sharing those images with physicians for review, yet many healthcare providers are not ensuring their PACS servers have appropriate security. Consequently, medical images (X-Ray, MRI, CT Scans), along with personally identifiable patient information, is being exposed over the Internet. Anyone who knows where to look and how to search for the files can find them, view them and, in many cases, download the images without any authentication required. The images are not accessible due to software vulnerabilities. Data access is possible because of the misconfiguration of infrastructure and PACS servers.

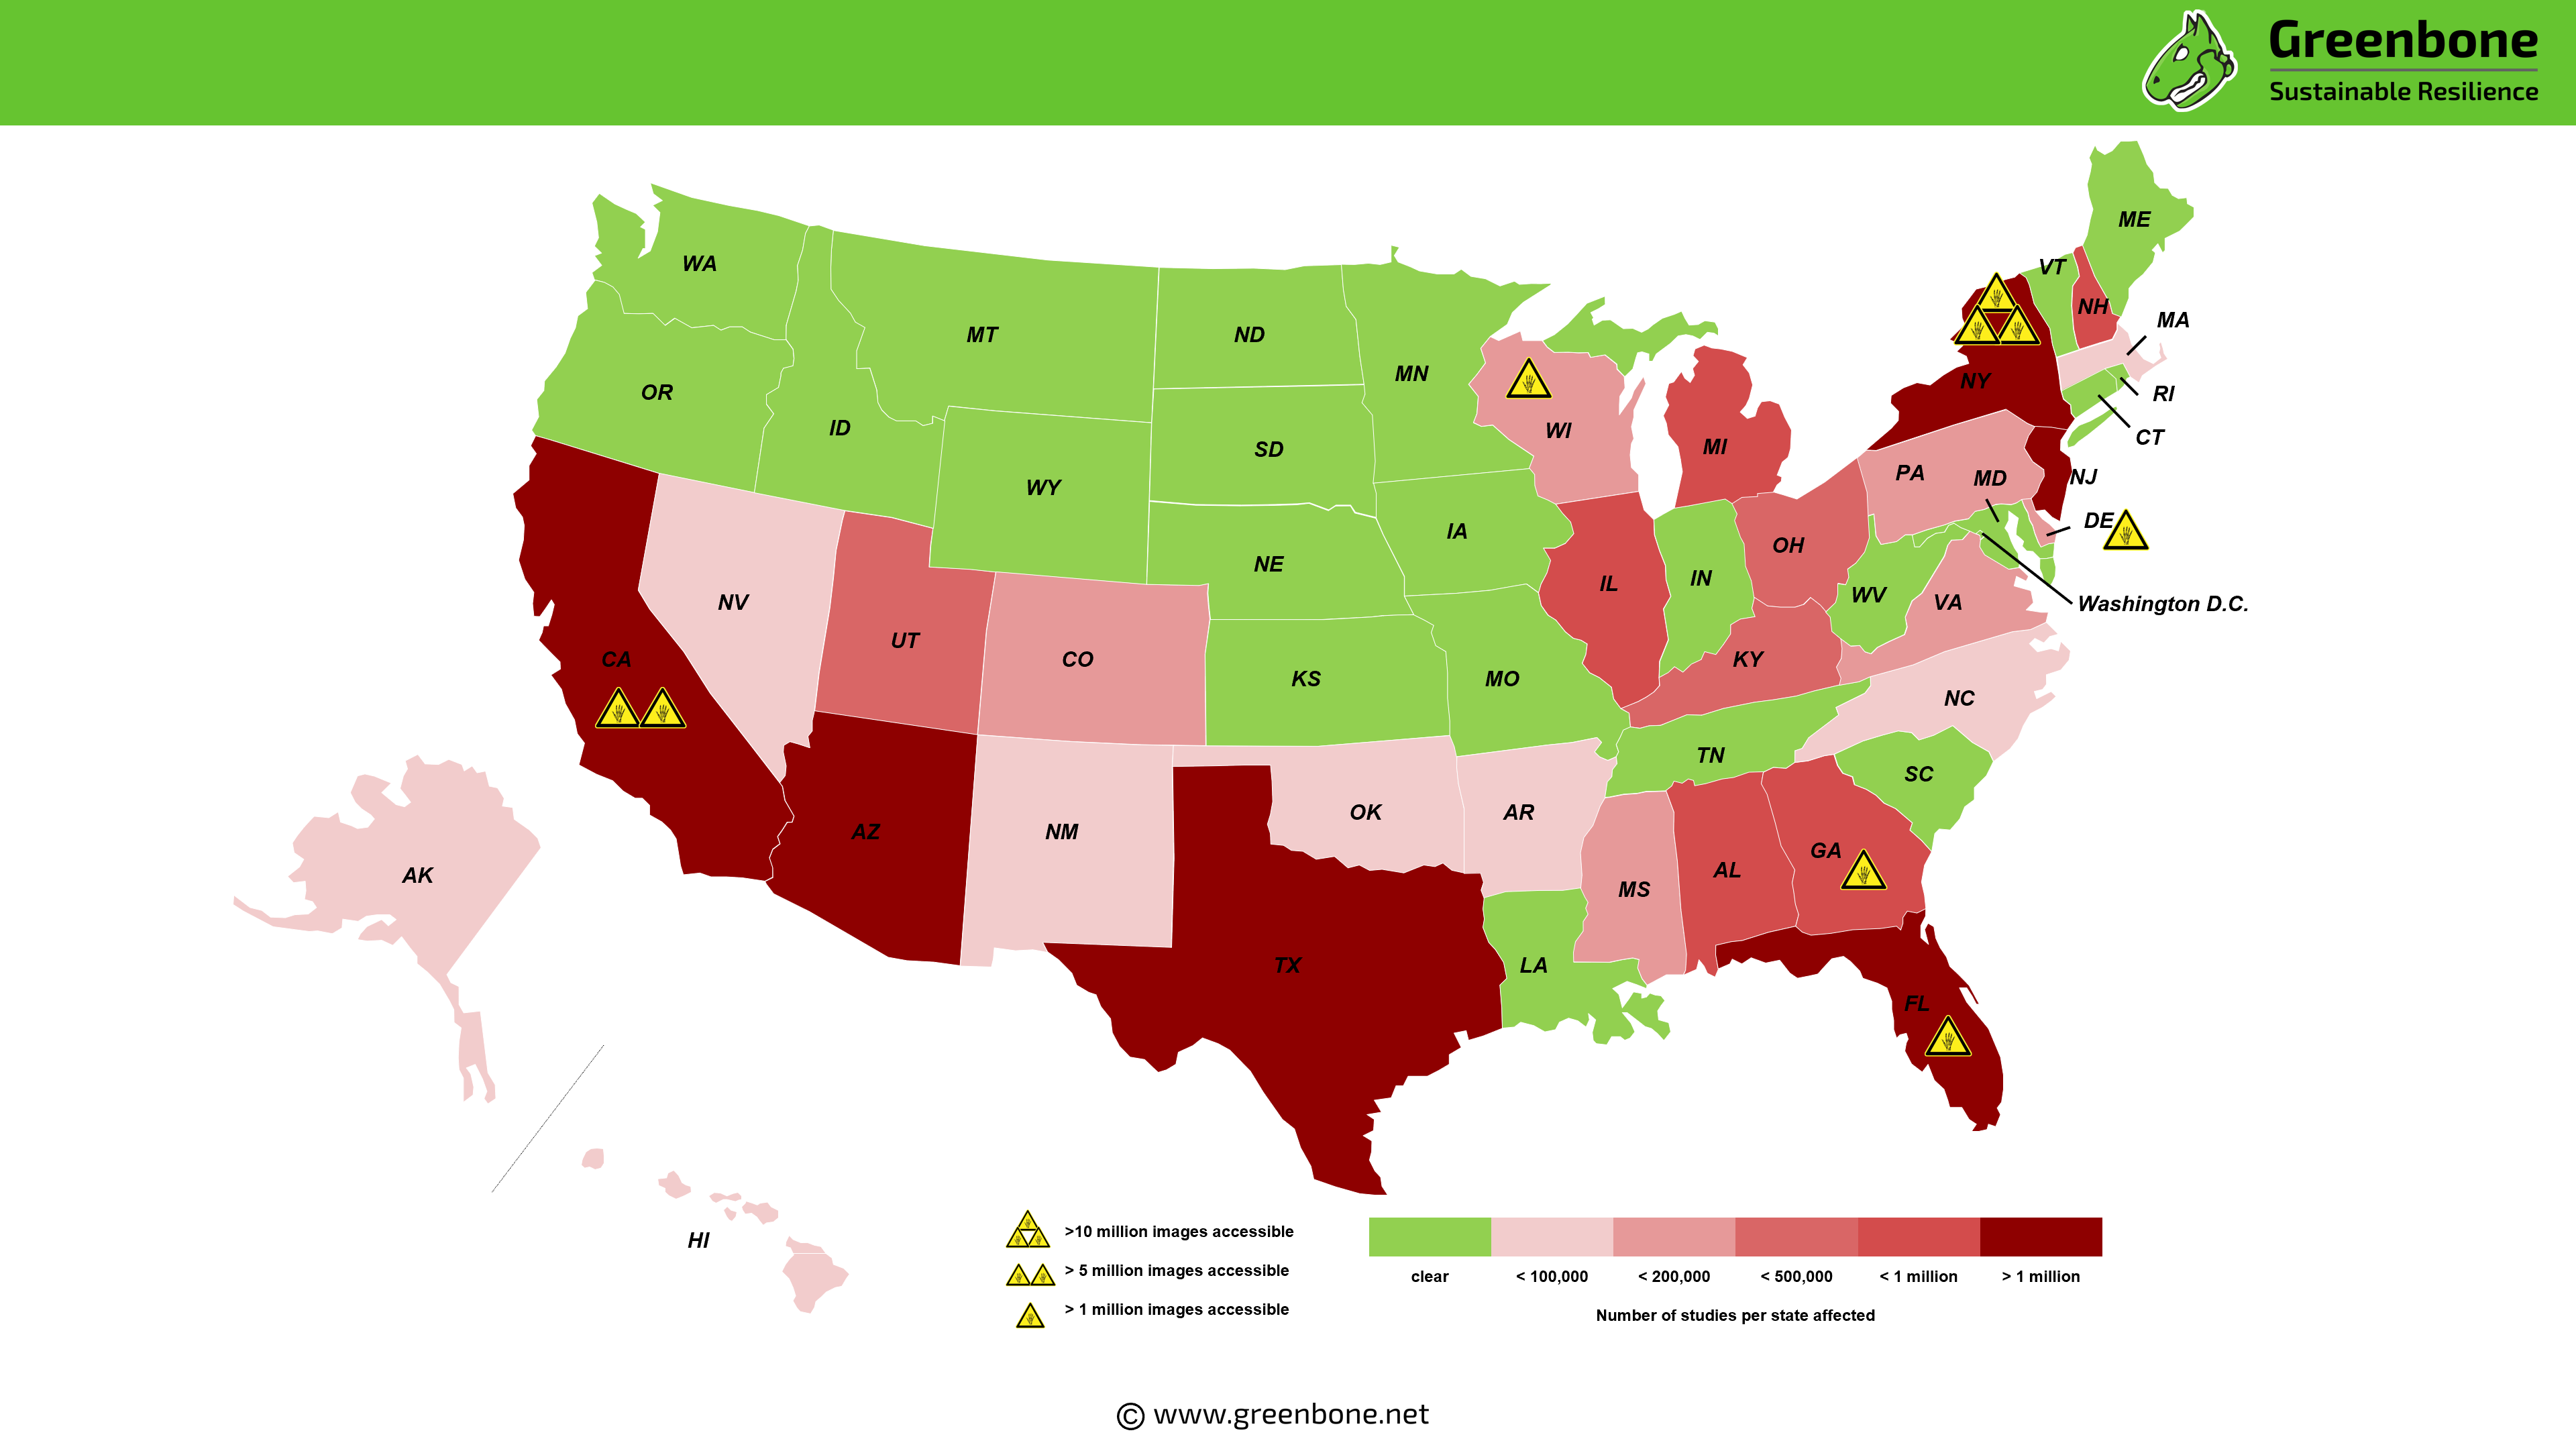
Between July and September 2019, Greenbone Networks conducted an analysis to identify unsecured PACS servers around the globe. The study shed light on the scale of the problem. In the United States, 13.7 million data sets were found on unsecured PACS servers, which included 303.1 million medical images of which 45.8 million were accessible. The discovery was widely reported in the media at the time, and now further information on the scale of the problem has been released.

On Monday, November 18, Greenbone Networks issued an updated report that shows globally, 1.19 billion medical images have now been identified, increasing the previous total of 737 million by 60%. The results of 35 million medical examinations are online, up from 24 million.

In the United States, the researchers found 21.8 million medical examinations and 786 million medical images. 114.5 of those images were accessible and there are 15 systems that allow unprotected Web/FTP access and directory listing. In one PACS alone, the researchers found 1.2 million examinations and 61 million medical images. The researchers had full access to the data, which included the images and associated personally identifiable information. Greenbone Networks has confirmed that in the 24 hours prior to publication of its latest report, data access was still possible. “For most of the systems we scrutinized, we had – and still have – continued access to the personal health information,” explained Greenbone Networks CMS, Dirk Schrader.

Exposed Medical Images on PACS Servers. Source: Greenbone Networks

Earlier in November, Sen. Mark. R. Warner wrote to HHS’ Office for Civil Rights Director, Roger Severino, expressing concern over the apparent lack of action from OCR over the exposed files. Far from the situation improving following the announcement about the exposed data, it appears that very little is being done to secure the PACS servers and stop further data exposure.

The types of information in the images, which is classed as Protected Health Information (PHI) under HIPAA, includes names, dates of birth, examination dates, scope of the investigations, imaging procedures performed, attending physicians’ names, location of scan, number of images and, for 75% of the images, Social Security numbers.

The exposure of this data places patients at risk of identity theft and fraud, although there are other risks. Previously, security researchers have shown that flaws in the DICOM image format allows the insertion of malicious code. Images could therefore be downloaded, have malicious code inserted, and be uploaded back to the PACS. This could all be down without the knowledge of the data owner. For the purpose of the study, Greenbone Networks only investigated reading access, not image manipulation and upload.

Images were accessed and viewed using the RadiAnt DICOM Viewer. Instructions on configuration to view images using the RadiAnt DICOM Viewer are freely available online, as is the viewer and the list of IPs where the images are stored.

Greenbone Networks estimates that the exposed medical images and PHI has a value in excess of $1 billion dollars. The data could be used for a variety of nefarious purposes including identity theft, social engineering and phishing, and blackmail.

The exposure of the data is in violation of the Health Insurance Portability and Accountability Act (HIPAA), the EU’ s General Data Protection Regulation (GDPR), and many other data privacy and security laws. The data relates to more individuals in more than 52 countries.

The post Update Issued on Unsecured PACS as Exposed Medical Image Total Rises to 1.19 Billion appeared first on HIPAA Journal.

Vulnerability Identified in Philips IntelliBridge EC40/80 Hubs

A vulnerability has been identified in the Philips IntelliBridge EC40/80 hub which could allow an attacker to gain access to the hub and execute software, modify files, change the system configuration, and gain access to identifiable patient information.

Philips IntelliBridge EC40/80 hubs are used to transfer medical device data from one format to another, based on set specifications. The hub does not alter the settings or parameters of any of the medical devices to which it connects.

The vulnerability could be exploited by an attacker to capture and replay a session and gain access to the hub. The flaw is due to the SSH server running on the affected products being configured to allow weak ciphers.

The vulnerability would only require a low level of skill to exploit, but in order to exploit the flaw an attacker would need to have network access. The flaw – CVE-2019-18241 – has a CVSS v3 base score of 6.3 out of 10 – Medium severity.

The flaw was reported to Philips by New York-Presbyterian Hospital’s Medical Technology Solutions team, and under its responsible vulnerability disclosure policy, Philips reported the vulnerability to the DHS Cybersecurity Infrastructure Security Agency.

The vulnerability is present in all versions of the EC40 and EC80 hubs and will be addressed in a new release, which will not be available until the end of Q3, 2020.

Until Philips issues the new release, users of the affected hubs have been advised to implement the following mitigation measures to reduce the potential for exploitation.

  1. Only operate the hub within Philips authorized specifications, using Philips approved software, configurations, system services, and security configurations
  2. There is no clinical requirement for these devices to communicate outside the Philips clinical network. The devices should be logically or physically separated from the hospital network.
  3. Users should block access to the SSH port. SSH is not meant to be used for clinical purposes, only for product support.
  4. Use a long and complex SSH password and make sure password distribution is controlled to ensure SSH is used via physical access only.

The post Vulnerability Identified in Philips IntelliBridge EC40/80 Hubs appeared first on HIPAA Journal.

Proofpoint Q3 2019 Threat Report Shows Increase in RAT and Banking Trojan Activity

The Proofpoint Q3 2019 Threat Report has been released. The report provides insights into the main threats in Q3, 2019 and reveals the changing tactics, techniques, and procedures used by cybercriminals.

The data for the report comes from an analysis of more than 5 billion email messages, hundreds of millions of social media posts, and over 250 million captured malware samples.

The report reveals scammers now favor embedded hyperlinks over attachments for spreading malware. 88% of malicious emails that were used to install malware used malicious URLs. This tactic is preferred as it makes it easier to bypass email security defenses.

Proofpoint notes that ransomware still poses a significant threat, but it was noticeably absent from most email campaigns. Proofpoint suggests that the fall in the value of cryptocurrencies is making it harder for threat actors to monetize their ransomware campaigns. Greater rewards can be gained through other types of malware, such as remote access Trojans (RATs) and banking Trojans.

RATs and banking Trojans were the main malware threats in Q3, 2019, accounting for 15% and 45% of all malware attacks, up from 6% and 23% respectively from the previous quarter. The most common banking Trojans were The Trick (37%), IcedID (26%), Ursnif (20%) and Dridex (14%). The most commonly used RATs were FlawedAmmyy (45%), FlawedGrace (30%), NanoCore RAT (12%), and LimeRAT (5%).

In contrast to ransomware, these malware variants are much quieter, have persistence, and can be used for extended periods to steal data, send spam email, and mine cryptocurrencies. Downloaders accounted for 13% of the total malicious payloads, followed by botnets (12%), and keyloggers (7%) and credential stealers (7%).

The change in spam stats can be attributed, in the main, to the disappearance of the Emotet botnet in May. Spamming activity did not recommence until the third week in September, which was the main reason why the total volume of malicious messages fell by 39% in Q3, 2019. Despite being absent for most of the quarter, the Emotet botnet still accounted for almost 12% of malicious payloads for the entire quarter.

Q3, 2019 saw an increase in web-based threats and malvertising redirects to exploit kits such as RIG and Fallout. A high percentage of traffic to the exploit kits came through the Keitaro traffic distribution system (TDS). Proofpoint notes that Keitaro abuse is driving the increase in exploit kit activity. It can also intelligently route traffic to legitimate websites if sandbox signals are detected to prevent the detection of malicious redirects. Confirming that HTTPS does not mean a website is genuine, 26% of malicious domains had valid SSL certificates, up from 20% in Q1, 2019.

Sextortion scams are still widely used. While these scams use social engineering techniques to scare people into making a payment, Proofpoint notes the emergence of malware that is capable of recording users’ online activities, which suggests that future campaigns may feature actual evidence of adult activity> That would greatly increase the attackers’ success rate.

One malware variant that has been tooled for this is PsiBot. PsiBort has had a new PornModule added. This module contains a list of words associated with adult content and monitors the open window titles in browsers. When there is a match, audio and video via the microphone and webcam are recorded and saved in an AVI file that is exfiltrated to the attacker’s C2.

The post Proofpoint Q3 2019 Threat Report Shows Increase in RAT and Banking Trojan Activity appeared first on HIPAA Journal.

Sen. Warner Demands Answers from HHS Over Apparent Lack of Response to Major PACS Data Breach

U.S. Senator, Mark. R. Warner (D-VA) has written to the Director of the HHS’ Office for Civil Rights, Roger Severino, expressing concern over the HHS response to the mass exposure of medical images by U.S. healthcare organizations.

Sen. Warner is the Vice Chairman of the Senate Intelligence Committee and co-founder of the Senate Cybersecurity Caucus. This is the latest in a series of communications in which he has voiced concerns about cybersecurity failures that have compromised the personal and private information of Americans. In February, Sen. Warner demanded answers from HHS agencies, NIST, and healthcare associations about healthcare cybersecurity following the continued increase in healthcare data breaches.

His recent letter to OCR was in response to a September 17, 2019 report about the exposure of millions of Americans’ medical images that were stored in unsecured picture archiving and communications systems (PACS).

The report detailed the findings of an investigation by ProPublica, German public broadcaster Bayerischer Rundfunk, and vulnerability and analysis firm, Greenbone Networks, which revealed almost 400 million medical images could be freely downloaded from the internet without authentication.  Sen. Warner pointed out that at the time of writing the letter, “for all U.S. territories there are 114.5 million images accessible, 22.1 million patient records, and 400,000 Social Security numbers, impacting an estimated 5 million patients in 22 states.”

Sen. Warner stated in the letter that the exposure of the medical images not only has potential to cause harm to individuals, it is also damaging to national security. The types of exposed information could potentially be used by cybercriminals in phishing campaigns and for other malicious attacks, such as those aimed at spreading malware. Flaws in the DICOM protocol could be exploited to incorporate malicious code into medical images. Nation state actors or cybercriminal groups could have downloaded the images, inserted malicious code, and then uploaded the images without being detected.

One of the U.S. firms implicated in the ProPublica report was TridentUSA Health Services and one of its affiliates, MobileX USA. In September 2019, following publication of the report, Sen. Warner wrote to TridentUSA Health Services demanding answers about its cybersecurity practices and how the data of millions of Americans, which the company was responsible for keeping private, came to be exposed online and required no password or other means of authentication to access.

In his letter to OCR, Sen. Warner explained that TridentUSA Health Services, a HIPAA-covered entity, responded to his letter and stated it had passed an HHS Security Rule audit in March 2019. That audit was passed even though at the time of the audit medical images under its control were exposed online and could be freely accessed over the internet.

“As your agency aggressively pushes to permit a wider range of parties (including those not covered by HIPAA) to have access to the sensitive health information of American patients without traditional privacy protections attaching to that information, HHS’s inattention to this particular incident becomes even more troubling,” wrote Warner.

The exposure of PACS data was reported to US-CERT by the German Federal Office for Information Security. US-CERT made contact with Greenbone Networks and confirmed the exposed data had been received and said that the matter would be reported to the HHS. Greenbone Networks had no contact from HHS and no further contact from US-CERT.

The researchers in Germany also demonstrated to Sen. Warner that even on October 15, 2019, several US-based PACS have open ports that support unencrypted communications protocols. Those unsecured PACS could be accessed without authentication and a wide range of medical images could be viewed and downloaded, including X-rays and mammograms that contain sensitive patient information such as names and Social Security numbers. Those images and personal information were still accessible freely online on the date of writing the letter (Nov 8, 2019).

“As of writing this letter, TridentUSA Health Services is not included on your breach portal website and I have seen no evidence that, once contacted by US-CERT, you acted on that information in a meaningful way,” wrote Sen. Warner.

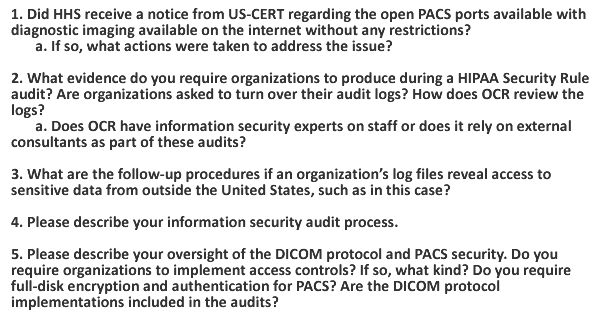
Sen. Warner has demanded answers to 5 questions:

The post Sen. Warner Demands Answers from HHS Over Apparent Lack of Response to Major PACS Data Breach appeared first on HIPAA Journal.

Microsoft Issues Fresh Warning to Patch BlueKeep Vulnerability

Prompt patching, or rather the lack of it, has prompted a fresh round of warnings to patch the BlueKeep vulnerability (CVE-2019-0708) that was exploited in a mass attack that started on October 23.

The attack was first detected on November 2, with the delay due to the failure of the attacker to take full advantage of the vulnerability. The campaign appears to have been conducted by a low-level threat actor who exploited the vulnerability to deliver cryptocurrency mining malware. Microsoft has issued yet another warning that worse is yet to come.

The first mass exploitation attempt certainly made the headlines, but it does not appear to have had much of an impact on the speed of patching. A scan conducted by the SANS Institute shows there has been little change in the rate of patching following the attacks. The number of unpatched devices has been steadily declining since Microsoft issued the patch in May, but hundreds of thousands of devices are still vulnerable to attack.

The attack was on a large scale, albeit with limited success. The exploit that was used failed to work properly and, in many cases, it just caused machines to crash. Successful exploitation of the vulnerability can allow a skilled threat actor to connect to vulnerable computers via RDP services with no user interaction required. Commands can be executed on vulnerable computers, which can allow the attacker to access, modify, and steal data, install malware, and launch attacks other unpatched devices on the network, even those that are not exposed to the internet.

Marcus Hutchins, the security researcher who discovered and activated a ‘kill switch’ to limit the harm caused by WannaCry ransomware in 2017, has warned that since most of the vulnerable devices are servers, even if the attacker does not develop a worm, an attack could still cause major disruption if, for instance, ransomware was deployed.

Microsoft has warned that the BlueKeep attacks are ongoing and it will only be a matter of time before a much more dangerous exploit is developed and used in a mass attack on vulnerable devices. Microsoft is urging customers to identify and update all vulnerable systems immediately.

The post Microsoft Issues Fresh Warning to Patch BlueKeep Vulnerability appeared first on HIPAA Journal.

Vulnerabilities Identified in Medtronic Valleylab Energy Platform and Electrosurgery Products

6 vulnerabilities have been identified in the Medtronic Valleylab energy platform and electrosurgery products, including one critical flaw that could allow an attacker to gain access to the Valleylab Energy platform and view/ overwrite files and remotely execute arbitrary code.

The vulnerabilities were identified by Medtronic which reported the flaws to the Department of Homeland Security Cybersecurity and Infrastructure Security Agency under its responsible vulnerability disclosure policy.

Four vulnerabilities have been identified in the following Medtronic Valleylab products

  • Valleylab Exchange Client, Version 3.4 and below
  • Valleylab FT10 Energy Platform (VLFT10GEN) software Version 4.0.0 and below
  • Valleylab FX8 Energy Platform (VLFX8GEN) software Version 1.1.0 and below

The critical vulnerability is an improper input validation flaw in the rssh utility, which facilitates file uploads. Exploitation of the vulnerability would allow an attacker to gain administrative access to files, allowing those files to be viewed, altered, or deleted. The flaw could also allow remote execution of arbitrary code.

The flaw has been assigned two CVE codes – CVE-2019-3464 and CVE-2019-3463. A CVSS v3 base score of 9.8 has been calculated for the flaws.

The products also use multiple sets of hard-coded credentials. If those credentials were discovered by an attacker, they could be used to read files on a vulnerable device. This flaw has been assigned the CVSS code – CVE-2019-13543 – and has a CVSS v3 base score of 5.4.

Vulnerable products use a descrypt algorithm for operating system password hashing. If interactive, network-based logons are disabled, combined with the other vulnerabilities, an attacker could obtain local shell access and view these hashes. The flaw – CVE-2019-13539 – has a CVSS v3 base score of 7.0.

Medtronic has released a patch for the FT10 platform, which should be applied as soon as possible. The FX8 platform will be patched in early 2020. Medtronic notes that the above products are supplied with network connections disabled by default and the Ethernet port is disabled on reboot; however, the company is aware that users often enable network connectivity.

Until the patches are applied to correct the flaws, Medtronic advises users to disconnect vulnerable products from IP networks or ensure those networks are segregated and are not accessible over the internet or via other untrusted networks.

Two further vulnerabilities have been identified in the following Medtronic Valleylab energy and electrosurgery products:

  • Valleylab FT10 Energy Platform (VLFT10GEN)
    • Version 2.1.0 and lower and Version 2.0.3 and lower
  • Valleylab LS10 Energy Platform (VLLS10GEN—not available in the United States)
    • Version 1.20.2 and lower

The FT10/LS10 Energy Platform incorporates an RFID security mechanism for authentication between the platform and instruments to prevent inauthentic instruments from being used. This security mechanism can be bypassed. The flaw has been assigned the CVE code, CVS-2019-13531, and has a CVSS v3 base score of 4.8.

The RFID security mechanism does not apply read protection, which could allow full read access to RFID security mechanism data. This flaw – CVE-2019-3535 – has a CVSS v3 base score of 4.6.

A patch has been issued to correct both of these flaws.

The post Vulnerabilities Identified in Medtronic Valleylab Energy Platform and Electrosurgery Products appeared first on HIPAA Journal.

Healthcare Data Breaches Predicted to Cost Industry $4 Billion in 2019

A recent survey has highlighted the cost of healthcare industry data breaches, the extent to which the healthcare industry is under attack, and how often those attacks succeed.

The survey was conducted by Black Book Market Research on 2,876 security professionals at 733 provider organizations between Q4, 2018 and Q3, 2019. Respondents were asked their views on cybersecurity to identify vulnerabilities and security gaps and determine why so many of these cyberattacks are succeeding.

96% of surveyed IT professionals believed that cybercriminals are outpacing medical enterprises, which is no surprise given that 93% of healthcare organizations reported having experienced a data breach since Q3, 2016. According to the report, 57% of organizations had experienced more than five data breaches during that time period. More than half of the data breaches reported by healthcare organizations were the result of hacks and other attacks by external threat actors.

The healthcare industry is being attacked because providers and insurers hold huge quantities of sensitive and valuable information and there are often security gaps that can be easily exploited. Even though the threat of attack is so high, the industry remains highly susceptible to data breaches.

The cost of these attacks to the healthcare industry is considerable. According to the report, the cost of data breaches at hospital organizations in 2019 was $423 per record. The report predicts that, based on the current level of data breaches, they will end up costing the healthcare industry $4 billion by the end of the year. Given the current trends and the annual increases in healthcare data breaches, that figure is likely to be considerably higher in 2020.

The survey confirmed that one of the main reasons why the healthcare industry is susceptible is due to budget constraints. Legacy systems and devices are still widely used in the healthcare industry, but the cost of replacing those systems is difficult to justify when that money does not increase revenue.

Overall, investment in cybersecurity for 2020 is planned to be increased to around 6% of total IT budgets at hospital systems, but smaller practices have seen a decrease in investment in cybersecurity, especially at physician organizations where only 1% of the 2020 IT budget will be spent on cybersecurity. 90% of hospital representatives surveyed said their cybersecurity budget had not changed since 2016.

When cybersecurity solutions are purchased, in many cases purchases are made blindly. A third of surveyed hospital executives said they chose cybersecurity solutions without much vision or discernment. 92% of data security product or service decisions since 2016 were made by C-level executives without including department managers and users in the purchasing decision. Only 4% of organizations said they had a steering committee to help evaluate the impact of investment in cybersecurity.

Many healthcare organizations are also operating without a dedicated security executive. Only 21% said they had a dedicated security executive and only 6% said that individual was the Chief Information Security Officer. At physician groups with more than 10 clinicians, only 1.5% said they had a dedicated CISO. Part of the reason is a shortage of qualified staff. 21% of healthcare organizations said they have had to outsource the role and are using cybersecurity-as-a-service as a stop gap measure.

The post Healthcare Data Breaches Predicted to Cost Industry $4 Billion in 2019 appeared first on HIPAA Journal.