Healthcare Data Privacy

NAAG Urges Apple and Google to Take Further Steps to Protect Privacy of Users of COVID-19 Contact Tracing Apps

On June 16, 2020, The National Association of Attorneys General (NAAG) wrote to Google and Apple to express concern about consumer privacy related to COVID-19 contact tracing and exposure notification apps. NAAG has made recommendations to help protect the personally identifiable information and sensitive health data of the millions of consumers who will be urged to download the apps to help control COVID-19.

“Digital contact tracing may provide a valuable tool to understand the spread of COVID-19 and assist the public health response to the pandemic,” explained the state AGs in the letter. “However, such technology also poses a risk to consumers’ personally identifiable information, including sensitive health information, that could continue long after the present public health emergency ends.”

Privacy protections are essential for ensuring that users of the apps do not have sensitive data exposed or used for purposes other than helping to control the spread of COVID-19. Without privacy protections, consumers will simply not download the apps, which will decrease their effectiveness. A study conducted by the University of Oxford suggests that in order for the aims of the apps to be achieved, there needs to be uptake of around 60% of a population. If consumers feel their privacy is at risk, that figure will not be achieved.

Current perceptions about the privacy protections of COVID-19 contact tracing apps were explored in a recent survey conducted on behalf of the antivirus firm Avira on 2,005 individuals in the United States. 71% of respondents said they do not plan to use the apps when they are made available. 44% were concerned about digital privacy, 39% said the apps provided a false sense of security, 37% said they did not think the apps would work, and 35% do not trust app providers.

The survey revealed most consumers do not trust Apple and Google to protect the data collected by the apps. Only 32% of respondents said they trusted the companies to protect their sensitive data, even though both companies have taken steps to implement privacy and security controls. There is even less trust in the government. Only 14% of respondents said they would trust contact tracing apps provided directly from the government. 75% of Americans said they believe their digital privacy would be placed at risk if COVID-19 contact tracing data was stored in a way that government and authorities could access the data.

In the letter, which was signed by 39 state attorneys general, concern was raised about the proliferation of contact tracing apps in the Google Play and Apple App Store. These apps are typically free to download and use and offer in-app adverts to generate revenue. Rather than using Google and Apple’s API and Bluetooth for identifying potential exposure, the apps rely on GPS tracking.

The state AGs also expressed concern that as more public health authorities start releasing contact tracing apps that use the Google and Apple API, it is likely many more developers will start releasing apps, and those apps may not incorporate the necessary privacy and security controls to comply with states’ laws.

Google and Apple were praised for the steps they have taken so far to ensure consumer privacy is protected but have been urged to go further. NAAG has requested any contact tracing app that is labeled or marketed as related to COVID-19 must be affiliated with either a municipal, county, state, or federal public health authority, or a hospital or university in the U.S. that is working with such public health authorities.

NAAG also called for Google and Apple to guarantee that all COVID-19 contact tracing apps will be removed from Google Play and the Apple App Store if they are not affiliated with the above entities, and for Google and Apple to pledge that all COVID-19 apps will be removed from Google Play and the App Store when the COVID-19 national public health emergency ends.

The post NAAG Urges Apple and Google to Take Further Steps to Protect Privacy of Users of COVID-19 Contact Tracing Apps appeared first on HIPAA Journal.
Software Glitch in Telehealth App Allowed Patients to View Videos of Other Patients’ Appointments

A UK-based chatbot and telehealth startup has suffered an embarrassing privacy breach this week. Babylon Health has developed a telehealth app that can be used by general practitioners for virtual appointments with patients. The app allows users to book appointments with their GP, use an AI-based chatbot for triage, and have voice and video calls with their doctor through the app.

On June 9, 2020, a patient used the app to check his prescription and found 50 videos of other patients’ appointments in the consultation replays section of the app. The files contained video replays of consultations between doctors and patients, exposing confidential and, potentially, extremely sensitive information.

The patient took to Twitter to announce the discovery, stating the “Why have I got access to other patients video consultations through your app? This is a massive data breach. Over 50 video recordings are on this list!”

According to a statement released by Babylon Health, the issue was due to a glitch in the software rather than a malicious attack. Babylon Health said it discovered the error shortly before the patient disclosed the breach on Twitter and said the issue was resolved within a couple of hours.

The investigation revealed three patients were able to access video footage of other patients, but in both of the other cases, the patients had not viewed any of the video replays. The error was only introduced in the UK version of the app and did not affect its international operations. The error was introduced when the app was updated to allow a patient to switch between audio and video while on a call with a physician.

Babylon Health has reported the breach to the UK Information Commissioner’s Office as required by the EU’s General Data Protection Regulation and will disclose full details about the data breach.

In this case the software error does not appeared to have exposed many patients’ consultations, but it is a cause for concern given the highly sensitive nature of health information disclosed through the app. There are currently around 2.3 million users of the app in the UK, so the breach could potentially have been far worse.

There has been a major expansion of telehealth services in the United States as a result of the COVID-19 pandemic. The HHS’ Centers for Medicare and Medicaid Services (CMS) expanded coverage for reimbursable telehealth services during the COVID-19 pandemic and the HHS’ Office for Civil Rights (OCR) issued a notice of enforcement discretion covering telehealth services, allowing healthcare providers to use communications solutions which may not be fully HIPAA compliant.

Given the increase in telehealth services, and the wide range of apps being used to provide telehealth services, this could well be just the first of several privacy breaches involving telehealth services this year.

While financial penalties may not be issued over privacy and security issues related to the good faith provision of telehealth services during the COVID_19 public health emergency, care should still be taken choosing a telehealth solution. Many video conferencing apps have not been developed with sufficient security protections to ensure patient information is properly protected, which places patient privacy at risk. As this incident shows, even purpose-built health apps are not immune to data leaks.

To ensure the privacy of patients is protected, all new technology should be subjected to a thorough security review. Now that the COVID-19 pandemic is under better control, now would be an ideal time to conduct a review of any telehealth applications and other software that has been introduced to ensure appropriate protections are in place to protect patient privacy.

It is also worth considering making the change from consumer-grade apps that have been rapidly deployed during the COVID-19 pandemic to support telehealth to a purpose built healthcare telehealth solution that is HIPAA compliant and incorporates comprehensive privacy and security controls.

The post Software Glitch in Telehealth App Allowed Patients to View Videos of Other Patients’ Appointments appeared first on HIPAA Journal.

Alert Issued by Feds to Raise Awareness of Scams Related to COVID-19 Economic Payments

A joint alert issued has been issued by the IRS, DHS’ Cybersecurity and Infrastructure Security Agency (CISA), and the Department of the Treasury to raise awareness of the risk of phishing and other cyberattacks related to the Coronavirus Aid, Relief, and Economic Security (CARES) Act.

The CARES Act has made $2 trillion available to support businesses and individuals adversely affected by the COVID-19 pandemic, which will help to reduce the financial burden through economic impact payments to eligible Americans. CARES Act payments are being used as a lure in phishing attacks to obtain personal and financial information and attempts have been made to redirect CARES Act payments. All Americans have been urged to be on the lookout for criminal fraud related to the CARES Act and COVID-19.

The U.S. Government reports that many cybercriminal groups are using stimulus-themed lures in phishing emails and text messages to obtain sensitive information such as bank account information. Financial institutions have been asked to remind their customers to practice good cybersecurity hygiene and to monitor for illicit account use and creation.

Criminals are using CARES Act-themed emails and websites to obtain sensitive information, spread malware, and gain access to computer networks. “Themes for these scams might include economic stimulus, personal checks, loan and grant programs, or other subjects relevant to the CARES Act. These CARES Act related cybercriminal attempts could support a wide range of follow-on activities that would be harmful to the rollout of the CARES Act.”

Threat actors may seek to disrupt the operations of organizations responsible for implementing the CARES Act, including the use of ransomware to interrupt the flow of CARES Act funds and to extort money from victims. Federal, state, local and tribal agencies are being urged to review their payment, banking, and loan processing systems and ramp up security to prevent attacks.

Foreign threat actors have been discovered to be submitting fraudulent claims for COVID-19 relief funds, with one Nigerian business email compromise (BEC) gang known to have submitted more than 200 fraudulent claims for unemployment benefits and CARES Act payments. The gang, known as Scattered Canary, has been submitting multiple claims via state unemployment websites to obtain payments using data stolen in W-2 phishing attacks. The gang has submitted at least 174 fraudulent claims with the state of Washington and more than a dozen with the state of Massachusetts. At least 8 states have been targeted to date.

The U.S. Government has been distributing threat intelligence and cybersecurity best practices to help disrupt and deter criminal activity and the U.S. Secret Service is currently focussed on investigative operations to identify individuals exploiting the pandemic to ensure they are brought to justice and any proceeds of the crimes are recovered.

The IRS has reminded taxpayers that it does not initiate contact with taxpayers via email, text message, or social media channels to request personal and financial information such as bank account numbers, credit card information, and PINs. The IRS has warned Americans that copycat domains that may be set up to obtain sensitive information and to carefully check any domain for transposed letters and mismatched SSL certificates. The IRS is only using is www.irs.gov and the IRS-run site, https://www.freefilefillableforms.com/.

All Americans have been advised to be vigilant and monitor their financial accounts for signs of fraudulent activity and to report any cases of phishing attacks and other scams to the appropriate authorities. They should also alert their employer if they feel they may have fallen for a scam and revealed sensitive information about their organization.

The alert, Avoid Scams Related To Economic Payments, COVID-19, can be viewed on this link.

The post Alert Issued by Feds to Raise Awareness of Scams Related to COVID-19 Economic Payments appeared first on HIPAA Journal.

April 2020 Healthcare Data Breach Report

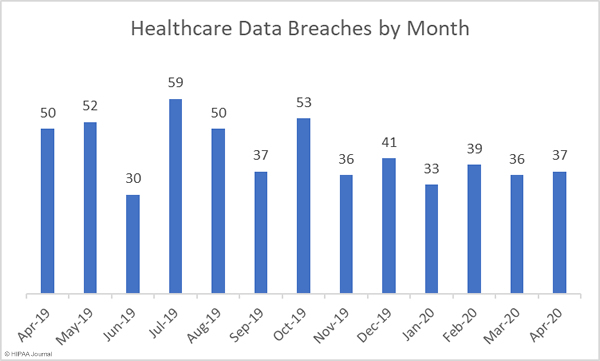
There were 37 healthcare data breaches of 500 or more records reported in April 2020, up one from the 36 breaches reported in March. As the graph below shows, the number of breaches reported each month has been fairly consistent and has remained well below the 12-month average of 41.9 data breaches per month.

Healthcare data breaches by month (2019-2020)

While the number of breaches increased slightly, there was a significant reduction in the number of breached healthcare records in April. 442,943 healthcare records were breached in April, down 46.56% from the 828,921 records breached in March. This is the second successive month where the number of exposed records has fallen. While this is certainly good news, it should be noted that in the past 12 months, 39.92 million healthcare records have been breached.

Healthcare records breached in the past 6 months

Largest Healthcare Data Breaches in April 2020


Name of Covered Entity Covered Entity Type Individuals Affected Type of Breach Location of Breached Information
Beaumont Health Healthcare Provider 112,211 Hacking/IT Incident Email
Meridian Health Services Corp. Healthcare Provider 111,372 Hacking/IT Incident Email
Arizona Endocrinology Center Healthcare Provider 74,122 Unauthorized Access/Disclosure Electronic Medical Record
Advocate Aurora Health Healthcare Provider 27,137 Hacking/IT Incident Email, Network Server
Doctors Community Medical Center Healthcare Provider 18,481 Hacking/IT Incident Email
Andrews Braces Healthcare Provider 16,622 Hacking/IT Incident Network Server
UPMC Altoona Regional Health Services Healthcare Provider 13,911 Hacking/IT Incident Email
Colorado Department of Human Services, Office of Behavioral Health Healthcare Provider 8,132 Unauthorized Access/Disclosure Network Server
Agility Center Orthopedics Healthcare Provider 7,000 Hacking/IT Incident Email
Beacon Health Options, Inc. Business Associate 6,723 Loss Other Portable Electronic Device


Causes of Healthcare Data Breaches in April

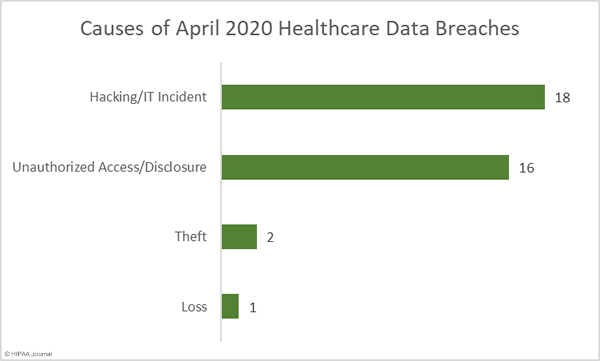
As was the case in March, hacking and IT incidents were the leading causes of healthcare data breaches. Unauthorized access/disclosure incidents were the next most common causes of breaches, an increase of 77.77% from the previous month.

333,838 records were compromised in the 18 reported hacking/IT incidents, which account for 75.37% of all records breached in April. The average breach size was 18,547 records and the median breach size was 4,631 records. There were 16 reported unauthorized access/disclosure incidents in April. The average breach size was 6,171 records and the median breach size was 1,122 records. In total, 98,737 records were breached across those 16 incidents.

There were two theft incidents reported in April, both involving portable electronic devices. The records of 3,645 individuals were stored on those devices. There was also one lost portable electronic device containing the records of 6,723 patients.

causes of healthcare data breaches in April 2020

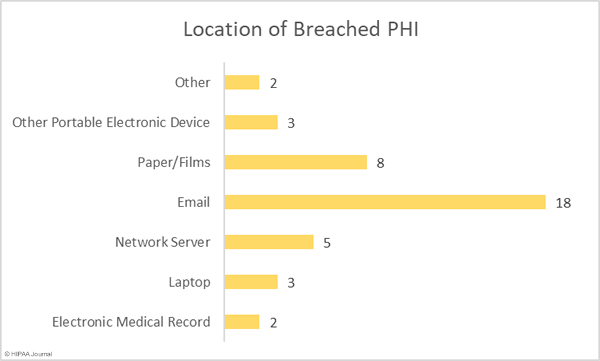
The bar chart below shows the location of breached protected health information. The chart shows email is by far the most common location of breached health information. 48.65% of all reported breaches in April involved PHI stored in emails and email attachments. The majority of those breaches were phishing attacks. Most healthcare data breaches involve electronic data, but one in five breaches involved PHI in paper files and charts.

Location of breached PHI in April 2020

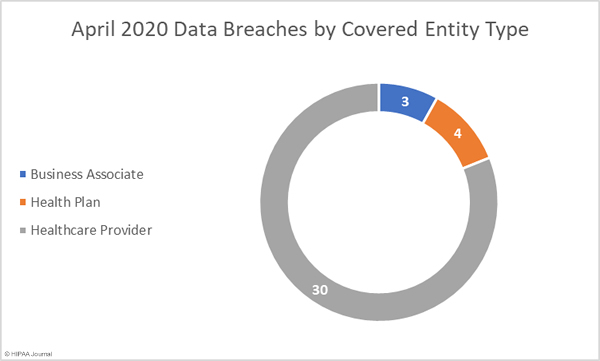
Healthcare Data Breaches by Covered Entity Type

Healthcare providers were the worst affected covered entity type in April with 30 breaches reported. 4 health plans reported a breach in April, and three breaches were reported by business associates of HIPAA-covered entities. A further 8 breaches had some business associate involvement.

Healthcare Data Breaches by State

April’s data breaches were reported by covered entities and business associates in 22 states. Florida and Texas were the worst affected with 4 breaches each. There were three data breaches reported in Michigan and Pennsylvania, and two breaches affecting covered entities and business associates based in California, Connecticut, Minnesota, Missouri, and Wisconsin. One breach was reported by entities based in Arkansas, Arizona, Colorado, Delaware, Indiana, Massachusetts, Maryland, North Carolina, New Mexico, Nevada, Tennessee, Utah, and Washington.

HIPAA Enforcement Activity in April

There were no financial penalties imposed on covered entities or business associates by state Attorneys General or the HHS’ Office for Civil Rights in April.

The post April 2020 Healthcare Data Breach Report appeared first on HIPAA Journal.

Republicans and Democrats Introduce Competing Bills Covering COVID-19 Contact Tracing Apps

Two privacy bills have been introduced relating to COVID-19 contact tracing apps that are now being considered by Congress. The competing bills, introduced by Republican and Democratic lawmakers, share some common ground and look to achieve similar aims.

The first bill, the COVID-19 Consumer Data Protection Act, was introduced by Republican senators Roger Wicker (R-Miss), John Thune (R-S.D), Jerry Moran, (R-Kan), and Marsha Blackburn (R-Tenn) last month “to protect the privacy of consumers’ personal health information, proximity data, device data, and geolocation data during the coronavirus public health crisis.”

The bill would make it illegal for personal health information, proximity data, device data, and geolocation data to be collected unless notice was given to consumers about the purpose of collecting data and consumers are required to give their consent to the collection, processing, and transfer of their data. The bill prohibits the collection, use, or transfer of data for any secondary purposes.

The allowed purposed for the collection, processing, and transfer of data is limited to tracking the spread, signs, and symptoms of COVID-19; the collection, processing and transfer of an individual’s data to measure compliance with social distancing guidelines and other requirements related to COVID-19 imposed on individuals; and the collection, processing, or transfer of data for COVID-19 contact tracing purposes.

The bill also requires companies to allow individuals to opt out, provide transparency reports describing data collection activities, establish data minimization and data security requirements, define what constitutes aggregate and de-identified data to ensure companies adopt certain technical and legal safeguards to prevent re-identification; and to require companies to delete collected data when the COVID-19 public health emergency is over.

According to Senator Thune, “This bill strikes the right balance between innovation – allowing technology companies to continue their work toward developing platforms that could trace the virus and help flatten the curve and stop the spread – and maintaining privacy protections for U.S. citizens.”

The Democratic bill, the Public Health Emergency Privacy Act, was introduced by Representatives Anna G. Eshoo (D-Calif), Jan Schakowsky (D-Ill), Suzan DelBene(D-Wash), and Senators Richard Blumenthal (D-Conn) and Mark Warner (D-Va). The aim of the bill is to ensure there is transparency over the health and location data collected by contact-tracing apps and to give Americans control over the collection and use of their data. The bill also ensures that businesses can be held to account by consumers if their data is used for any activities other than the fight against COVID-19.

The bill requires health data to only be used for public health purposes; prohibits the use of health data for discriminatory, unrelated, or intrusive purposes, including commercial advertising or to gate access to employment, finance, insurance, housing, or education opportunities; prevents misuse of data by government agencies that have no role in public health; ensures meaningful data security and data integrity protections are implemented; prohibits conditioning the right to vote based on a medical condition or use of contact tracing apps; and requires reports to be regularly produced on the impact of digital collection tools on civil rights.

The bill requires the public to be given control over participation in contact tracing through opt-in consent, there must be meaningful transparency, and robust private and public enforcement. The bill also calls for the destruction of data within 60 days of the end of the public health emergency. The bill would not apply to HIPAA-covered entities or their business associates, which would continue to be required to comply with HIPAA Rules.

“As we continue to respond to the devastating suffering caused by COVID-19, our country’s first and foremost public health response must be testing, testing, testing, AND manual contact tracing. Digital contact tracing can and should complement these efforts, but it is just that – complimentary. However, if we do pursue digital contact tracing, consumers need clearly-defined privacy rights and strong enforcement to safeguard these rights,” said Rep. Jan Schakowsky.

Given the similarity of both bills and their common goals, it may be possible for some consensus to be reached on the content of any new legislation and for both sides to work together to get a bill passed to protect the privacy of Americans and ensure that data collected by COVID-19 contact tracing apps is not misused.

The post Republicans and Democrats Introduce Competing Bills Covering COVID-19 Contact Tracing Apps appeared first on HIPAA Journal.
AMA Publishes Set of Privacy Principles for Non-HIPAA-Covered Entities

The American Medical Association (AMA) has published a set of privacy principles for non-HIPAA-covered entities to help ensure that the privacy of consumers is protected, even when healthcare data is provided to data holders that do not need to comply with HIPAA Rules.

HIPAA only applies to healthcare providers, health plans, healthcare clearinghouses (covered entities) and business associates of those entities. HIPAA requires those entities to protect the privacy of patients and implement security controls to keep their healthcare data private and confidential. When the same healthcare data is shared with an entity that is not covered by HIPAA, those protections do not need to be in place. HIPAA also gives patients rights over their health data, but those rights do not apply to health data sent to a non-HIPAA-covered entity.

The Centers for Medicare and Medicaid Services (CMS) and the Office of the National Coordinator for Health IT (ONS) have recently published rules to prevent information blocking and improve sharing of healthcare data. One requirement is to allow patients to have their health data sent to a third-party app of their choice. In most cases, the developers of those apps are not HIPAA-covered entities.

Discussions are taking place in Congress about new federal regulations covering healthcare data provided to non-HIPAA-covered entities and several legislative acts have been proposed, although none have so far attracted sufficient support.

The new privacy principles developed by the AMA are intended to give consumers greater control over their healthcare data when it is held by a non-HIPAA-covered entity and to inform discussions about new legislation to better protect privacy when health data is shared with third-parties outside of the healthcare system.

In a recent blog post announcing the new privacy principles, the AMA explained that patients’ confidence in the privacy and security of their data has been shaken. The business models of many tech companies involve gathering extensive information about consumers personal lives, in many cases with a lack of transparency and consent. There have been many scandals over personal data which have made consumers nervous about sharing data not only with tech companies but also with their healthcare providers.

Consumers are now less willing to provide health information to physicians, as they are worried that the information may not remain private and confidential and may even be shared with tech companies. The AMA is particularly concerned that the recent CMS and ONC rule changes will make it even more likely that patients will feel that they should withhold certain healthcare data from their healthcare providers.

The privacy principles will help to ensure that guardrails are placed around healthcare data and patients are given meaningful control over their healthcare data and will be told, in clear and easy to understand language, exactly how their health data will be used and with whom that information will be shared. The privacy principles also cover data that has not historically been considered to be personally identifiable such as IP addresses and mobile phone advertising identifiers but could in fact be used to identify an individual.

The privacy principles detail rights that individuals should have over their healthcare data and protections that need to be implemented to protect against healthcare data being used to discriminate against individuals. The AMA is also attempting to shift the responsibility for privacy from individuals to data holders, who must be responsible stewards of any data provided to them. In cases where privacy is violated, the AMA is calling for tough penalties to be imposed and for there to be robust enforcement of any new national privacy legislation. Robust enforcement will help to maintain trust in digital health tools, including smartphone apps that can be used to access healthcare data.

The privacy principles establish 12 rights that individuals should have over their health data, equity factors that must be taken into account in any privacy laws, and the responsibilities of data holders to protect the privacy of consumers. Also included are a set of requirements for enforcement of new privacy regulations covering health data.

“The AMA privacy principles set a framework for national protections that provide patients with meaningful control and transparency over the access and use of their data,” said AMA President Patrice A. Harris, M.D., M.A. “Preserving patient trust is critical if digital health technologies are to facilitate an era of more accessible, coordinated, and personalized care.

You can view the AMA’s privacy principles on this link.

The post AMA Publishes Set of Privacy Principles for Non-HIPAA-Covered Entities appeared first on HIPAA Journal.

Zoom Reaches Settlement with NY Attorney General Over Privacy and Security Issues

Zoom reached an agreement with the New York Attorney General’s office and has committed to implementing better privacy and security controls for its teleconferencing platform. New York Attorney General Letitia James launched an investigation into Zoom after researchers uncovered a number of privacy and security issues with the platform earlier this year.

Zoom has proven to be one of the most popular teleconferencing platforms during the COVID-19 pandemic. In March, more than 200 million individuals were participating in Zoom meetings with usership growing by 2,000% in the space of just three months. As the number of users grew and the platform started to be used more frequently by consumers and students, flaws in the platform started to emerge.

Meeting participants started reporting cases of uninvited people joining and disrupting private meetings. Several of these “Zoombombing” attacks saw participants racially abused and harassed on the basis of religion and gender. There were also several reported cases of uninvited individuals joining meetings and displaying pornographic images.

Then security researchers started uncovering privacy and security issues with the platform. Zoom stated on its website that Zoom meetings were protected with end-to-end encryption, but it was discovered that Zoom had used AES 128 bit encryption rather than AES 256 bit encryption and its end-to-end encryption claim was false. Zoom was also discovered to have issued encryption keys through data centers in China, even though meetings were taking place between users in the United States.

Zoom used Facebook’s SDK for iOS to allow users of the iOS mobile app to login through Facebook, which meant that Facebook was provided with technical data related to users’ devices each time they opened the Zoom app. While Zoom did state in its privacy policy that third-party tools may collect information about users, data was discovered to have been passed to Facebook even when users had not used the Facebook login with the app.  There were also privacy issues associated with the LinkedIn Sales Navigator feature, which allowed meeting participants to view the LinkedIn profiles of other meeting participants, even when they had taken steps to remain anonymous by adopting pseudonyms. The Company Directory feature of the platform was found to violate the privacy of some users by leaking personal information to other users if they had the same email domain.

Zoom responded quickly to the privacy and security issues and corrected most within a few days of discovery. The firm also announced that it was halting all development work to concentrate on privacy and security. The company also enacted a CISO Council and Advisory Board to focus on privacy and security and Zoom recently announced that it has acquired the start-up firm Keybase, which will help to implement end-to-end encryption for Zoom meetings.

Under the terms off the settlement with the New York Attorney General’s office, Zoom has agreed to implement a comprehensive data security program to ensure its users are protected. The program will be overseen by Zoom’s head of security. The company has also agreed to conduct a comprehensive security risk assessment and code review and will fix all identified security issues with the platform. Privacy controls will also be implemented to protect free accounts, such as those used by schools.

Under the terms of the settlement, Zoom must continue to review privacy and security and implement further protections to give its users greater control over their privacy. Steps must also be taken to regulate abusive activity on the platform.

“This agreement puts protections in place so that Zoom users have control over their privacy and security, and so that workplaces, schools, religious institutions, and consumers don’t have to worry while participating in a video call,” said Attorney General James.

The post Zoom Reaches Settlement with NY Attorney General Over Privacy and Security Issues appeared first on HIPAA Journal.

FTC Seeks Comment on Health Breach Notification Rule

The U.S. Federal Trade Commission (FTC) is seeking comment on its breach notification requirements for non-HIPAA-covered entities that collect personally identifiable health information.

The FTC’s Health Breach Notification Rule was introduced in 2009 as part of the American Recovery and Reinvestment Act of 2009 (ARRA). The rule took effect on August 22, 2010 and the FTC started actively enforcing compliance on February 22, 2010.

Healthcare data collected, maintained, or transmitted by healthcare providers, health plans, healthcare clearinghouses (HIPAA-covered entities) and their business associates is covered by the Health Insurance Portability and Accountability Act (HIPAA) and is classed as protected health information (PHI).

The FTC’s Health Breach Notification Rule applies to personal health records (PHRs), which are electronic records containing personally identifiable health information that are managed, shared, and controlled by or primarily for the individual. The FTC rule applies to vendors of personal health records and PHR-related entities, which are companies that offer products and services through PHR websites, send information to PHRs, or access some of the information in PHRs.

All entities covered by the FTC’s Health Breach Notification Rule are required to issue notifications to affected consumers and the FTC without unreasonable delay and no later than 60 days from the date of discovery of a breach. The FTC must be notified within 10 days of discovery of a breach if it impacts 500 or more individuals. If a breach is experienced by a service provider, the service provider is required to notify the PHR company. The FTC publishes notices of data breaches affecting 500 or more individuals on its website.

The FTC routinely reviews rules every 10 years. In the 10 years since the rule was passed, only 2 breaches have been published on the FTC website, as most breaches reported to the FTC have involved fewer than 500 records. The FTC also reports that it has not needed to enforce compliance, as the entities to which the rule applies are somewhat limited.

Most PHR vendors and related entities are either HIPAA-covered entities or business associates of those entities and are therefore required to comply with the HIPAA Breach Notification Rule; however, the FTC explains that its rule may soon apply to a greater number of entities.

“As consumers turn towards direct-to-consumer technologies for health information and services (such as mobile health applications, virtual assistants, and platforms’ health tools), more companies may be covered by the FTC’s Rule.”

The COVID-19 pandemic has increased use of these communication platforms following the move by the HHS to temporarily refrain from imposing financial penalties for use of non-HIPAA-compliant platforms in relation to the provision of telehealth services. The FTC rule may therefore be more relevant today than it was 10 years ago when the rule was introduced.

The FTC is seeking answers to specific questions about its rule in relation to its effectiveness, benefits, and relevance to determine whether the rule should remain as it is, should be scrapped, or updated to increase the benefits to consumers.

Comment is being accepted for 90 days from the date of publication in the Federal Register. You can view a copy of the request for public comment on Bloomberg Law.

The post FTC Seeks Comment on Health Breach Notification Rule appeared first on HIPAA Journal.

EFF Warns of Privacy and Security Risks with Google and Apple’s COVID-19 Contact Tracing Technology

The contact tracing technology being developed by Apple and Google to help track people who have come into close contact with individuals confirmed as having contracted COVID-19 could be invaluable in the fight against SARS-CoV-19; however, the Electronic Frontier Foundation (EFF) has warned that in its current form, the system could be abused by cybercriminals.

Google and Apple are working together on the technology, which is expected to be fully rolled out next month. The system will allow app developers to build contact tracing apps to help identify individuals who may have been exposed to SARS-CoV-2. When a user downloads a contact tracing app, each time they come into contact with another person with the app installed on their phone, anonymous identifier beacons called rolling proximity identifiers (RPIDs) will be exchanged via Bluetooth Low Energy.

How Does the Contact-Tracing System Work?

RPIDs will be exchanged only if an individual moves within a predefined range – 6 feet – and stays in close contact for a set period of time. Range can be determined by strength of the pings sent out by users’ smartphones. Should a person be diagnosed with COVID-19 and enters the information into the app, all individuals that the person has come into contact with over the previous 14 days will be sent an electronic notification.

The data sent is anonymously, so notifications will not provide any information about the person that has contracted COVID-19. The RPIDs will change every 10-20 minutes, which will prevent a person from being tracked and data will be stored on smartphones rather than being sent to a central server and RPIDs will only be retained for 14 days. Permission is also required from a user before a public health authority can share the user’s temporary exposure key that confirms the individual has contracted COVID-19, which will prevent false alarms.

When a COVID-19 diagnosis is confirmed, a diagnosis key will be logged in a public registry which will be accessible by all app users and will be used for generating alerts. The diagnosis keys contain all of the RPIDs for a particular user to allow all individuals who have been in contact with them to be notified.

Electronic Frontier Foundation Concerned About Privacy and Security Risks

The public registry is one of the problems with the system, as EFF’s Bennett Cypher and Gennie Gebhart explained in a recent blog post, “any proximity tracking system that checks a public database of diagnosis keys against RPIDs on a user’s device—as the Apple-Google proposal does—leaves open the possibility that the contacts of an infected person will figure out which of the people they encountered is infected.”

Each day, users of the apps will share their diagnosis keys, which opens up the possibility of linkage attacks. It would be possible for a threat actor to collect RPIDs from many different places simultaneously through the use of static Bluetooth beacons in public places. This would only provide information about where pings occurred and would not allow an individual to be tracked. However, when the diagnosis keys are broadcast, an attacker could link the RPIDs together and determine a person’s daily routine from their RPIDs. Since a person’s movements would be unique, it would potentially be possible to identify that individual and discover their movements and where they live and work. EFF suggests that risk could be reduced by sending diagnosis keys more frequently, such as every hour rather than once a day.

Another problem with the system in its current form is there is currently no way of verifying that a device sending contact-tracing data is the device that generated the RPID. This means a malicious actor could intercept RPIDs and rebroadcast them.

“Imagine a network of Bluetooth beacons set up on busy street corners that rebroadcast all the RPIDs they observe,” explained. “Anyone who passes by a ‘bad’ beacon would log the RPIDs of everyone else who was near any one of the beacons. This would lead to a lot of false positives, which might undermine public trust in proximity-tracing apps—or worse, in the public-health system as a whole.”

Concern has also been raised about the potential for developers to centralize the data collected by the apps, which EFF warns could expose people to more risk. EFF recommends developers stick to the proposal outlined by Apple and Google and keep users’ data on their phones rather than in a central repository. EFF also says it is important to limit the data sent out over the internet as far as possible and to only send data that is absolutely necessary.

Echoing the advice of more than 300 scientists who recently signed an open letter about the privacy and security risks of contact-tracing technology, EFF said it is also essential for the program to sunset once the COVID-19 public health emergency is over to ensure there will be no secondary uses that could impact personal privacy in the future. They also recommend that app developers must operate with complete transparency and clearly explain to users what data is collected, and should allow users to stop pings should they wish and also access the RPIDs they have received and delete data from their contact history.

Further, any app must be extensively tested to ensure it functions as it should and does not have any vulnerabilities that can be exploited. Post-release, testing will need to continue to find vulnerabilities and patches and updates will need to be developed and rolled out rapidly to correct flaws that are discovered. In order for the system to work as it should, a high percentage of the population will need to be using the system, which would likely make it an attractive target for cybercriminals and nation state hacking groups. The latter are already conducting campaigns spreading disinformation about COVID-19 and are conducting cyberattacks to disrupt the COVID-19 response.

No contact tracing system is likely to be free of privacy risks, as there must be a trade-off to perform this type of contact tracing, but EFF says that steps must be taken to reduce those privacy risks as far as possible. The whole system is based on trust and, if trust is undermined, the system will not be able to achieve its aims.

The post EFF Warns of Privacy and Security Risks with Google and Apple’s COVID-19 Contact Tracing Technology appeared first on HIPAA Journal.