Healthcare Data Privacy

Idaho Hospitals Must Now Comply with New Idaho Patient Rights Rules

New rules for hospitals have been implemented in Idaho that give patients new rights. The rules were implemented by the Idaho Department of Health and Welfare (IDHW) and are effective from July 1, 2019.

The new rules were suggested by patient advocacy groups and “incorporate standards that parallel—but do not exactly mirror—existing law and/or Medicare conditions of participation for hospitals,” according to IDHW. The policies align with the MyHealthEData initiative, which was launched in 2018 with the aim of removing the barriers to secure access to electronic medical records.

Under previous state law, critical access hospitals (CAHs) were not required to comply with many of the regulatory conditions that applied to other healthcare providers. The new rules change that, which will mean new policies and procedures will need to be implemented by CAHs. That will come with a considerable administrative burden.

The new rules apply to all hospitals in Idaho as well as any provider that renders services in hospitals. All hospitals and providers have been advised to check their policies and procedures to make sure they are compliant with the new rules.

The main purpose of the new rules is to improve patient rights and make it easier – and quicker – for patients to obtain copies of their health information and access to their EHRs.

As required by HIPAA, patients must be provided with a copy of their medical records on request within 30 days of the request being received. Under the new rules in Idaho, access to EMRs must be provided within 3 days of the request being received. The copy must also be provided in a readily readable format on a popular portable media storage device.

HIPAA limits the amount that can be charged for providing patients with copies of their health information. The new Idaho rules further protect patients by only permitting hospitals to charge a reasonable fee for labor and restricting the charges for copies to the cost of copying at the local library.

A patient’s right to privacy has been further protected. Patients have the right to privacy when personal care is being provided, which extends to continuous observation and video and audio monitoring of patients. As of July 1, 2019, hospitals are not permitted to record video or audio, except in common areas, without first obtaining written consent from the patient. Those recordings must then be included in a patient’s medical record.

The new rules also cover notices of discontinuation of care, advance directives, obtaining and documenting informed consent, patient safety, patient grievances, restraint and seclusion, and law enforcement restraints.

The post Idaho Hospitals Must Now Comply with New Idaho Patient Rights Rules appeared first on HIPAA Journal.

HHS Declares Limited Waiver of HIPAA Sanctions and Penalties in Louisiana

The Secretary of the U.S. Department of Health and Human Services (HHS) has issued a limited waiver of HIPAA sanctions and penalties in Louisiana due to the devastation likely to be caused by Tropical Storm Barry as it made landfall on July 13 as a hurricane. The HHS announced the public health emergency in Louisiana on Friday July 12, 2019.

The waiver only applies to healthcare organizations in the emergency area and only for the length of time stated in the declaration. The waiver only applies to specific provisions of the HIPAA Privacy Rule and only for a maximum period of 72 hours after the hospital has implemented its emergency protocol.

Once the time period for the waiver ends, healthcare providers will be required once again to comply with all aspects of the HIPAA Privacy Rule, even for patients still under their at the time the declaration ends, even if the 72-hour time window has not expired.

While a waiver has been issued, the Privacy Rule does not prohibit the sharing of protected health information during disasters to assist patients and make sure they get the care they require. That includes sharing some health information with friends, family members and other individuals directly involved in a patient’s care.

The HIPAA Privacy Rule allows the sharing of PHI for public health activities and to prevent or reduce a serious and imminent threat to health or safety. HIPAA-covered entities are also permitted to share information with disaster relief organizations that have been authorized by law to assist with disaster relief efforts without first obtaining permission from patients.

During natural disasters the HIPAA Privacy and Security Rules remain in effect, although following the secretarial declaration, sanctions and penalties against HIPAA covered entities are waived for the following aspects of the HIPAA Privacy Rule:

  • The requirements to obtain a patient’s agreement to speak with family members or friends involved in the patient’s care. See 45 CFR 164.510(b).
  • The requirement to honor a request to opt out of the facility directory. See 45 CFR164.510(a).
  • The requirement to distribute a notice of privacy practices. See 45 CFR 164.520.
  • The patient’s right to request privacy restrictions. See 45 CFR 164.522(a).
  • The patient’s right to request confidential communications. See 45 CFR 164.522(b).

“We are working closely with state health and emergency management officials to anticipate the communities’ healthcare needs and be ready to meet them,” said Secretary Azar. The HHS emergency declaration and limited HIPAA waiver can be viewed on this link (PDF).

The post HHS Declares Limited Waiver of HIPAA Sanctions and Penalties in Louisiana appeared first on HIPAA Journal.

Webinar: Ransomware, Malware, Phishing, and HIPAA Compliance

Compliancy Group is offering healthcare professionals an opportunity to take part in a webinar covering the main threats facing the healthcare industry.

Threats such as ransomware, malware, and phishing will be discussed by compliance experts in relation to HIPAA and the privacy and security of patient data.

Cybersecurity has become more important than ever in healthcare. The industry is seen as a weak target by hackers, large volumes of data are stored, and patient information carries a high value on the black market.

April 2019 saw the highest number of healthcare data breaches in a single month and more healthcare data breaches were reported in 2018 than in any other year to date. The increased frequency of attacks on organizations of all sizes highlights just how important cybersecurity has become.

Cyberattacks are not only negatively affecting businesses in the healthcare sector, but also place the privacy of patient’s health information at risk. While it was once sufficient to implement standard security tools, the sophisticated nature of attacks today mean new solutions are required to protect against cyberattacks.

Protecting against cyberattacks while ensuring compliance with HIPAA can be a challenge and oversights could easily lead to a costly breach or regulatory fine.

In the latest Compliancy Group webinar, compliancy experts will walk you through the inns and outs of the regulations and you can find out more about cybersecurity with respect to the requirements of HIPAA and HITECH.

Webinar:

Ransomware, Malware, Phishing, Oh My!

Wednesday, July 10th

2:00 ET/11:00 PT

Advance Registration

The post Webinar: Ransomware, Malware, Phishing, and HIPAA Compliance appeared first on HIPAA Journal.

CMS Uses Weak ID Verification and Has No Plans to Change

According to a recent Government Accountability Office (GAO) audit, the Department of Health and Human Services’ Centers for Medicare and Medicaid Services (CMS) is using an outdated and weak method of remote ID verification which is no longer considered to provide sufficient protection against fraud.

The CMS website, which is used to find federal income-based financial subsidies and private health insurance, uses knowledge-based verification to confirm an individual’s identity. Individuals are asked to confirm their name, address and date of birth and are then asked questions to which only they would know the answer, such as information found in their credit file.

While knowledge-based ID verification based on entries in a credit file does provide a good level of security, that all changed with the massive data breach at Equifax. A great deal of personal information was stolen by hackers – information that could be used to answer security questions. Without a more secure system of ID verification, Americans will be at risk of fraud.

There are several alternative methods for ID verification that provide a greater level of security and protection against fraud, such as the use of a mobile phone to take a photo of an ID document which is compared to the document on file. Alternatively, instead of using credit files, entries in an individual’s mobile phone records could be used. Several federal agencies have attempted to strengthen their remote ID verification methods but have struggled with implementing new solutions.

GAO conducted audits at six agencies following the Equifax breach to assess the extent to which new methods of verification had been implemented. Two of the six agencies have now transitioned to new forms of ID verification (General Services Administration (GSA) and the Internal Revenue Service (IRS)).

The Department of Veterans Affairs (VA) has partially transitioned, but still uses knowledge-based verification for some individuals. The Social Security Administration (SSA) and the United States Postal Service (USPS) are committed to eliminating knowledge-based ID verification, but do not yet have a formal plan or timescale for doing so.

Only the CMS is using knowledge-based ID verification and has no plans to reduce or eliminate knowledge-based ID verification in the future. Healthcare.gov only has email address confirmation, even though that only confirms that the user who provided the information also owns the email account used to create the account.

Several reasons have been given as to why alternative methods of ID verification are not suitable, including cost, the lack of viable solutions, and implementation difficulties. One difficulty is not everyone possesses a mobile device, so mobile-based verification is not universal solution.

The reason given for not changing Healthcare.gov was it was not cost-effective; however, GAO pointed out that NIST guidance does not permit federal agencies to use knowledge-based verification simply because it is cost effective to do so.

CMS also argued that NIST guidance was insufficient. GAO agreed that more could be done and has called for NIST to issue further guidance that can be followed by federal agencies to implement more secure ID verification methods.

GAO has urged CMS to continue to explore alternative options. “Until CMS takes steps to develop a plan with time frames and milestones to eliminate the use of knowledge-based verification, CMS and Healthcare.gov applicants will remain at an increased risk of identity fraud,” wrote Gao in the report.

GAO has also called for the Office of Management and Budget (OMB) to issue guidance to federal agencies requiring them to report their progress in adopting more secure ID verification methods.

The post CMS Uses Weak ID Verification and Has No Plans to Change appeared first on HIPAA Journal.

OCR Clarifies Allowable Uses and Disclosures by Health Plans for Care Coordination and Continuity of Care

The Department of Health and Human Services’ Office for Civil Rights has issued new HIPAA guidance for health plans on how protected health information can be shared to support care coordination and continuity of care.

The guidance, which is in the form of an FAQ, answers two questions commonly asked by health plans:

Can PHI be disclosed to another health plan for care coordination purposes?

OCR has confirmed that the HIPAA Privacy Rule allows PHI to be used and disclosed for healthcare operations, so it is possible to share PHI with another health plan or other covered entity if doing so is necessary for the entity’s own healthcare operations. PHI can also be shared with another health plan for the recipient’s healthcare operations provided the following conditions are met: Both entities have or had a relationship with the individual, the disclosure pertains to that relationship, and the healthcare operation is one permitted by HIPAA (See 45 CFR 164.502(a)(1)(ii); 45 CFR 164.506(c)(4))

Case management and care coordination are included in permitted ‘healthcare operations,’ so they are permitted without patient authorization, but any disclosures should be limited to the minimum necessary information.

Can a health plan use and disclose PHI to inform individuals about other available health plans, without first obtaining authorization and Is this possible if PHI was received for another purpose?

Uses and disclosures of PHI for marketing purposes is generally not permitted without prior authorization. Using PHI for the purposes of offering an individual a different health plan could be seen to be marketing and would therefore only be permitted with prior authorization.

However, there are exceptions to marketing rule. Marketing communications are permitted face to face – 5 CFR 164.508(a)(3)(i) and HIPAA also does not count communications regarding replacements to, or enhancements of, existing health plans, provided the covered entity is not receiving financial remuneration for the communications. (See 45 CFR 164.506(c)(1) and 45 CFR 164.501). It is also permitted to use PHI that has been received for another purpose if the above conditions are met.

You can view the new OCR FAQ on this link.

The post OCR Clarifies Allowable Uses and Disclosures by Health Plans for Care Coordination and Continuity of Care appeared first on HIPAA Journal.

Patient Care Coordinator Gets 1 Year Jail Term for HIPAA Violation

A former patient care coordinator at University of Pittsburgh Medical Center (UPMC) has received a 1-year jail term for accessing the medical records of patients and using that information to cause malicious harm.

Sue Kalina, 62, of Butler, PA, had previously worked at UPMC Tri Rivers Musculoskeletal and Allegheny Health Network as a patient care coordinator. On March 30, 2016, while employed by UPMC, Kalina first started accessing patients’ medical records without authorization. She continued to do so until June 15, 2017.

Kalina accessed the records of friends, old classmates, and individuals that she had an aggrievance with. She used information from the medical records in a campaign of vengeance against her former employer, Frank J. Zottola Construction.

Kalina had worked at the firm as office manager for 24 years before losing the position and being replaced by a younger woman. Kalina accessed that woman’s medical records and disclosed gynecological information about the moan to the Zottola controller in June 2017. Kalina also left a voicemail message in which the medical information of the new office manager and one other Zottola employee was disclosed.

Zottola informed UPMC and Kalina was terminated. She was later hired by Allegheny Health Network where she is alleged to have continued to access patient records without authorization. In total, Kalina accessed the records of 111 patients without authorization.

Kalina took responsibility for her actions but claimed she was going through a difficult time in her life and had health issues. She also claimed she was not aware she was breaking the law and thought she was not prohibited from looking at patient files. Kalina and her legal team were seeking probation due to Kalina’s ongoing family commitments.

Prosecutors argued Kalina had been provided with HIPAA training and was aware that she was breaking the law and to claim ignorance of that was ‘a complete farce.” The U.S. attorney’s office sought a jail term of between 6 and 12 months.

At sentencing, U.S. District Judge Arthur Schwab opted for a jail term at the top end of that scale as the crime was particularly ‘egregious.’ Kalina was sentenced to 12 months in jail followed by 3 years of probation. During that time frame Kalina is not permitted to have any contact with any of the 111 victims.

The post Patient Care Coordinator Gets 1 Year Jail Term for HIPAA Violation appeared first on HIPAA Journal.

2,200 Franciscan Health Patients Notified of Unauthorized PHI Access by Employee

Mishawaka, IN-based Franciscan Health has discovered the protected health information of approximately 2,200 patients has been accessed by a former employee without authorization.

The privacy violation was discovered during a routine privacy audit. Franciscan Health announced that it was confirmed on May 24, 2019 that an employee in the quality research department had accessed the electronic medical records of patients without authorization and with no legitimate work reason for doing so.

The individual concerned is no longer employed by Franciscan Health and the matter has been reported to law enforcement. While unauthorized PHI access was confirmed, Franciscan Health found no evidence to suggest that the employee copied, transmitted, or disclosed any patient information.

Patient information was stored in Franciscan Health’s medical record system, which has been in use since 2012. Through that system, the former employee accessed patient records containing information such as names, addresses, email addresses, dates of birth, phone numbers, gender information, race/ethnicity, last four digits of social security numbers, and medical record numbers.

For certain patients, the following information may also have been accessed: Physician name, diagnoses, lab test results, medications, other treatment information, driver’s license numbers, emergency contact information, and insurance claims information. The records contained the full Social Security numbers of a small subset of patients.

All patients whose protected health information was compromised will be notified by mail and provided with information on how they can sign up for identity theft protection services.  Franciscan Health will cover the cost of those services for 2 years.

Medical Records Abandoned Outside Shuttered Chicago Medical Center

City crews have begun a clean up operation to remove boxes of medical records that have been abandoned outside a shuttered medical center in the Chatham area of Chicago, IL.

Boxes of medical records containing sensitive patient information had been dumped outside the former Medical Professional Home Healthcare center.

The Medical Professional Home Healthcare center was run by Carmen Dooley. In April 2017, the state health medical department license for Dooley and her business expired and was not renewed. The Illinois Department of Public Health visited the property and found it to be unoccupied with utilities cut off. The owner of the business could not be contacted and the agency was decertified by Medicare in 2017.

According to a recent report on CBS, the records had been stored in storage containers on the property. However, the containers were removed and their contents were dumped on site in 5-foot high piles. Some owners of local properties said the records had been there for months and some paperwork containing sensitive information had blown into their years. According to the report, Dooley had not authorized the removal of the storage containers and was unaware that the records had been abandoned.

The post 2,200 Franciscan Health Patients Notified of Unauthorized PHI Access by Employee appeared first on HIPAA Journal.

Vulnerabilities in Servers Behind Majority of Healthcare Data Breaches

Cybercriminals are managing to find and exploit vulnerabilities to gain access to healthcare networks and patient data with increasing regularity. The past two months have been the worst and second worst ever months for healthcare data breaches in terms of the number of breaches reported.

Phishing attacks on healthcare organizations have increased and email is now the most common location of breached protected health information. However, a recent analysis of the data breaches reported to the Department of Health and Human Services’ Office for Civil Rights (OCR) in the past 12 months has revealed servers to be the biggest risk. Servers were found to be involved in more than half of all healthcare data breaches.

Clearwater Cyberintelligence Institute (CCI) analyzed the 90 healthcare data breaches reported to OCR in the past 12 months. Those breaches resulted in the exposure, impermissible disclosure, or theft of the records of more than 9 million individuals.

The CCI analysis revealed 54% of all reported breaches of 500 or more healthcare records were in some way related to servers.

Servers house essential programs that are used across the healthcare organization. As a central repository of programs and data, they are an attractive target for hackers. Once access has been gained, data can be viewed, copied, altered, or deleted, systems can be sabotaged, and healthcare organizations can be subjected to extortion using ransomware.

CCI performed a risk analysis to determine high and critical risks facing health systems and hospitals. CCI determined 63% of all identified risks were related to the failure to adequately address vulnerabilities in servers.

The high number of server-related data breaches clearly shows that those flaws are being exploited by hackers to gain access to healthcare networks.

According to CCI, one of the most common server vulnerabilities is the failure to keep on top of user account management. When employees leave the company their accounts must be deleted. Dormant accounts are a major risk and are often used by malicious actors to access systems and mask their activities. CCI notes the risk increases with the number of accounts that are left dormant. The longer those accounts are left open, the greater the likelihood that at least one will be used for illicit or malicious purposes.

To address this risk, security controls should be implemented that automatically disable or delete accounts when the HR department changes the status of an employee. If that is not possible, CCI recommends conducting frequent, periodic reviews to ensure all unused accounts are disabled.

In an ideal world, an account would be disabled instantly. In practice, CCI recommends having the systems, policies, and procedures in place to ensure no account remains open for more than 48 hours after it is no longer required.

Reviews of system activity logs should also be conducted to determine whether dormant accounts have been used inappropriately or if any actively used accounts have been compromised or are being misused.

Excessive permissions on user accounts is another serious server vulnerability. Excessive permissions can result in accidental or deliberate access, alteration, or deletion of data. The failure to restrict access rights is also a violation of the HIPAA principle of least privilege.

CCI reports that the risk of excessive user permissions is highest in organizations that do not regularly review user permissions (43.6%), perform user activity reviews (43.6%), or when there is a lack of proper user account management (43.1%).

Regular reviews of user activity will help healthcare organizations to quickly identify anomalies in user data that could be indicative of account misuse or a cyberattack. The frequency of those reviews should be dictated by several factors, including staff turnover and the number of users. CCI suggests user permission and user activity log reviews at least every quarter for an organization with 100 or more users.

The post Vulnerabilities in Servers Behind Majority of Healthcare Data Breaches appeared first on HIPAA Journal.

May 2019 Healthcare Data Breach Report

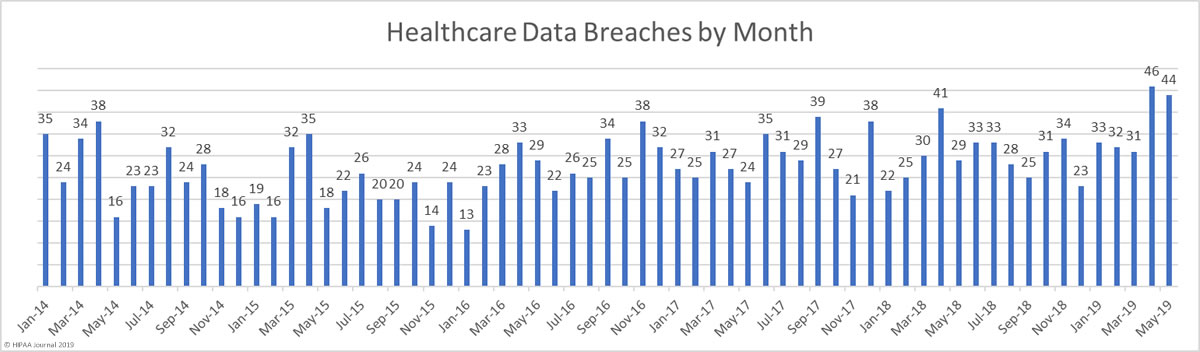
In April, more healthcare data breaches were reported than in any other month to date. The high level of data breaches has continued in May, with 44 data breaches reported. Those breaches resulted in the exposure of almost 2 million individuals’ protected health information.
Healthcare data breaches by month 2014-2019

On average, 2018 saw 29.5 healthcare data breaches reported to the HHS’ Office for Civil Rights each month – a rate of more than one a day.

From January 2019 to May 2019, an average of 37.2 breaches have been reported each month. Up until May 31, 2019, 186 healthcare data breaches had been reported to OCR, which is more than half (52%) the number of breaches reported last year.

It remains to be seen whether the increase in data breaches is just a temporary blip or whether 40+ healthcare data breaches a month will become the new norm.
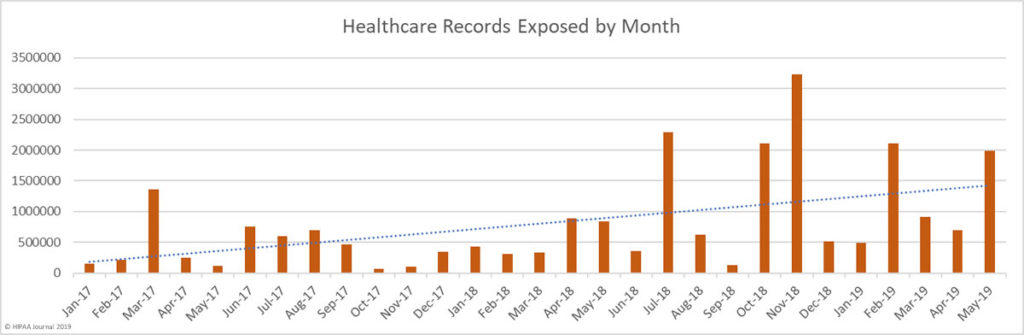
Healthcare records exposed by month 2017-2019

May saw a 186% increase in the number of exposed records compared to April. Across the 44 breaches, 1,988,376 healthcare records were exposed or compromised in May. So far this year, more than 6 million healthcare records have been exposed, which is more than half of the number of records exposed in 2018.
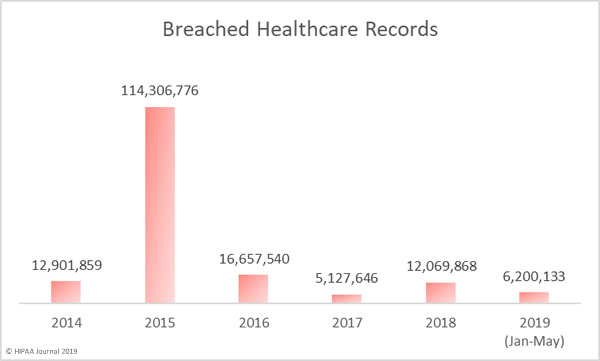
Healthcare records exposed by year 2014-2019

In terms of the number of records exposed, May would have been similar to April were it not for a massive data breach at the healthcare clearinghouse Inmediata Health Group. The breach was the largest of the year to date and resulted in the exposure of 1,565,338 records.

A web page which was supposed to only be accessible internally had been misconfigured and the page could be accessed by anyone over the internet.


Rank Name of Covered Entity Covered Entity Type Individuals Affected Type of Breach
1 Inmediata Health Group, Corp. Healthcare Clearing House 1,565,338 Unauthorized Access/Disclosure
2 Talley Medical Surgical Eyecare Associates, PC Healthcare Provider 106,000 Unauthorized Access/Disclosure
3 The Union Labor Life Insurance Company Health Plan 87,400 Hacking/IT Incident
4 Encompass Family and internal medicine group Healthcare Provider 26,000 Unauthorized Access/Disclosure
5 The Southeastern Council on Alcoholism and Drug Dependence Healthcare Provider 25,148 Hacking/IT Incident
6 Cancer Treatment Centers of America® (CTCA) at Southeastern Regional Medical Center Healthcare Provider 16,819 Hacking/IT Incident
7 Takai, Hoover, and Hsu, P.A. Healthcare Provider 16,542 Unauthorized Access/Disclosure
8 Hematology Oncology Associates, PC Healthcare Provider 16,073 Hacking/IT Incident
9 Acadia Montana Treatment Center Healthcare Provider 14,794 Hacking/IT Incident
10 American Baptist Homes of the Midwest Healthcare Provider 10,993 Hacking/IT Incident

Causes of May 2019 Healthcare Data Breaches

Hacking/IT incidents were the most numerous in May with 22 reported incidents. In total, 225,671 records were compromised in those breaches. The average breach size was 10,258 records with a median of 4,375 records.

There were 18 unauthorized access/disclosure incidents in May, which resulted in the exposure of 1,752,188 healthcare records. The average breach size was 97,344 records and the median size was 2,418 records.

8,624 records were stolen in three theft incidents. The average breach size 2,875 records and the median size was 3,578 records. There was one loss incident involving 1,893 records.
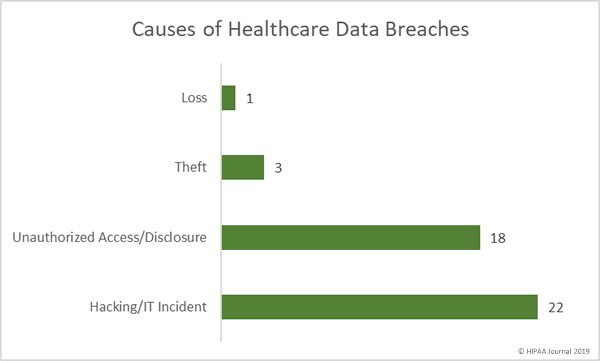
causes of May 2019 healthcare data breaches

Location of Breached PHI

Email continues to be the most common location of breached PHI. 50% of the month’s breaches involved at least some PHI stored in email accounts. The main cause of these types of breaches is phishing attacks.

Network servers were the second most common location of PHI. They were involved in 11 breaches, which included hacks, malware infections and ransomware attacks.  Electronic medical records were involved in 7 breaches, most of which were unauthorized access/disclosure breaches.

Location of breached PHi (may 2019)

May 2019 Healthcare Data Breaches by Covered Entity Type

Healthcare providers were the worst affected covered entity type in May with 34 breaches. 5 breaches were reported by health plans and 4 breaches were reported by business associates of HIPAA-covered entities. A further two breaches had some business associate involvement. One breach involved a healthcare clearinghouse.
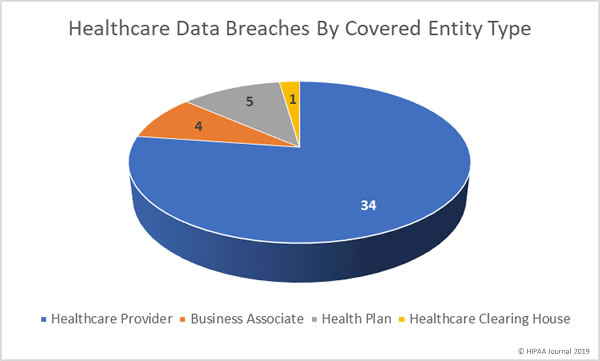
May 2019 healthcare data breaches by covered entity type

May 2019 Healthcare Data Breaches by State

May saw healthcare data breaches reported by entities in 17 states.  Texas was the worst affected state in May with 7 reported breaches. There were 4 breaches reported by covered entities and business associates in California and 3 breaches were reported in each of Indiana and New York.

2 breaches were reported by entities base in Connecticut, Florida, Georgia, Maryland, Minnesota, North Carolina, Ohio, Oregon, Washington, and Puerto Rico. One breach was reported in each of Colorado, Illinois, Kentucky, Michigan, Missouri, Montana, and Pennsylvania.

HIPAA Enforcement Actions in May 2019

OCR agreed two settlements with HIPAA covered entities in May and closed the month with fines totaling $3,100,000.

Touchstone Medical Imaging agreed to settle its HIPAA violation case for $3,000,000. The Franklin, TN-based diagnostic medical imaging services company was investigated after it was discovered that an FTP server was accessible over the internet in 2014.

The settlement resolves 8 alleged HIPAA violations including the lack of a BAA, insufficient access rights, a risk analysis failure, the failure to respond to a security incident, a breach notification failure, a media notification failure, and the impermissible disclosure of the PHI of 307,839 individuals.

Medical Informatics Engineering settled its case with OCR and agreed to pay a financial penalty of $100,000 to resolve alleged HIPAA violations uncovered during the investigation of its 2015 breach of 3.5 million patient records. Hackers had gained access to MIE servers for 19 days in May 2015.

OCR determined there had been a failure to conduct a comprehensive risk analysis and, as a result of that failure, there was an impermissible disclosure of 3.5 million individuals’ PHI.

It did not end there for MIE. MIE also settled a multi-state lawsuit filed by 16 state attorneys general. A multi-state investigation uncovered several HIPAA violations. MIE agreed to pay a penalty of $900,000 to resolve the case.

The post May 2019 Healthcare Data Breach Report appeared first on HIPAA Journal.