OneTouchPoint Agrees to Multi-Million Dollar Data Breach Settlement – The HIPAA Journal
OneTouchPoint Agrees to Multi-Million Dollar Data Breach Settlement The HIPAA Journal
OneTouchPoint Agrees to Multi-Million Dollar Data Breach Settlement
The Wisconsin mailing and printing vendor OneTouchPoint Corp. has agreed to settle class action litigation over a 2022 ransomware attack and data breach that affected more than 2.65 million individuals. The cyberattack that sparked the litigation was identified on April 28, 2022, when files were encrypted on its network. The forensic investigation determined that a ransomware group first accessed its network the previous day on April 27, 2022.
Data exposed and potentially stolen in the incident included names, subscriber ID numbers, diagnoses, medications, addresses, dates of birth, sex, physician demographic information, family histories, social histories, allergies, vitals, immunizations, and other information. OneTouchPoint reported the data breach to the HHS’ Office for Civil Rights as affecting 2,651,396 individuals and issued notifications to the affected individuals in April 2022.
Multiple class action lawsuits were filed in response to the data breach, all of which asserted similar claims. The lawsuits alleged that the data breach should have been prevented and was due to the failure of the defendant to implement reasonable and appropriate cybersecurity measures. The individual lawsuits were consolidated into a single action – Dusterhoft v. OneTouchPoint, Inc. – which is pending in the Circuit Court of Waukesha County, Wisconsin.
The consolidated lawsuit asserted claims for negligence, negligence per se, breach of contract, breach of implied contract, breach of fiduciary duty, breach of confidence, invasion of privacy, fraud, misrepresentation, unjust enrichment, bailment, wantonness, failure to provide adequate notice pursuant to any breach notification statute or common law duty, and violations of state consumer protection laws. All claims and contentions in the lawsuit were denied by the defendant, including claims of fault, wrongdoing, and liability. To avoid the costs and risks associated with a trial and related appeals, all parties agreed to settle the litigation.

Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
Under the terms of the settlement, OneTouchPoint has agreed pay attorneys’ fees and expenses up to $1,500,000, settlement administration costs, service awards of $1,000 for each of the class representatives, and monetary benefits and credit monitoring. The defendant also agreed to injunctive relief and will implement security enhancements valued at approximately $2,000,000, which will be maintained for at least five years.
The settlement class is divided into two subclasses – a monetary relief class and an injunctive relief class. The monetary relief class consists of individuals who were notified that their information had been impacted by the data breach. Those individuals may submit claims for monetary benefits. The injunctive relief class consists of individuals who were notified about the data breach, but the investigation could not determine that the data breach had an actual impact. Those individuals will benefit from the injunctive relief only.
All members of the monetary relief class may choose to receive a complimentary two-year subscription to a single-bureau credit monitoring service, which includes a $1 million identity theft insurance policy. In addition, claims may be submitted for compensation for documented, unreimbursed ordinary losses up to a maximum of $500 per class member, and up to $5,000 compensation for documented, unreimbursed extraordinary losses. In addition, compensation may be claimed for up to four hours of lost time at $25 per hour. Monetary relief class members who choose not to submit a compensation claim may claim an alternative one-time cash payment of $75.
The deadline for opting out of the settlement and objecting is October 16, 2026. Claims must be submitted by November 16, 2026, and the final approval hearing has been scheduled for November 18, 2026. Further information can be found on the settlement website: https://otpdataincident.com/
The post OneTouchPoint Agrees to Multi-Million Dollar Data Breach Settlement appeared first on The HIPAA Journal.
NFI North Data Breach Affects Almost 50,000 Individuals – The HIPAA Journal
NFI North Data Breach Affects Almost 50,000 Individuals The HIPAA Journal
NFI North Data Breach Affects Almost 50,000 Individuals
Data breaches have been announced by NFI North in New Hampshire, Nephrology Associates in Kansas, PAMCAH-UA Local 675 Health and Welfare Fund in Hawaii, and Indico Data Solutions in Massachusetts.
NFI North, Inc.
NFI North, Inc., a Contoocook, New Hampshire-based nonprofit human services organization that provides mental health, behavioral, and educational support services in New Hampshire and Maine, has notified the U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) about a breach of the protected health information of 49,540 individuals.
According to the NFI North substitute breach notice, suspicious activity was identified within its network on or around September 6, 2025. The investigation and data review concluded on July 6, 2026, when it was confirmed that data compromised in the incident included names, addresses, birth dates, Social Security numbers, driver’s license numbers, financial account information, medical information, and health insurance information. NFI North engaged cybersecurity professionals to assist with the investigation, and additional technical safeguards have been implemented to prevent similar incidents in the future.
Nephrology Associates
Nephrology Associates, M.D., P.A., a network of clinics in Kansas and Missouri that provide care to patients with chronic kidney disease and other kidney disorders, has announced a data security incident that has affected 24,088 individuals. Suspicious network activity was identified on or around April 9, 2026. Assisted by third-party cybersecurity experts, the practice determined that its network had been accessed by an unauthorized third party between January 17, 2026, and April 9, 2026. The affected systems were reviewed and, on July 1, 2026, the practice confirmed that data exposed in the incident included names, birth dates, Social Security numbers, driver’s license numbers/state identification numbers, other government identifiers, diagnosis and treatment information, and health insurance information.
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
On or around July 30, 2026, notification letters started to be mailed to the affected individuals. At the time of issuing the notifications, Nephrology Associates was unaware of any actual or attempted misuse of the exposed data. As a precaution against identity theft and fraud, individuals whose Social Security numbers were involved have been offered complimentary credit monitoring services. While not mentioned in the data breach notice, this appears to have been an attack by the cybercriminal group called The Gentlemen. No data appears to have been leaked; however, the group has offered the data for sale.
PAMCAH-UA Local 675 Health and Welfare Fund
PAMCAH-UA Local 675 Health and Welfare Fund, a multiemployer trust fund in Honolulu, Hawaii, that provides medical, dental, vision, and welfare benefits to union plumbers and fitters and their families, has identified unauthorized access to the email accounts of some of its employees.
The forensic investigation determined that certain employee email accounts were accessed by an unauthorized third party between September 23, 2025, and October 9, 2025. During that time, emails and files in the account may have been viewed or acquired. The accounts were reviewed and found to contain the personal and protected health information of 8,319 individuals, including names, dates of birth, medical information, health insurance information, driver’s license numbers, and Social Security numbers. Notification letters have now been mailed to the affected individuals with information on how they can protect themselves against data misuse.
Indico Data Solutions
Indico Data Solutions, Inc., a Massachusetts-based AI-powered software company whose products include an intake and orchestration platform, has announced a data security incident involving the protected health information of 4,840 individuals. It is unclear from the data breach notice when the incident was detected or for how long unauthorized individuals had access to its systems, only that a cybersecurity incident was confirmed by Indico Data Solutions on May 7, 2026. Data potentially compromised in the incident includes names, addresses, and Social Security numbers.
Indico Data Solutions has taken several steps in response to the incident, including rotating access credentials, tightening access controls, and implementing additional monitoring tools. The affected corporate customers have been notified, and Indico Data Solutions has mailed notification letters to the affected individuals and has offered complimentary credit monitoring and identity restoration services.
The post NFI North Data Breach Affects Almost 50,000 Individuals appeared first on The HIPAA Journal.
Luminis Health Working to Restore Systems After Cyberattack – The HIPAA Journal
Luminis Health Working to Restore Systems After Cyberattack The HIPAA Journal
Luminis Health Working to Restore Systems After Cyberattack
Luminis Health in Maryland is investigating a cyberattack that has taken certain systems offline. Data breaches have been announced by Texas Orthopedic surgeon Jeffrey David Reuben, M.D, Well Child in Tennessee, and Horizon Eye Care Laser & Eye Surgery Center in New Jersey.
Luminis Health, Maryland
Luminis Health, a nonprofit health system that includes Anne Arundel Medical Center in Annapolis and Doctors Community Medical Center in Lanham, announced on September 4, 2026, that it has fallen victim to a cyberattack. The incident has affected both hospitals, which continue to serve patients, although certain appointments have had to be rescheduled. Currently, the phone system and MyChart patient portal remain offline.
Luminis Health said the priority continues to be providing safe, high-quality care to patients; meanwhile, third-party cybersecurity and legal experts have been engaged to investigate and rectify the incident and safely and securely restore access to the affected systems. The health system is currently unable to provide a timeline for how long those processes will take, and it is too soon to tell what extent, if any, that patient data was involved. Should it be determined that patient data was exposed or stolen, patients will be notified in due course. At present, no ransomware or data extortion group appears to have claimed responsibility for the attack.
Jeffrey David Reuben, M.D.
Jeffrey David Reuben, M.D., a Texas-based orthopedic surgeon serving patients at NW Surgery in Houston and medical centers in Bellaire, has recently reported a data security incident that has affected 17,017 current and former patients. The incident was identified on or around April 27, 2026, and assisted by third party cybersecurity professionals, it was confirmed that an unauthorized third party accessed systems containing patient information between April 18 and April 19, 2026.
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
The investigation and data review were completed on or around July 15, 2026, when it was confirmed that the exposed data included names, Social Security numbers, driver’s license numbers, government-issued ID numbers, and financial information. While no actual or attempted misuse of the affected data has been identified, the affected individuals have been offered complimentary credit monitoring and identity theft protection services for 12 months.
Well Child
Well Child, a provider of school-based healthcare services through partnerships with school districts in Tennessee and Mississippi, has announced a cybersecurity incident that was first identified on June 1, 2026. All servers were immediately taken offline when the incident was identified to prevent further unauthorized access, and an investigation was launched to determine the nature and scope of the unauthorized activity. On June 5, 2026, the investigation confirmed that files containing sensitive personal information had been exfiltrated from a temporary storage server.
The investigation and data review are ongoing; however, it has been determined that the exfiltrated data included Vision Screening Reports, Vision Screening Data Files, Available Students Lists, and PEDS (Parents’ Evaluation of Developmental Status) assessment documents. In addition to student names, the files contained protected health information such as birth dates, medical record numbers, provider names, diagnoses, assessment/test results, treatment dates, and billing and/or procedure codes. For a limited number of individuals, Social Security numbers were also involved. The incident has been reported to the HHS’ Office for Civil Rights using a placeholder figure of at least 500 individuals. The total will be updated when the data review is concluded.
Horizon Eye Care Laser & Eye Surgery Center
Horizon Eye Care Laser & Eye Surgery Center, an ophthalmology practice and eye surgery center with six locations in New Jersey, is investigating a network server hacking incident. Suspicious network activity was identified on or around June 8, 2026. Immediate action was taken to isolate the affected systems, and third-party cybersecurity experts were engaged to investigate the incident.
The investigation and data review are ongoing; however, it has now been confirmed that patient data was compromised in the incident, including names, demographic information, treatment information, and health insurance information. The breach has been reported to the HHS’ Office for Civil Rights using a placeholder figure of at least 501 affected individuals, as the number of affected individuals has yet to be determined.
The post Luminis Health Working to Restore Systems After Cyberattack appeared first on The HIPAA Journal.
June 2026 Healthcare Data Breach Report – The HIPAA Journal
June 2026 Healthcare Data Breach Report The HIPAA Journal
June 2026 Healthcare Data Breach Report
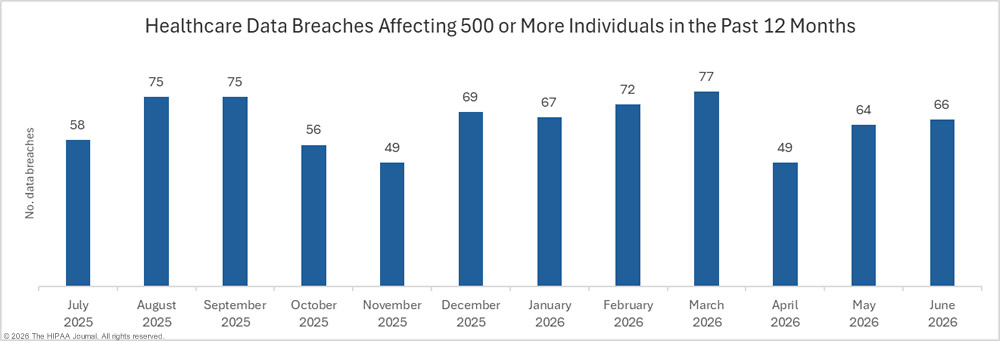
In June 2026, 66 large healthcare data breaches – data breaches involving the protected health information of 500 or more individuals – were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) – a slight increase from the 64 data breaches reported in May. More than two large data breaches a day is the new normal. Over the past 12 months, an average of 65 large healthcare data breaches have been reported per day; eight years ago in 2018, large healthcare data breaches occurred at a rate of around one per day.
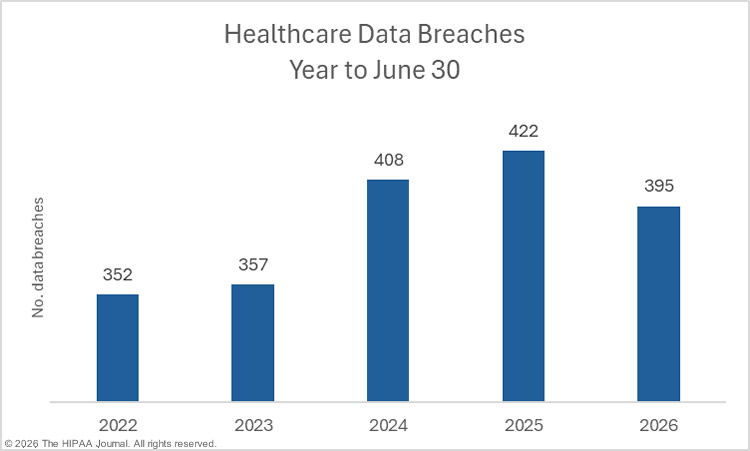
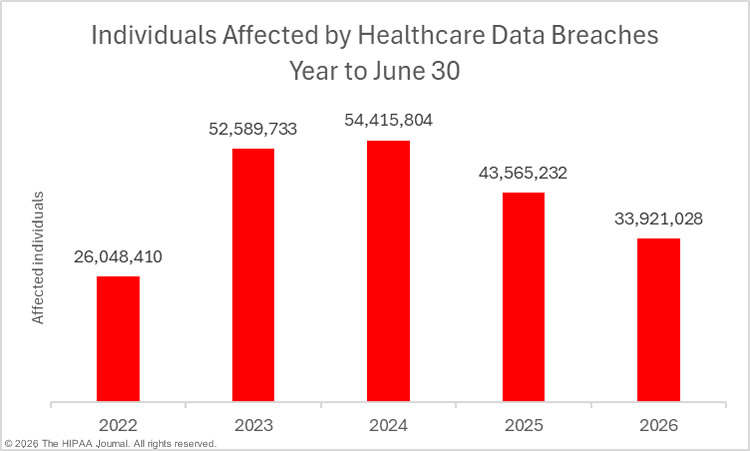
The year-to-date figures (Jan 1-Jun 30) show that healthcare data breaches are down 3.2% from the corresponding period in 2024 and down 6.4% from the corresponding period last year, although they are still occurring in significantly higher numbers than in 2022 and 2023.
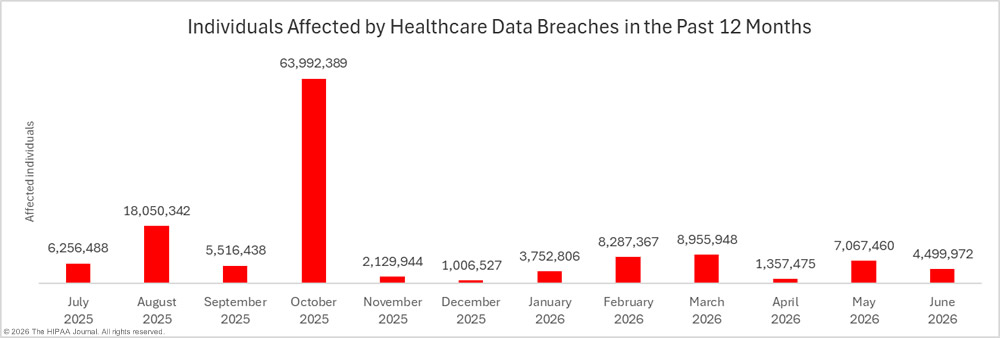
Across June’s 66 large healthcare data breaches, the protected health information of at least 4,499,972 individuals was exposed, stolen, or impermissibly disclosed. As data breach investigations continue, that figure is likely to increase. Based on current data, on average, 68,181 individuals were affected by each breach. The median data breach size was 6,306 individuals. While June’s victim total is substantial, the victim count is down 36.3% month-over-month, and 58.7% lower than the 12-month average of 10,906,096 individuals per month. It should be noted that the 12-month average is skewed by an unusually high total for October 2025.
The year-to-date figures for 2026 show a substantial improvement compared to recent years, and while almost 34 million individuals have had their protected health information exposed, stolen, or impermissibly disclosed so far in 2026, the victim count is down 37.7% from a high of 54.4 million individuals in 2024, and down 22.1% from 2025.
Get The FREE
HIPAA Compliance Checklist
Immediate Delivery of Checklist Link To Your Email Address
Please Enter Correct Email Address
Your Privacy Respected
HIPAA Journal Privacy Policy
The Biggest Healthcare Data Breaches Reported in June 2026
In June, 25 healthcare data breaches affecting 10,000 or more individuals were reported to the HHS. The two largest data breaches of the month occurred at business associates of HIPAA-covered entities, the largest of which was reported by Xsolis and affected almost 1.4 million individuals. Xsolis is a technology company that provides healthcare organizations with AI-powered solutions for case and utilization management. The incident occurred in January 2026 and started with a phishing email. The phishing attack provided the threat actor with access to systems and data for four days. Files exposed in the incident contained names, dates of birth, Social Security numbers, health insurance information, and medical treatment information.
The second-largest data breach of the month occurred at MCBS (Medical Computer Business Services) and affected more than 1.25 million individuals. MCBS is a healthcare billing, management, and revenue cycle management company. A data theft and extortion group called PEAR breached its network, exfiltrated files, and demanded a ransom to prevent the publication of the data. The threat group had access to the network for four days in September 2025 and stole files containing names, addresses, dates of birth, Social Security numbers, medical histories, health insurance information, and other sensitive data.
A significant breach was reported by the New Jersey-based Centers Lab NJ, a diagnostic testing laboratory for hospitals and other healthcare providers. This was also a data theft and extortion incident, involving the protected health information of more than 542,000 individuals. A threat group called Worldleaks claimed responsibility for the incident and had access to its network for 5 days in August 2025. Data stolen in the incident included names, dates of birth, Social Security numbers, passport numbers, driver’s license number/state ID numbers, medical information, and health insurance information.
| HIPAA-Regulated Entity | State | Covered Entity Type | Individuals Affected | Cause of Breach |
| Xsolis, Inc. | TN | Business Associate | 1,396,519 | Network server hacking incident |
| MCBS, LLC | GA | Business Associate | 1,261,464 | Data theft and extortion incident (PEAR) |
| Centers Lab NJ LLC | NJ | Healthcare Provider | 542,377 | Data theft and extortion incident (Worldleaks) |
| Anatomic and Clinical Laboratory Associates, P.C. | TN | Healthcare Provider | 169,626 | Network server hacking incident |
| Operation PAR, Inc. | FL | Business Associate | 145,714 | Data theft and extortion incident (Worldleaks) |
| Chicago Family Health Center | IL | Healthcare Provider | 90,000 | Network server hacking incident |
| Aitkin County Health and Human Services | MN | Business Associate | 83,114 | Phishing incident |
| Minnesota Epilepsy Group, P.A. | MN | Healthcare Provider | 80,061 | Network server hacking incident |
| Gay & Lesbian Community Services Center of Orange County, Inc. | CA | Healthcare Provider | 75,532 | Network server hacking incident |
| Colorado Health Network Inc. | CO | Healthcare Provider | 68,212 | Network server hacking incident – data theft confirmed |
| Women’s Center for Radiology | FL | Healthcare Provider | 66,422 | Network server hacking incident |
| Blue Fish Pediatrics | TX | Healthcare Provider | 62,150 | Network server hacking incident |
| NYC Health + Hospitals | NY | Healthcare Provider | 58,778 | Hacking incident at business associate |
| UnitedHealth Care Services, Inc. Single Affiliated Covered Entity | CT | Health Plan | 37,384 | Phishing incident at business associate |
| UnitedHealth Care Services, Inc. Single Affiliated Covered Entity | CT | Health Plan | 34,574 | Network server hacking incident |
| Kentucky Mountain Health Alliance | KY | Healthcare Provider | 30,830 | Network server hacking incident – data theft confirmed |
| Center for Hearing and Speech dba Texas Hearing Institute | TX | Healthcare Provider | 29,774 | Ransomware attack (Interlock) – data theft confirmed |
| Waveny LifeCare Network, Inc. | CT | Healthcare Provider | 27,113 | Network server hacking incident |
| Elara Caring | TX | Healthcare Provider | 22,172 | Hacking incident at third party vendor – data theft confirmed |
| Minidoka Memorial Hospital | ID | Healthcare Provider | 22,000 | Data theft and extortion incident (Blackwater) |
| Meridian Health Plan of Illinois | IL | Health Plan | 21,027 | Employee errors – Impermissible granting certain providers access to its network |
| City of Middletown | OH | Healthcare Provider | 20,608 | Ransomware attack – data theft confirmed |
| McLeod Physician Associates II | SC | Healthcare Provider | 19,553 | Malware identified on network server awaiting decommissioning |
| Optalis Management Solutions | MI | Healthcare Provider | 13,723 | Network server hacking incident |
| All About Women’s Care | CO | Healthcare Provider | 12,000 | Hacking incident via an employee VPN account – data theft confirmed |
In June, nine healthcare data breaches were reported to HHS with totals of 500 or 501 affected individuals. These totals are often used as placeholder figures when data reviews are ongoing and the 60-day reporting deadline under the HIPAA Breach Notification Rule is reached. HIPAA requires an estimate to be provided if the total number of affected individuals has yet to be determined. The data breaches in the table below may prove to be far larger than the initial breach report indicates. It may be several weeks or even months before the total number of affected individuals is confirmed.
| HIPAA Regulated Entity | State | Covered Entity Type | Individuals Affected | Cause of Breach |
| Gail J May Ltd d/b/a/ Insight Optical | IL | Healthcare Provider | 501 | Network server hacking incident at business associate |
| Community Health Center of Buffalo Inc. | NY | Healthcare Provider | 501 | Network server hacking incident |
| Cherry Street Services, Inc. | MI | Healthcare Provider | 501 | Network server hacking incident |
| Northeast Professional Caregivers | OH | Healthcare Provider | 500 | Email compromise |
| Columbia Orthopaedic Group | MO | Healthcare Provider | 500 | Network server hacking incident |
| Decatur Diagnostic Laboratory Inc. | AL | Healthcare Provider | 500 | Network server hacking incident |
| Ohio Living | OH | Healthcare Provider | 500 | Network server hacking incident |
| Signature Healthcare Corporation | MA | Healthcare Provider | 500 | Network server hacking incident |
| MVP VIP Holdco dba Heart of America Eye Care | MO | Healthcare Provider | 500 | Network server hacking incident |
Causes of June 2026 Healthcare Data Breaches
Out of the 25 data breaches affecting 10,000 or more individuals, all but one was due to hacking. Across all of June’s reported data breaches, 81.8% of the breaches were hacking/IT incidents, and 1,481,468 individuals were affected by those incidents – 89.7% of all individuals affected by data breaches in June. The average breach size was 81,091 individuals, and the median breach size was 6,504 individuals.
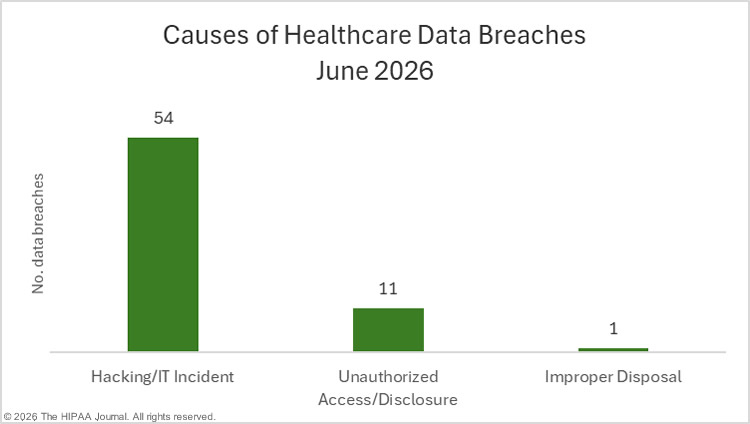
The largest unauthorized access/disclosure incident of the month – Meridian Health Plan of Illinois – affected 21,027 individuals and was due to employees granting healthcare providers access to a portal for managing patient information and processing claims that should not have been given access. There were 11 unauthorized access/disclosure incidents in June, accounting for 16.7% of the month’s data breaches, and 10,914 individuals were affected – 2.7% of the month’s affected individuals. The average breach size was 10,914 individuals, and the median breach size was 6,721 individuals. One improper disposal incident was reported affecting an estimated 1,000 patients. Paper records were disposed of along with regular trash, rather than being sent for shredding. No loss or theft incidents were reported in June.
Location of Breached Protected Health Information
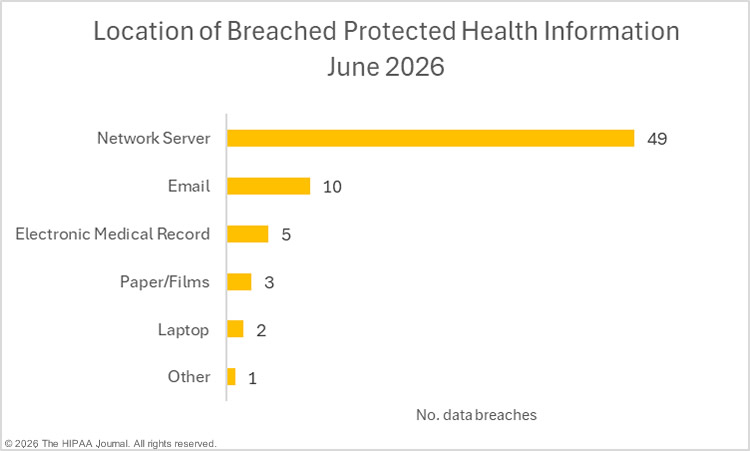
The bar chart below shows the locations of breached protected health information in June 2026 healthcare data breaches. Network servers were the most common location of breached protected health information, followed by email accounts and electronic health records.
Data Breaches at HIPAA Regulated Entities
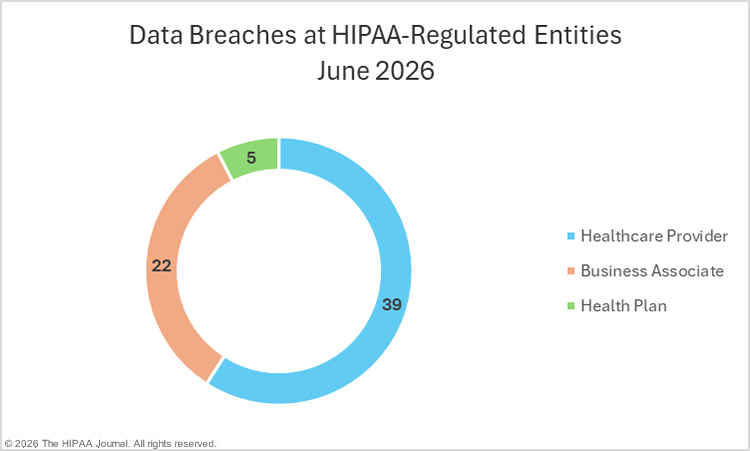
When a data breach occurs at a HIPAA-covered entity – healthcare provider, health plan, or healthcare clearinghouse – the HIPAA Breach Notification Rule requires them to report the breach within 60 days of discovery. When a data breach occurs at a business associate of a HIPAA-covered entity, the business associate must notify each affected covered entity within the same time frame.
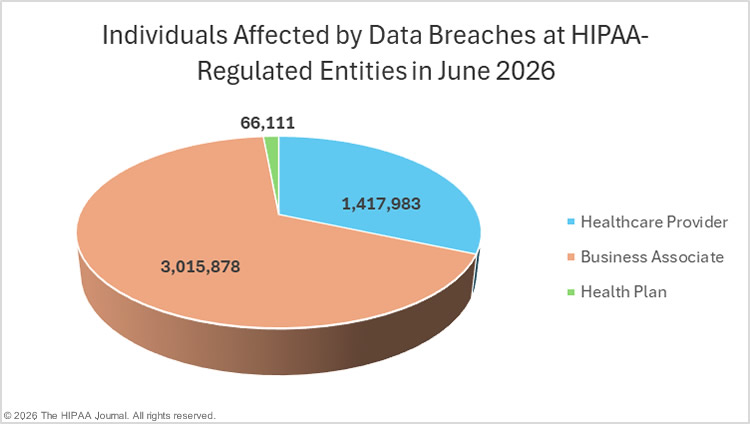
The affected covered entities are ultimately responsible for ensuring that notifications are issued to the HHS, individuals, and in some cases the media, within 60 days of being notified. A HIPAA-covered entity may delegate the notification responsibilities to the business associate. Some choose to issue notifications themselves. The raw breach data on the OCR breach portal shows data breaches based on the reporting entity, not where the data breach occurred. In June, healthcare providers reported 45 breaches, business associates reported 14 breaches, and 7 breaches were reported by health plans. The pie charts below show where the breach actually occurred rather than the reporting entity to better reflect breaches at business associates.
Geographical Distribution of Healthcare Data Breaches
In June, HIPAA-regulated entities based in 24 U.S. states reported large healthcare data breaches. Florida and Texas were the worst affected states with seven reported breaches per state.
| State | Breaches |
| Florida & Texas | 7 |
| Illinois | 5 |
| Colorado, Michigan & New York | 4 |
| California, Connecticut, Minnesota, Missouri, Ohio & Tennessee | 3 |
| Idaho, Kentucky, Massachusetts, South Carolina & Washington | 2 |
| Alabama, Georgia, Indiana, Kansas, New Jersey, Oklahoma & Pennsylvania | 1 |
While Florida and Texas ranked top for breaches, they ranked 4th and 6th in terms of the number of affected individuals. Tennessee, Georgia, and New Jersey topped the list for affected individuals, with each state only registering one large data breach.
| State | Individuals Affected | State | Individuals Affected |
| Tennessee | 1,567,038 | Michigan | 24,396 |
| Georgia | 1,261,464 | Idaho | 22,750 |
| New Jersey | 542,377 | Ohio | 21,608 |
| Florida | 233,367 | South Carolina | 20,690 |
| Minnesota | 164,893 | Washington | 9,825 |
| Texas | 124,459 | Missouri | 3,311 |
| Illinois | 120,089 | Indiana | 3,070 |
| Connecticut | 99,071 | Pennsylvania | 2,720 |
| Colorado | 87,814 | Oklahoma | 1,607 |
| California | 80,783 | Massachusetts | 1,506 |
| New York | 74,733 | Kansas | 534 |
| Kentucky | 31,367 | Alabama | 500 |
HIPAA Enforcement Activity in June 2026
In June, OCR announced a single enforcement action to resolve potential violations of the HIPAA Rules by the American mall-based retailer, Spencer Gifts. Retailers are not typically HIPAA-covered entities, but Spencer Gifts is a health plan under HIPAA as it sponsors employee benefits and welfare benefit plans. Spencer Gifts was investigated after OCR received a report about a breach of the protected health information of 10,023 members of its flexible benefits and welfare benefit plans. The OCR investigation determined that Spencer Gifts failed to conduct a HIPAA-compliant risk analysis and failed to implement HIPAA Privacy, Security, and Breach Notification Rule policies and procedures. The alleged HIPAA violations were resolved with a settlement that includes a $450,000 financial penalty and a corrective action plan.
In the year to June 30, 2026, OCR resolved seven HIPAA investigations with financial penalties with penalties totaling $1,728,000. All seven of the investigations found risk analysis failures, and two involved breach notification failures. State attorneys general may also investigate data breaches and impose financial penalties for HIPAA violations, although no cases were announced in June 2026.
About this Report
The HIPAA Journal monthly data breach reports are based on data obtained from the HHS Office for Civil Rights and have been combined with breach report data from other sources. The data breaches included in this report were reported in June 2026 but occurred weeks or months previously. The figures in this report may increase or decrease as HIPAA-regulated entities complete their breach investigations, and will be reflected in our healthcare data breach statistics page and our annual HIPAA data breach reports. Further information about HIPAA enforcement actions can be found in our HIPAA violations cases page.
The post June 2026 Healthcare Data Breach Report appeared first on The HIPAA Journal.