Healthcare Cybersecurity

September 2019 Healthcare Data Breach Report

September saw 36 healthcare data breaches of more than 500 records reported to the Department of Health and Human Services’ Office for Civil Rights, which represents a 26.53% decrease in breaches from the previous month.

1,957,168 healthcare records were compromised in those breaches, an increase of 168.11% from August. The large number of breached records is largely down to four reported incidents, each of which involved hundreds of thousands of healthcare records. Three of those incidents have been confirmed as ransomware attacks.
Largest Healthcare Data Breaches in September 2019

The largest breach of the month was due to a ransomware attack on Jacksonville, FL-based North Florida OB-GYN, part of Women’s Care of Florida. 528,188 healthcare records were potentially compromised as a result of the attack. Sarrell Dental also experienced a ransomware attack in which the records of 391,472 patients of its Alabama clinics were encrypted. 320,000 records of patients of Premier Family Medical in Utah were also potentially compromised in a ransomware attack. The University of Puerto Rico reported a network server hacking incident involving 439,753 records of Intramural Practice Plan members. The exact nature of the breach is unclear.

Those four breaches accounted for 85.80% of the healthcare records breached in September.

Name of Covered Entity Covered Entity Type Individuals Affected Type of Breach Location of Breached Information
Women’s Care Florida, LLC Healthcare Provider 528188 Hacking/IT Incident Network Server
Intramural Practice Plan – Medical Sciences Campus – University of Puerto Rico Healthcare Provider 439753 Hacking/IT Incident Network Server
Sarrell Dental Healthcare Provider 391472 Hacking/IT Incident Network Server
Premier Family Medical Healthcare Provider 320000 Hacking/IT Incident Network Server
Magellan Healthcare Business Associate 55637 Hacking/IT Incident Email
CHI Health Orthopedics Clinic -Lakeside Healthcare Provider 48000 Hacking/IT Incident Desktop Computer, Electronic Medical Record, Network Server
Kilgore Vision Center Healthcare Provider 40000 Hacking/IT Incident Network Server
Peoples Injury Network Northwest Healthcare Provider 27000 Hacking/IT Incident Network Server
Sweetser Healthcare Provider 22000 Hacking/IT Incident Email
Perfect Teeth Yale, P.C. Healthcare Provider 15000 Loss Other Portable Electronic Device

Causes of September 2019 Healthcare Data Breaches

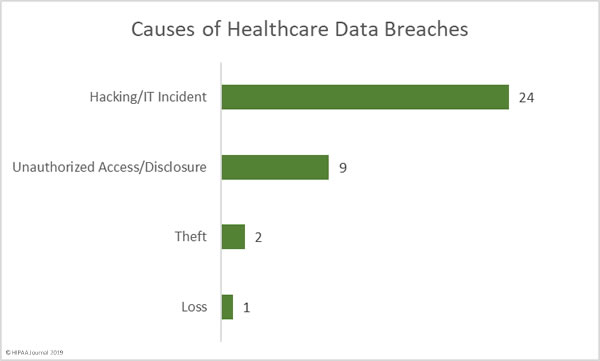
Hacking/IT incidents dominated the breach reports in September with 24 incidents reported. There were 9 unauthorized access/disclosure incidents and three cases of loss/theft of physical and electronic records.

1,917,657 healthcare records were compromised in the 24 hacking/IT incidents which accounted for 97.98% of breached records in September. The mean breach size was 958,829 records and the median breach size was 5,255 records.

Unauthorized access/disclosure incidents in September accounted for 1% or 19,741 breached records. The mean breach size was 2,193 records and the median breach size was 998 records. There were two reported theft incidents involving 4,770 physical and electronic records and a single loss incident involving 15,000 records stored on a portable electronic device.
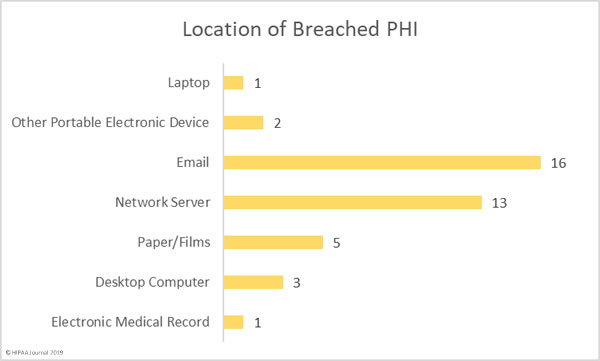
Location of Breached Protected Health Information

Phishing continues to be a major problem area for the healthcare industry. In September, 44.44% of all breaches – 16 incidents – involved PHI stored in email accounts. There were 13 network server incidents, a large percentage of which were ransomware attacks.
September 2019 Healthcare Data Breaches by Covered Entity Type

28 data breaches were reported by healthcare providers in September, four incidents were reported by health plans/health insurers, and four incidents were reported by business associates of HIPAA covered entities. A further four breaches had some business associate involvement but were reported by the covered entity.

States Affected by September 2019 Healthcare Data Breaches

September’s data breaches were reported by entities in 23 states and Puerto Rico. California, Maryland, and Washington were the worst affected with three breaches each. There were two breaches reported by entities based in Arkansas, Arizona, Colorado, Georgia, Indiana, and South Carolina, and one breach was reported in each of Alabama, Florida, Iowa, Illinois, Maine, Michigan, Nebraska, New Jersey, Ohio, Oklahoma, Tennessee, Texas, Utah, West Virginia, and Puerto Rico.

HIPAA Enforcement Activity in September 2019

In September 2019, the HHS’ Office for Civil Rights announced its third HIPAA violation penalty of the year. Bayfront Health St Petersburg in Florida was issued with an $85,000 financial penalty for the failure to provide a patient with a copy of her child’s fetal heart monitor records within a reasonable time frame. It took 9 months and multiple attempts by the patient before she was provided with the records.

This month, OCR Director Roger Severino gave an update on OCR’s main enforcement priorities and confirmed that noncompliance with the HIPAA right of access is still a major focus for OCR. Further financial penalties can be expected over the coming weeks and months for healthcare organizations that fail to provide individuals with copies of their health information within a reasonable time frame and at a reasonable cost.

There were no financial penalties issued by state attorneys general in September over HIPAA violations.

The post September 2019 Healthcare Data Breach Report appeared first on HIPAA Journal.

Microsoft and NCCoE Start Working on Guidelines for Implementing an Effective Enterprise Patch Management Strategy

A new project has been launched by Microsoft and the National Institute of Standards and Technology (NIST) National Cybersecurity Center of Excellence (NCCoE) to develop guidance on developing and implementing an effective patch management strategy.

Following the (Not)Petya wiper attacks in 2017, Microsoft embarked on a voyage of discovery into why companies had failed to exercise basic cybersecurity hygiene and had not patched their systems, even though patches had been released months previously and could have protected against the attacks.

Over the past 12 months, feedback has been sought from the Department of Homeland Security, the Cybersecurity and Infrastructure Security Agency (CISA), and the Center for Internet Security on the risk of exploitation and patch management strategies. Microsoft has also sat down with customers to find out more about the challenges they face applying patches and to discover exactly why patching is often delayed and why in some cases patches are not applied.

These meetings revealed many companies were unsure about what they should be doing in terms of patch testing. In some cases, patch testing appeared to consist only of asking questions on online forums to see if anyone had experienced any problems with recently released patches. Many customers were unsure about how fast patches needed to be applied.

The meetings prompted Microsoft to form a partnership with NCCoE to develop an enterprise patch management strategy to help companies plan and implement an effective patching strategy. The aim of the initiative is to devise industry guidance and standards to help companies improve their patch management processes.

The project is just about to commence and will involve developing common patch management architectures and processes. Appropriate vendors will assist by building and validating implementation instructions in the NCCoE lab and the project will ultimately result in a new NIST Special Publication 1800 practice guide on patch management.

An invitation has now been extended to vendors with technology offerings that can help with patch management, such as scanning, reporting, deployment, and risk measurement. Individuals and organizations willing to share patch management tips and tactics, and the lessons they have learned are also welcome to participate.

Any vendor, organization, or individual that wishes to participate should contact the project team on at cyberhygiene@nist.gov

The post Microsoft and NCCoE Start Working on Guidelines for Implementing an Effective Enterprise Patch Management Strategy appeared first on HIPAA Journal.

Adoption of Standards Improves Cybersecurity of Internet of Medical Things (IoMT) Devices

Internet of Medical Things (IoMT) technology is helping to increase efficiency, improve the quality of healthcare, and lower healthcare costs; however, IoMT introduces risks. The failure to reduce those risks to a low and acceptable level leaves IoMT devices vulnerable to cyberattacks. Those attacks can be expensive to resolve, which drives up the cost of healthcare and can result in patients coming to harm.

Not only must the devices be secured, cybersecurity must also be managed throughout the entire lifespan of the devices. Software and firmware must be kept up to date, patches must be applied promptly to fix vulnerabilities, and the devices need to be returned when they reach end of life and support comes to an end. Without a thorough understanding of the risks, securing IoMT devices can be a major challenge.

The U.S. Department of Veteran Affairs (VA) has taken steps to improve the safety and security of IoMT devices and has been seeking solutions for securing large-scale IoMT device deployments to better protect the 9 million people under its care. The VA, in conjunction with the global safety science organization, UL, launched a Cooperative Research and Development Agreement (CRADA) Program for medical device cybersecurity in 2016. This week, the VA announced that the program has now been completed.

The program was conducted between 2016 and 2018 and used the UL 2900 Series of Standards as a benchmark to identify critical medical device cybersecurity vulnerabilities in large-scale connected medical device deployments, including lifecycle management and created baseline cybersecurity requirements for medical device manufacturers.

“This collaboration helped us uncover new insights and further accelerate the sharing of medical device cybersecurity information, standards and lifecycle requirements with the intention of benefiting not only the VA hospital system but also the larger U.S. healthcare system of providers and manufacturers,” explained Anura Fernando, UL’s chief innovation architect, Life and Health Sciences.

Throughout the two years, the VA and UL tested hypotheses to expand their understanding of medical device cybersecurity and identify security gaps between in-facility and in-home care and ensure product functionality for FIPS 140-2 compliance. A simulated hacking attack was also conducted on a UL 2900 certified medical device at the Veterans Health Administration (VHA) site in Tampa, FL.

The report shows adoption of standards helps to ensure the safety and security of new medical devices. The findings of the study have resulted in the creation of a series of actionable steps that can be taken by healthcare organizations to improve the security of their medical devices.

“The report findings will help the VA ensure safety for its patient community while also serving as a model for how we can continue to drive innovation within the larger healthcare ecosystem,” said Marc Wine, Director, Technical Integration Support and Industry Liaison, U.S. Department of Veterans Affairs.

CRADA findings included:

  • Use of UL 2900 Series of Standards and product testing/certification accelerated adoption of innovative healthcare technologies through improved pre-procurement product vetting and post-procurement product management.
  • Testing and certification improved confidence in product development processes, security control design evaluation, post market patch management support provided by device manufacturers.
  • Compliance with UL 2900 enhanced endpoint security resulted in improved allocation of cybersecurity resources allowing them to be focused on critical threats to veterans’ safety and security.

The post Adoption of Standards Improves Cybersecurity of Internet of Medical Things (IoMT) Devices appeared first on HIPAA Journal.

Report Reveals the Most Common Cyber Threats Faced by Healthcare Organizations

A new report from Proofpoint offers insights into the cyber threats faced by healthcare organizations and the most common attacks that lead to healthcare data breaches.

Proofpoint’s 2019 Healthcare Threat Report highlights the ever-changing threat landscape and how the tactics used by cybercriminals are in a constant state of flux.

The study – conducted between Q2, 2018 and Q1, 2019 – shows how the malware variants used in attacks often change. Ransomware was a popular form of malware in Q2, 2018 and was used in many attacks on healthcare organizations, but ransomware incidents then dwindled rapidly as cybercriminals switched their attention to banking Trojans. For the remaining three quarters of the study period, banking Trojans were the malware variant of choice, although ransomware is now proving popular once again.

Proofpoint’s research shows banking Trojans were the biggest malware threat to healthcare organizations for the period of the study, accounting for 41% of malicious payloads delivered via email between Q2 2018 and Q1 2019. In Q1, 2019, the biggest threat came from the Emotet banking Trojan, which accounted for 60% of all malicious payloads.

While phishing attacks are a constant threat, malware attacks were more numerous over the period of study, although phishing attacks have increased considerably in 2019. Malware is often spread via email attachments, but URLs are also used to deliver malware. The embedded hyperlinks can direct users to phishing websites where credentials are stolen, but they can also send healthcare employees to websites where malware is silently downloaded. 77% of email-based attacks during the period of study used malicious URLs

Malicious emails are more likely to be opened if the sender of the email is known to the recipient. 95% of targeted healthcare companies received emails that spoofed their own trusted domain and 100% of targeted healthcare companies had their domain spoofed in attacks on their patients and business partners.

On average, targeted healthcare organizations received 43 imposter emails in Q1, 2019, an increase of 300% from Q1, 2018. Those attacks saw an average of 65 members of staff attacked at each healthcare organization.

While the subjects of the emails were highly varied, most commonly the subject lines contained the words “urgent”, “payment”, or “request.” Those words were included in 55% of malicious emails. Malicious emails are most commonly sent during business hours when employees are at their desks, usually between 7am and 1pm, Monday to Friday.

While spray and pray tactics are still used by cybercriminals to get their phishing emails and malware out to as many individuals as possible, many healthcare email attacks are much more targeted. Proofpoint analyzed email attacks at several healthcare organizations and found that some individuals are more targeted than others.

These “Very Attacked Persons” or VAPs include doctors/physicians, researchers, and admin staff at healthcare providers, customer support/sales staff, admin staff, and IT teams at health insurers, and executives, marketing employees, and logistics/sourcing and supply chain staff at pharma firms.

Shared email aliases used to request patient information or for patient portals received the most malicious emails. These email addresses have the potential to result in multiple malware infections and several responses to phishing emails.

Blocking these threats requires layered defenses. Anti-phishing and anti-malware solutions should be implemented to protect the email system, filtering controls are required to block web-based threats, anti-malware controls are required on endpoints, and employees must receive regular training to help them identify threats and condition them to take appropriate action when a suspicious email is received.

The post Report Reveals the Most Common Cyber Threats Faced by Healthcare Organizations appeared first on HIPAA Journal.

MITA Publishes New Medical Device Security Standard

The Medical Imaging & Technology Alliance (MITA) has released a new medical device security standard which provides healthcare delivery organizations (HDOs) with important information about risk management and medical device security controls to harden the devices against unauthorized access and cyberattacks.

The new voluntary standard – Manufacturer Disclosure Statement for Medical Device Security (MDS2) (NEMA/MITA HN 1-2019) – was developed in conjunction with a diverse range of industry stakeholders and aligns with the 2018 U.S. Food and Drug Administration (FDA) Medical Device Cybersecurity Playbook, issued in October 2018.

The guidance explains that cybersecurity of medical devices is a shared responsibility. HDOs must collaborate with medical device manufacturers to ensure best practices are adopted. Device manufacturers, HDOs, government entities, and cybersecurity researchers need to work together to ensure threats to medical devices are managed and reduced to reasonable and appropriate levels.

The new standard is intended to help streamline communications between device manufacturers and HDOs, increase transparency of information, and clarify the roles of each with respect to the security of medical devices.

“Transparent information and speed of getting that information from manufacturers to health delivery organizations are crucial, and this Standard helps foster both,” said Tim Walsh, Principal Information Security Analyst – CIS Operations, Mayo Clinic, and member of the MDS2 Canvass Group.

The guidance includes information on the standard security controls incorporated into medical devices to ensure they meet industry standards and can be used safely and securely; however, it is the responsibility of HDOs to ensure that the devices are configured correctly. HDOs need to assess medical device security controls and determine whether they are appropriate, work within their own environments, and allow risk to be effectively controlled and managed.

Worksheets have been created for assessing the features and security capabilities of each medical device, including the specifications, the management of personally identifiable information, audit controls, authorization controls, data backup and disaster recovery functions, data integrity controls, anti-malware protections, connectivity, node authentication, security guidance, how cybersecurity upgrades will be performed throughout the lifecycle of devices, and other key information for HDOs.

Medical device manufacturers should complete the worksheets to provide HDOs with the technical information they will need to conduct their own security risk assessments and build their security risk management programs.

While the MDS2 form contains important technical information on medical devices, MITA warns that it is not intended to be used as the sole basis for medical device procurement, as writing medical device procurement specifications requires more extensive knowledge of an HDO’s security environment and healthcare mission.

The information on the MDS2 form must be combined with detailed information collected about the care delivery environment in which the devices will be used. Tools such as ECRI’s Guide for Information Security for Biomedical Technology are useful in this regard.

The post MITA Publishes New Medical Device Security Standard appeared first on HIPAA Journal.

HHS Proposes New Stark Law Safe Harbor Covering Cybersecurity Donations

The U.S. Department of Health and Human Services (HHS) has proposed changes to physician self-referral and federal anti-kickback regulations which will see the creation of a new safe harbor covering hospital donations of cybersecurity software and associated services to physicians.

The proposed law change is detailed in two new rules issued by the HHS’ Office of Inspector General (OIG) and the Centers for Medicaid and Medicare Services (CMS) which aim to modernize and clarify regulations that interpret the Federal Anti-Kickback Statute and Physician Self-Referral law known as Stark Law.

The proposed rules are part of the HHS’s Regulatory Sprint to Coordinated Care which promotes value-based care by eliminating federal regulatory barriers that are impeding efforts to improve the coordination of care between providers.

“The digitization of the healthcare delivery system and related rules designed to increase interoperability and data sharing in the delivery of healthcare create numerous targets for cyberattacks,” explained OIG. “The healthcare industry and the technology used to deliver healthcare have been described as an interconnected ‘ecosystem’ where the ‘weakest link’ in the system can compromise the entire system.”

Physician practices are a possible weak link that could be exploited by threat actors to compromise the whole system. Many small healthcare providers lack the necessary resources to improve their security posture and ensure that their systems, networks, and patient data are adequately protected.

The proposed updates are intended to provide greater clarity for healthcare providers participating in value-based arrangements and are providing coordinated care for patients. They are intended to ease the compliance burden for healthcare providers while ensuring strong safeguards are maintained to protect patients and programs from fraud and abuse.

There is already an exception to Stark Law which permits healthcare providers to make EHR-related donations to physicians as well as donations of cybersecurity software and services. The proposed rule seeks to provide greater certainty for healthcare providers that such donations do not violate Stark Law.

The new safe harbor will remove real or perceived barriers that prevent parties from using cybersecurity technologies to improve security. The safe harbor was recommended by the HHS Healthcare Industry Cybersecurity Task Force in 2017 and will cover certain cybersecurity technologies and associated services that are essential for protecting against cyberattacks on the healthcare industry. Those attacks increase the costs of healthcare delivery and often prevent healthcare providers from accessing health records and other information essential for healthcare delivery.

In the context of the proposed rule changes, OIG defines cybersecurity as “the process of protecting information by preventing, detecting, and responding to cyberattacks.” Covered cybersecurity technology includes software or information technology that improves cybersecurity, but there are limitations on what can be donated. The rule includes software, cybersecurity training services, business continuity and data recovery services, services associated with security risk assessments, threat sharing services, and cybersecurity-as-a-service offerings.

The OIG rule does not permit donations of hardware as it could have uses outside of cybersecurity and would increase the risk of donations being made to influence referrals. OIG says it may consider updating its proposed rule to include certain types of stand-alone hardware that can only be used for cybersecurity purposes, such as multi-factor authentication dongles.

The proposed rules will help to reduce the cost of healthcare by helping smaller healthcare providers avoid the costs of improving their security posture and reduce the potential for costly cyberattacks. By receiving donations of necessary software and cybersecurity services, they will be able to direct funds to other items and services not covered by the proposed safe harbor.

“Administrative costs are driving up the cost of healthcare in America – to the tune of hundreds of billions of dollars. The Stark proposed rule is an important next step in President Trump’s healthcare agenda for Americans. We are updating our antiquated regulations to decrease burden for providers and helping bring down these increasingly escalating costs,” said CMS administrator Seema Verma.

“Regulatory reform has been a key piece of President Trump’s agenda not just for faster innovation and economic growth, but also better, higher-value healthcare. Our proposed rules would be an unprecedented opportunity for providers to work together to deliver the kind of high-value, coordinated care that patients deserve,” said HHS Secretary, Alex Azar.

The post HHS Proposes New Stark Law Safe Harbor Covering Cybersecurity Donations appeared first on HIPAA Journal.

McCombs School of Business Offers Nation’s First Healthcare-Specific Professional Cybersecurity Certification Program

The University of Texas at Austin McCombs School of Business has launched a unique healthcare-specific professional cybersecurity certificate program. The professional leadership and educational program is the first healthcare oriented cybersecurity certification program to be offered in the United States.

The Leadership in Healthcare Privacy and Security Risk Management program aligns with the NICE Cybersecurity Workforce Framework and will equip individuals with the knowledge and leadership skills they will need to effectively manage cyber risks faced by the healthcare industry.

Figures from the (ISC)² Global Information Security Workforce Study indicate the cybersecurity workforce gap is growing and there will be 1.8 million unfilled cybersecurity positions in 2022. The new certification program will help to address that shortfall in trained cybersecurity personnel, which is hampering many healthcare organizations’ efforts to address privacy and security risks.

The new course was developed in collaboration with the cybersecurity industry, healthcare privacy and security experts, and government agencies and is focused on risk management in the healthcare industry. The course aims to teach the necessary cybersecurity, risk assessment, and problem-solving skills to meet the needs of healthcare providers, vendors serving the healthcare industry, and government agencies.

The 8-week course will equip students with problem solving competencies and provide them with experience of healthcare security technologies through practical exercises and case studies. Tuition will be provided by experienced healthcare technology educators and cross-sector privacy and security experts. The course comprises of multiple thematic modules to provide students with core healthcare and privacy & security knowledge, processes to ensure organizational safety and security, policies and governance in healthcare entities, enterprise risk management and leadership in healthcare, along with practical applications of healthcare privacy and security.

The program will be constantly updated based on feedback from members of the privacy and cybersecurity industry on real-world cyber threats to ensure the program remains current and relevant.

The new program has been endorsed by the Texas Hospital Association, CynergisTek, and Clearwater Compliance. “What is unique about this curriculum is that they have integrated cybersecurity knowledge so that graduates of this program not only prepare themselves for a career in healthcare by learning practical skills, but they learn about where cybersecurity is important and why they need to understand it to be successful,” said Mac McMillan, co-founder and CEO of CynergisTek, Inc. “These are the type of visionary programs we need more of if we are going to close this gap in cybersecurity skills.”

The course is aimed at experienced professionals in cybersecurity, health IT, risk management, clinical professions, and information technology who are looking to move into non-technical leadership positions in healthcare privacy and security. The program will commence in July 2020.

The post McCombs School of Business Offers Nation’s First Healthcare-Specific Professional Cybersecurity Certification Program appeared first on HIPAA Journal.

Pulse Connect, GlobalProtect, Fortigate VPN Vulnerabilities Being Actively Exploited by APT Actors

Vulnerabilities in popular VPN products from Pulse Secure, FortiGuard, and Palo Alto are being actively exploited by advanced persistent threat (APT) actors to gain access to vulnerable VPNs and internal networks.

The DHS’ Cybersecurity and Infrastructure Security Agency (CISA) and other cybersecurity agencies issued security advisories about multiple vulnerabilities in VPN products over the summer of 2019; however, many organizations have been slow to take action. Weaponized exploits for the vulnerabilities have now been developed and are being used by APT actors and exploit code is freely available online on GitHub and the Metasploit framework.

On October 1, 2019, the UK’s National Cyber Security Centre issued a warning about the vulnerabilities following several attacks on government agencies, the military, businesses, and the education and healthcare sectors. The National Security Agency (NSA) also issued a security advisory about the vulnerabilities along with mitigations on October 7.

The vulnerabilities are present in outdated versions of the Pulse Secure VPN (CVE-2019-11508 and CVE-2019-11538), the Palo Alto GlobalProtect VPN (CVE-2019-1579), and the Fortinet Fortigate VPN (CVE 2018-13379, CVE-2018-13382, CVE-2018-13383).

No mention was made about the APT actors responsible for the attacks, although there have been reports that the Chinese APT group APT5 has been conducting attacks on Pulse Secure and Fortinet VPNs.

The weaponized exploits allow APT actors to retrieve arbitrary files, including those containing authentication credentials. Those credentials can then be used to gain access to vulnerable VPNs, change configurations, remotely execute code, hijack encrypted traffic sessions, and connect to other network infrastructure.

The flaws are serious and require immediate action to prevent exploitation. The NSA security advisory urges all organizations using any of the above products to check to make sure they are running the latest versions of VPN operating systems and to upgrade immediately if they are not.

The NSA advisory also provides information on actions to take to check whether the flaws have already been exploited and steps to take if an attack is discovered. If a threat actor has already exploited one of the vulnerabilities and has obtained credentials, upgrading to the latest version of the OS will not prevent those credentials from being used.

The NSA therefore advises all entities running vulnerable VPN versions to reset credentials after the upgrade and before reconnection to the external network as a precaution, since it may be difficult to identify an historic attack from log files.

User, administrator, and service account credentials should be reset, and VPN server keys and certificates should be immediately revoked and regenerated. If a compromise is suspected, accounts should be reviewed to determine whether the attacker has created any new accounts.

The NSA has also provided recommendations for public-facing VPN deployment and long-term hardening controls.

The post Pulse Connect, GlobalProtect, Fortigate VPN Vulnerabilities Being Actively Exploited by APT Actors appeared first on HIPAA Journal.

An Internal Security Operations Center Cuts Data Breach Costs by More Than Half

A recent survey conducted by B2B International on behalf of Kaspersky Lab has revealed the average cost of an enterprise-level data breach has risen to $1.41 million from $1.23 million in 2018.

The increased risk of a data breach and the increasing remediation costs has prompted enterprises to invest more heavily in cybersecurity. When the Kaspersky Global Corporate IT Security Risks Survey was last conducted in 2018, average IT security budgets were $8.9 million. In 2019, budgets had increased to an average of $18.9 million.

The biggest costs from a data breach were found to be damage to the company’s credit rating and increased insurance costs, followed by the cost of hiring external security consultants, loss of business, brand repair, additional wages for internal staff, compensation, and financial penalties and regulatory fines.

While there are several things enterprises can do to cut data breach costs, the appointment of a dedicated Data Protection Officer (DPO) and deploying an internal Security Operations Center (SOC) are the two most important for reducing cyberattack-related costs.

A DPO is responsible for creating and implementing a data protection strategy and monitoring and managing compliance issues. 34% of enterprises that had a dedicated DPO said security incidents at their company did not result in financial losses, compared to 20% of businesses overall.

The average data breach cost at an organization with an internal SOC was $675,000 – Less than half the cost of a breach at an organization without an internal SOC. The equivalent cost at large SMBs (500+ employees) was $129,000. With an internal SOC in place to monitor and respond to security incidents, the cost of a data breach was reduced to $106,000.

The survey revealed outsourcing security to managed service providers can result in increased data breach costs, at least for enterprises. 23% of businesses that used an MSP for security experienced data breach costs in the range of $100,000 to $249,000, compared to 19% of businesses with an in-house IT security team.

Appointing a DPO and setting up an internal SOC can help to reduce the likelihood of a data breach occurring, but it does not mean all data breaches will be prevented. With these key personnel in place, when a breach does occur the company will be prepared and will be able to respond quickly and efficiently, which will keep the costs to a minimum.

Recruiting a DPO, hiring staff for an internal SOC, and purchasing the necessary tools to support those personnel can be a time consuming and costly process, but the survey shows investment in key internal security personnel is certainly worthwhile and can significantly reduce the costs of data breaches. 61% of enterprises and SMBs in the United States are planning on increasing investment in specialized IT staff in the next 12 months.

The post An Internal Security Operations Center Cuts Data Breach Costs by More Than Half appeared first on HIPAA Journal.