Healthcare Cybersecurity

Summary of 2018 HIPAA Fines and Settlements

This post summarizes the 2018 HIPAA fines and settlements that have resulted from the enforcement activities of the Department of Health and Human Services’ Office for Civil Rights (OCR) and state attorneys general.

Another Year of Heavy OCR HIPAA Enforcement

In 2016, there was a significant increase in HIPAA files and settlements compared to the previous year. In 2016, one civil monetary penalty was issued by OCR and 12 settlements were agreed with HIPAA covered entities and their business associates. In 2015, OCR only issued 6 financial penalties.

The high level of HIPAA enforcement continued in 2017 with 9 settlements agreed and one civil monetary penalty issued.

While there were two settlements agreed in February 2018 to resolve HIPAA violations, there were no further settlements or penalties until June. By the end of the summer it was looking like OCR had eased up on healthcare organizations that failed to comply with HIPAA Rules.

However, in September, a trio of settlements were agreed with hospitals that had allowed a film crew to record footage of patients without first gaining consent. Further settlements were agreed in October, November, and December and OCR finished the year on one civil monetary penalty and 9 settlements to resolve HIPAA violations.
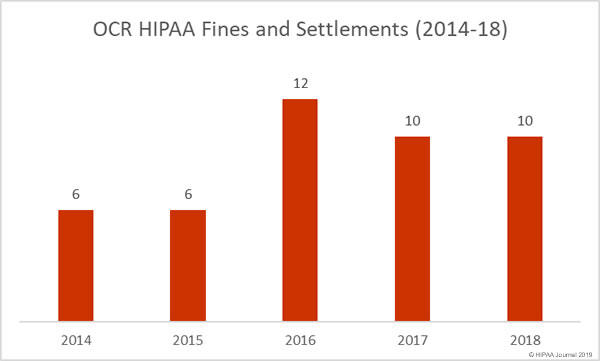
Summary of 2018 HIPAA Fines and Settlements

While 2018 was not a record-breaking year in terms of the number of financial penalties for HIPAA violations, it was a record-breaker in terms of the total penalty amounts paid. OCR received $25,683,400 in financial penalties in 2018. The mean financial penalty was $2,568,340.
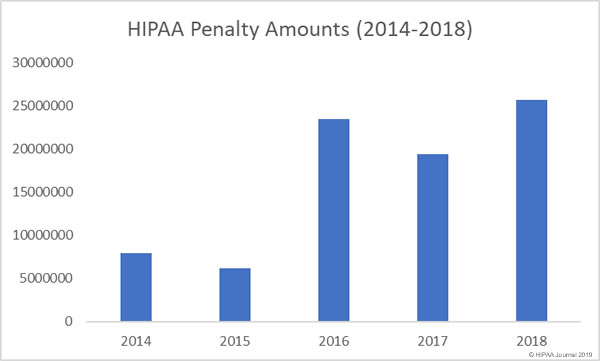
2018 HIPAA fines and penalties total

The median HIPAA fine in 2018 was $442,000: Much lower than 2017 median of $2,250,000. It was also the lowest median fine amount of the last 5 years, although 2018 did see the largest ever HIPAA violation penalty.

In October 2018, Anthem Inc., settled its HIPAA violation case with OCR for $16,000,000. The massive fine was due to the extent of the HIPAA violations discovered by OCR and the scale of its 2015 data breach, which saw the protected health information of around 78,800,000 plan members stolen by hackers.

2018 HIPAA Fines and Settlements

Year Covered Entity Amount Settlement/CMP Reason
February 2018 Fresenius Medical Care North America $3,500,000 Settlement Risk analysis failures, impermissible disclosure of ePHI; Lack of policies covering electronic devices; Lack of encryption; Insufficient security policies; Insufficient physical safeguards
February 2018 Filefax, Inc. $100,000 Settlement Impermissible disclosure of PHI
June 2018 University of Texas MD Anderson Cancer Center $4,348,000 Civil Monetary Penalty Impermissible disclosure of ePHI; No Encryption
September 18 Massachusetts General Hospital $515,000 Settlement Filming patients without consent
September 18 Brigham and Women’s Hospital $384,000 Settlement Filming patients without consent
September 18 Boston Medical Center $100,000 Settlement Filming patients without consent
October 2018 Anthem Inc $16,000,000 Settlement Risk Analysis failures; Insufficient reviews of system activity; Failure related to response to a detected breach; Insufficient technical controls to prevent unauthorized ePHI access
November 2018 Allergy Associates of Hartford $125,000 Settlement PHI disclosure to reporter; No sanctions against employee
December 2018 Advanced Care Hospitalists $500,000 Settlement Impermissible PHI Disclosure; No BAA; Insufficient security measures; No HIPAA compliance efforts prior to April 1, 2014
December 2018 Pagosa Springs Medical Center $111,400 Settlement Failure to terminate employee access; No BAA

State Attorneys General HIPAA Enforcement Activities

It is difficult to obtain meaningful statistics on HIPAA fines and settlements by state attorneys general. While state attorneys general can issue fines for violations of HIPAA Rules, in many cases, financial penalties instead issued for violations of state laws. That said, 2018 did see a major increase in HIPAA enforcement activity by state attorneys general.

There were 12 HIPAA-related financial penalties issued in 2018 by state attorneys general. The New Jersey attorney general was the most active HIPAA enforcer behind OCR with 4 HIPAA fines, followed by New York with 3, Massachusetts with 2, and 1 financial penalty issued by each of Connecticut, District of Columbia, and Washington.

The largest attorney general HIPAA fine of 2018 – Aetna’s $1,150,000 penalty – was issued by New York. Aetna was also fined a total of $640,171 in a multi-state action by Connecticut, New Jersey, Washington, and the District of Columbia. Washington has yet to agree to a settlement amount with Aetna.

EmblemHealth was fined a total of $675,000 for a 2016 data breach: $575,000 by New York and $100,000 by New Jersey.

State Covered Entity Amount State Residents Affected
Massachusetts McLean Hospital $75,000 1,500
New Jersey EmblemHealth $100,000 6,443
New Jersey Best Transcription Medical $200,000 1,650
Washington Aetna TBA* 13,160 (multi-state total)
Connecticut Aetna $99,959 13,160 (multi-state total)
New Jersey Aetna $365,211.59 13,160 (multi-state total)
District of Columbia Aetna $175,000 13,160 (multi-state total)
Massachusetts UMass Memorial Medical Group / UMass Memorial Medical Center $230,000 15,000
New York Arc of Erie County $200,000 3,751
New Jersey Virtua Medical Group $417,816 1,654
New York EmblemHealth $575,000 81,122
New York Aetna $1,150,000 13,160 (multi-state total)

*Washington yet to determine settlement amount

The post Summary of 2018 HIPAA Fines and Settlements appeared first on HIPAA Journal.
IT Service Providers and Customers Warned of Increase in Chinese Malicious Cyber Activity

The Department of Homeland Security (DHS) United States Computer Emergency Readiness Team (US-CERT) has issued an alert about increased Chinese malicious cyber activity targeting IT service providers such as Managed Service Provider (MSPs), Managed Security Service Providers (MSSPs), Cloud Service Providers (CSPs) and their customers.

The attacks take advantage of trust relationships between IT service providers and their customers. A successful cyberattack on a CSP, MSP or MSSP can give the attackers access to healthcare networks and sensitive patient data.

The DHS Cybersecurity and Infrastructure Security Agency (CISA) has issued technical details on the tactics and techniques used by Chinese threat actors to gain access to services providers’ networks and the systems of their customers.

The information has been shared to allow network defenders to take action to block the threats and reduce exposure to the Chinese threat actors’ activities. Guidance has been released for IT service providers and their customers on the steps that should be taken to improve security to prevent successful attacks. While a range of mitigations have been specified, there is no single solution that will work for all organizations and mitigating these malicious activities can be a complex process.

Advice for Customers of IT Service Providers

Healthcare organizations that utilize IT service providers are advised to:

  • Ensure their providers have conducted a review to determine if there is a security concern or has been a compromise
  • Ensure their IT service providers have implemented solutions and tools to detect cyberattacks.
  • Review and verify connections between healthcare systems and those used by IT service providers.
  • Verify all IT service provider accounts are being used for appropriate purposes.
  • Disable IT service provider accounts when they are not in use.
  • Ensure business associate agreements require IT service providers to implement appropriate security controls, require logging and monitoring of client systems and connections to their networks, and the need to promptly issue notifications when suspicious activity is detected.
  • Integrate system log files and network monitoring data into intrusion detection and security monitoring systems for independent correlation, aggregation and detection.
  • Ensure service providers view US-CERT pages related to APT groups targeting IT service providers, specifically TA-18-276A and TA-18-276B.

Advice for IT Service Providers

IT service providers have been advised to take the following actions to mitigate the risk of cyberattacks:

  • Ensure the mitigations detailed in US-CERT alerts are fully implemented.
  • Ensure the principle of least privilege is applied to their environments, customers’ data are logically separated, and access to clients’ networks is not shared.
  • Implement advanced network and host-based monitoring systems that look for anomalous behavior that could indicate malicious activity.
  • Aggregate and correlate log information to maximize the probability of detection of malicious activity and account misuse.
  • Work closely with customers to ensure that all hosted infrastructure is carefully monitored and maintained.

The post IT Service Providers and Customers Warned of Increase in Chinese Malicious Cyber Activity appeared first on HIPAA Journal.

HHS Publishes Cybersecurity Best Practices for Healthcare Organizations

The U.S. Department of Health and Human Services has issued voluntary cybersecurity best practices for healthcare organizations and guidelines for managing cyber threats and protecting patients.

Healthcare technologies are essential for providing care to patients, yet those technologies introduce risks. If those risks are not properly managed they can result in disruption to healthcare operations, costly data breaches, and harm to patients.

The HHS notes that $6.2 billion was lost by the U.S. Health Care System in 2016 as a result of data breaches and 4 out of 5 physicians in the United States have experienced some form of cyberattack. The average cost of a data breach for a healthcare organization is now $2.2 million.

“Cybersecurity is everyone’s responsibility. It is the responsibility of every organization working in healthcare and public health,” said Janet Vogel, HHS Acting Chief Information Security Officer. “In all of our efforts, we must recognize and leverage the value of partnerships among government and industry stakeholders to tackle the shared problems collaboratively.”

The guidance and best practices – Health Industry Cybersecurity Practices (HICP): Managing Threats and Protecting Patients – were developed in response to a mandate in the Cybersecurity Act of 2015 Section 405(d) to issue practical guidelines to help healthcare organizations cost-effectively reduce healthcare cybersecurity risks.

The guidance was developed over two years with assistance provided by more than 150 cybersecurity and healthcare experts from industry and the government under the Healthcare and Public Health (HPH) Sector Critical Infrastructure Security and Resilience Public-Private Partnership.

“The healthcare industry is truly a varied digital ecosystem. We heard loud and clear through this process that providers need actionable and practical advice, tailored to their needs, to manage modern cyber threats. That is exactly what this resource delivers,” said Erik Decker, industry co-lead and Chief Information Security and Privacy Officer for the University of Chicago Medicine.

Two technical volumes have also been published that outline cybersecurity best practices for healthcare organizations tailored to the size of the organization: One for small healthcare providers such as clinics and a second volume for medium healthcare organizations and large health systems. The documents contain a common set of voluntary, consensus-based, and industry-led guidelines, best practices, methodologies, procedures, and processes.

The aim of the guidance and best practices is threefold: To help healthcare organizations reduce cybersecurity risks to a low level in a cost-effective manner, to support the voluntary adoption and implementation of Cybersecurity Act recommendations, and to provide practical, actionable, and relevant cybersecurity advice for healthcare organizations of all sizes.

The guidance aims to raise awareness of cybersecurity threats to the healthcare sector and help healthcare organizations mitigate the most impactful cybersecurity threats: Email phishing attacks, ransomware attacks, loss/theft of equipment and data, accidental and intentional insider data breaches, and medical device attacks that could affect patient safety.

Ten cybersecurity practices are detailed in the technical volumes to mitigate the above threats in the following areas:

  • E-mail protection systems
  • Endpoint protection systems
  • Access management
  • Data protection and loss prevention
  • Asset management
  • Network management
  • Vulnerability management
  • Incident response
  • Medical device security
  • Cybersecurity policies

A “cybersecurity practices assessments toolkit” has also been made available to help healthcare organizations prioritize threats and develop action plans to mitigate those threats.

Over the next few months, the HHS will be working closely with industry stakeholders to raise awareness of cybersecurity threats and implement the best practices across the health sector.

The post HHS Publishes Cybersecurity Best Practices for Healthcare Organizations appeared first on HIPAA Journal.

Most Common Security Weaknesses in Healthcare Identified

The most common security weaknesses in healthcare have been identified by Clearwater. Clearwater analyzed data from IRM analyses conducted over the past six years. Millions of risk records were assessed from hospitals, Integrated Delivery Networks, and business associates of those entities to identify the most common security vulnerabilities in healthcare.

The analysis revealed almost 37% of high and critical risks were in three areas:

  • User authentication
  • Endpoint leakage
  • Excessive user permissions

The most common security weaknesses in healthcare were deficiencies in user authentication. These are failures to correctly authenticate users and verify the level of access that users should have to an organization’s resources. These deficiencies include the use of default passwords and generic user IDs, writing down passwords and posting them on computer monitors or hiding them under keyboards, and the transmission of user credentials via email in plain text.

User authentication deficiencies were most commonly associated with servers and SaaS solutions. Clearwater also notes that more than 90% of healthcare organizations said they had password/token management policies and procedures, but in many cases the technical implementation of procedures was found to be lacking.

Clearwater recommends enforcing the use of strong passwords, enabling single sign-on, and implementing rate limiting to lock accounts after a set number of failed login attempts. Of the organizations that had user authentication deficiencies, 84.4% had deficiencies in password requirements, 52.2% failed to implement single sign-on, and 40.4% had not implemented rate limiting.

The cybersecurity best practice of limiting the use of admin accounts and restricting the systems and data that end users can access was often not adopted by healthcare organizations.

The failure to restrict access to drives and networks not required by users to perform their work duties increases risk. By restricting user permissions, if credentials are compromised, the damage that can be caused will be restricted. Healthcare organizations should adopt the principle of least privilege and should only give users access to data and networks that they require to perform their work duties.

The post Most Common Security Weaknesses in Healthcare Identified appeared first on HIPAA Journal.

NIST Releases Final Version of Risk Management Framework Update

The National Institute of Standards and Technology (NIST) has released the final version of its updated Risk Management Framework (RMF 2.0).

RMF 2.0 (SP 800-37 Revision 2: Risk Management Framework (RMF) for Information Systems and Organizations: A System Life Cycle Approach for Security and Privacy) addresses privacy and security concerns in IT risk management.

One key change in the updated version of the RMF is the introduction of a ‘Prepare’ step. This additional step involves assigning responsibilities to specific individuals, enabling enterprise-wide privacy and security controls, eliminating unnecessary functions, publishing common controls, prioritizing resources for high value assets, and establishing communication channels to ensure effective communication between the C-Suite and employees. The ‘Prepare’ step, which comes before the Categorize step, was introduced to help organizations “achieve more effective, efficient, and cost-effective security and privacy risk management processes.”

RMF 2.0 requires maximum use of automation in executing the framework rules to allow continuous assessment and monitoring of privacy and security controls, and the preparation of authorization packages for timely decision making.

NIST has listed seven main objectives for the updated RMF. By achieving some or all of the objectives listed below, execution of the RMF will be simplified, organizations will be able to employ innovative approaches for risk management, and will increase the level of automation for risk management-related tasks.

The seven objectives are:

  • To achieve closer linkage and communication between the risk management processes and activities at the C-suite and the individuals, processes, and activities at the system and operational level of the organization.
  • To institutionalize critical risk management preparatory activities at all risk management levels.
  • To demonstrate how the NIST Cybersecurity Framework can be aligned with the RMF and implemented using current NIST risk management processes.
  • To integrate privacy risk management processes into the RMF
  • To promote the development of secure software and systems through the alignment of life cycle-based systems engineering processes.
  • To integrate security-related, supply chain risk management (SCRM) concepts into the RMF to address untrustworthy suppliers, insertion of counterfeits, tampering, unauthorized production, theft, insertion of malicious code, and poor manufacturing and development practices throughout the SDLC.
  • To allow for an organization-generated control selection approach to complement the traditional baseline control selection approach and support the use of the NIST consolidated control catalog (SP 800-53, Revision 5).

The Office of Management and Budget (OMB) requires all states and agencies to follow RMF 2.0 to manage security and privacy risks. RMF 2.0 allows them to manage privacy and security risk in a single, unified framework.

According to NIST fellow, Ron Ross, “[RMF 2.0] ensures the term compliance means real cybersecurity and privacy risk management – not just satisfying a static set of controls in a checklist.”

The post NIST Releases Final Version of Risk Management Framework Update appeared first on HIPAA Journal.

Largest Healthcare Data Breaches of 2018

This post summarizes the largest healthcare data breaches of 2018: Healthcare data breaches that have resulted in the loss, theft, unauthorized accessing, impermissible disclosure, or improper disposal of 100,000 or more healthcare records.

2018 has seen 18 data breaches that have exposed 100,000 or more healthcare records. 8 of those breaches saw more than half a million healthcare records exposed, and three of those breaches exposed more than 1 million healthcare records.

A Bad Year for Healthcare Data Breaches

As of December 27, 2018, the Department of Health and Human Services’ Office for Civil Rights (OCR) has received notifications of 351 data breaches of 500 or more healthcare records. Those breaches have resulted in the exposure of 13,020,821 healthcare records.

It is likely that the year will finish on a par with 2017 in terms of the number of reported healthcare data breaches; however, more than twice as many healthcare records have been exposed in 2018 than in 2017.

In 2017, there were 359 data breaches of 500 or more records reported to OCR. Those breaches resulted in the exposure of 5,138,179 healthcare records.

The Largest Healthcare Data Breaches of 2018

Listed below is a summary of the largest healthcare data breaches of 2018. A brief description of those breaches has been listed below.

At the time of writing, OCR is still investigating all but one of the breaches listed below. Only the LifeBridge Health breach investigation has been closed.

Rank


Name of Covered Entity Covered Entity Type Individuals Affected Type of Breach
1 AccuDoc Solutions, Inc. Business Associate 2,652,537 Hacking/IT Incident
2 UnityPoint Health Business Associate 1,421,107 Hacking/IT Incident
3 Employees Retirement System of Texas Health Plan 1,248,263 Unauthorized Access/Disclosure
4 CA Department of Developmental Services Health Plan 582,174 Theft
5 MSK Group Healthcare Provider 566,236 Hacking/IT Incident
6 CNO Financial Group, Inc. Health Plan 566,217 Unauthorized Access/Disclosure
7 LifeBridge Health, Inc Healthcare Provider 538,127 Hacking/IT Incident
8 Health Management Concepts, Inc. Business Associate 502,416 Hacking/IT Incident
9 AU Medical Center, INC Healthcare Provider 417,000 Hacking/IT Incident
10 SSM Health St. Mary’s Hospital – Jefferson City Healthcare Provider 301,000 Improper Disposal
11 Oklahoma State University Center for Health Sciences Healthcare Provider 279,865 Hacking/IT Incident
12 Med Associates, Inc. Business Associate 276,057 Hacking/IT Incident
13 Adams County Healthcare Provider 258,120 Unauthorized Access/Disclosure
14 MedEvolve Business Associate 205,434 Unauthorized Access/Disclosure
15 HealthEquity, Inc. Business Associate 165,800 Hacking/IT Incident
16 St. Peter’s Surgery & Endoscopy Center Healthcare Provider 134,512 Hacking/IT Incident
17 New York Oncology Hematology, P.C. Healthcare Provider 128,400 Hacking/IT Incident
18 Boys Town National Research Hospital Healthcare Provider 105,309 Hacking/IT Incident


Causes of the Largest Healthcare Data Breaches of 2018

Further information on the causes of the largest healthcare breaches of 2018.

AccuDoc Solutions, Inc.

Morrisville, NC-based AccuDoc Solutions, a billing company that operates the online payment system used by Atrium Health’s network of 44 hospitals in North Carolina, South Carolina and Georgia, discovered that some of its databases had been compromised between September 22 and September 29, 2018. The databases contained the records of 2,652,537 patients. While data could have been viewed, AccuDoc reports that the databases could not be downloaded. Not only was this the largest healthcare data breach of 2018, it was the largest healthcare data breach to be reported since September 2016.

UnityPoint Health

A UnityPoint Health phishing attack was detected on May 31, 2018. The forensic investigation revealed multiple email accounts had been compromised between March 14 and April 3, 2018 as a result of employees being fooled in a business email compromise attack. A trusted executive’s email account was spoofed, and several employees responded to the messages and disclosed their email credentials. The compromised email accounts contained the PHI of 1,421,107 individuals.

Employees Retirement System of Texas

The Employees Retirement System of Texas discovered a flaw in its ERS OnLine portal that allowed certain individuals to view the protected health information of other members after logging into the portal. The breach was attributed to a coding error. Up to 1,248,263 individuals’ PHI was potentially viewed by other health plan members.

CA Department of Developmental Services

The California Department of Developmental Services experienced a break in at its offices. During the time the thieves were in the offices they potentially accessed the sensitive information of approximately 15,000 employees, contractors, job applicants, and parents of minors who receive DDS services, in addition to the PHI of 582,174 patients.

MSK Group

Tennessee-based MSK Group, P.C, a network of orthopedic medical practices, discovered in May 2018 that hackers had gained access to its network. Certain parts of the network had been accessed by the hackers over a period of several months. The records of 566,236 patients, which included personal, health and insurance information, may have been viewed or copied by the hackers.

CNO Financial Group, Inc.

Chicago-based health insurer Bankers Life, a division of CNO Financial Group Inc., discovered hackers gained access to its systems between May 30 and September 13, 2018 and potentially stole the personal information of 566,217 individuals.

LifeBridge Health, Inc

The Baltimore-based healthcare provider LifeBridge Health discovered malware had been installed on a server that hosted the electronic medical record system used by LifeBridge Potomac Professionals and LifeBridge Health’s patient registration and billing systems. Those systems contained the PHI of 538,127 patients.

Health Management Concepts, Inc.

Health Management Concepts discovered hackers gained access to a server used for sharing files and installed ransomware. The ransom demand was paid to unlock the encrypted files; however, HMC reported that the hackers were ‘inadvertently provided’ with a file that contained the PHI of 502,416 individuals. It is suspected that the file was unwittingly sent to the attackers to prove they could decrypt files.

AU Medical Center, INC

An Augusta University Medical Center phishing attack resulted in an unauthorized individual gaining access to the email accounts of two employees. The compromised email accounts contained the PHI of 417,000 patients.

SSM Health St. Mary’s Hospital – Jefferson City

St. Mary’s Hospital moved to new premises and all patients’ medical records were transferred to the new facility; however, on June 1, 2018, the hospital discovered administrative documents containing the protected health information of 301,000 patients had been left behind. In the most part, the breach was limited to names and medical record numbers.

Oklahoma State University Center for Health Sciences

Oklahoma State University Center for Health Sciences discovered an unauthorized individual gained access to parts of its computer network and potentially accessed files containing billing information of Medicaid patients. The breach affected 279,865 patients, although only a limited amount of PHI was accessible.

Med Associates, Inc.

The Latham, NY-based health billing company Med Associates, which provides claims services to more than 70 healthcare providers, discovered an employee’s computer has been accessed by an unauthorized individual. It is possible that the attacker gained access to the PHI of up to 276,057 patients.

Adams County

Adams County, WI, discovered hackers gained access to its network and potentially accessed the PHI and PII of 258,102 individuals. The compromised systems were used by the departments of Health and Human Services, Child Support, Veteran Service Office, Extension Office, Adams County Employees, Solid Waste, and the Sheriff’s Office.

MedEvolve

MedEvolve, a provider of electronic billing and record services to healthcare providers, discovered an FTP server had been left unsecured between March 29, 2018 and May 4, 2018. A file on the FTP server contained the PHI of 205,434 patients of Premier Immediate Medical Care.

HealthEquity, Inc.

HealthEquity, a Utah-based company that provides services to help individuals gain tax advantages to offset the cost of healthcare, experienced a phishing attack that resulted in hackers gaining access to the email accounts of two employees. Those accounts contained the PHI of 165,800 individuals.

St. Peter’s Surgery & Endoscopy Center

St. Peter’s Surgery & Endoscopy Center in New York discovered malware had been installed on one of its servers which potentially allowed hackers to view the PHI of 134,512 patients. The malware was discovered the same day it was installed. The fast detection potentially prevented patients’ data from being viewed or copied.

New York Oncology Hematology, P.C.

A phishing attack on New York Oncology Hematology in Albany, NY, resulted in hackers gaining access to the email accounts of 15 employees. Those accounts contained the PHI of 128,400 current and former patients and employees.

Boys Town National Research Hospital

Boys Town National Research Hospital, an Omaha, NE hospital specializing in pediatric deafness, visual and communication disorders, experienced a phishing attack that allowed hackers to gain access to a single email account. The email account contained the PHI of 105,309 patients.

The post Largest Healthcare Data Breaches of 2018 appeared first on HIPAA Journal.

November 2018 Healthcare Data Breach Report

For the second consecutive month there has been an increase in both the number of reported healthcare data breaches and the number of records exposed, stolen, or impermissibly disclosed.

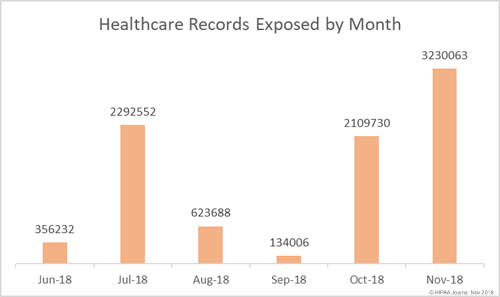
November was the worst month of the year to date for healthcare data breaches in terms of the number of exposed healthcare records. 3,230,063 records were exposed, stolen, or impermissibly disclosed in the breaches reported in November.

To put that figure into perspective, that’s more records than were exposed in all 180 data breaches reported to the HHS’ Office for Civil Rights (OCR) in the first half of 2018.

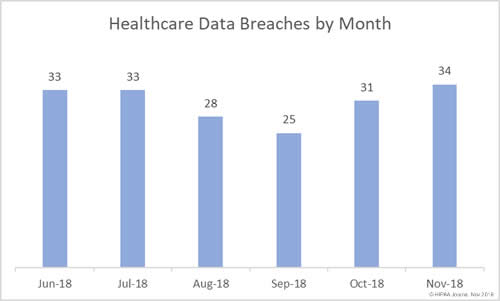
Healthcare Data Breaches June-November 2018

There were 34 healthcare data breaches reported to OCR in November, making it the second worst month of the year to date for breaches, behind June when 41 breaches were reported.

Healthcare Data Breaches June to November 2018

Largest Healthcare Data Breaches in November 2018

The largest healthcare data breach of 2018 was reported in November by Accudoc Solutions, a business associate of Atrium Health that provides healthcare billing services. That single breach resulted in the exposure of more than 2.65 million healthcare records.

AccuDoc Solutions discovered hackers had gained access to some of its databases for a week in September 2018. According to AccuDoc, the information in the databases could only be viewed, not downloaded.

Rank Name of Covered Entity Covered Entity Type Individuals Affected Type of Breach
1 AccuDoc Solutions, Inc. Business Associate 2652537 Hacking/IT Incident
2 HealthEquity, Inc. Business Associate 165800 Hacking/IT Incident
3 New York Oncology Hematology, P.C. Healthcare Provider 128400 Hacking/IT Incident
4 Baylor Scott & White Medical Center – Frisco Healthcare Provider 47984 Hacking/IT Incident
5 Cancer Treatment Centers of America (CTCA) at Western Regional Medical Center Healthcare Provider 41948 Hacking/IT Incident
6 Oprex Surgery (Baytown), L.P. d/b/a Altus Baytown Hospital Healthcare Provider 40000 Hacking/IT Incident
7 Center for Vitreo-Retinal Diseases Healthcare Provider 20371 Unauthorized Access/Disclosure
8 Veterans Health Administration Healthcare Provider 19254 Unauthorized Access/Disclosure
9 Steward Medical Group Healthcare Provider 16276 Hacking/IT Incident
10 Mind and Motion, LLC Healthcare Provider 16000 Hacking/IT Incident

Main Causes of November 2018 Healthcare Data Breaches

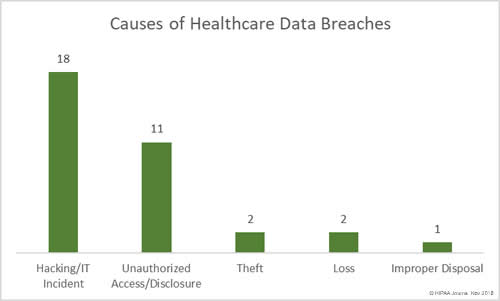
As was the case in October, hacking/IT incidents accounted for the highest number of data breaches and the most exposed/stolen healthcare records. There were 18 hacking/IT incidents reported in November. Those breaches impacted 3,138,657 individuals.

There were 11 breaches classified as unauthorized access/disclosure incidents which impacted 65,143 individuals, and 4 loss/theft incidents that resulted in the exposure of 22,333 healthcare records. One improper disposal incident exposed 3,930 healthcare records.

Causes of Healthcare Data Breaches in November 2018

Location of Breached Protected Health Information

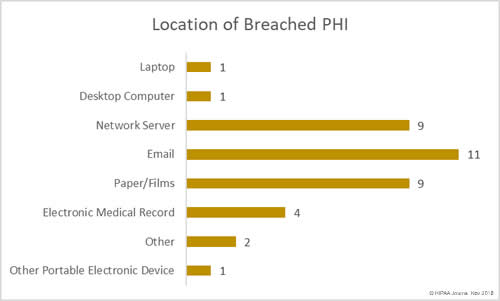
Email breaches continue to be a major problem in healthcare. These breaches include phishing attacks, unauthorized accessing of email accounts, and misdirected emails. There were 11 email-related breaches of PHI in November. Up until December 19, 2018, 111 email-related healthcare data breaches have been reported to OCR. Those breaches involved more than 3.4 million healthcare records.

Technical solutions can be implemented to reduce the number of email related breaches. Spam filters will prevent the majority of phishing emails from reaching inboxes, but no technical solution will be 100% effective so employees need to be trained how to recognize phishing attacks and other email threats.

All individuals in an organization from the CEO down should receive regular security awareness training with a particular emphasis on phishing. In addition to regular training sessions, phishing simulation exercises should be conducted. Through phishing simulations, healthcare organizations can assess their security awareness training programs and find out which employees require further training.

Location of Breached Protected Health Information November 2018

Data Breaches by Covered-Entity Type

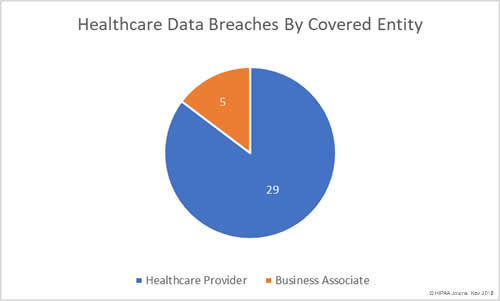
Healthcare providers were the covered entities worst affected by healthcare data breaches in November 2018 with 29 reported incidents.

Business associates of HIPAA-covered entities reported 5 breaches and there were a further five breaches reported by healthcare providers that had some business associate involvement – Twice the number of breaches involving business associates (to some degree) as October.

There were no health plan data breaches reported in November.

November 2018 healthcare data breaches by Covered-Entity type

Healthcare Data Breaches by State

Texas was the state worst affected by healthcare data breaches in November with 8 reported breaches. New York experienced three healthcare data breaches and there were two breaches reported in each of Georgia, Iowa, Illinois, Missouri, North Carolina, Utah, and Virginia.

One healthcare data breach was reported in Arizona, California, District of Columbia, Massachusetts, Maryland, Nebraska, New Jersey, Pennsylvania, and Washington.

Penalties for HIPAA Violations in November 2018

The Department of Health and Human Services’ Office for Civil Rights settled one HIPAA violation case with a healthcare provider in November.

Allergy Associates of Hartford was fined $125,000 over a physician’s impermissible disclosure of PHI to a TV reporter. The disclosure occurred after the physicians was instructed by the Allergy Associates of Hartford Privacy Officer not to respond to the reporter’s request for information about a patient, or to reply with ‘no comment’. Allergy Associates of Hartford failed to take any action against the physician over the HIPAA violation.

New Jersey also issued a financial penalty to a HIPAA-covered entity in November to resolve a HIPAA violation case. Best Transcription Medical was fined $200,000 for exposing the electronic protected health information of patients over the Internet. The breach affected 1,650 New Jersey residents.

The post November 2018 Healthcare Data Breach Report appeared first on HIPAA Journal.

27% of Healthcare Organizations Have Experienced a Ransomware Attack in the Past Year

According to a new report from Kaspersky Lab, 27% of healthcare employees said their organization had experienced at least one ransomware attack in the past five years and 33% said their organization had experienced multiple ransomware attacks.

In its report – Cyber Pulse: The State of Cybersecurity in Healthcare – Kaspersky lab explained that up until January 1, 2018, the U.S. Department of Health and Human Services’ Office for Civil Rights has been notified of more than 110 hacking/IT-related data breaches that have affected more than 500 individuals.

The impact of those breaches can be serious for the organizations concerned. Not only can breaches result in millions of dollars in costs, they can permanently damage the reputation of a healthcare organization and can result in harm being caused to patients.

To investigate the state of cybersecurity in healthcare, Kaspersky Lab commissioned market research firm Opinion Matters to conduct a survey of healthcare employees in the United States and Canada to explore the perceptions of healthcare employees regarding cybersecurity in their organization. 1,758 U.S. and Canadian healthcare employees were surveyed.

81% of small healthcare organizations (1-49 employees), 83% of medium-sized healthcare organizations (50-249 employees), and 81% of large healthcare organizations (250+ employees) said they had experienced between 1 and 4 ransomware attacks.

The cost of mitigating ransomware and malware attacks is considerable. According to the Ponemon Institute/IBM Security’s 2018 Cost of a Data Breach Report, the average cost of a data breach has now risen to $3.86 million. Kaspersky Lab’s 2018 Cost of a Data Breach Report places the average cost at $1.23 million for enterprises and $120,000 for SMBs.

While cybersecurity is important for reducing financial risk, 71% of healthcare employees said it was important for cybersecurity measures to be implemented to protect patients and 60% said it was important to have appropriate cybersecurity solutions in place to protect people and companies they work with.

Even though healthcare organizations have invested heavily in cybersecurity, many employees lack confidence in their organization’s cybersecurity strategy. Only 50% of healthcare IT workers were confident in they cybersecurity strategy, that fell to 29% for management and doctors, 21% for nurses, 23% for finance department employees, and 13% for the HR department.

Many healthcare employees appear to have a false sense of security. Even though healthcare data breaches are being reported on a daily basis, 21% of respondents had total faith in their organization’s ability to prevent cyberattacks and did not believe they would suffer a data breach in the forthcoming year.

While 73% of surveyed employees said they would inform their security team if they received an email from an unknown individual requesting PHI or login credentials, 17% of employees said they would do nothing if they received such a request. 17% of employees also admitted to having received an email request from a third-party vendor for ePHI and provided the ePHI as requested.

“Healthcare companies have become a major target for cybercriminals due to the successes they’ve had, and repeatedly have, in attacking these businesses. As organizations look to improve their cybersecurity strategies to justify employee confidence, they must examine their approach,” explained Rob Cataldo, VP of enterprise sales at Kaspersky Lab. “Business leaders and IT personnel need to work together to create a balance of training, education, and security solutions strong enough to manage the risk.”

The post 27% of Healthcare Organizations Have Experienced a Ransomware Attack in the Past Year appeared first on HIPAA Journal.

Vulnerability Identified in Medtronic Encore and Carelink Programmers

ICS-CERT has issued an advisory about a vulnerability that has been identified in certain Medtronic CareLink and Encore Programmers. Some personally identifiable information (PII) and protected health information (PHI) stored on the devices could potentially be accessed due to a lack of encryption for data at rest.

The programmers are used in hospitals to program and manage Medtronic cardiac devices and may store reports containing patients’ PII/PHI. An attacker with physical access to one of the vulnerable programmers could access the reports and view patients PII/PHI. The vulnerability would require a low level of skill to exploit.

The vulnerability, tracked as CVE-2018-18984 (CWE-311), was identified by security researchers Billy Rios and Jonathan Butts of Whitescope LLC who discovered encryption was either missing or stored PII/PHI was not sufficiently encrypted. The vulnerability has been assigned a CVSS V3 base score of 4.6.

The vulnerability is present in all versions of CareLink 2090 Programmers, CareLink 9790 Programmers, and the 29901 Encore Programmers.

Medtronic has advised all hospitals to stop using CareLink 9790 Programmers for any purpose as they have reached end-of-life and are no longer supported.

Users of CareLink 2090 and 29901 Encore Programmers should ensure that PII/PHI is stored on the Programmers for the shortest possible time. The devices are only intended to be used to store PII/PHI for short periods of time until the information can be transferred to other medical systems or printed to paper reports.

All affected programmers allow reports containing PII/PHI to be manually deleted when they are no longer required. Users of all vulnerable Programmers should ensure that all PII/PHI is deleted from the devices before they are decommissioned.

Medtronic has also advised users to ensure physical control of the Programmers is maintained at all times to prevent unauthorized access and only to use legitimately obtained Programmers and not to use any that are supplied by a third party.

The post Vulnerability Identified in Medtronic Encore and Carelink Programmers appeared first on HIPAA Journal.